
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/darksh3llgr/autoscan
Vulnerability ScannersExploit FrameworksPenetration Testing
GitHubdarksh3llgr/autoscan

autoscan

Automated Scanning, Pentesting , Exploiting and Reporting

View Repository
213384 years agoReviewed by Kitploit
Share

autoscan.sh

Overview autoscan.sh

is fully automated penetration test tool linked with Metasploit, nmap and other free avialable tools and report all of this in faraday (faraday is one tool, you can use it for other open source reporting tools, an example is to export it in jira). Autoscan identifies the status of all opened ports, search for vulnerabilities on the target system, and execute avialable exploits.

Procedure

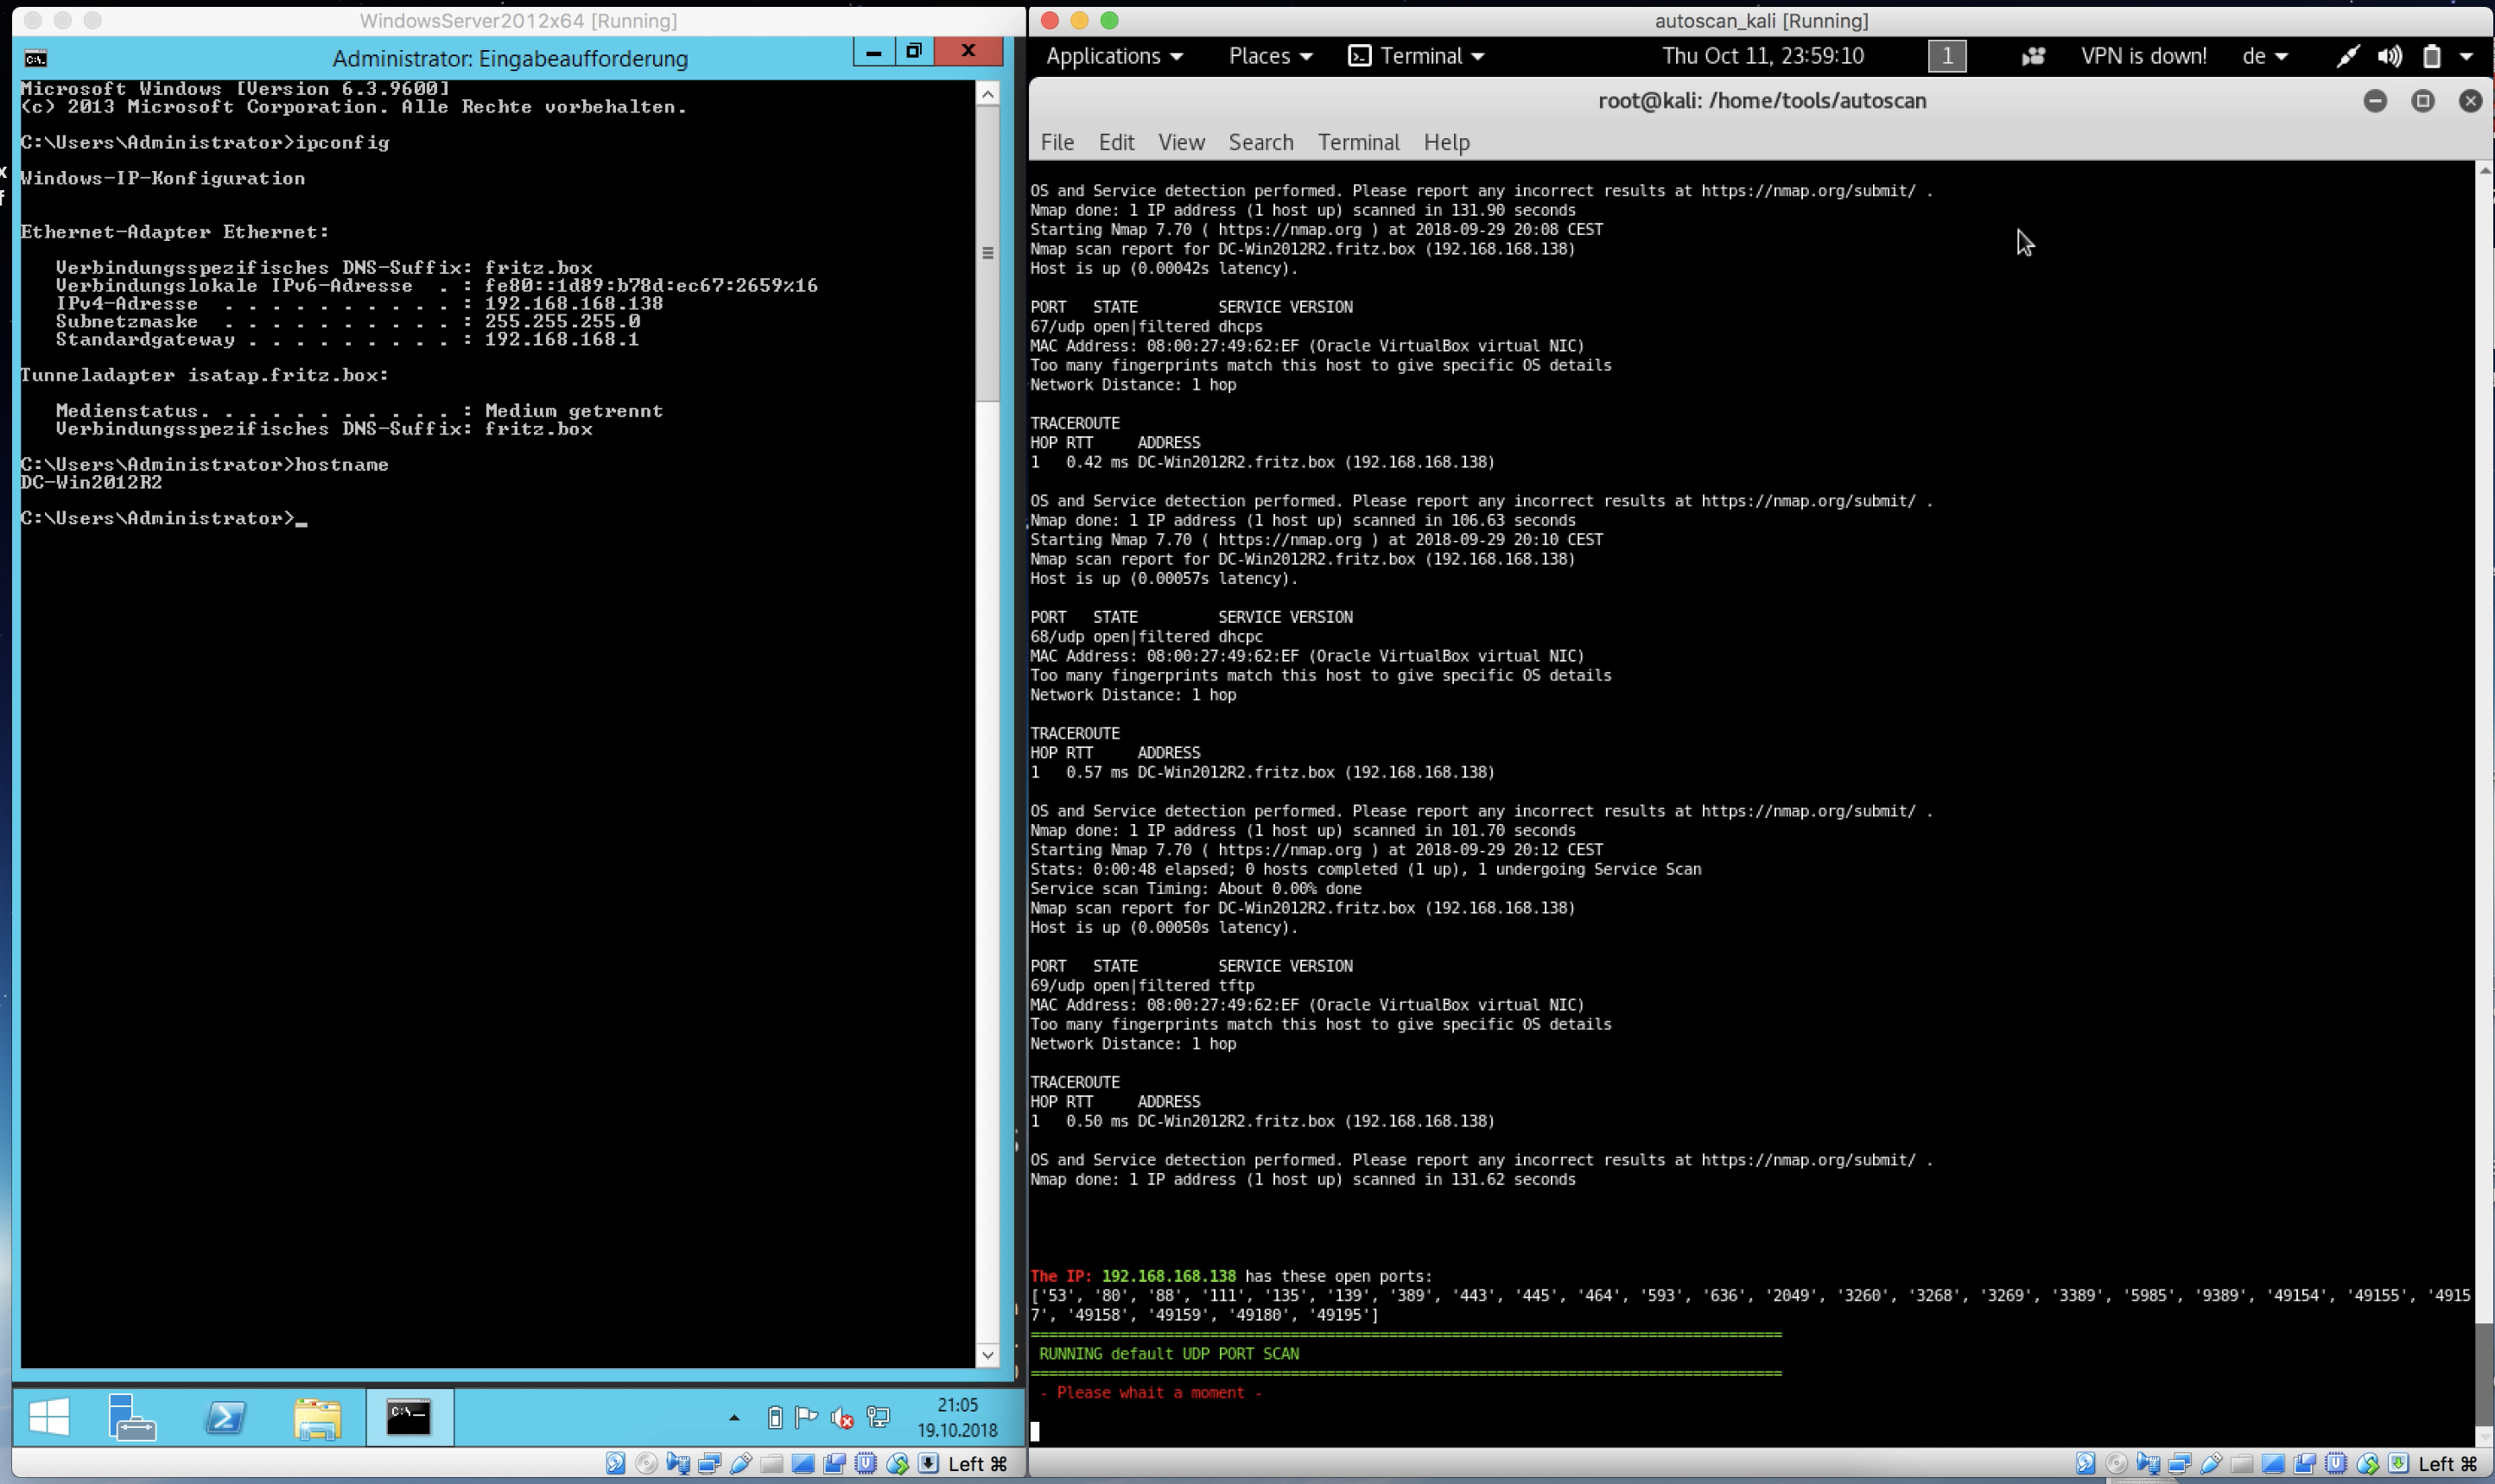
  • Scan all TCP ports, and most used UDP Ports.
  • Many services enumerated and exploited.
  • For every tool action, generate a logfile. The pentester can grab a coffee (or two...) and read the logs once the scan has been completed.
  • then the real pentest can start ;-)
  • Enumerate the System OS and start exploits for this OS. Enumerate the services running on ports and start another tool or exploit, or both.
  • Import all generated xml, csv and nessus files to faraday reporting and colaboration server. (I am not the owner of these tools!) Most of the tools are started from $TOOL_DIR. So if a tool does not exist, check if the required tool is installed or linked to your tool directory (../autoscan/tools/).

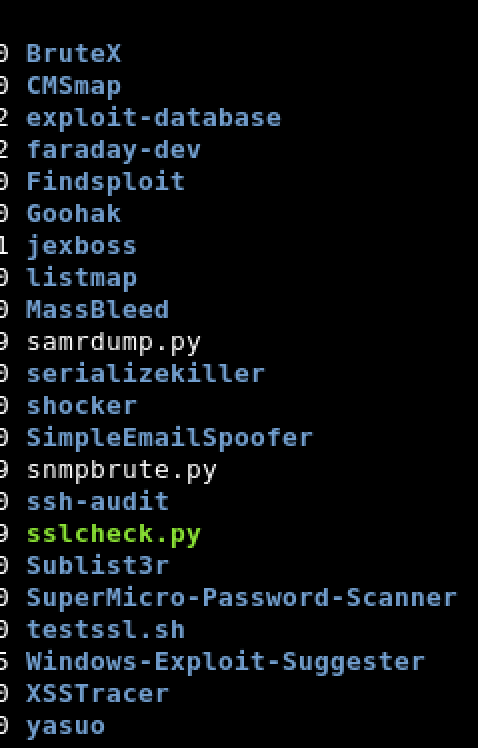
Other tools

#Brutex #CMSmap #exploit-database #Findsploit #Goohak #listmap #MassBled #serializekiller #shoker #ssh-audit #Sublist3r #testssl #Windows-Exploit-Suggester #XSSTracer #yasuo #arachni #wpscan #... #.. #. #Scann all TCP ports, and the most used UDP Ports.

HAFTUNGSAUSSCHLUSS Dieses Tool bezieht sich auf IT, Hacking, Programmierung und Computer | Netzwerk | Software-Sicherheit. Das Wort "Hack", "Pen Testing", "Hacking", das auf diesen Projektseiten verwendet wird, wird als "Ethical Hack" bzw. "Ethical Hacking" bezeichnet. Dies ist kein Tool, das illegale Informationen bereitstellt. Wir fördern weder Hacking noch Software-Cracking. Alle auf diesen Seiten bereitgestellten Informationen dienen ausschließlich Bildungszwecken.

Reporting

For Reporting you need a comercial license from Farady. This tool never include a Faraday license. For more informations about faraday, please contact the faraday team.

Install and execute

You need before use it, install some tools. The most of this tools are (pre) installed in Kali Linux This script are testet with Kali Linux. Installation script exist, but is in development, if you use it, you use it at your own risk. Download the scripts to /home/tools/autoscan. If the directory dont exist, make it. Clone the repository in this folder.

Windows

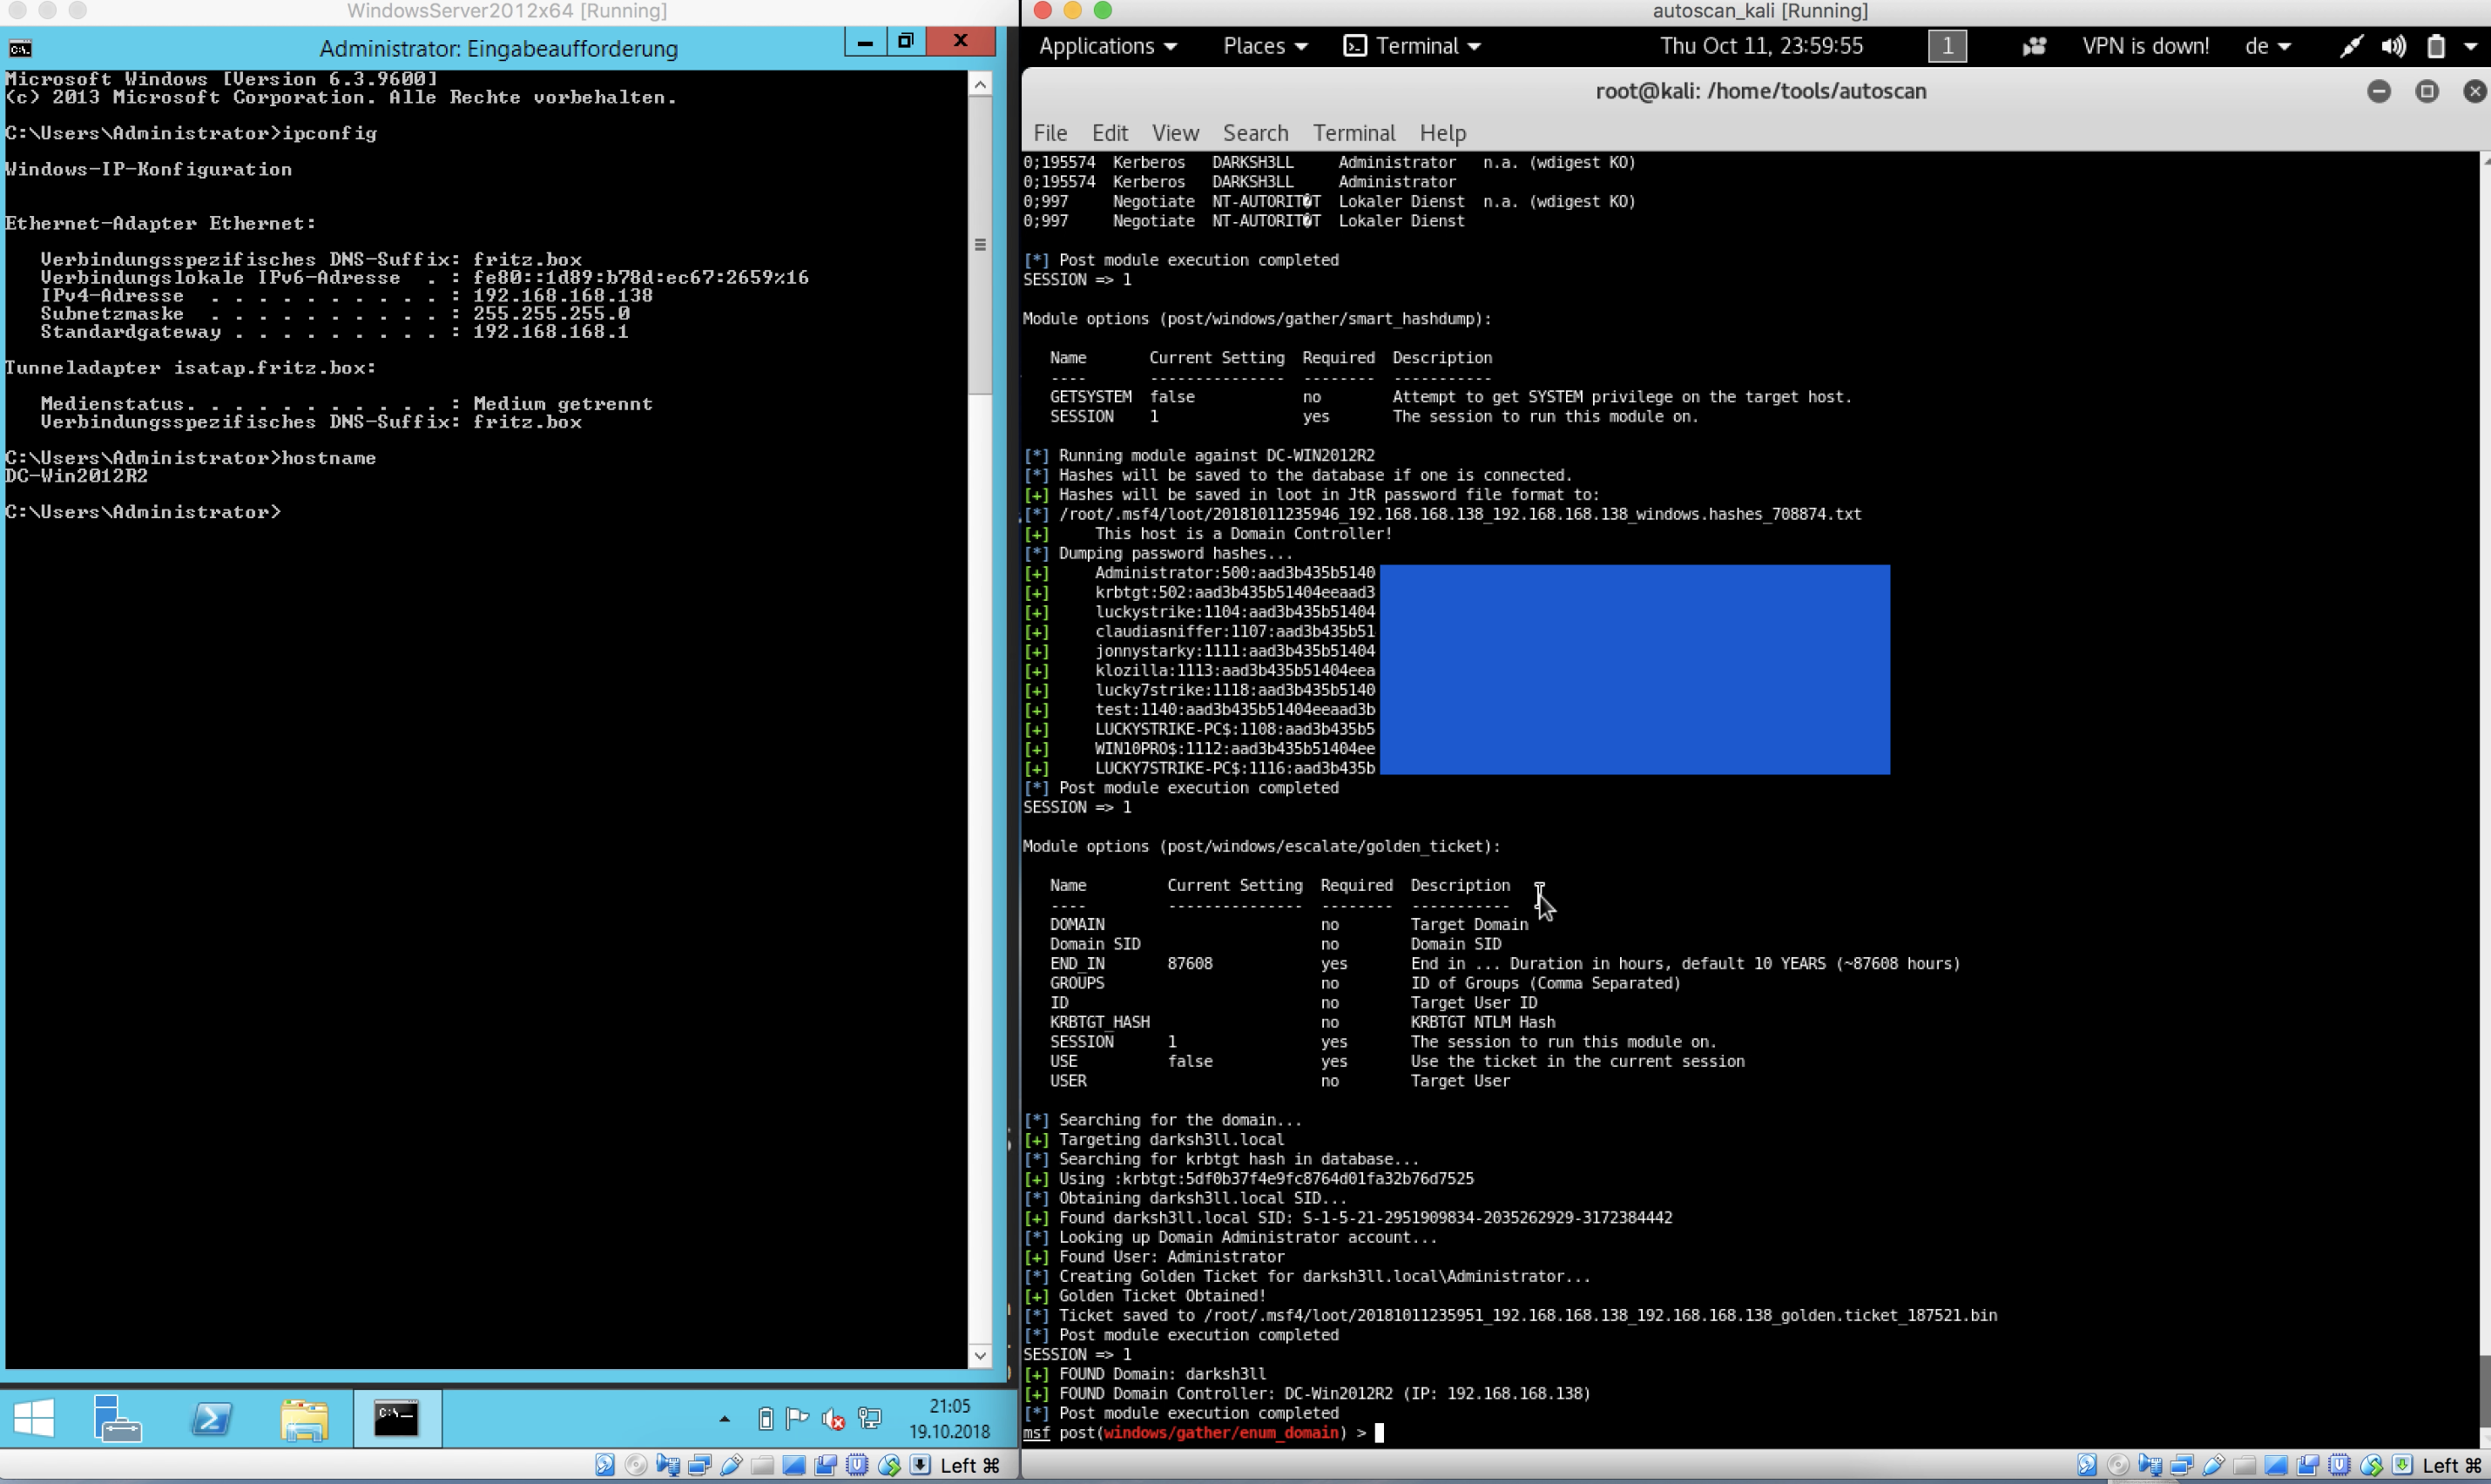
This script use standard exploits to exploit Windows Server 2012, Win7, WinXP and other Windows based OS, Websites and CMS systems and other services.

Linux

The functionality exploiting remote unixoide OS systems are in progress. But, many services enumerated and exploited also if the server is a linux host.

Development

New tools are work in progress. This tools at the moment have issues, so I never give a garanty for work without errors. If you use it, you use it at your own risk.

Webinterface

Exist, is a simple PHP Script, in development.

Video

Yes, not on youtube :-)

Images

to do

  • export function for jira
  • start nessus scan
  • start a burp scan with the burp api
  • add more tools and exploits
  • solve all issues and complete the install script
  • add veil support and nps_payload to distribute the payload over smb port
  • add kerberos silver ticket extraction without msf
  • more in smb enum and enum4linux ....
  • compare more the output, example: is port 445 and win system then do .... also in linux .....
  • ...... ......
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    831
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    534
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    429
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    355
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    284
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    275

Explore all tools

Browse our collection of tools

View all tools →