
ioctlance
 zeze-zeze/ioctlance
A tool that is used to hunt vulnerabilities in x64 WDM drivers
binary-analysisdynamic-analysis-sandboxingexploit-frameworks+4
4733 months ago
zeze-zeze/ioctlanceA tool that is used to hunt vulnerabilities in x64 WDM drivers
 edu0x01/hack-tools
Project that brings together several pentest tools
 erarnitox/malvexc2
A simple C2 Framework written in modern C++
 s-retlaw/l4s_poc
Log4Shell (Cve-2021-44228) Proof Of Concept
 allevon412/teamsimplant
Stealthy DLL proxying implant for Microsoft Teams that injects AES-encrypted shellcode via unhooking techniques, providing persistent backdoor access…
 jephthai/evilvm
Forth-based compiler deployed as position-independent x86_64 shellcode, providing a remote code execution agent with interactive REPL over TCP, HTTP,…
 samugit83/redamon
An AI-powered agentic red team framework that automates offensive security operations, from reconnaissance to exploitation to post-exploitation, with…
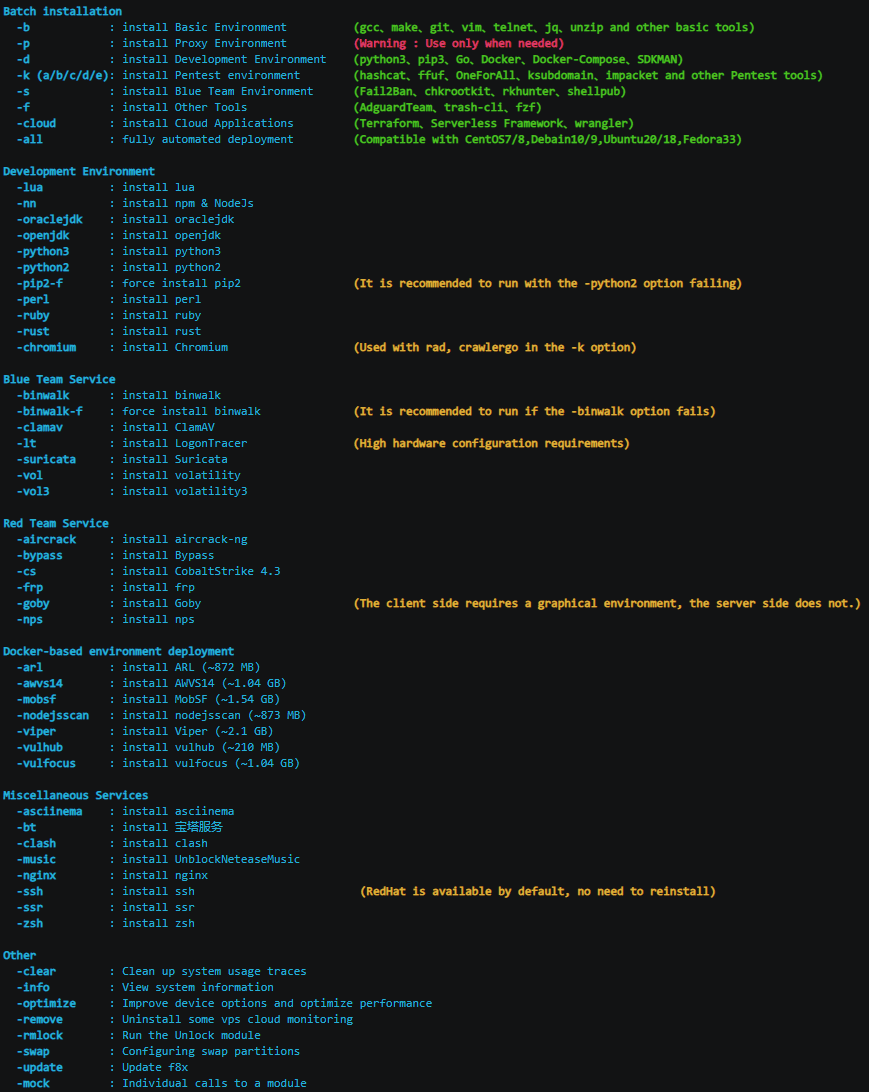 ffffffff0x/f8x
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool
 frkngksl/shoggoth
Polymorphic encryptor that transforms shellcode, PE, and COFF files into obfuscated, position-independent payloads with RC4 and random block cipher…
 seungsoo-lee/delta
PROJECT DELTA: SDN SECURITY EVALUATION FRAMEWORK
 cisc0-gif/kitt-lite
Python-Based Pentesting CLI Tool
 ch0pin/aviator
Antivirus evasion project
 beefproject/beef
The Browser Exploitation Framework Project
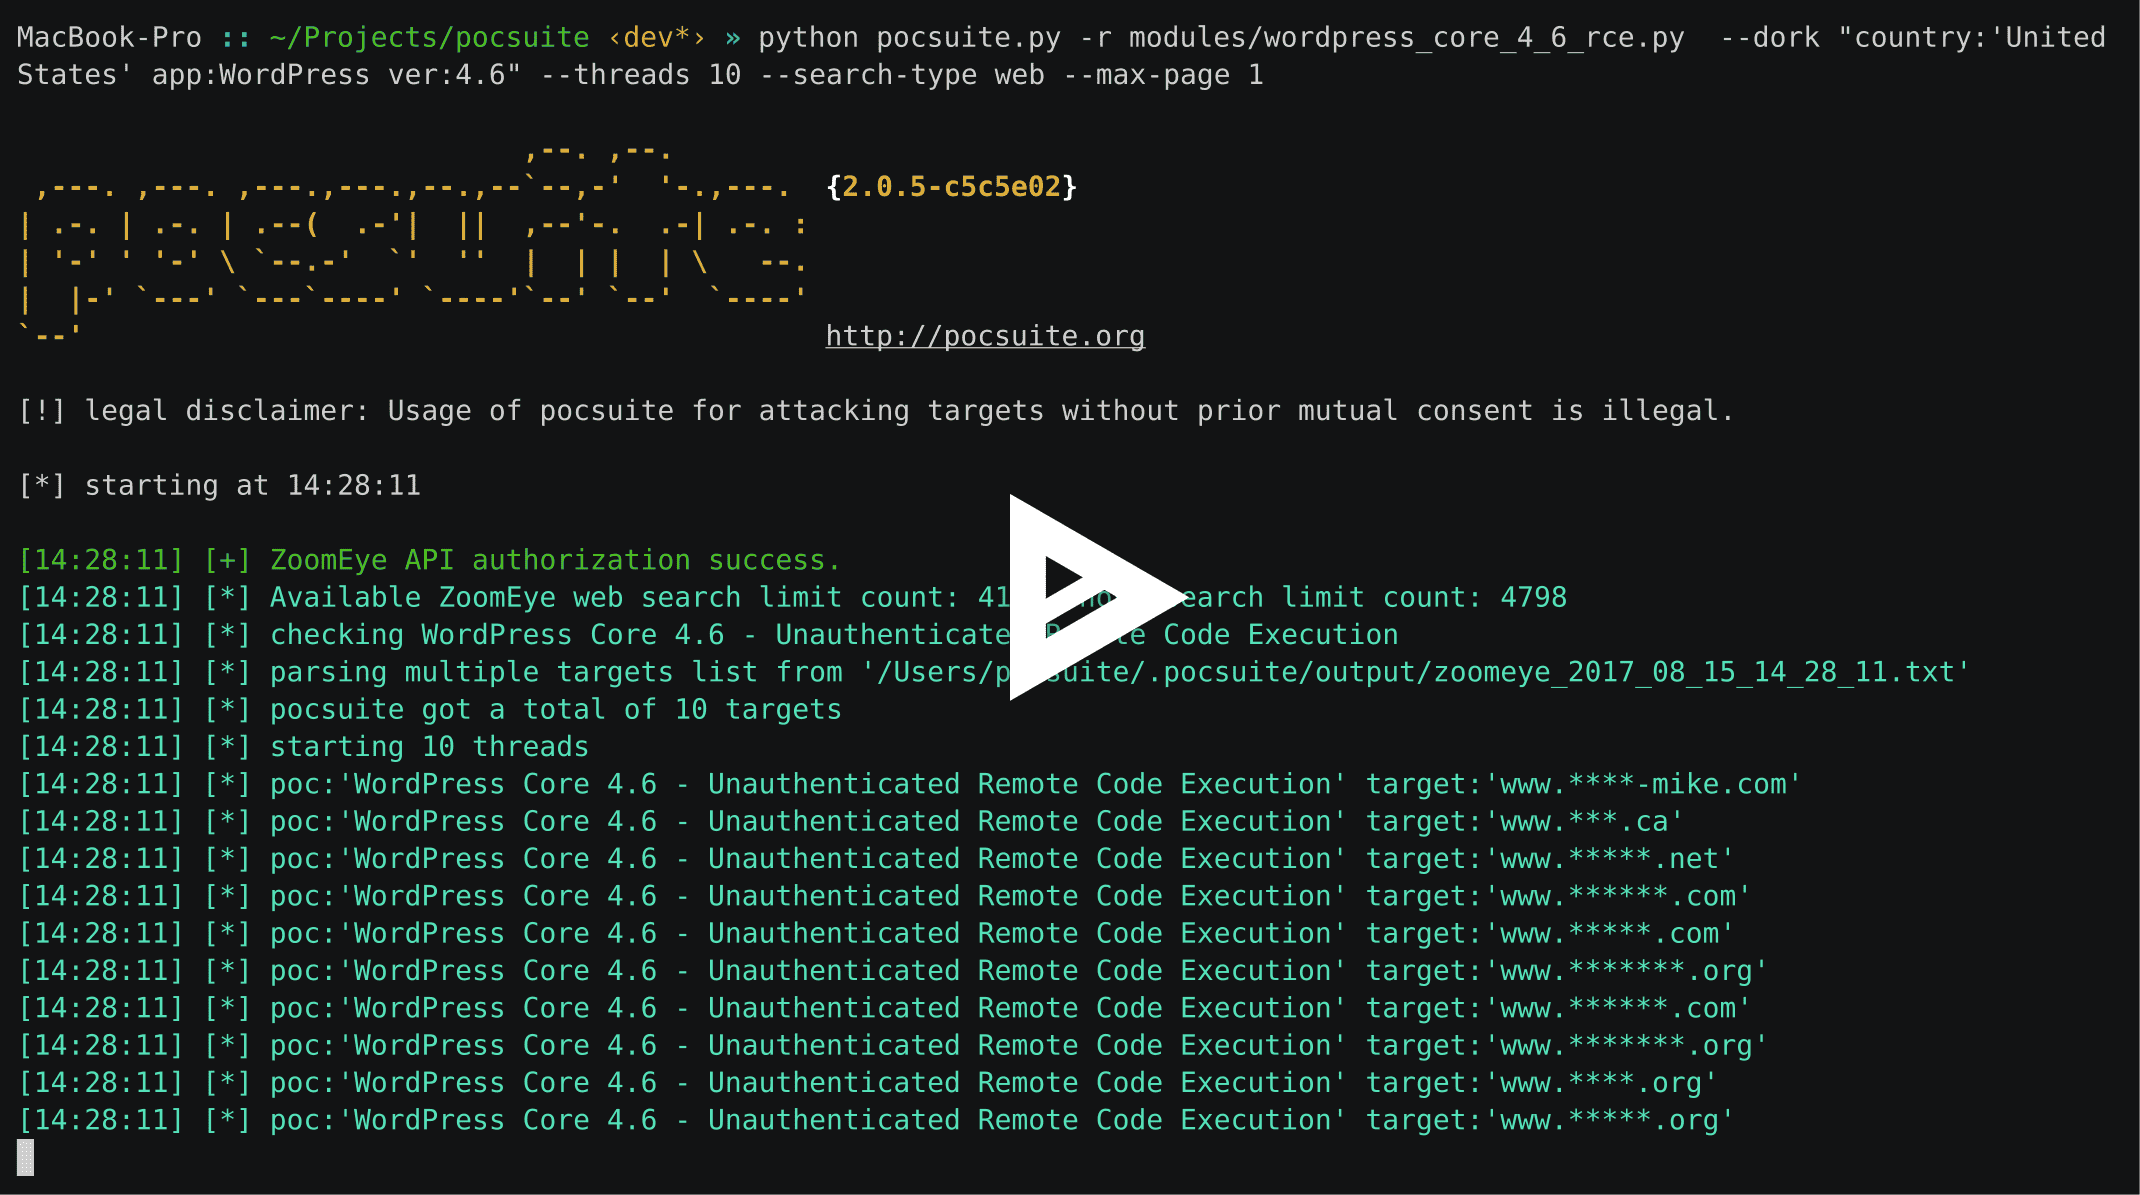 knownsec/pocsuite
This project has stopped to maintenance, please to https://github.com/knownsec/pocsuite3 project.
 dviros/excalibur
Excalibur is an Eternalblue exploit payload based "Powershell" for the Bashbunny project.
 enelg52/kittystager
KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…
 chacka0101/exploits
Exploits project Hacking Command Center