
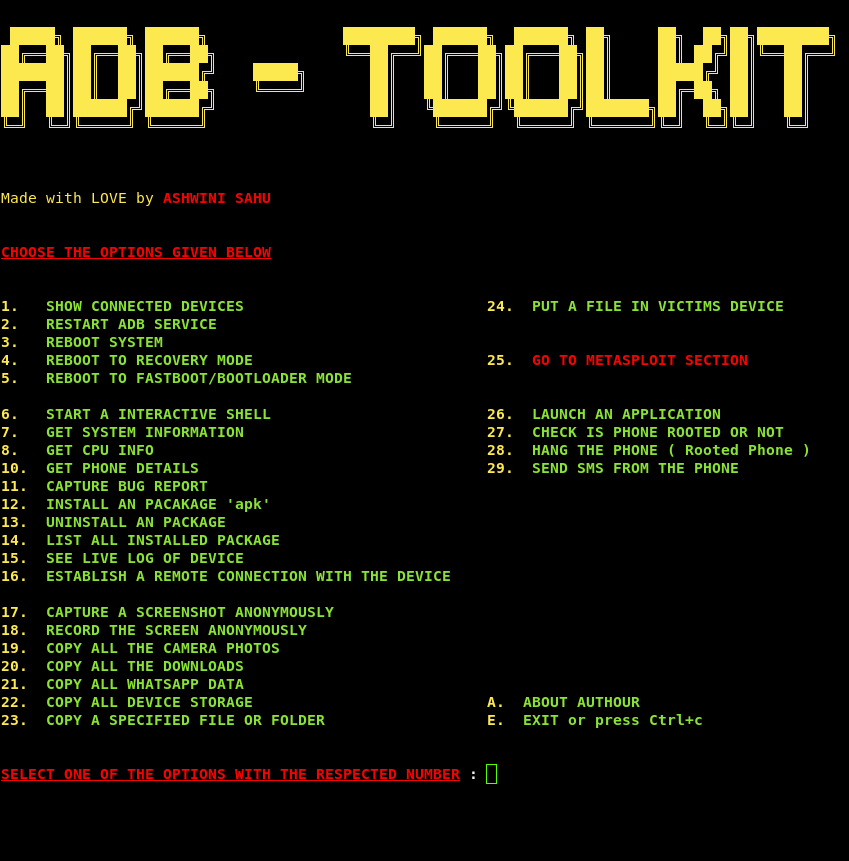
ADB-Toolkit
 ashwin990/adb-toolkit
ADB-Toolkit V2 for easy ADB tricks with many perks in all one. ENJOY!
android-securityexploit-frameworksinformation-gathering+3
2.0k
ashwin990/adb-toolkitADB-Toolkit V2 for easy ADB tricks with many perks in all one. ENJOY!

 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 firerpa/lamda
Android Full-Stack Device Control Platform: WebRTC/H.264 remote desktop, UI/OCR/image-matching automation, one-click MITM, built-in Frida,…
 redhuntlabs/redhunt-os
Virtual Machine for Adversary Emulation and Threat Hunting
 vp777/windows-kernel-exploitation
Techniques and tools for Windows kernel exploitation, covering pool overflow exploitation, segment heap metadata abuse, and debugging scripts for…
 d4vinci/pastejacker
Hacking systems with the automation of PasteJacking attacks.
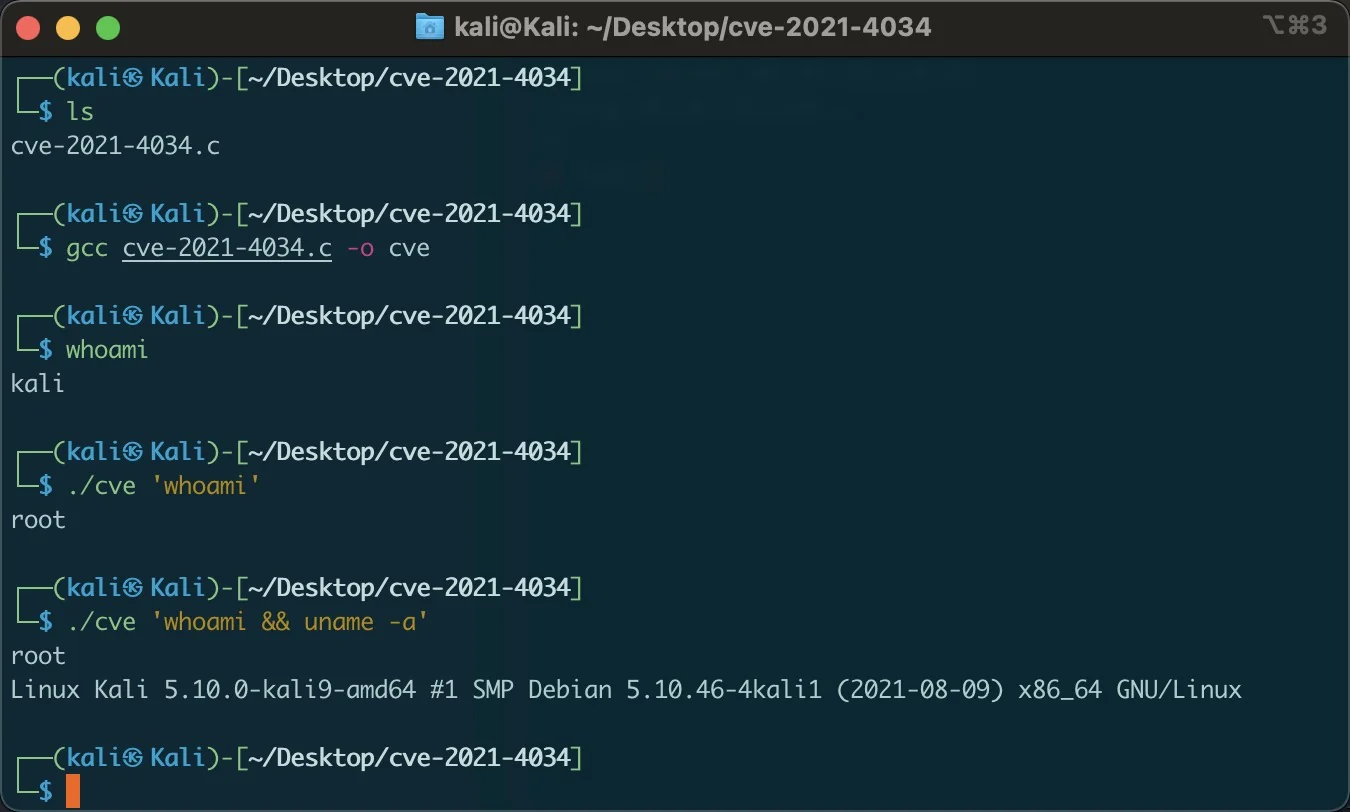 zhzyker/cve-2021-4034
polkit pkexec Local Privilege Vulnerability to Add custom commands
 quyicheng03-boop/xiaomi15-dada-cve-2026-64560
Device-bound CVE-2026-64560 adaptation for Xiaomi 15 dada OS4.0.0.8
 darksh3llgr/autoscan
Automated Scanning, Pentesting , Exploiting and Reporting
 thejoyofhacking/berdav-cve-2021-4034
Exploit for CVE-2021-4034 (PwnKit) that provides a root shell via polkit pkexec. Includes a dry-run mode to test vulnerability and a one-liner script…
 w3llr00t3d/cve-2026-31431-poc
LPE exploit for CVE-2026-31431 CopyFail. Compatible with Python 3.9.
 joaoaugustom/wordpress_backup_migration-rce_unauthenticated
This exploit is based on CVE-2023-6553 and was built upon the original exploit by Chocapik, it was added that a direct reverse shell can be obtained.
 rakhithjk/cve-2021-4034-new
Exploit for CVE-2021-4034 (polkit pkexec) that provides a root shell. Includes build instructions and references the original advisory.
 pengalaman-1t/cve-2021-4034
Exploit for CVE-2021-4034 (PwnKit) that provides a root shell via polkit pkexec vulnerability. Includes source code and build instructions.
 phvilasboas/cve-2021-4034
Exploit for CVE-2021-4034, a local privilege escalation in polkit's pkexec, providing a root shell via a shared library and GCONV_PATH manipulation.
 cinnamon1212/modified-cve-2020-10915-msfmodule
THIS IS NOT AN ORIGINAL EXPLOIT. THIS IS AN AUDITED VERSION FOR A THM BOX
