

PyStegosploit
 charmve/pystegosploit
PoC - Exploit Delivery via Steganography and Polyglots, CVE-2014-0282
educationexploit-frameworkspapers-research+5
542 years ago
charmve/pystegosploitPoC - Exploit Delivery via Steganography and Polyglots, CVE-2014-0282
 ruped24/killchain
A unified console to perform the "kill chain" stages of attacks.
 stationedk-06/darksword_analysis
Static analysis of the DarkSword iOS WebKit exploit chain — delivery, staging, and CVE breakdown (CVE-2025-31277, CVE-2025-43529)
 cxyofficial/x200-cve-2026-43499
Exploit tool targeting CVE-2026-43499 with automated payload delivery and vulnerability verification for penetration testing engagements.
 kaleth4/cve-2026-4747-
Remote kernel exploit for FreeBSD CVE-2026-4747, leveraging a stack buffer overflow in kgssapi.ko to achieve RCE with a reverse shell. Includes…
 huynambka/cve-2026-26114-poc
Proof-of-concept exploit for CVE-2026-26114, a remote code execution vulnerability in Microsoft SharePoint, with a Python PoC and Metasploit module…
 b3mb4m/shellsploit-framework
Framework for generating shellcode and exploit payloads, designed for penetration testing and security research to automate payload creation and…
 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool
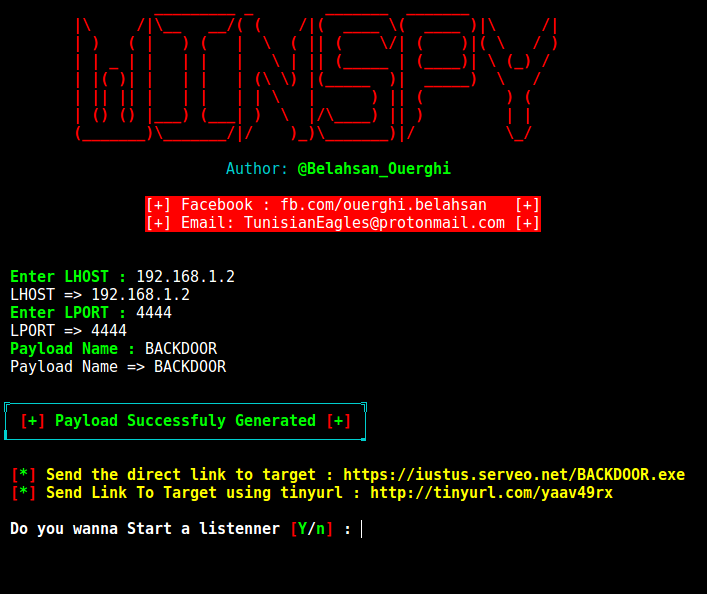 cyb0r9/winspy
Generates Windows reverse shell backdoors with automatic IP poisoning, leveraging Metasploit for payload creation and Apache for delivery in…