
CVE-2019-0708-EXP-MSF-
 qing-root/cve-2019-0708-exp-msf-
CVE-2019-0708-EXP(MSF) Vulnerability exploit program for cve-2019-0708
exploitationexploit-frameworkspenetration-testing+3
11
qing-root/cve-2019-0708-exp-msf-CVE-2019-0708-EXP(MSF) Vulnerability exploit program for cve-2019-0708
 justakazh/sicat
Multi-source vulnerability and exploit aggregator with auto-discovery via Nmap and Wappalyzer, searching Exploit-DB, NVD, CVE.org, GitHub, Nuclei,…
 emmmmllll/copy-fail-zig
Zig implementation of the Copy Fail Linux LPE (CVE-2026-31431) providing a standalone binary to exploit the vulnerability for security research and…
 mauricelambert/cve-2022-47986
CVE-2022-47986: Python, Ruby, NMAP and Metasploit modules to exploit the vulnerability.
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 bhassani/eternalbluec
EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…
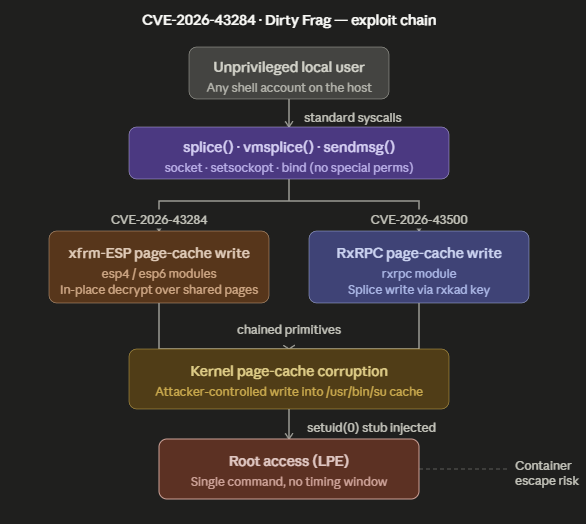 lucaspdiniz/cve-2026-43284
Dirty Frag - kernel Linux critical Vulnerability
 ashutoshrohilla/cve-2021-4034
Exploit for CVE-2021-4034, a local privilege escalation vulnerability in polkit's pkexec, allowing unprivileged users to gain root access.
 taroballzchen/cve-2021-36260-metasploit
the metasploit script(POC) about CVE-2021-36260
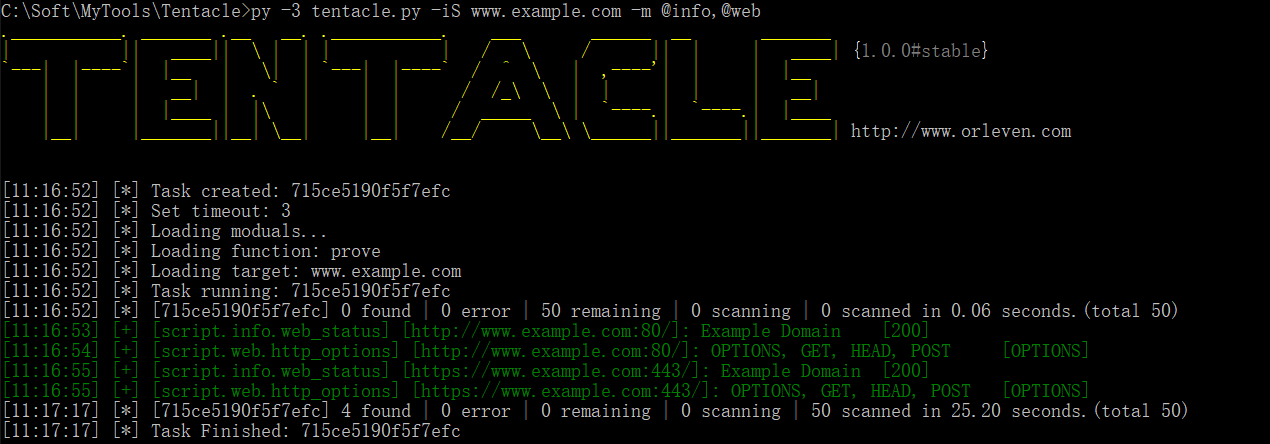 orleven/tentacle
Tentacle is a POC vulnerability verification and exploit framework. It supports free extension of exploits and uses POC scripts. It supports calls to…
 ireshchaminda1/android-privilege-escalation-remote-access-vulnerability-cve-2015-1805
AndroRAT is a capability that can be used to inject a root exploit as a silent installation to perform a malicious task on the device. This AndroRAT…
 abdurahmon3236/cve-2024-6366
Metasploit exploit module for CVE-2024-6366, an unauthenticated file upload remote code execution in WordPress User Profile Builder before 3.11.8,…
 dannyendortest/ollama-consumer
Demo consumer for ollama v0.5.0 (vulnerable range for CVE-2024-12886) — endorctl scan target
 j4nn/cve-2020-0041
Local privilege escalation exploit for Android kernel vulnerability CVE-2020-0041, with portability across devices and kernel versions.
 bishopfox/cve-2021-35211
Python exploit for Serv-U SSH vulnerability (CVE-2021-35211) with multiple payload modes: stage, exec, and download-execute, enabling shellcode…
 jpmcb/pwnkit-go
Exploit for the PwnKit vulnerability, CVE-2021-4034, written in Go
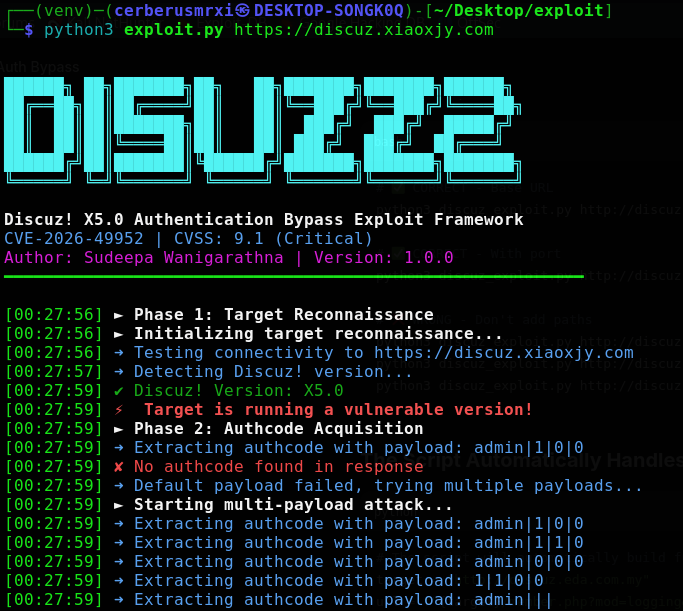 cerberusmrxi/discuz-x5.0-authentication-bypass-exploit-framework
Discuz! X5.0 Authentication Bypass Exploit Framework (CVE-2026-49952) - Critical vulnerability allowing unauthenticated database backup access via…
 kimocoder/eternalblue
Python implementation of the EternalBlue exploit (CVE-2017-0144) targeting SMBv1 vulnerability for remote code execution on Windows systems.