
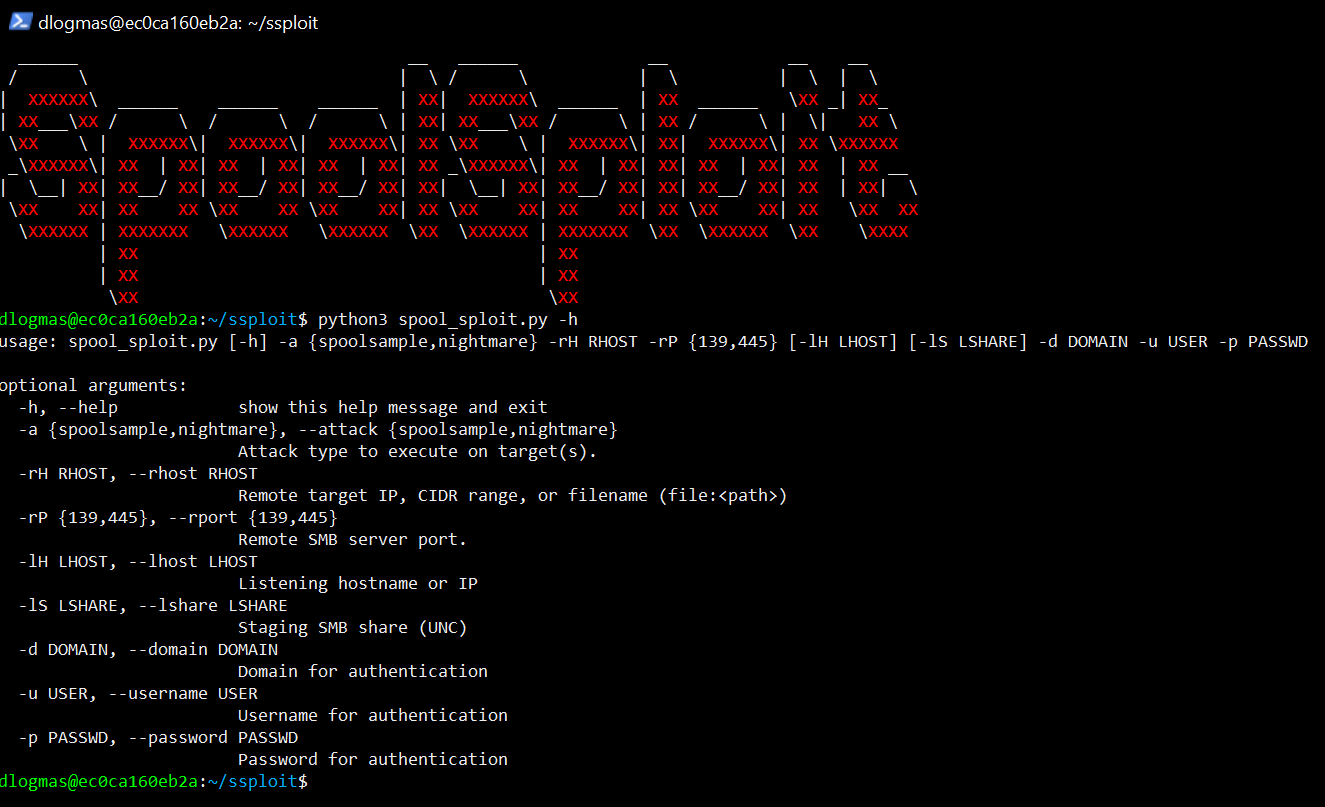
SpoolSploit
 beetlechunks/spoolsploit
A collection of Windows print spooler exploits containerized with other utilities for practical exploitation.
container-securityexploitationexploit-frameworks+4
550
beetlechunks/spoolsploitA collection of Windows print spooler exploits containerized with other utilities for practical exploitation.
 pensarai/apex
AI-powered offensive security testing using autonomous agents, directly in your terminal.
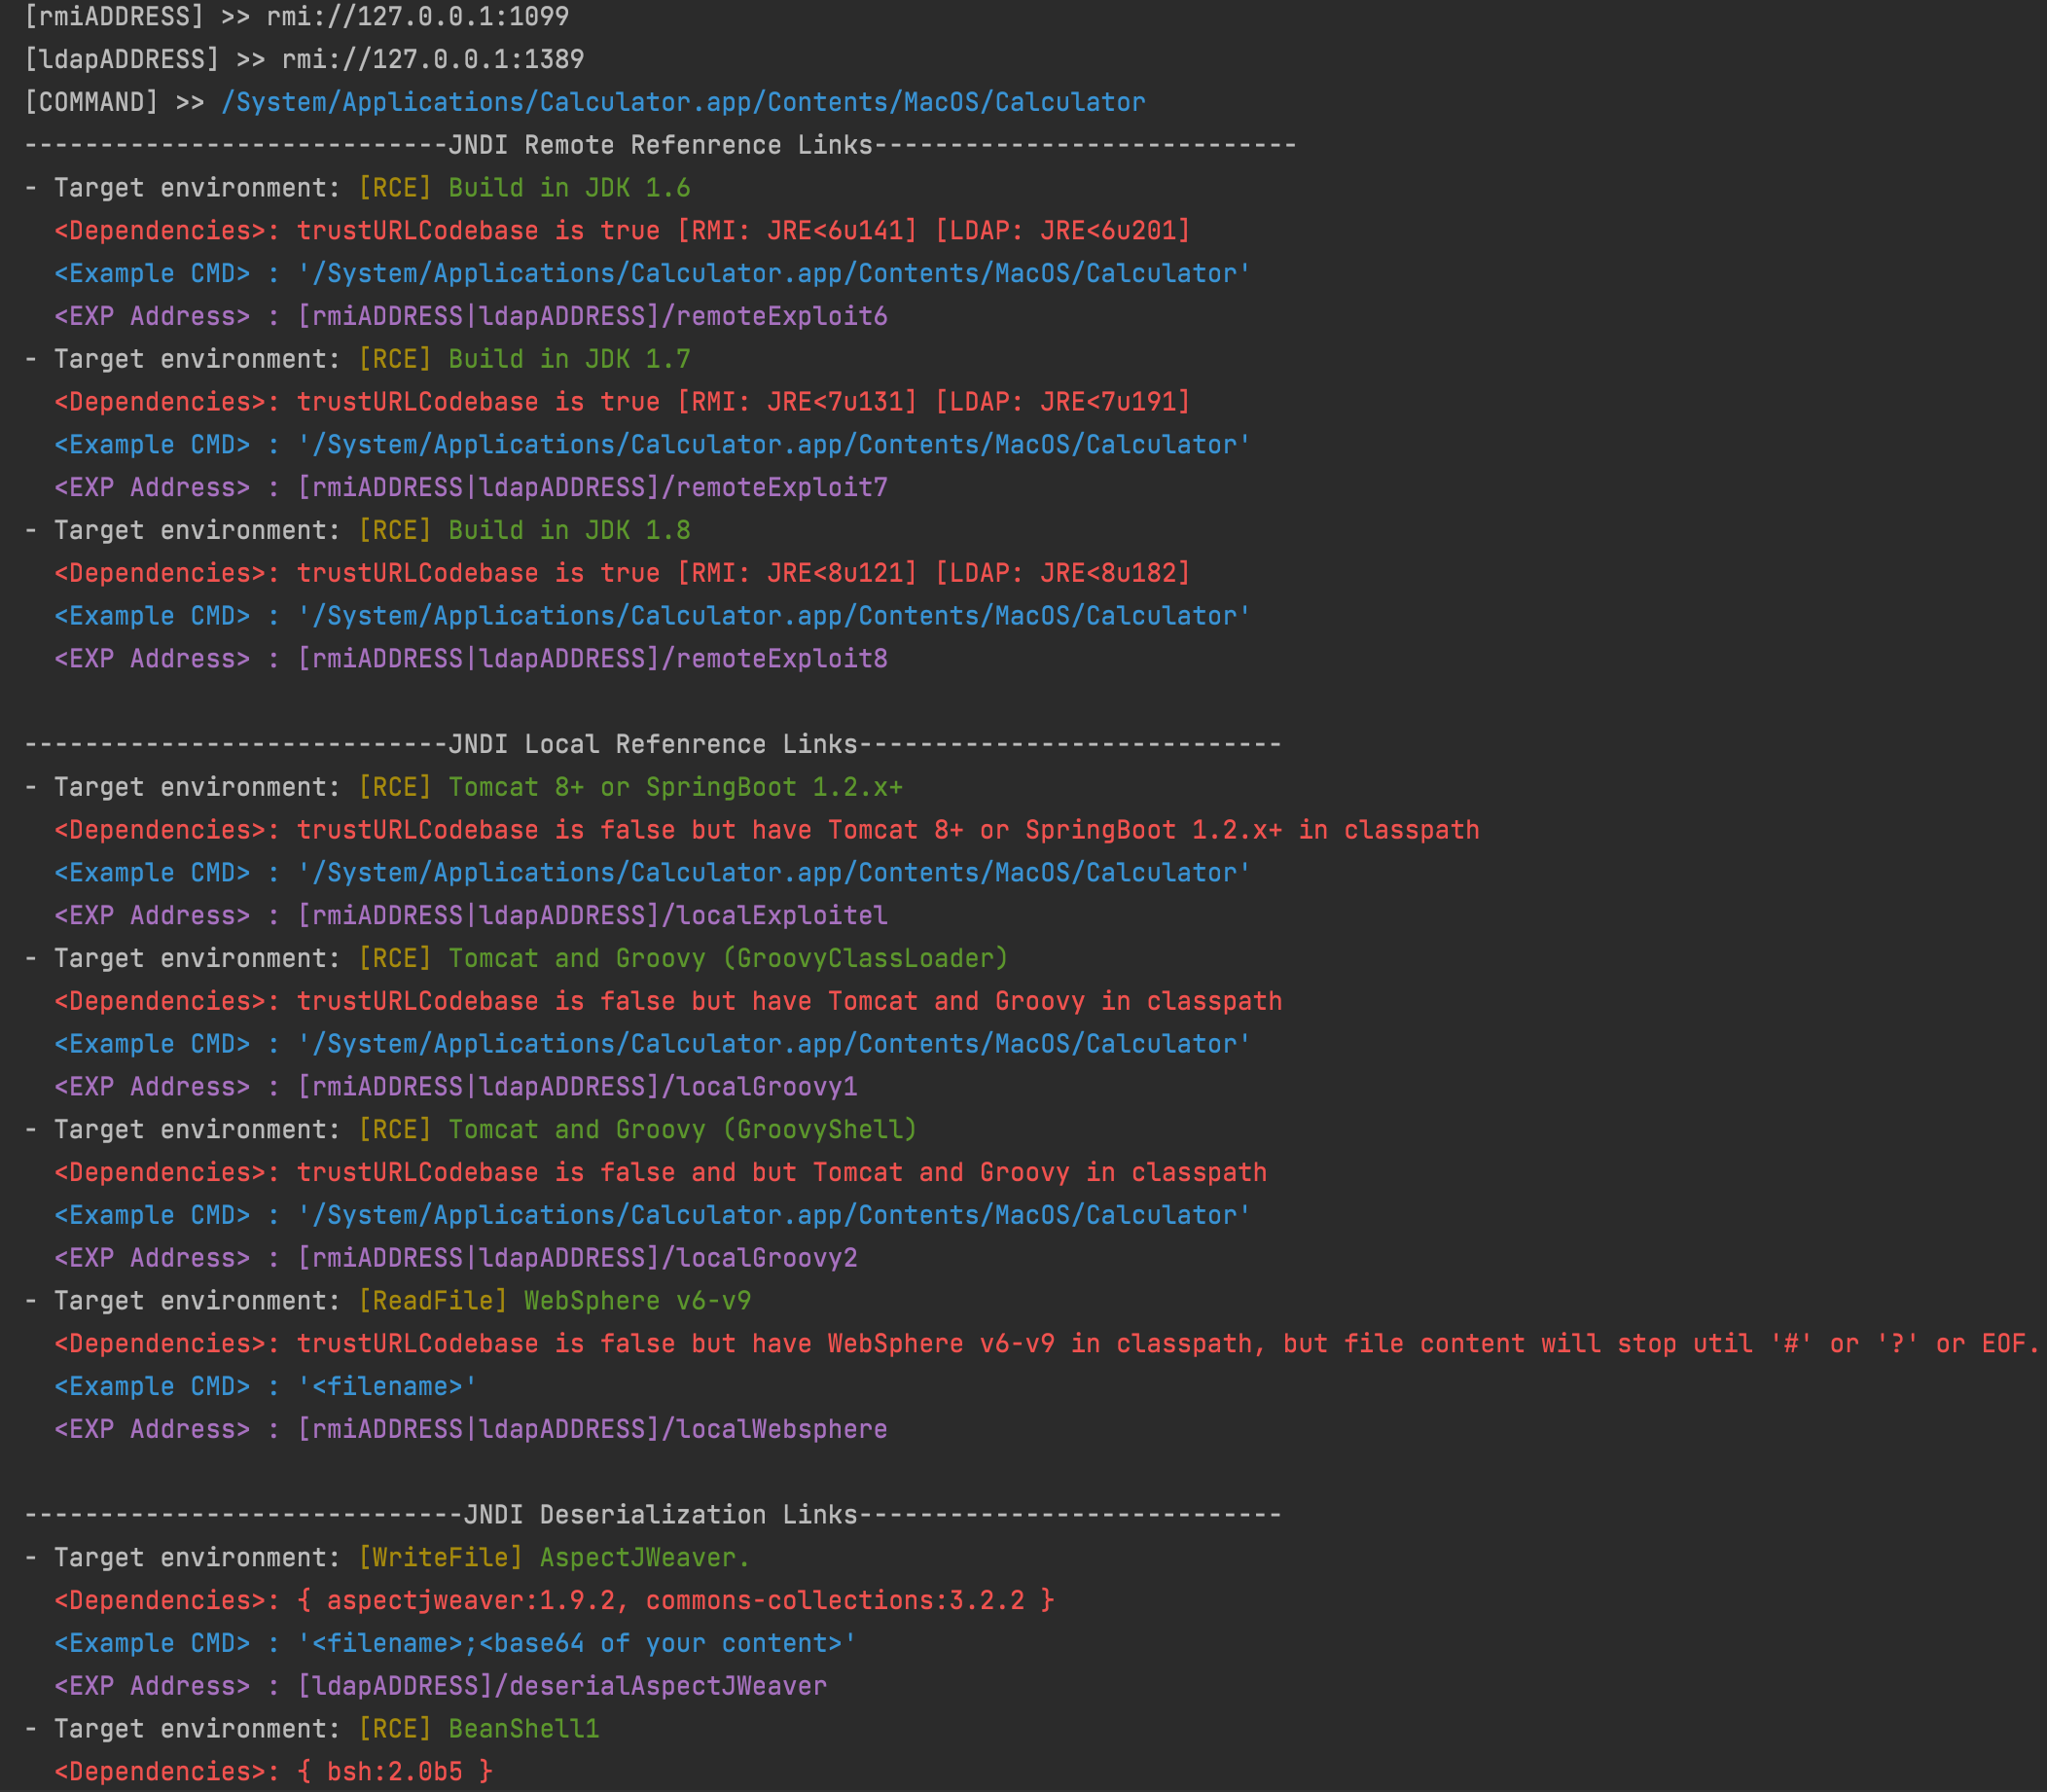 cckuailong/jndi-injection-exploit-plus
Generates workable JNDI injection links and deserialization payloads with 80+ gadgets, supporting RMI, LDAP, and HTTP servers for automated…
 ronin-rb/ronin
Ronin is a Free and Open Source Ruby Toolkit for Security Research and Development. Ronin also allows for the rapid development and distribution of…
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 nettitude/poshc2_old
Powershell C2 Server and Implants
 justakazh/sicat
Multi-source vulnerability and exploit aggregator with auto-discovery via Nmap and Wappalyzer, searching Exploit-DB, NVD, CVE.org, GitHub, Nuclei,…
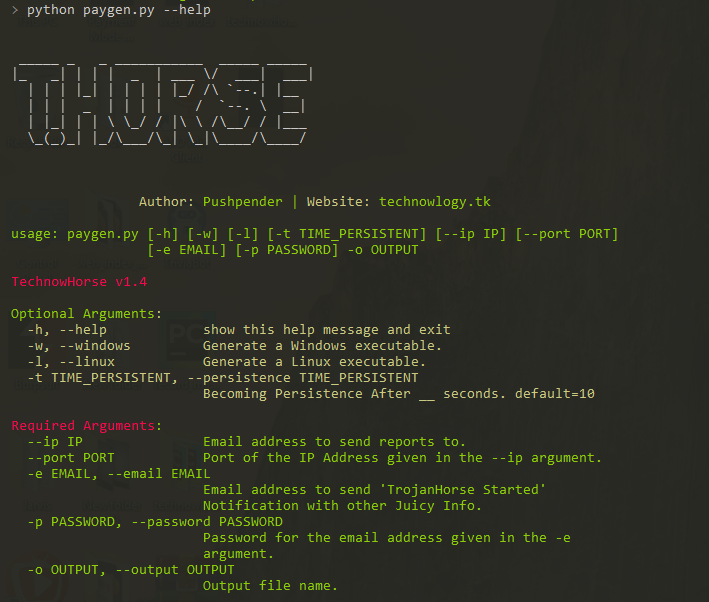 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
 arpsyndicate/puncia
Panthera(P.)uncia - Official CLI utility for Subdomain Center & Exploit Observer.
 bluscreenofjeff/malleable-c2-randomizer
A script to randomize Cobalt Strike Malleable C2 profiles and reduce the chances of flagging signature-based detection controls
 exploit-database/exploitdb
exploitdb // The official Exploit-Database repository
 orleven/tentacle
Tentacle is a POC vulnerability verification and exploit framework. It supports free extension of exploits and uses POC scripts. It supports calls to…
 artkond/cisco-rce
CVE-2017-3881 Cisco Catalyst Remote Code Execution PoC
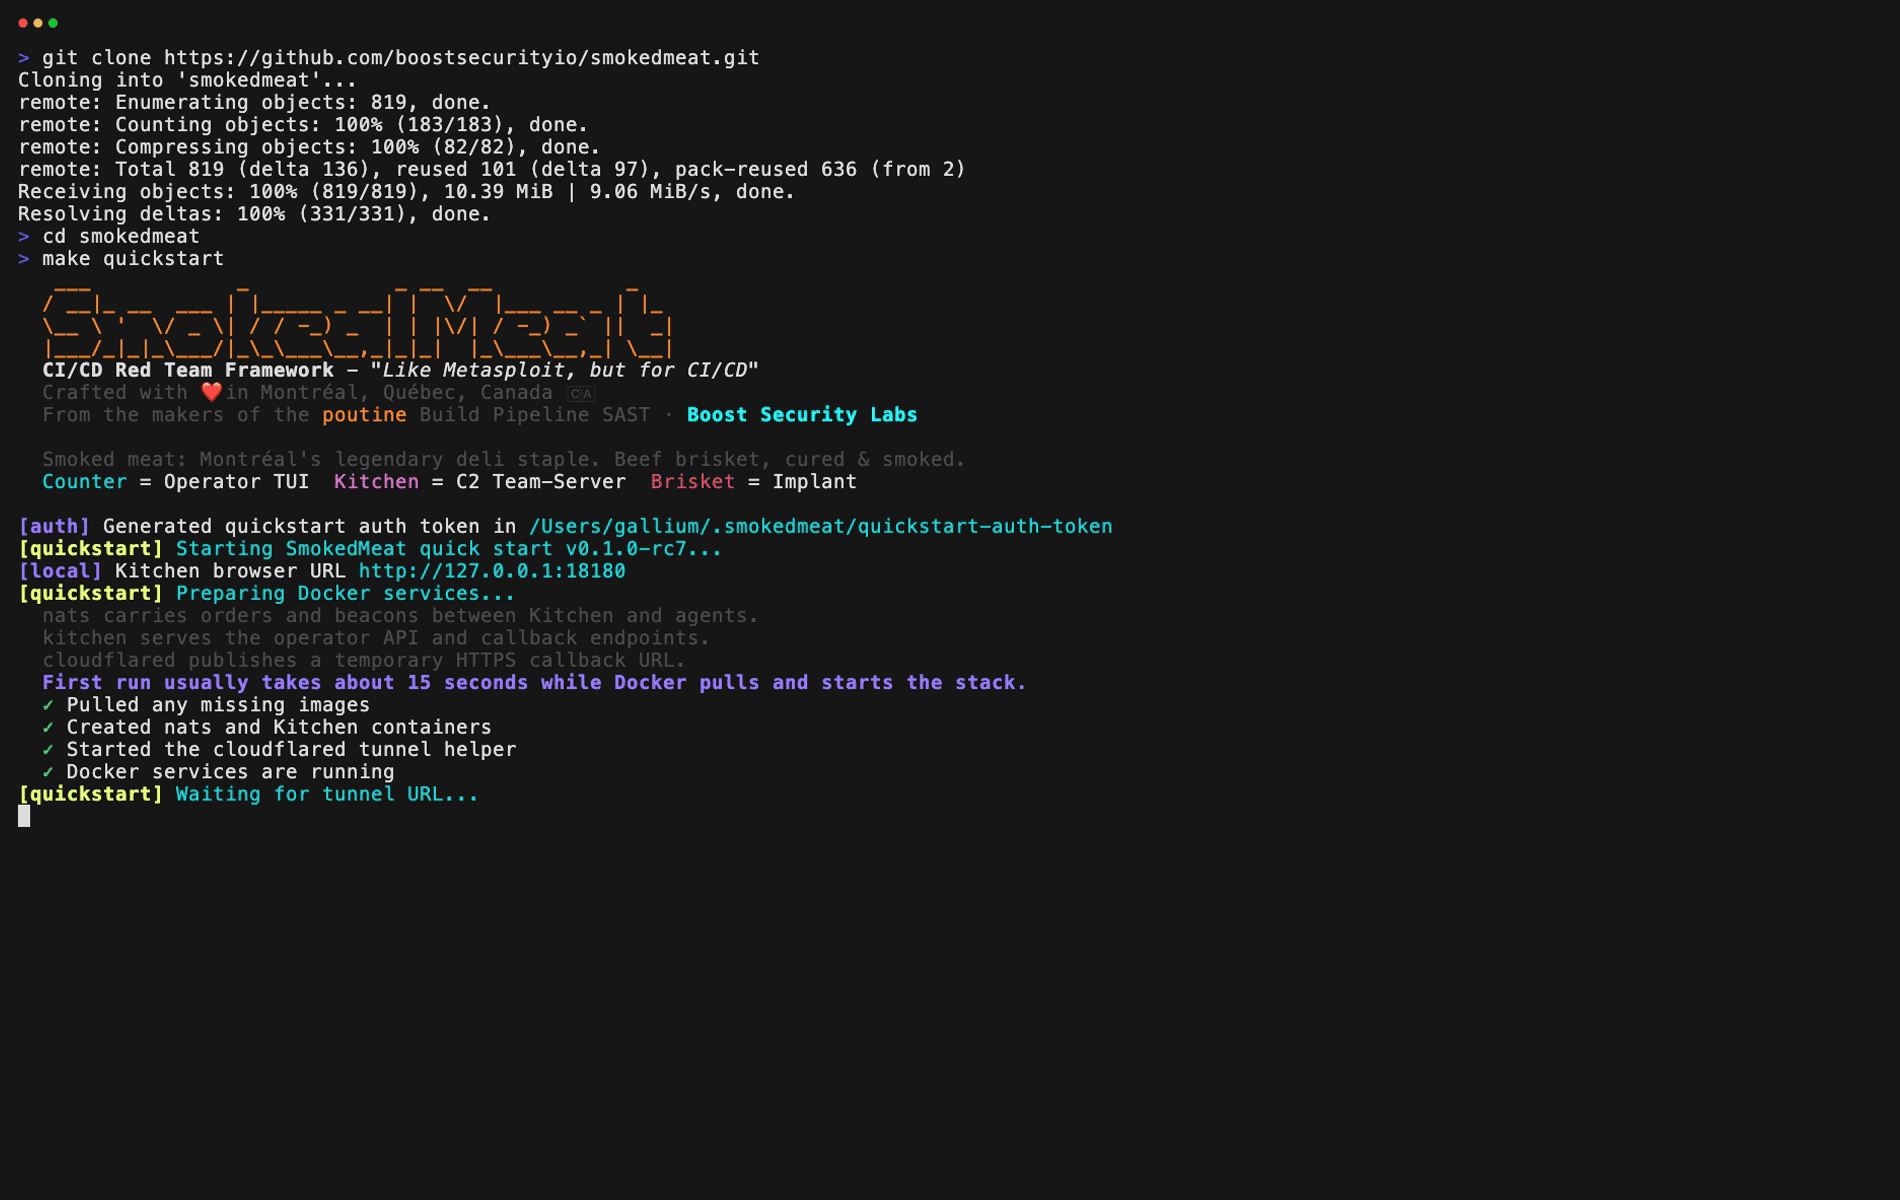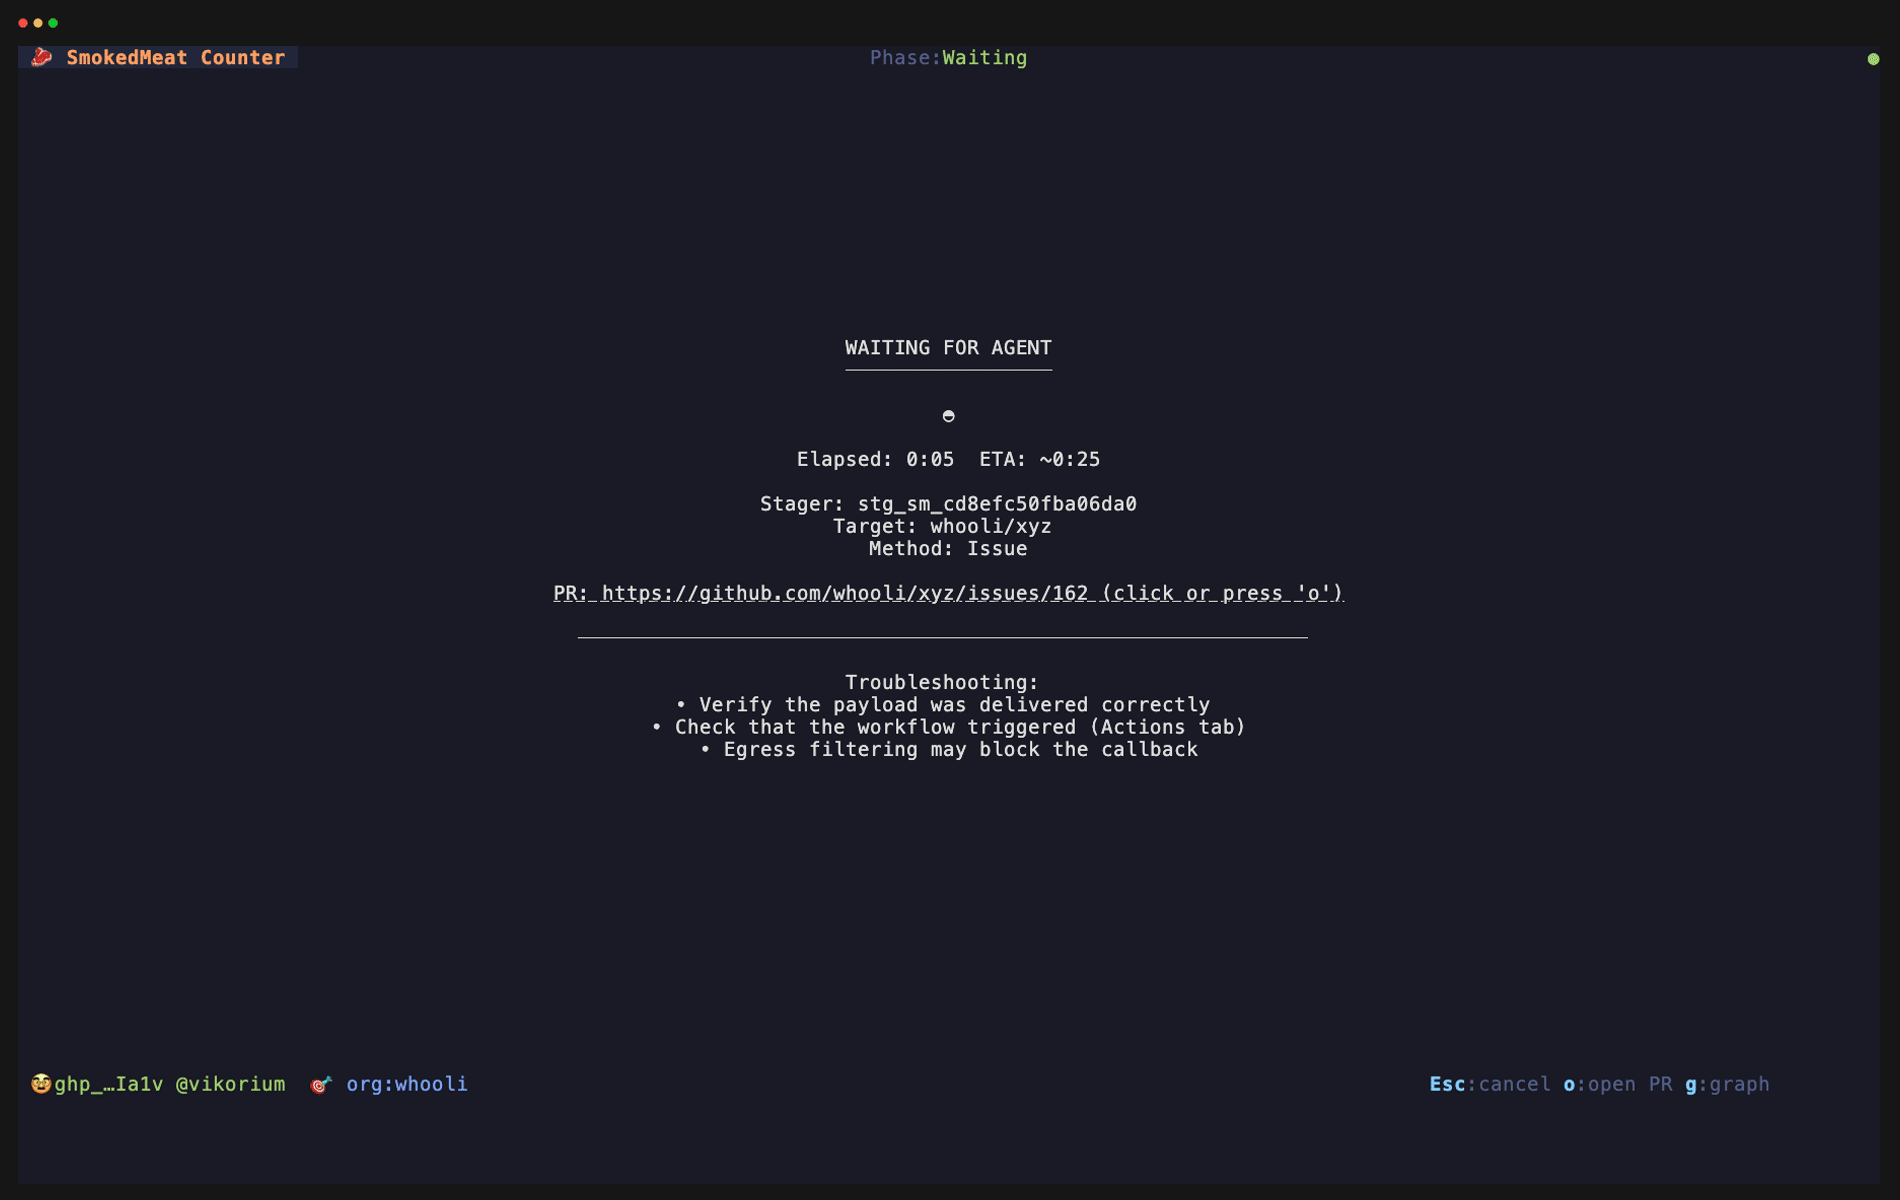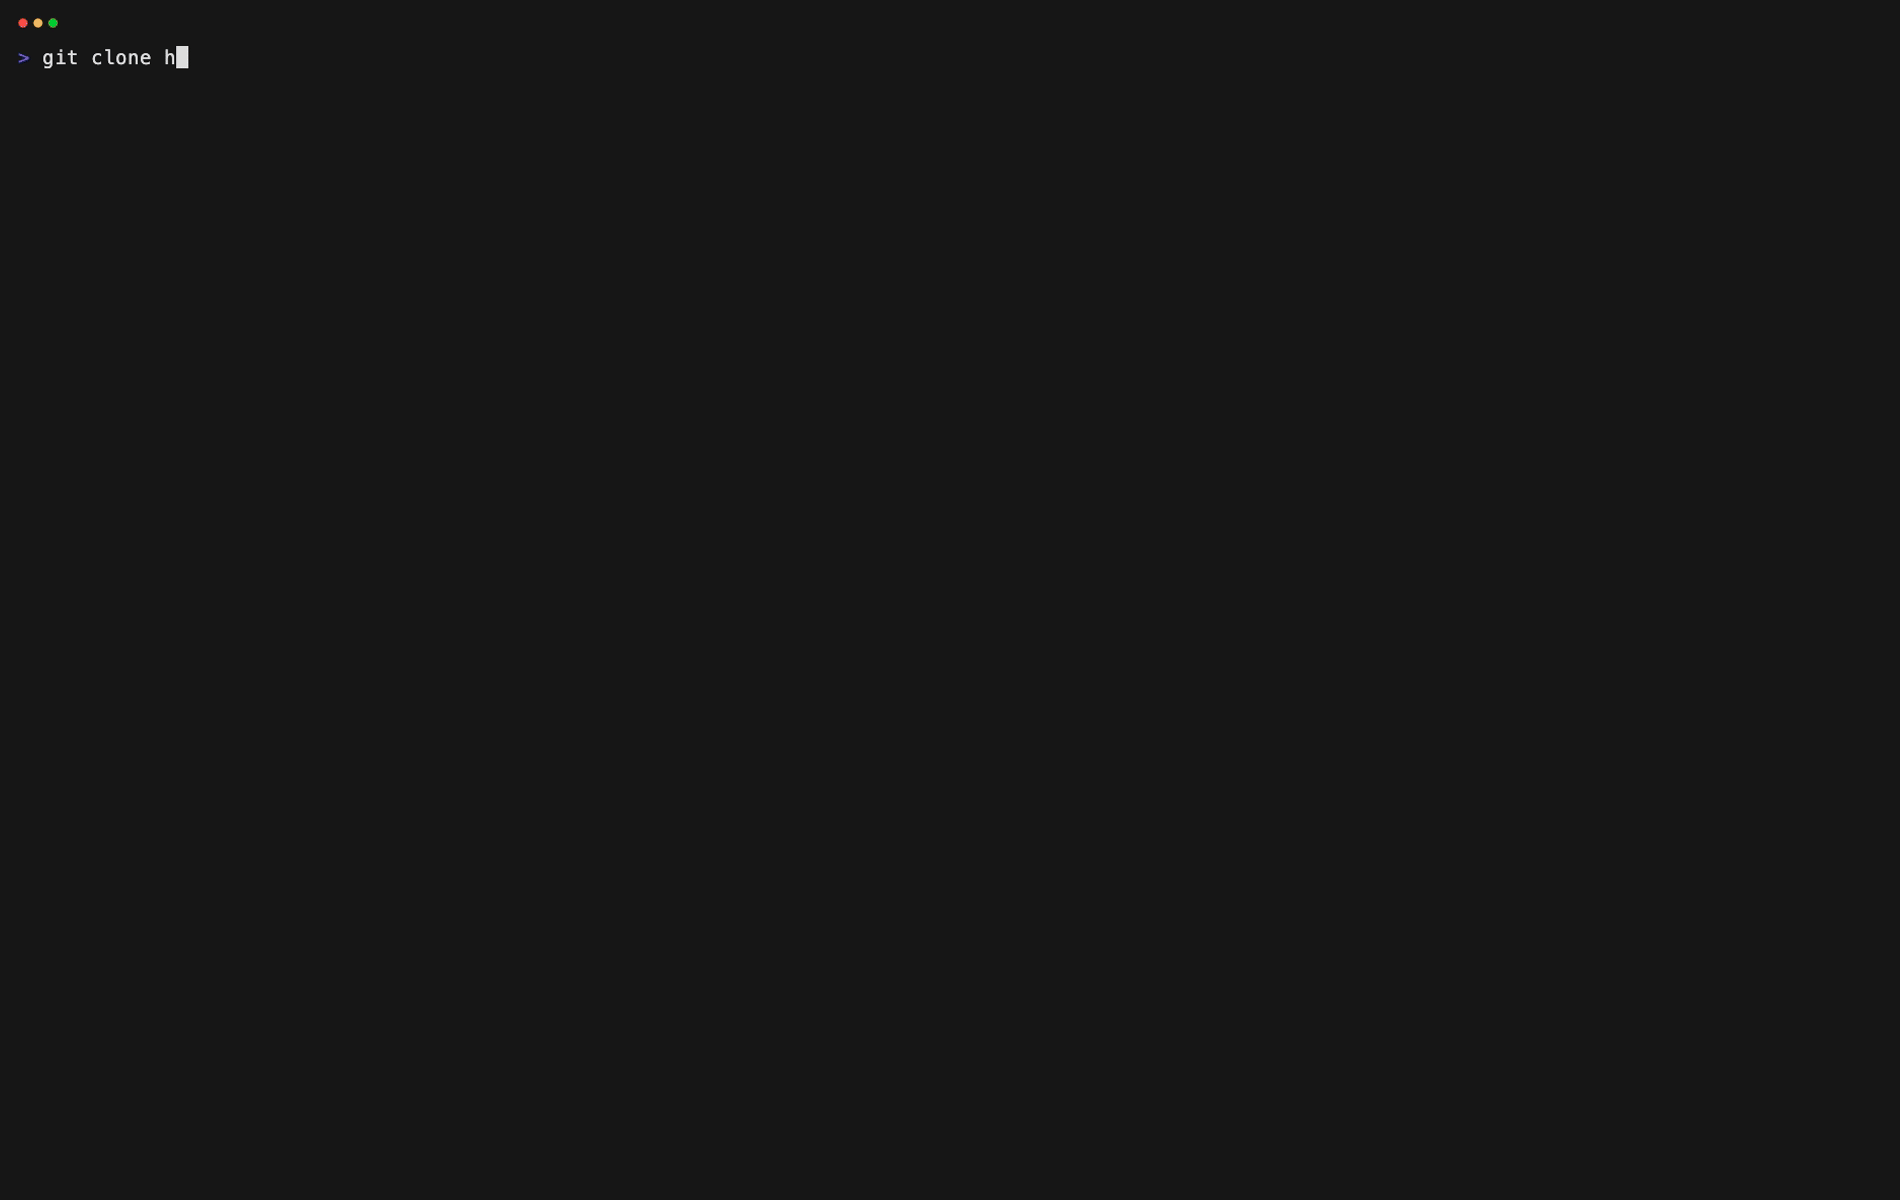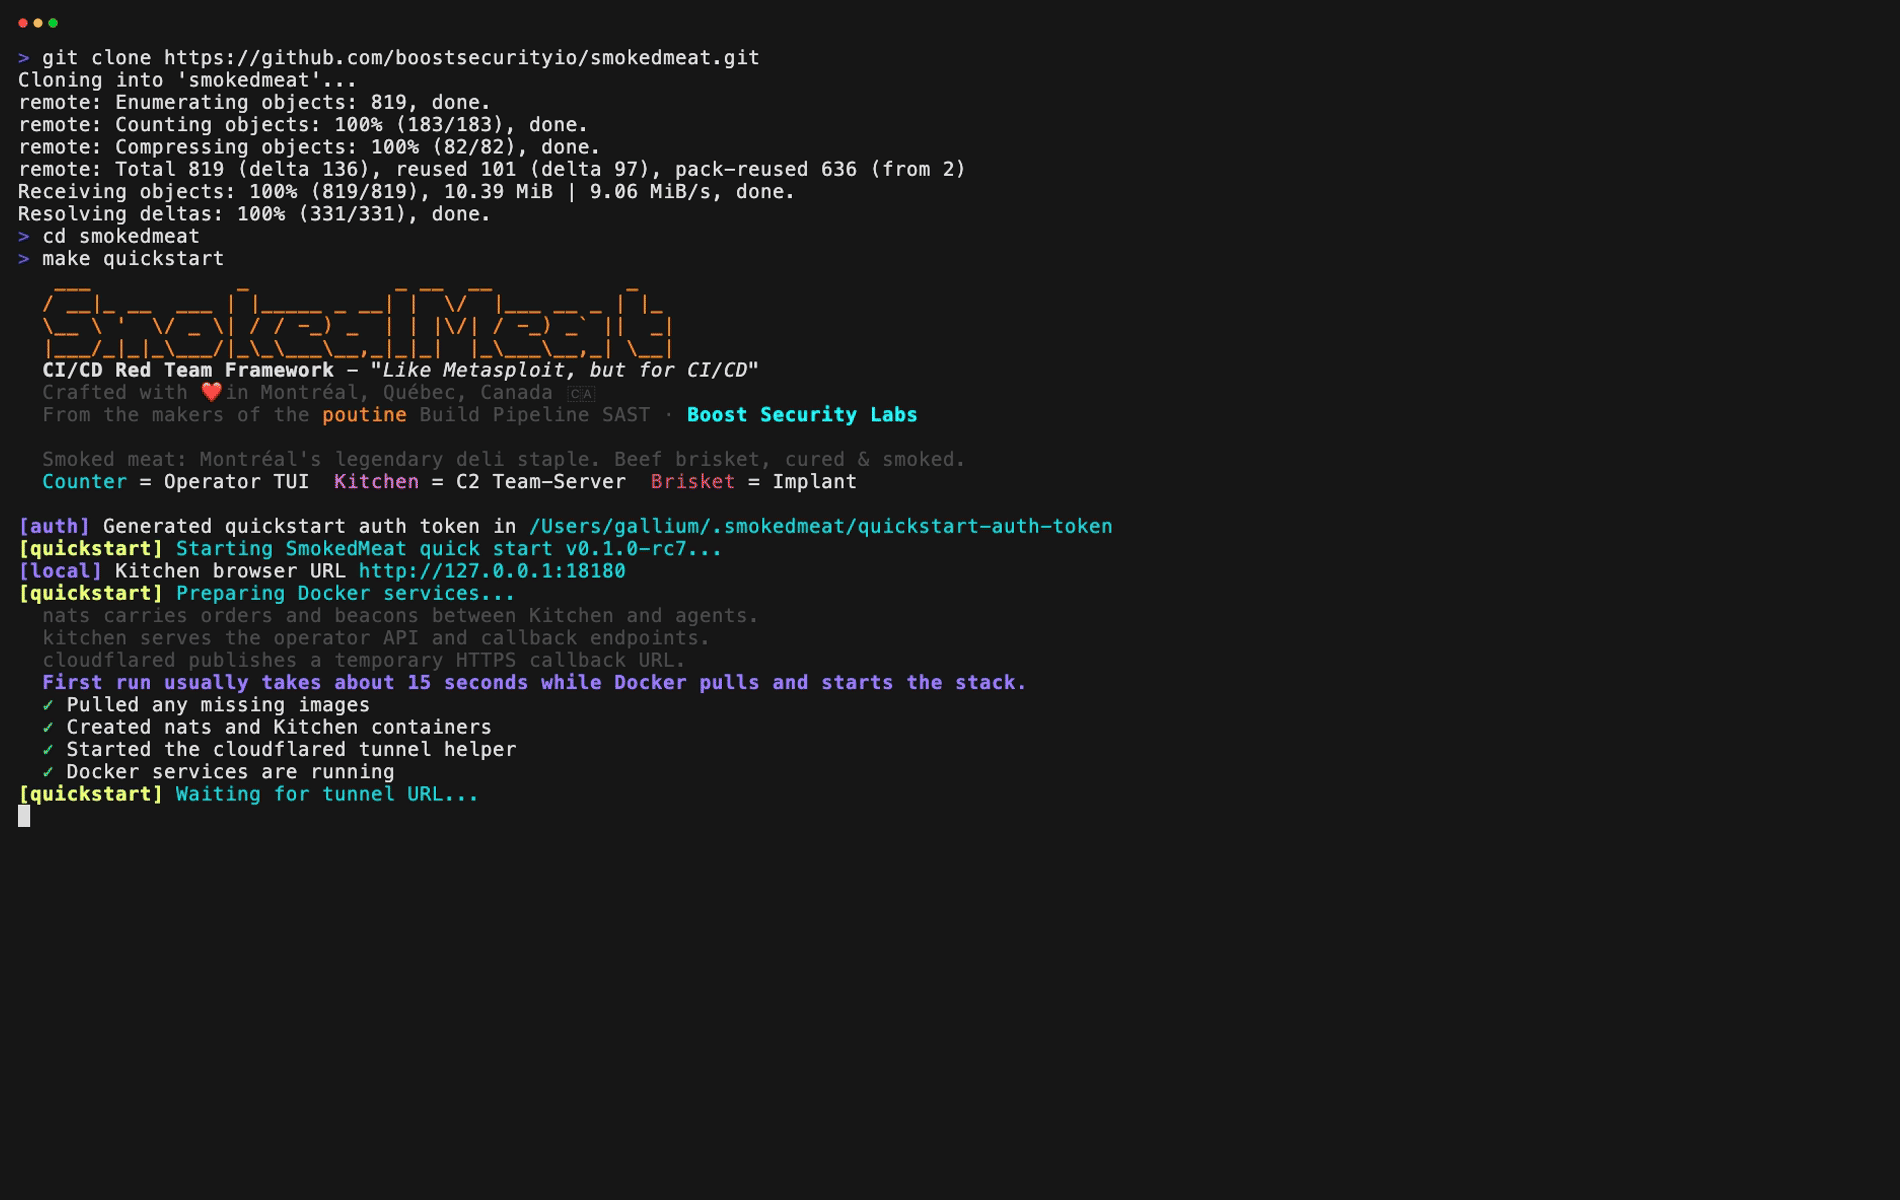 boostsecurityio/smokedmeat
A CI/CD Red Team Framework for demonstrating Build Pipeline security risks.
 mythicagents/medusa
Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
 0ca/boxpwnr
A modular framework for benchmarking LLMs and agentic strategies on security challenges across HackTheBox, TryHackMe, PortSwigger Labs, Cybench,…
 gl4ssesbo1/nebula
Nebula is a cloud C2 Framework, which at the moment offers reconnaissance, enumeration, exploitation, post exploitation on AWS, but still working to…