

Cooolis-ms
 rvn0xsy/cooolis-ms
Cooolis-ms是一个包含了Metasploit Payload Loader、Cobalt Strike External C2 Loader、Reflective DLL injection的代码执行工具,它的定位在于能够在静态查杀上规避一些我们将要执行且含有特征的代码,帮助红队人员更方便快…
command-and-controlexploit-frameworksids-ips-evasion+7
925
rvn0xsy/cooolis-msCooolis-ms是一个包含了Metasploit Payload Loader、Cobalt Strike External C2 Loader、Reflective DLL injection的代码执行工具,它的定位在于能够在静态查杀上规避一些我们将要执行且含有特征的代码,帮助红队人员更方便快…
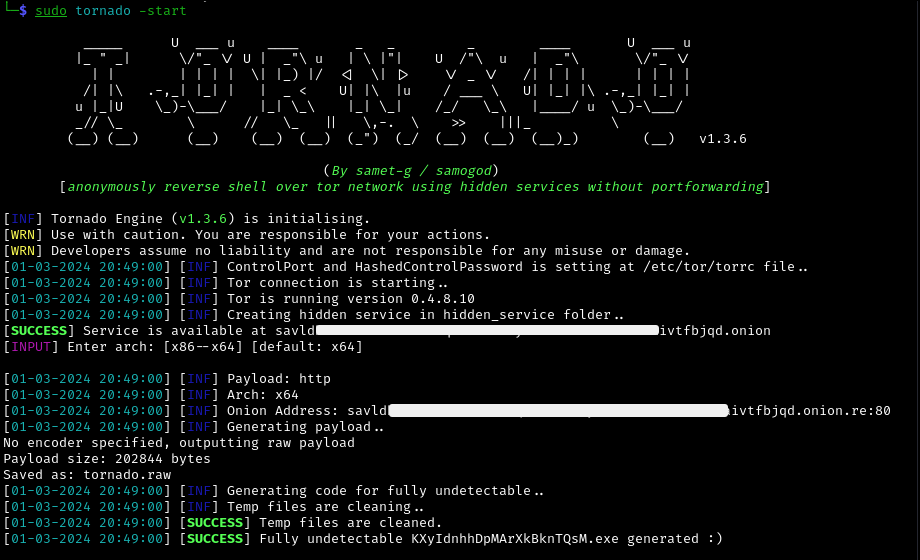 samogod/tornado
Anonymously Reverse Shell over Tor Network using Hidden services without Portforwarding.
 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
 bluscreenofjeff/malleable-c2-randomizer
A script to randomize Cobalt Strike Malleable C2 profiles and reduce the chances of flagging signature-based detection controls
 mythicagents/medusa
Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
 b4rtik/redpeanut
RedPeanut is a small RAT developed in .Net Core 2 and its agent in .Net 3.5 / 4.0.
 allevon412/teamsimplant
Stealthy DLL proxying implant for Microsoft Teams that injects AES-encrypted shellcode via unhooking techniques, providing persistent backdoor access…
 ryhanson/externalc2
A library for integrating communication channels with the Cobalt Strike External C2 server
 xorrior/raven
CobaltStrike External C2 for Websockets
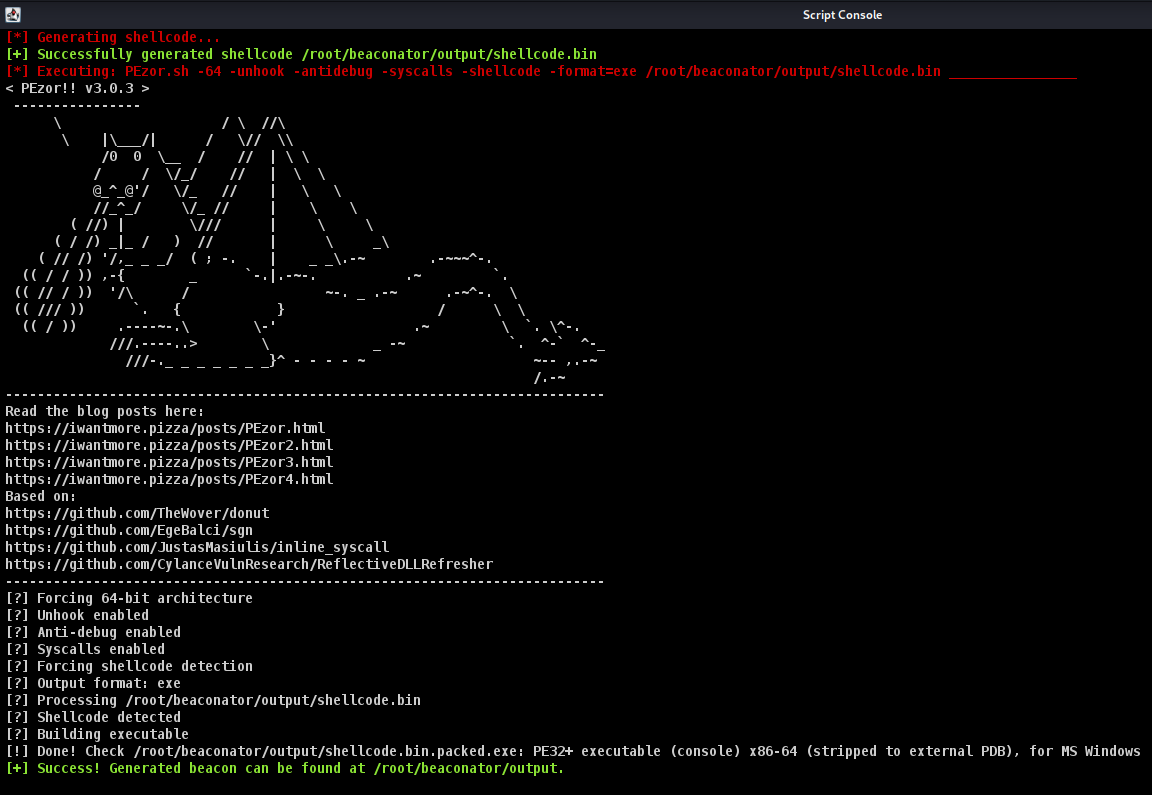 capt-meelo/beaconator
A beacon generator using Cobalt Strike and a variety of tools.
 flangvik/cobaltbus
Cobalt Strike External C2 Integration With Azure Servicebus, C2 traffic via Azure Servicebus
 jephthai/evilvm
Forth-based compiler deployed as position-independent x86_64 shellcode, providing a remote code execution agent with interactive REPL over TCP, HTTP,…
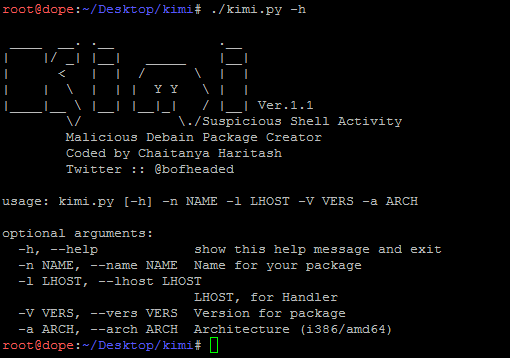 chaitanyaharitash/kimi
Script to generate malicious debian packages (debain trojans).
 1135/1135-cobaltstrike-toolkit
about CobaltStrike
 outflanknl/external_c2
POC for Cobalt Strike external C2
 mythicagents/apfell
JavaScript for Automation (JXA) macOS agent
 licitrasimone/crystalsliver
Crystal Palace Evasion kit for Sliver
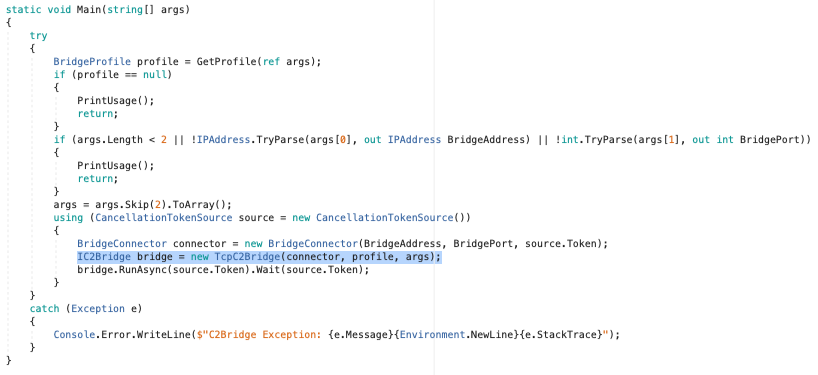 cobbr/c2bridge
C2Bridges allow developers to create new custom communication protocols and quickly utilize them within Covenant.