
Atomic-Red-Team-C2
ARTi-C2 is a post-exploitation framework used to execute Atomic Red Team test cases with rapid payload deployment and execution capabilities via…

ARTi-C2 is a post-exploitation framework used to execute Atomic Red Team test cases with rapid payload deployment and execution capabilities via…

PROJECT DELTA: SDN SECURITY EVALUATION FRAMEWORK

Python SQL injection framework

Cloud Exploit Framework

DropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…

Framework for exploiting local vulnerabilities

quick and dirty canbus h4xing framework

Modular framework for Windows UAC bypass attacks and mitigation, featuring DLL hijacking, fileless execution, and real-time monitoring to detect and…

EXPLIoT - Internet of Things Security Testing and Exploitation framework

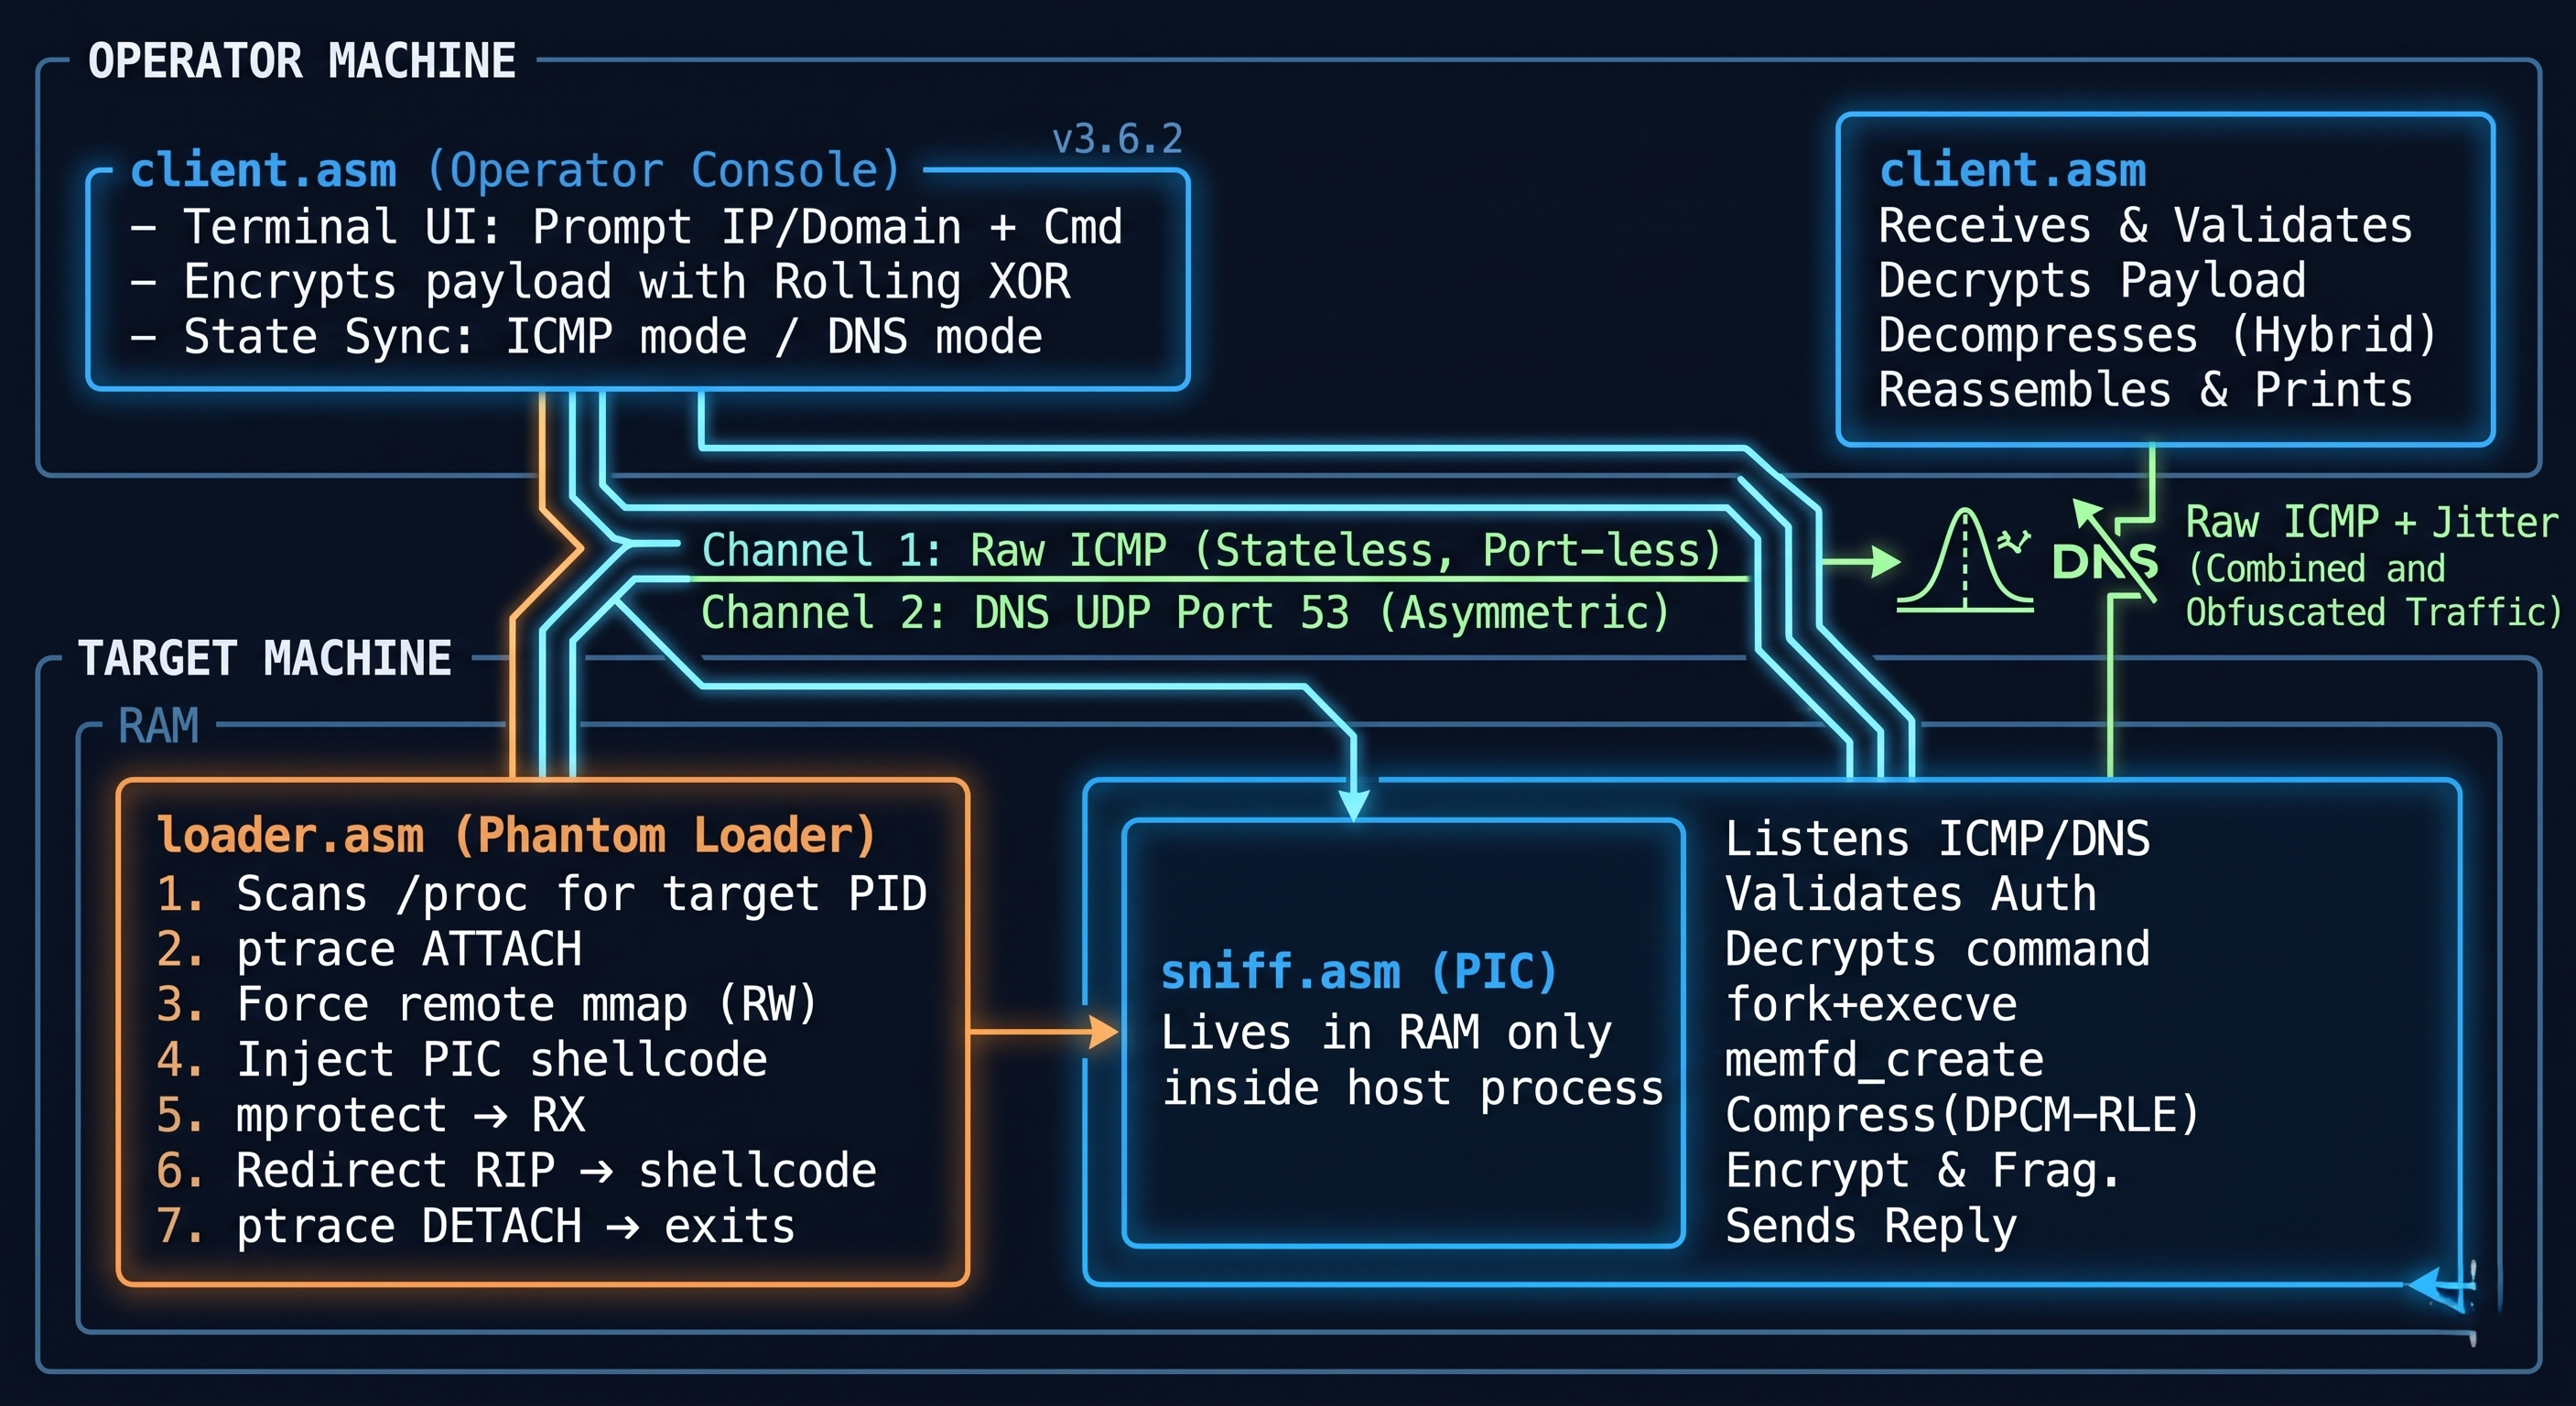
Fileless x64 Assembly C2 framework with dual-channel ICMP/DNS protocol pivoting, direct syscall execution, and ptrace-based process injection for…

Polymorphic C2 framework with graphical interface, automatic reconnection, payload generation, and integrated hacking tools for red team operations…

Multi-Thread Vulnerability Verify Framework

A collaborative web exploitation framework.

Modular framework to exploit UPS devices


Modular Python3 attack framework for automating exploitation of SIEM platforms (Splunk, Graylog, OSSIM, QRadar, McAfee) via credential theft, payload…

nginx CVE scanner + RCE exploit framework (CVE-2026-42945 + 16 others)

This is an implementation of the CVE-2020-0796 aka SMBGhost vulnerability, compatible with the Metasploit Framework