
Archived
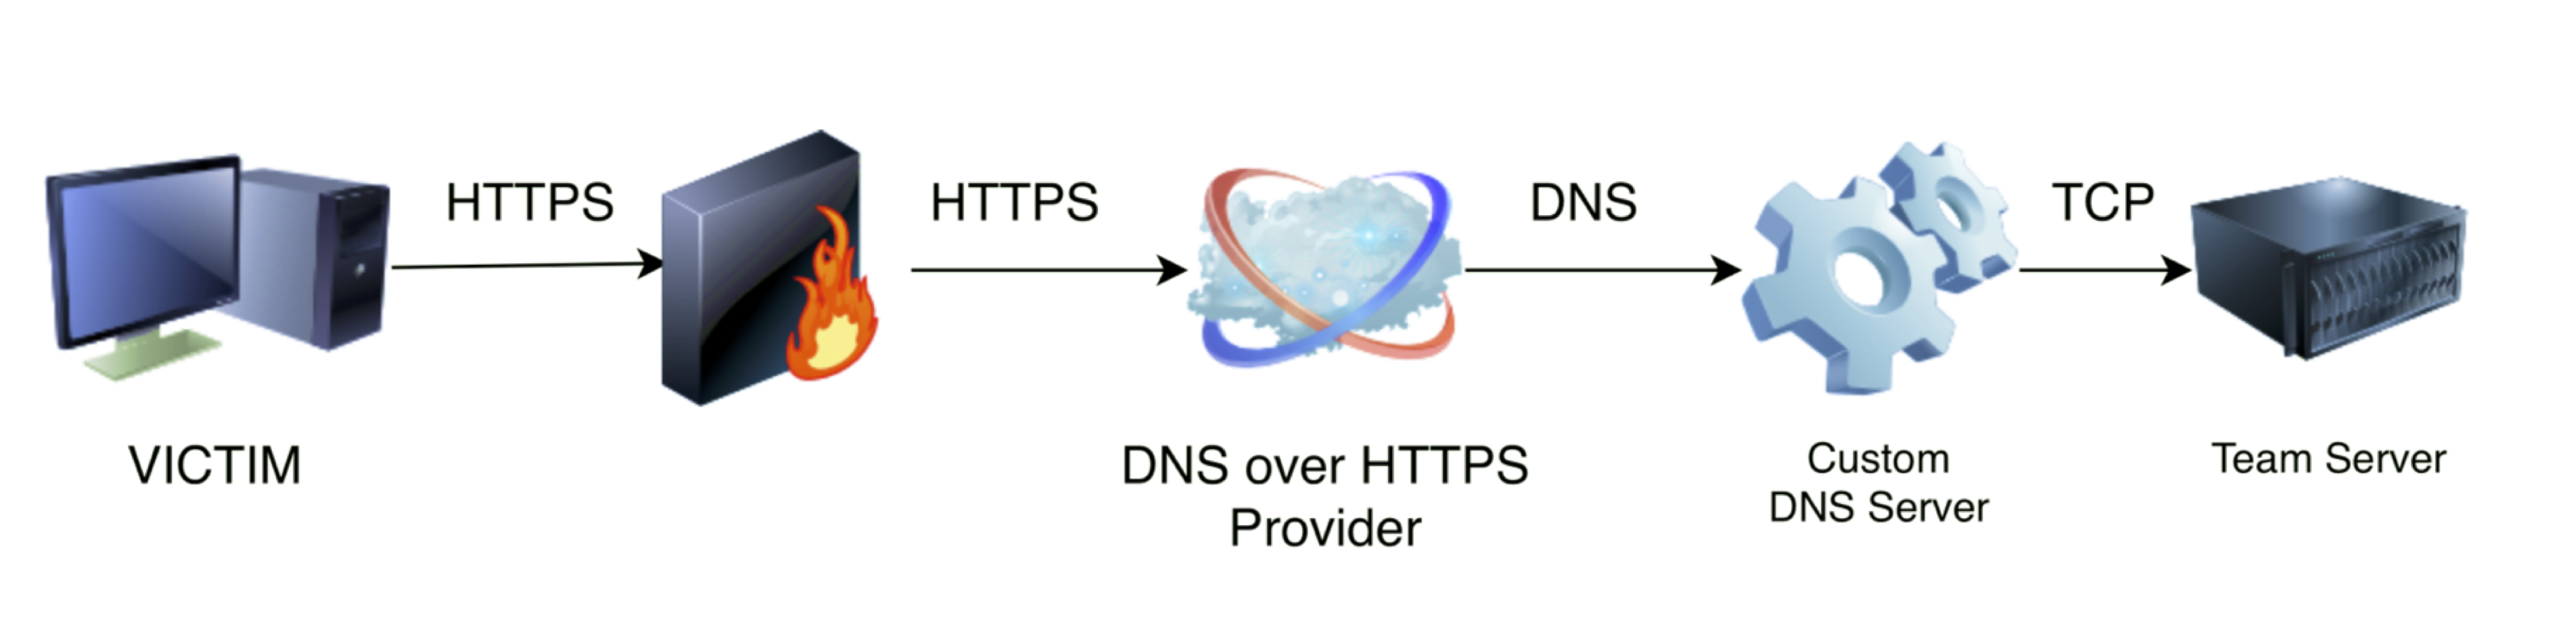
DoHC2
 spiderlabs/dohc2
DoHC2 allows the ExternalC2 library from Ryan Hanson (https://github.com/ryhanson/ExternalC2) to be leveraged for command and control (C2) via DNS…
command-and-controldns-analysisexploit-frameworks+3
 ne0nd0g/merlin
Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.
 jonstratton/selenium-node-takeover-kit
A collection of selenium tests that might aid it takeover of a selenium node
 ethicalhackinglabs/metasploitable2-exploitation-metasploit
Full Metasploit exploitation walkthrough against Metasploitable2 — vsftpd backdoor, Samba CVE-2007-2447, UnrealIRCd backdoor, Netcat exfiltration,…
 gushmazuko/metasploit_in_termux
Install and run Metasploit Framework 6 on Android via Termux with automated setup, payload generation (msfvenom), and full msfconsole access for…
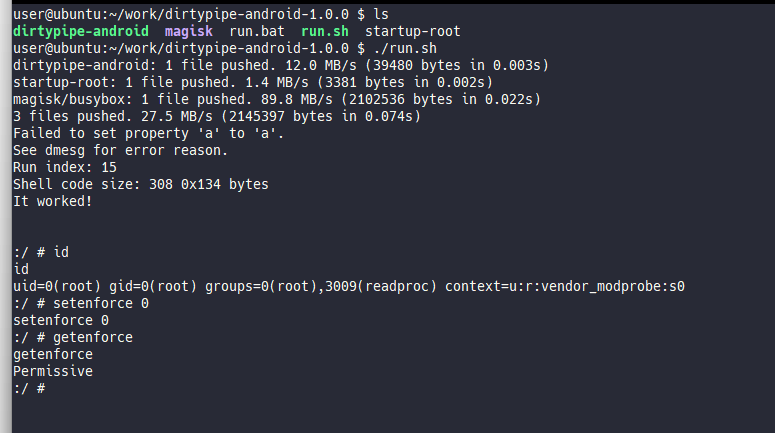 polygraphene/dirtypipe-android
Dirty Pipe root exploit for Android (Pixel 6)
 nettitude/scrounger
Mobile application testing toolkit
 jingmatrix/pixel-ksu-root
CVE research and exploits to help gaining roots for Pixel devices
 darmado/atomic-red-team-c2
ARTi-C2 is a post-exploitation framework used to execute Atomic Red Team test cases with rapid payload deployment and execution capabilities via…
 rasta-mouse/process-inject-kit
Port of Cobalt Strike's Process Inject Kit
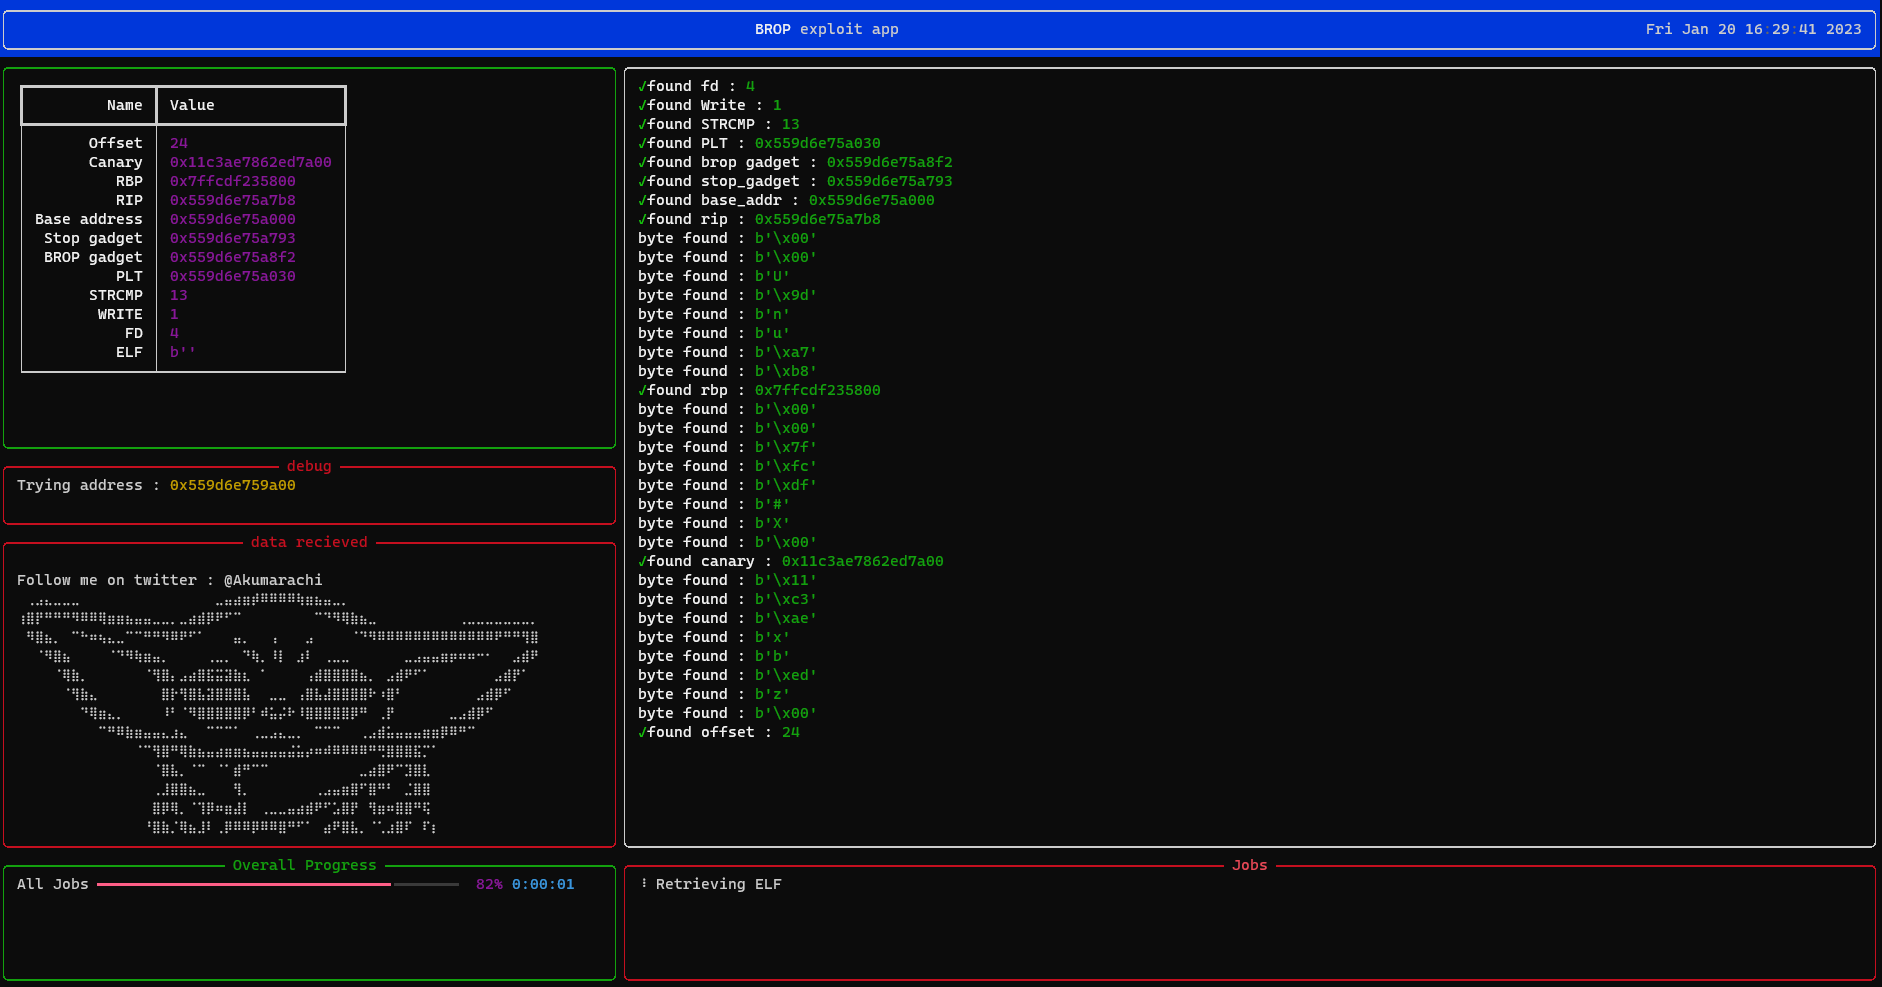 hakumarachi/bropper
An automatic Blind ROP exploitation tool
 r0rt1z2/ghostlock
Kernel root exploit (CVE-2026-43499) for some Amazon devices
 y3a/cve-2023-28229
Proof-of-concept exploit for Windows CNG KeyIso RPC elevation of privilege and sandbox escape, demonstrating exploitation of CVE-2023-28229.
 timwr/cve-2019-2215
Android kernel privilege escalation exploit for CVE-2019-2215, providing a proof-of-concept to achieve root access via a use-after-free vulnerability…
 rew-sploit/rew-sploit
Emulate and Dissect MSF and *other* attacks
 karollooool/cve-2026-50416-writeup-and-poc
CVE-2026-50416: Windows 11 KASLR bypass
 boundaryx/cloudrasp-log4j2
一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.
 ayrx/cve-2021-4034
Exploit for CVE-2021-4034 (PwnKit) that leverages a race condition in pkexec to escalate privileges to root on Linux systems.