
chakra-exploit-framework
 ntdelta/chakra-exploit-framework
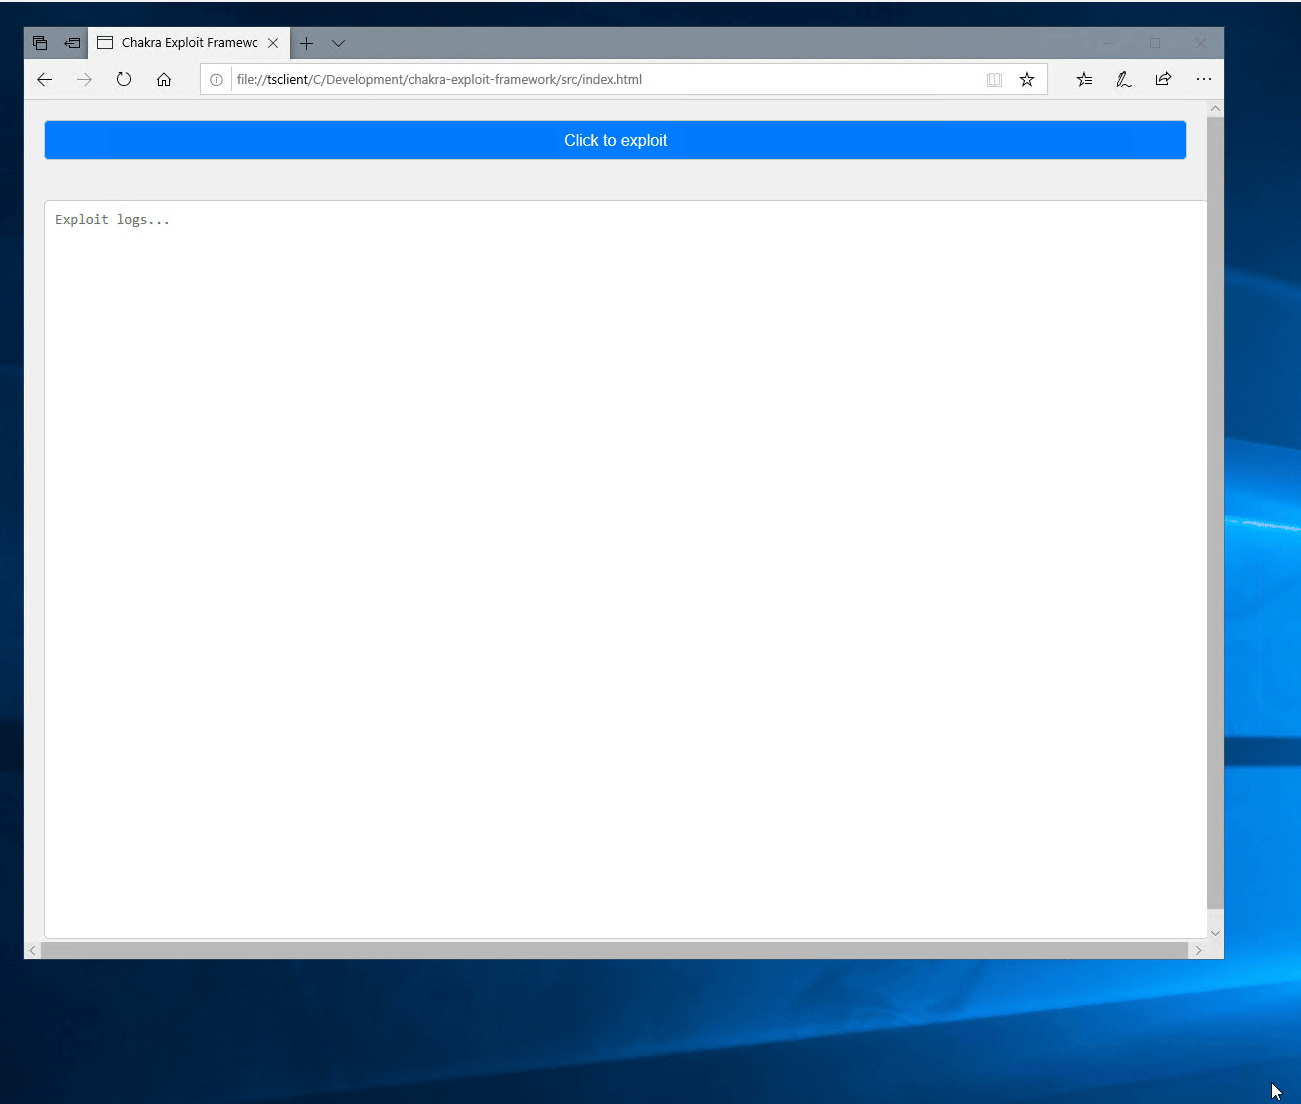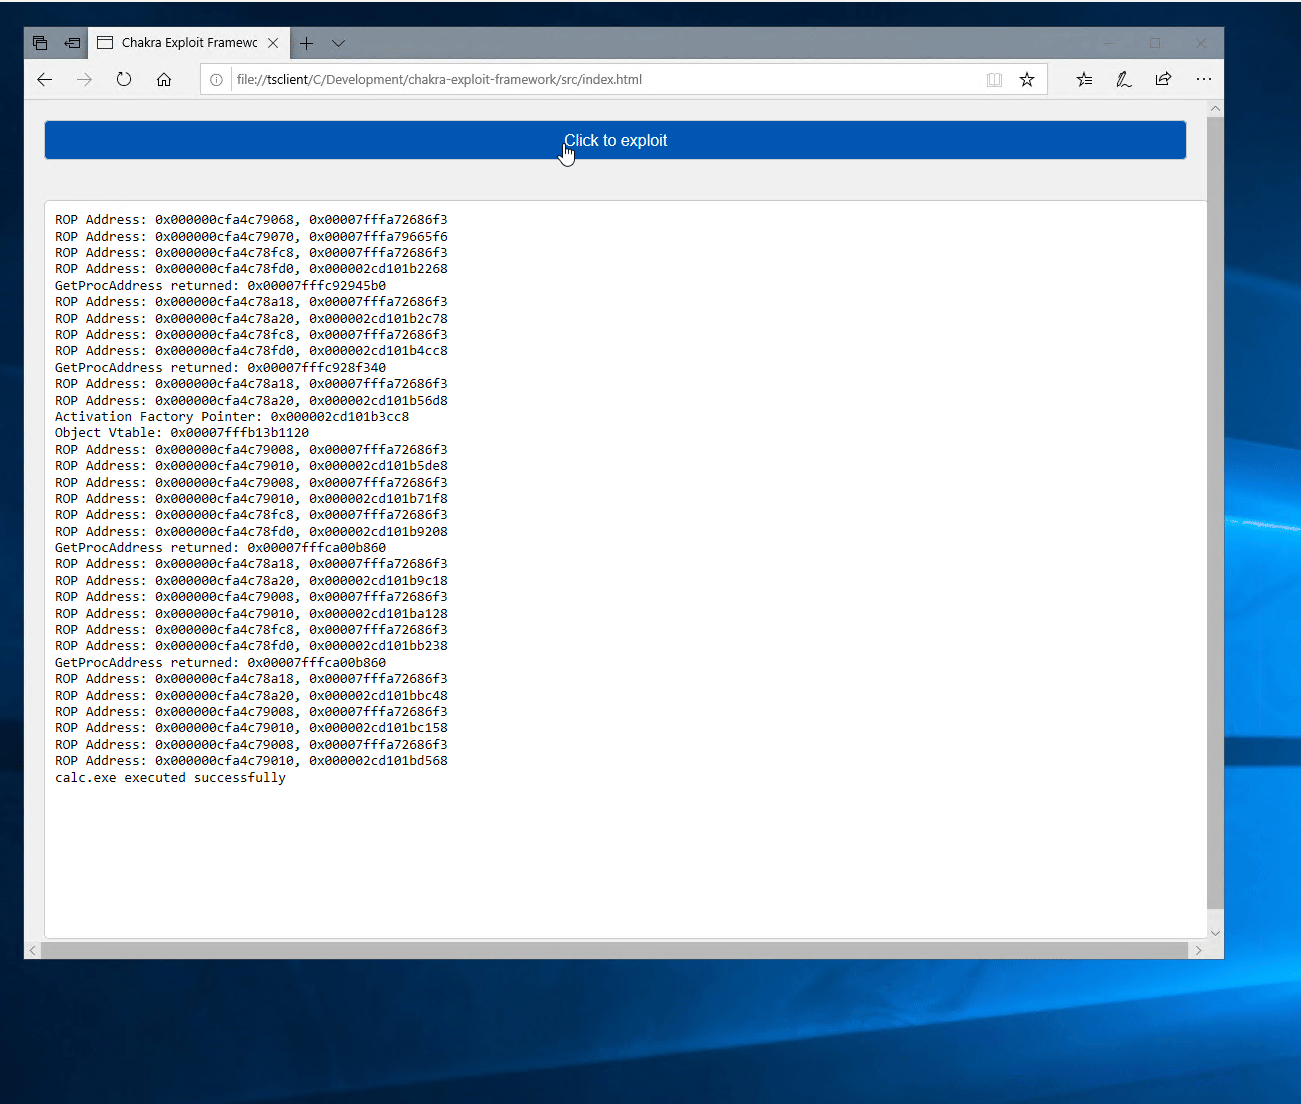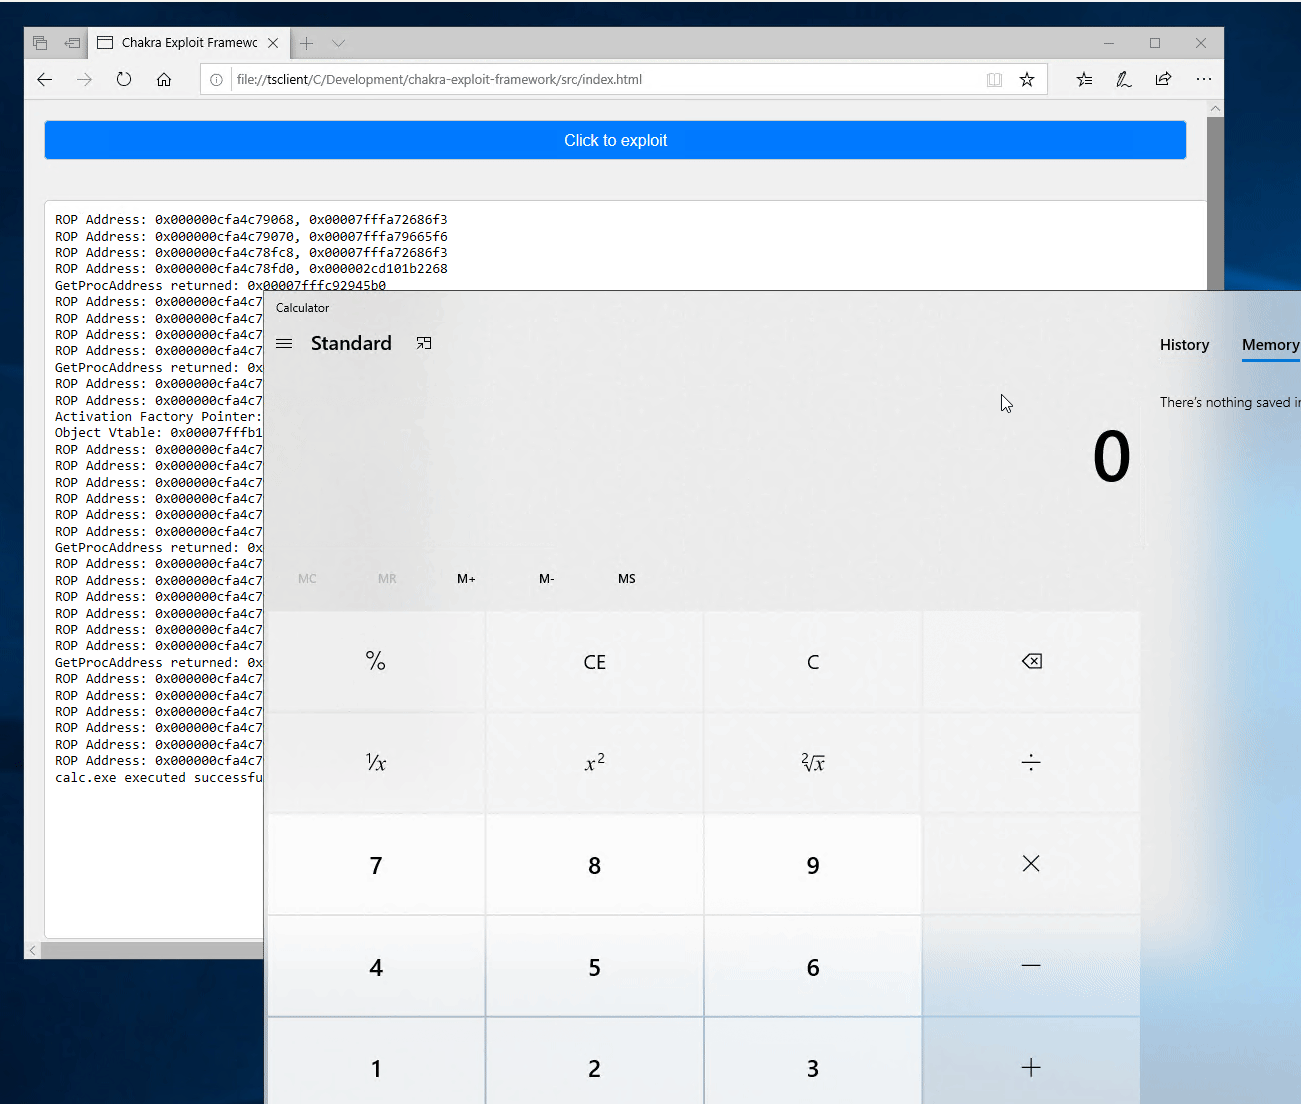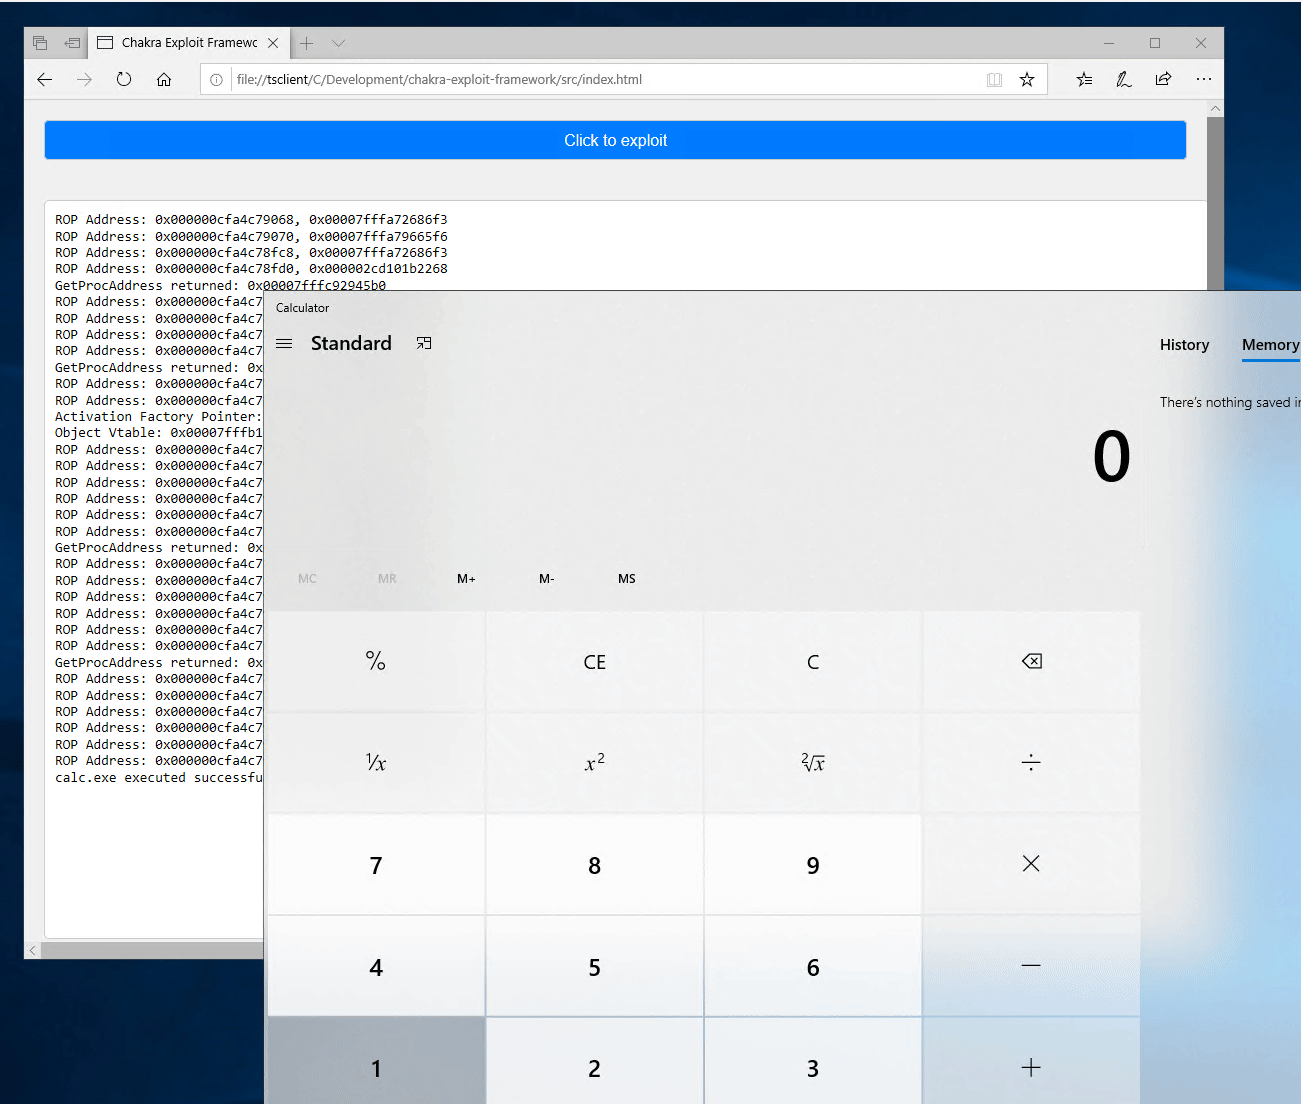
Browser exploitation framework for Chakra (Edge). Written as part of OSEE preparation. Demo bug: CVE-2019-0567
binary-exploitationeducationexploit-frameworks+6
1
ntdelta/chakra-exploit-frameworkBrowser exploitation framework for Chakra (Edge). Written as part of OSEE preparation. Demo bug: CVE-2019-0567
 ermensonx/cve-2024-38077-madlicense-exploit
Modular exploit framework for CVE-2024-38077 (Windows RDL heap overflow) with ASLR bypass, heap grooming, ROP chain generation, and DLL injection…
 optiv/scarecrow
ScareCrow - Payload creation framework designed around EDR bypass.
 didi/kemon
An Open-Source Pre and Post Callback-Based Framework for macOS Kernel Monitoring.
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 darkr4y/geacon
Practice Go programming and implement CobaltStrike's Beacon in Go
 vysecurity/morphhta
morphHTA - Morphing Cobalt Strike's evil.HTA
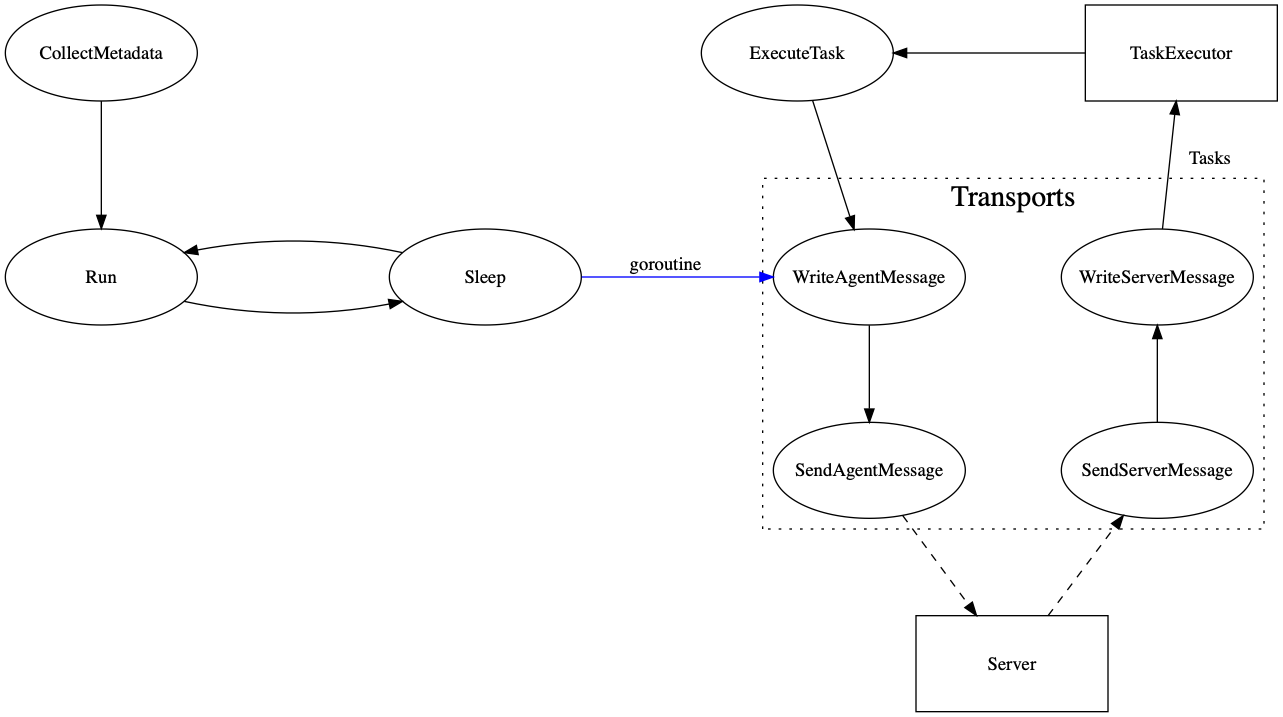 kcarretto/paragon
Red Team engagement platform with the goal of unifying offensive tools behind a simple UI
 rew-sploit/rew-sploit
Emulate and Dissect MSF and *other* attacks
 s1eezer/cve-2026-8069
Technical write-up and proof-of-concept for CVE-2026-8069, a local privilege escalation in Acer NitroSense and PredatorSense services, exploiting a…
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 egebalci/hercules
HERCULES is a special payload generator that can bypass antivirus softwares.
 getrektboy724/meterpwrshell
Automated Tool That Generates The Perfect Meterpreter Powershell Payload
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 gloxec/crossc2
generate CobaltStrike's cross-platform payload
 boku7/bokuloader
A proof-of-concept Cobalt Strike Reflective Loader which aims to recreate, integrate, and enhance Cobalt Strike's evasion features!
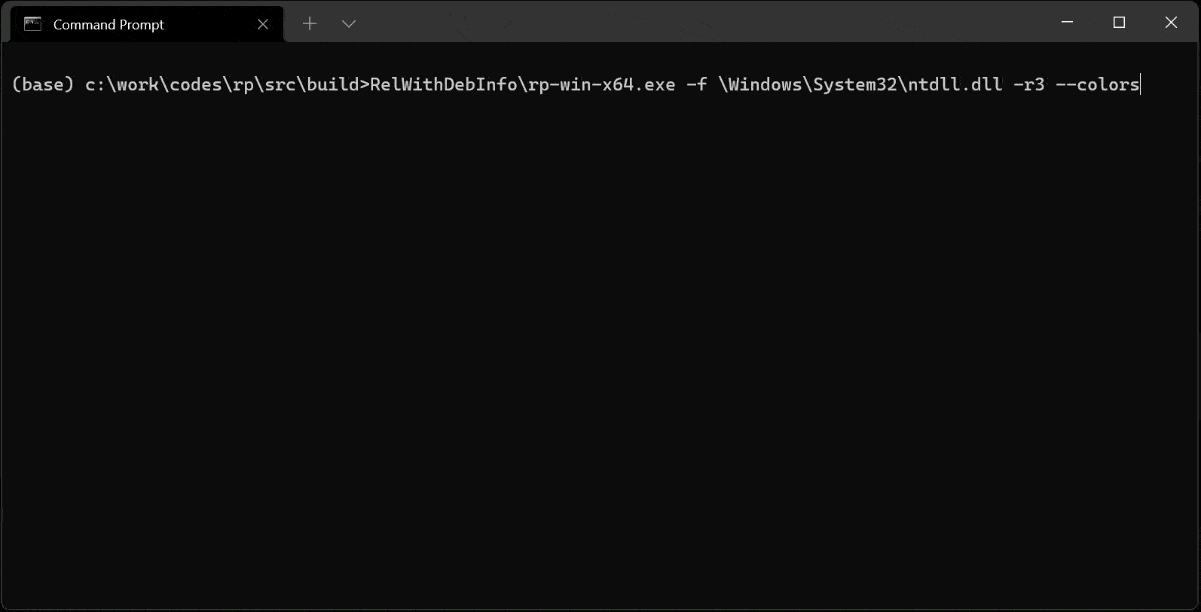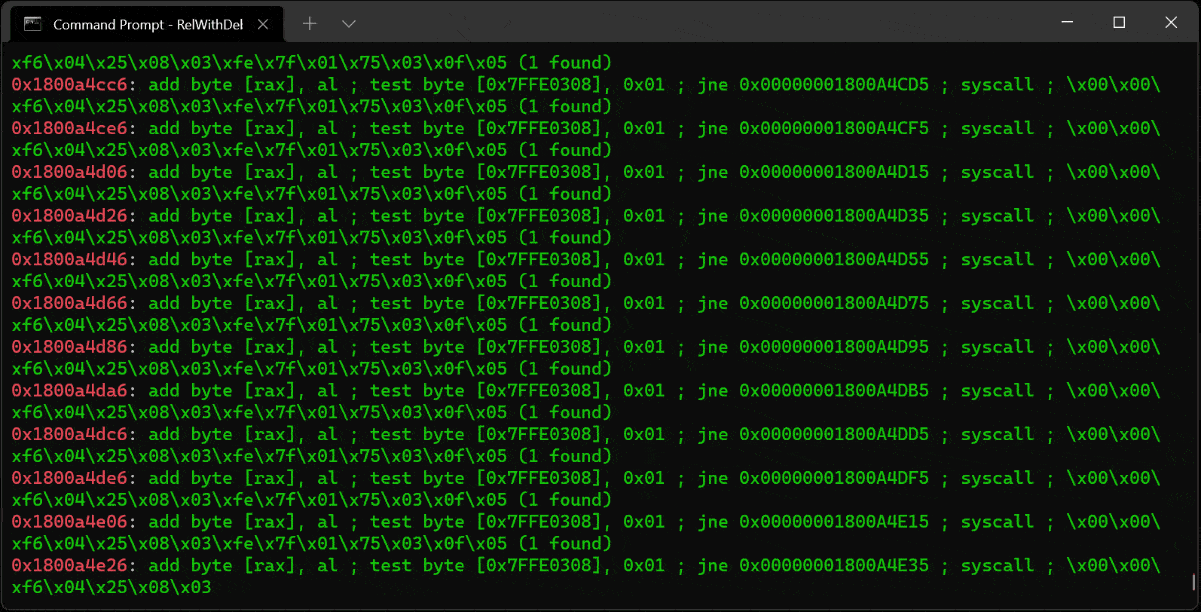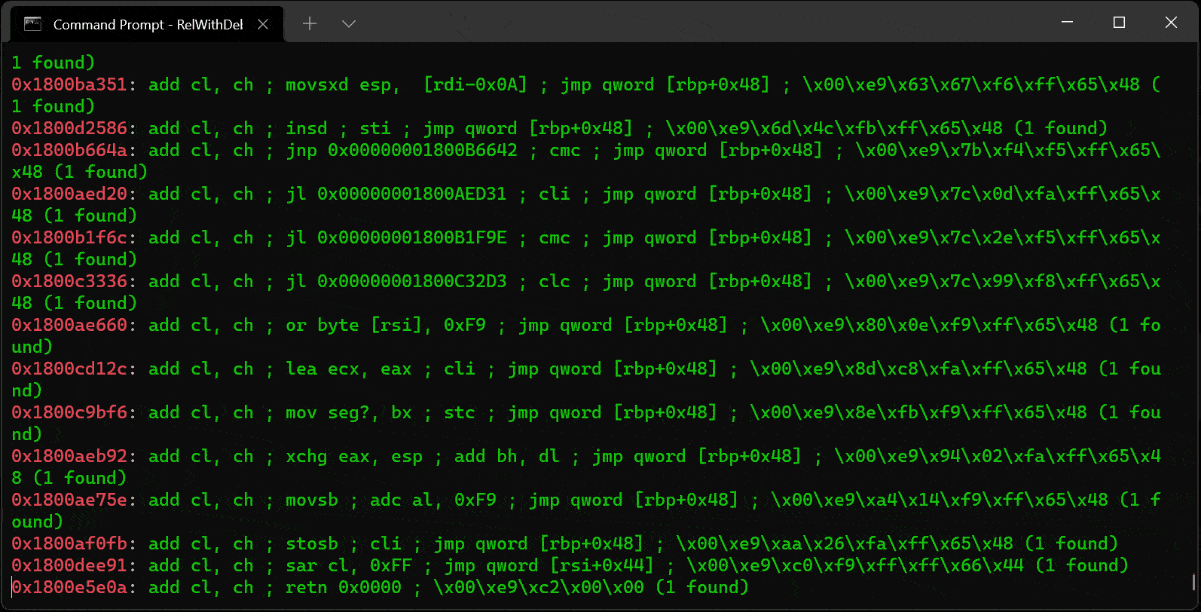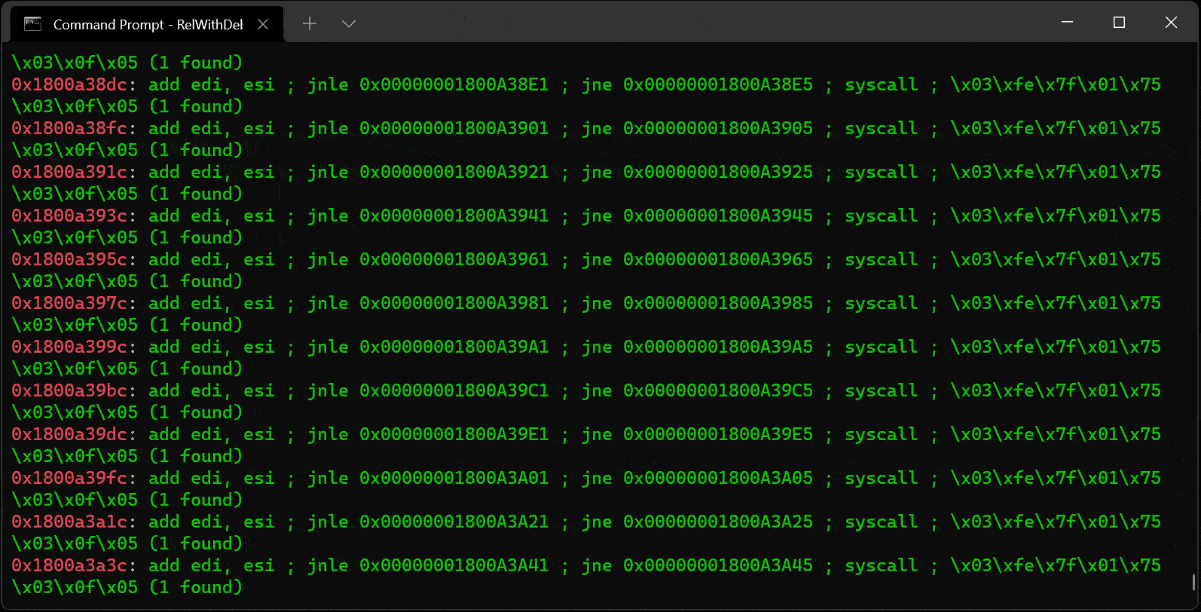 0vercl0k/rp
Fast C++ ROP gadget finder for PE/ELF/Mach-O binaries across x86/x64/ARM/ARM64 architectures, enabling efficient return-oriented programming chain…
 jackofmosttrades/gadgetinspector
A byte code analyzer for finding deserialization gadget chains in Java applications