
Archived
PhoenixC2
 phoenixc2/phoenixc2
Command & Control-Framework created for collaboration in python3
command-and-controlexploit-frameworkspayload-development+4
324
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 byt3bl33d3r/silenttrinity
An asynchronous, collaborative post-exploitation agent powered by Python and .NET's DLR
 pandasec888/taowu-cobalt_strike
Red team automation framework built on Cobalt Strike, integrating exploit modules, post-exploitation tools, and lateral movement capabilities for…
 r00t-3xp10it/venom
venom - C2 shellcode generator/compiler/handler
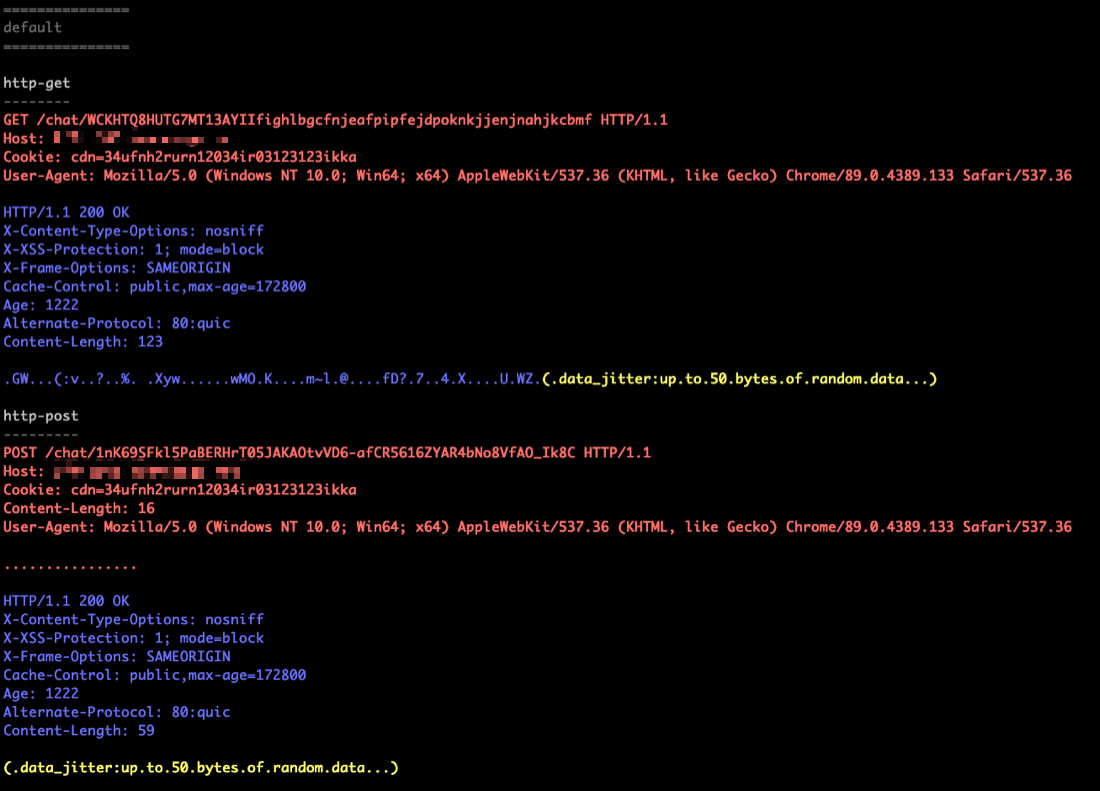 tylous/sourcepoint
Polymorphic C2 profile generator for Cobalt Strike that automates creation of evasive beacon configurations with randomized options for HTTP, DNS,…
 r00ts3c/ddos-rootsec
Explore RootSec's DDOS Archive, featuring top-tier scanners, powerful botnets (Mirai & QBot) and other variants, high-impact exploits, advanced…
 bats3c/shad0w
A post exploitation framework designed to operate covertly on heavily monitored environments
 outflanknl/c2-tool-collection
A collection of tools which integrate with Cobalt Strike (and possibly other C2 frameworks) through BOF and reflective DLL loading techniques.

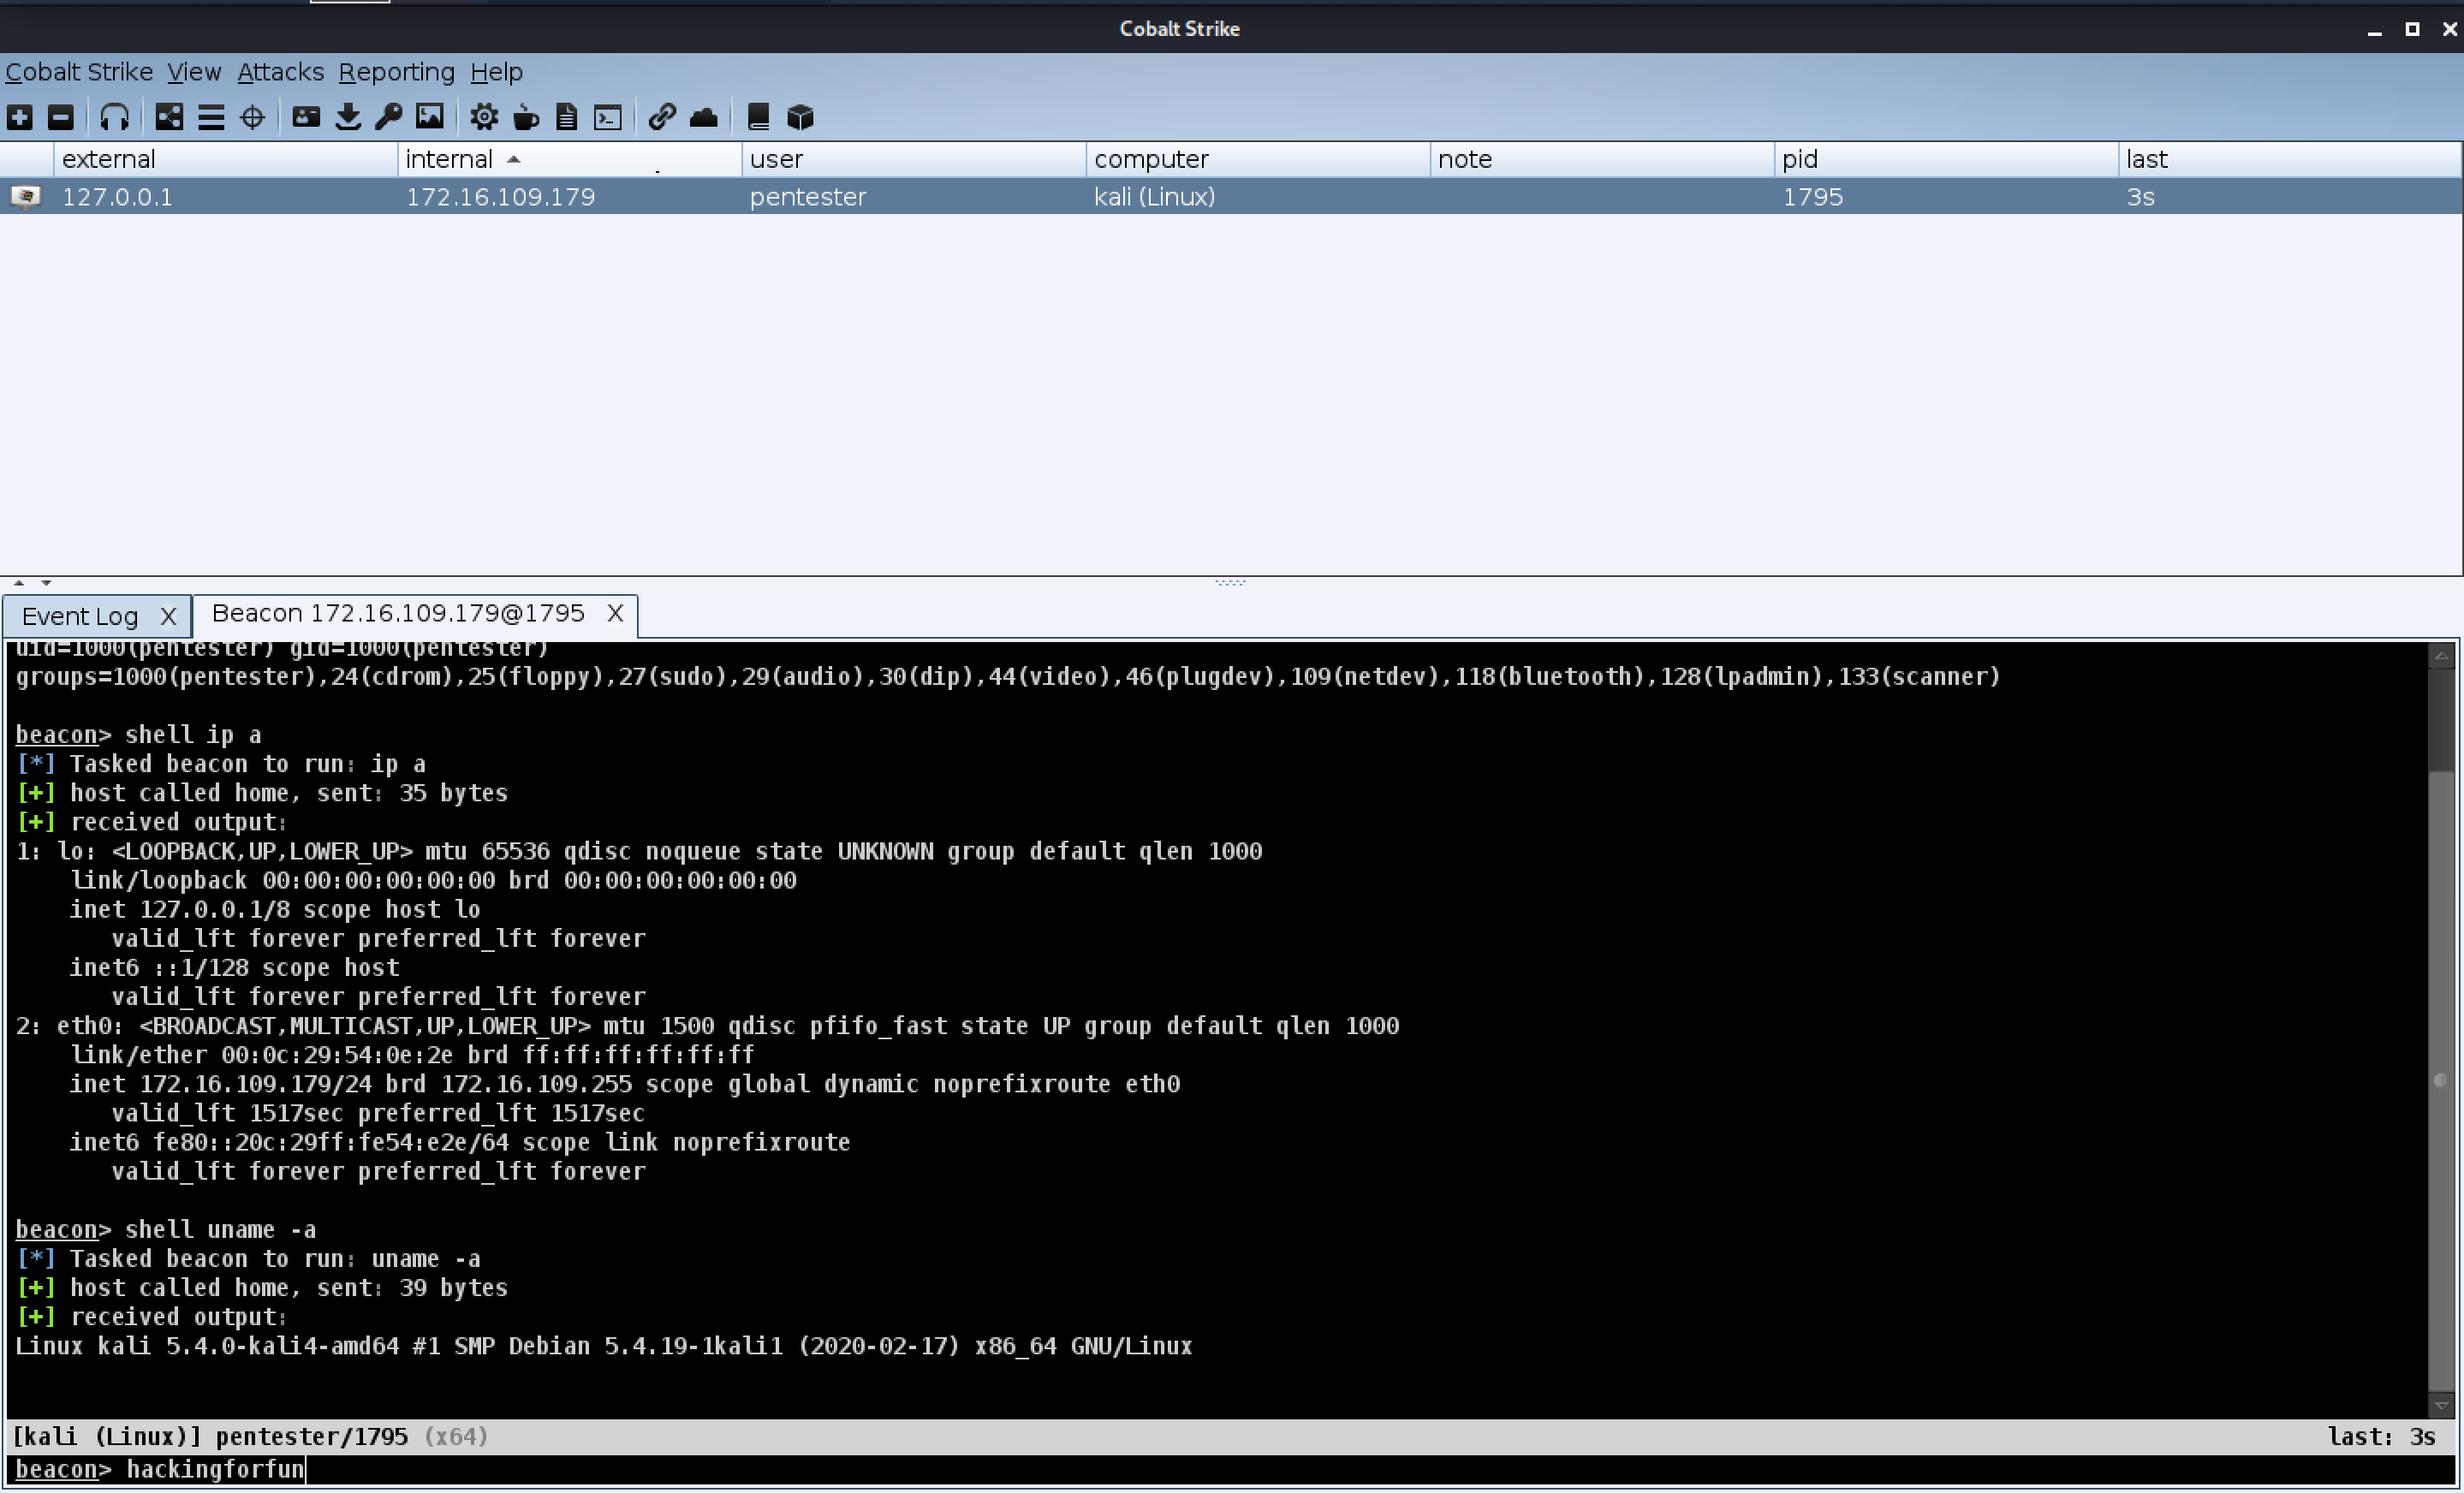 darkr4y/geacon
Practice Go programming and implement CobaltStrike's Beacon in Go
 mandiant/gopacket
A complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…
 xx0hcd/malleable-c2-profiles
Cobalt Strike - Malleable C2 Profiles. A collection of profiles used in different projects using Cobalt Strike https://www.cobaltstrike.com/.
 wkl-sec/hiddendesktop
HVNC for Cobalt Strike
 vulncheck-oss/go-exploit
Go-based exploit development framework with built-in phases for target verification, version scanning, exploitation, and C2. Supports multiple…
 mythicagents/thanatos
Mythic C2 agent targeting Linux and Windows hosts written in Rust