
CVE-2021-4034
 anonymous-family/cve-2021-4034
Exploit for CVE-2021-4034 (PwnKit) in Polkit's pkexec, providing local privilege escalation to root on Linux systems. Includes build instructions and…
binary-exploitationexploitationexploit-frameworks+2
2
anonymous-family/cve-2021-4034Exploit for CVE-2021-4034 (PwnKit) in Polkit's pkexec, providing local privilege escalation to root on Linux systems. Includes build instructions and…
 v-rzh/cve-2021-4034
Root exploit for CVE-2021-4034 (PwnKit) that abuses pkexec's out-of-bounds write to escalate privileges to root on Linux systems.
 oreosec/pwnkit
Exploit for CVE-2021-4034, a memory corruption vulnerability in pkexec of polkit, enabling local privilege escalation to root on Linux systems.
 tachote/cve-2021-4034
Exploit for CVE-2021-4034, a Polkit pkexec privilege escalation vulnerability, allowing unprivileged users to gain root on Linux systems.
 ankit-ojha16/cve-2021-4034
Local privilege escalation exploit for CVE-2021-4034 targeting pkexec, enabling unprivileged users to gain root access on vulnerable Linux systems.
 nel0x/pwnkit-vulnerability
Local privilege escalation exploit for CVE-2021-4034 (PWNKIT) targeting Polkit's pkexec, allowing unprivileged users to gain root on vulnerable Linux…
 jostmart/-cve-2021-4034
Exploit for CVE-2021-4034, a local privilege escalation in polkit's pkexec, providing root access on Linux systems.
 an0n7os/cve-2021-4034
Exploit for CVE-2021-4034, a polkit pkexec privilege escalation vulnerability, providing a root shell on vulnerable Linux systems.
 teelrabbit/polkit-pkexec-exploit-for-linux
Exploit for CVE-2021-4034, a local privilege escalation vulnerability in polkit's pkexec, allowing unprivileged users to gain root on Linux systems.
 shibaaa204/pack2theroot
Proof-of-concept exploit for CVE-2026-41651, a Linux local privilege escalation vulnerability in Pack2 software, demonstrating root access and system…
 hegaz0y/-bul
EDSEC_BKIF is a keystroke injection tool for Android, Linux, and iOS. With the help of CVE-2023-45866, it grants users unprecedented control over…
 pyroceper/copy-fail-cve-2026-31431
C-based proof-of-concept exploit for CVE-2026-31431, a Linux kernel privilege escalation vulnerability, providing root shell access on affected…
 b5null/cve-2026-31431-c
Local privilege escalation exploit for Linux kernel CVE-2026-31431, abusing AF_ALG and splice to patch /usr/bin/su and gain root.
 spensercai/copy_fail
Rust exploit PoC for Linux kernel LPE CVE-2026-31431 (AF_ALG page-cache write) plus eBPF runtime defense blocking AF_ALG socket creation via LSM or…
 rosnlr5/modrosnlr5
Proof-of-concept exploit for Linux kernel CVE-2026-31431, leveraging AF_ALG sockets to escalate privileges to root via payload injection and shell…
 hori0729/cve-2026-31431-verificador-exploit
Local privilege escalation exploit for Linux kernel CVE-2026-31431, exploiting AF_ALG and splice() to modify page cache and gain root shell.
 gr-1m/cve-2026-31431
Golang rewrite of the Copy Fail (CVE-2026-31431) local privilege escalation exploit, corrupting page cache to gain root on Linux systems.
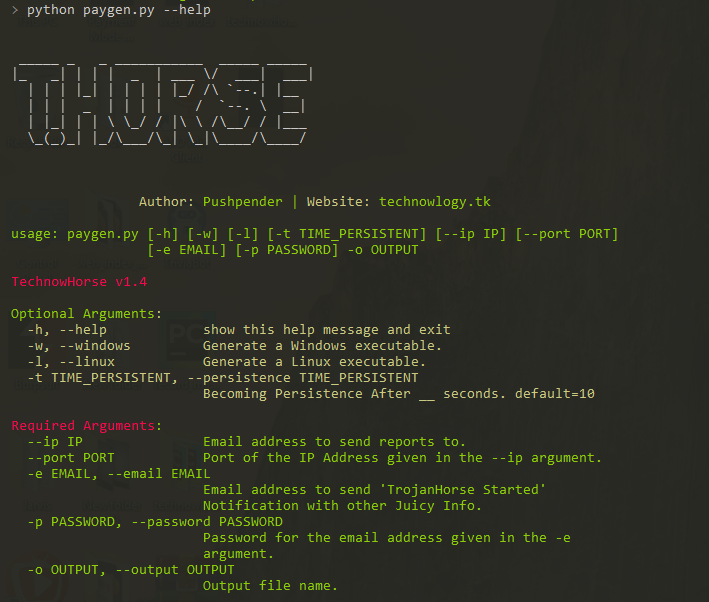 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.