
CyberStrike
 cyberstrikeus/cyberstrike
Autonomous AI red team agent for penetration testing with 13+ specialized agents, 120+ OWASP test cases, and MITRE ATT&CK integration. Supports 15+…
ai-securitycloud-securityeducation+9
1.7k
cyberstrikeus/cyberstrikeAutonomous AI red team agent for penetration testing with 13+ specialized agents, 120+ OWASP test cases, and MITRE ATT&CK integration. Supports 15+…
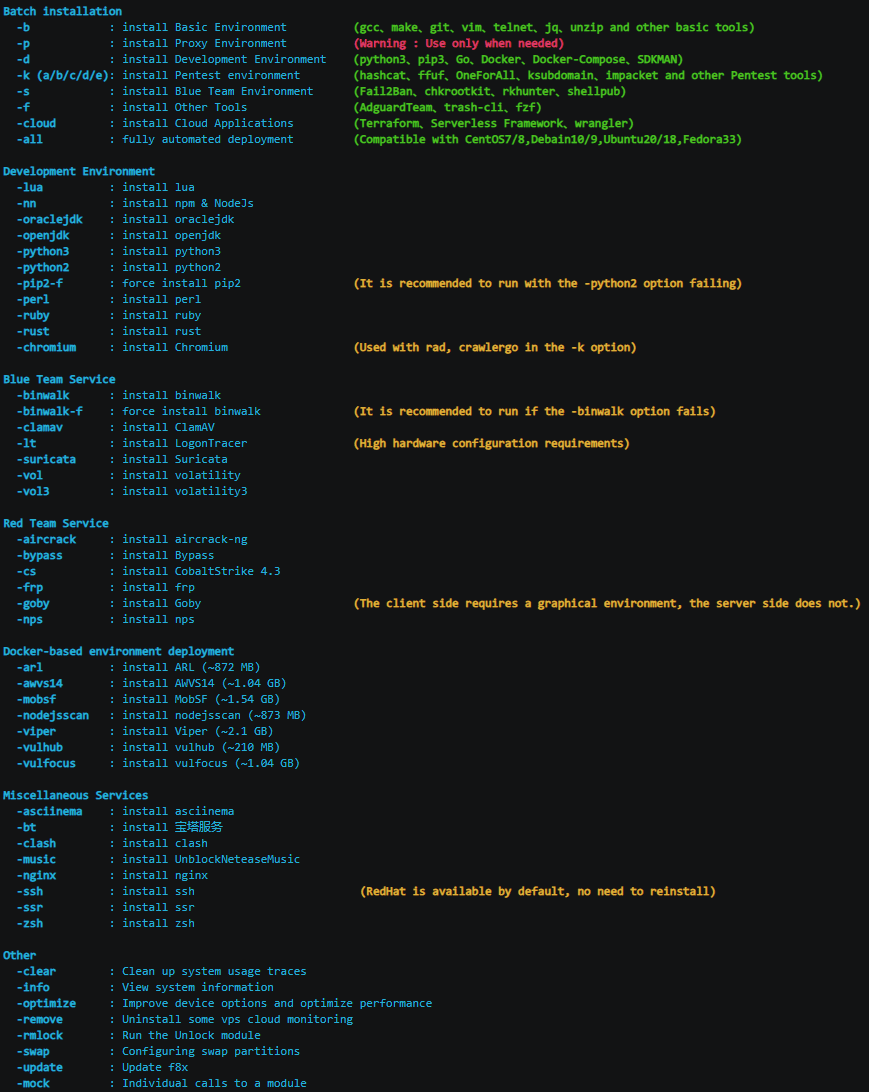 ffffffff0x/f8x
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool
 zakirkun/guardian-cli
Guardian is a production-ready AI-powered penetration testing automation CLI tool that leverages Google Gemini and LangChain to orchestrate…
 mafifrizi/ares
Autonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…
 metarget/metarget
Metarget is a framework providing automatic constructions of vulnerable infrastructures.
 v4bel/januscape
KVM/x86 guest-to-host escape exploit (CVE-2026-53359) leveraging a use-after-free in shadow MMU emulation. Includes PoC for triggering host kernel…
 redsiege/graphstrike
Cobalt Strike HTTPS beaconing over Microsoft Graph API
 secdevops-cuse/cyberrange
The Open-Source AWS Cyber Range
 gl4ssesbo1/nebula
Nebula is a cloud C2 Framework, which at the moment offers reconnaissance, enumeration, exploitation, post exploitation on AWS, but still working to…
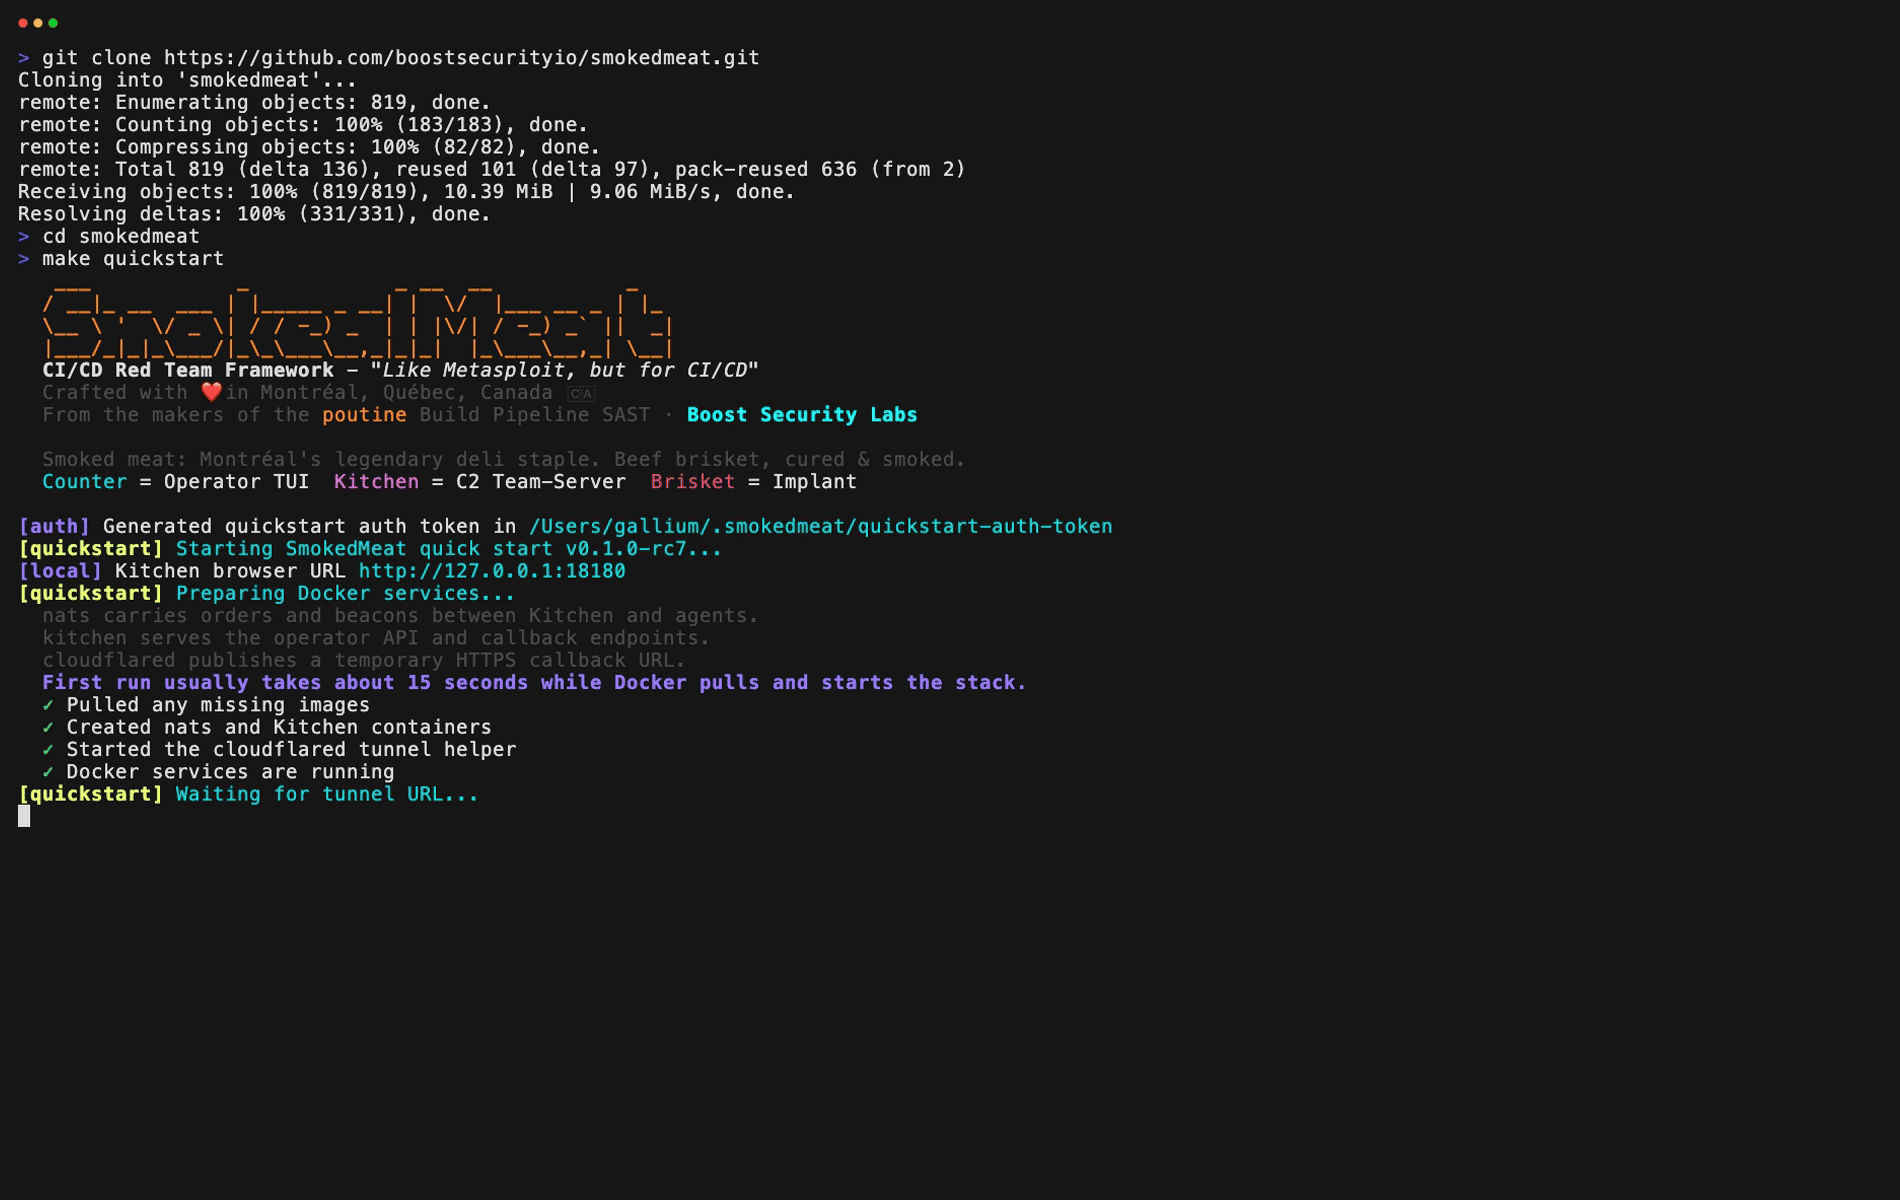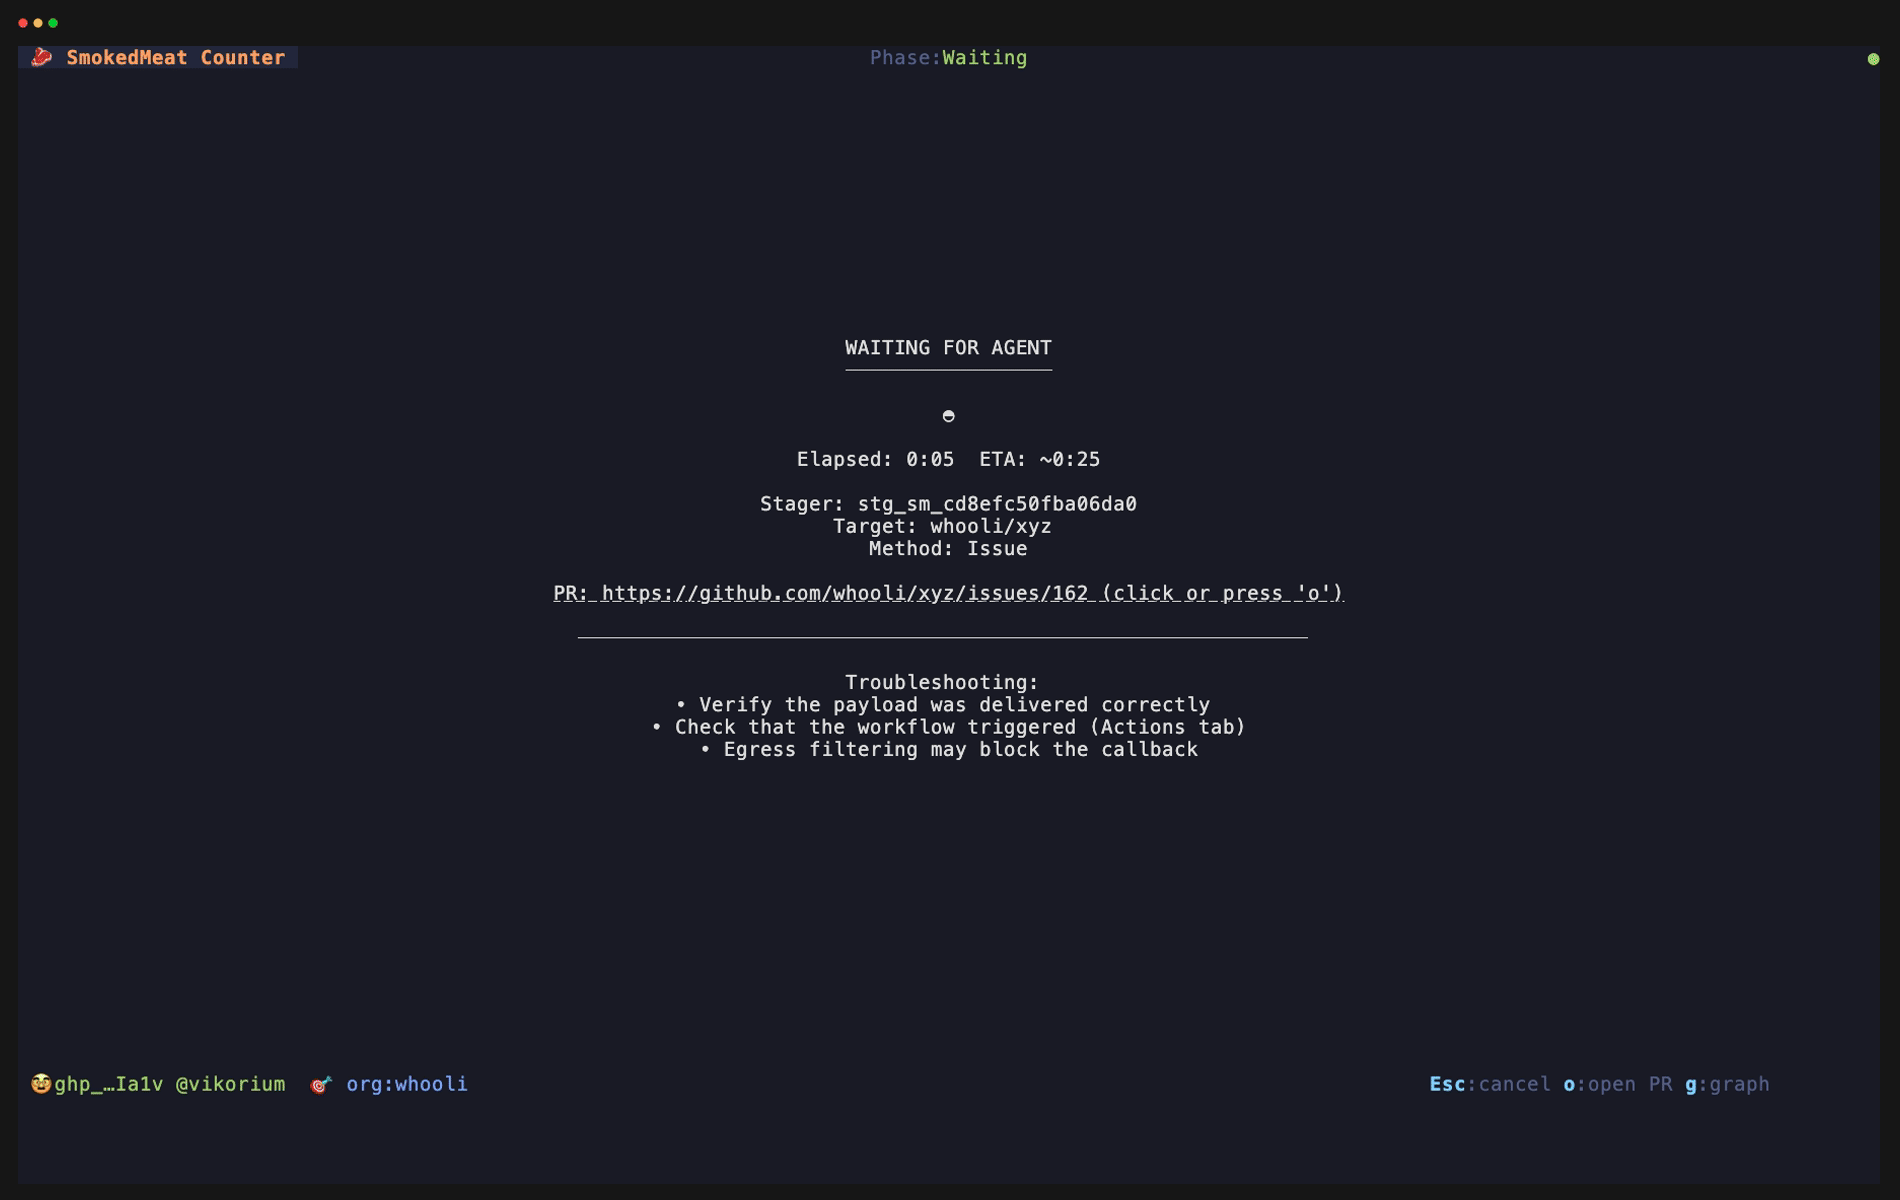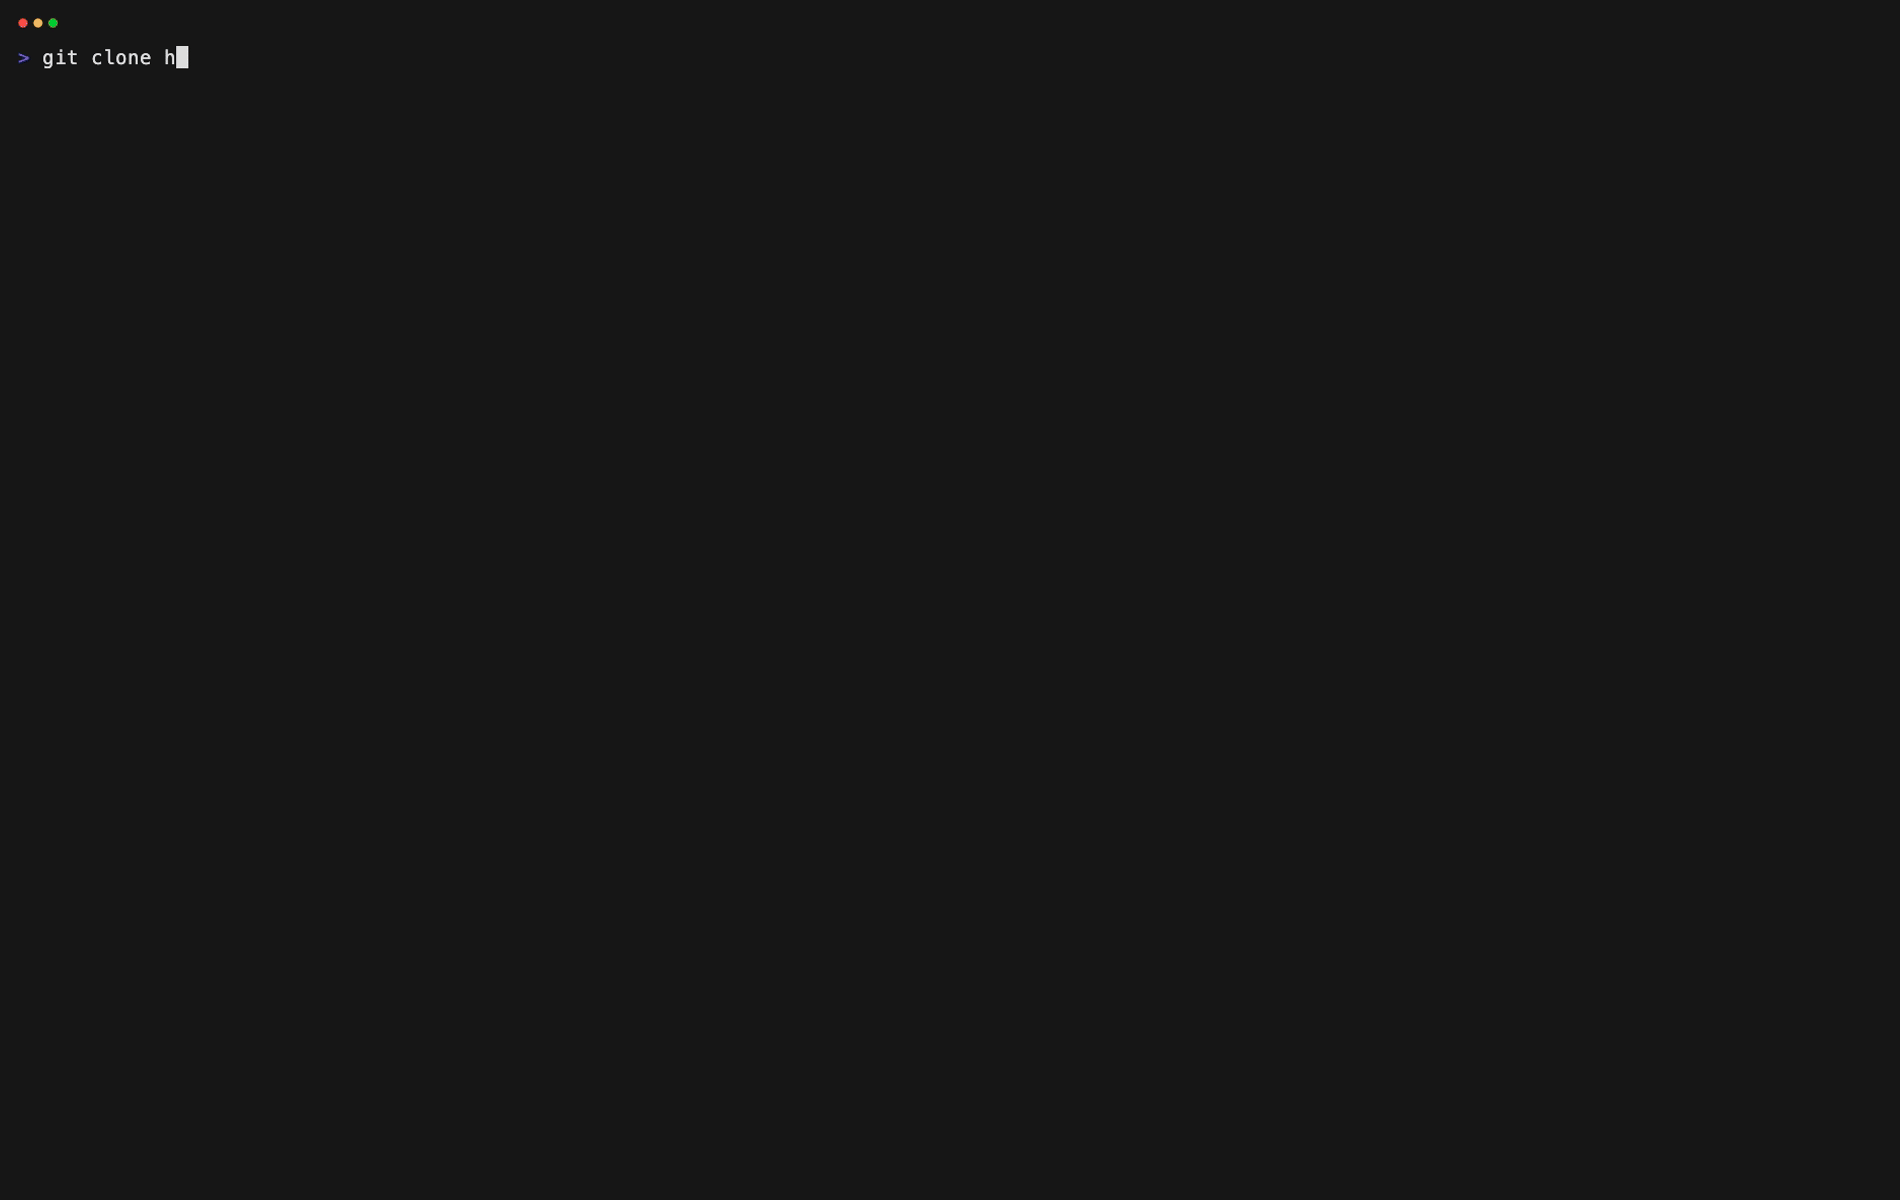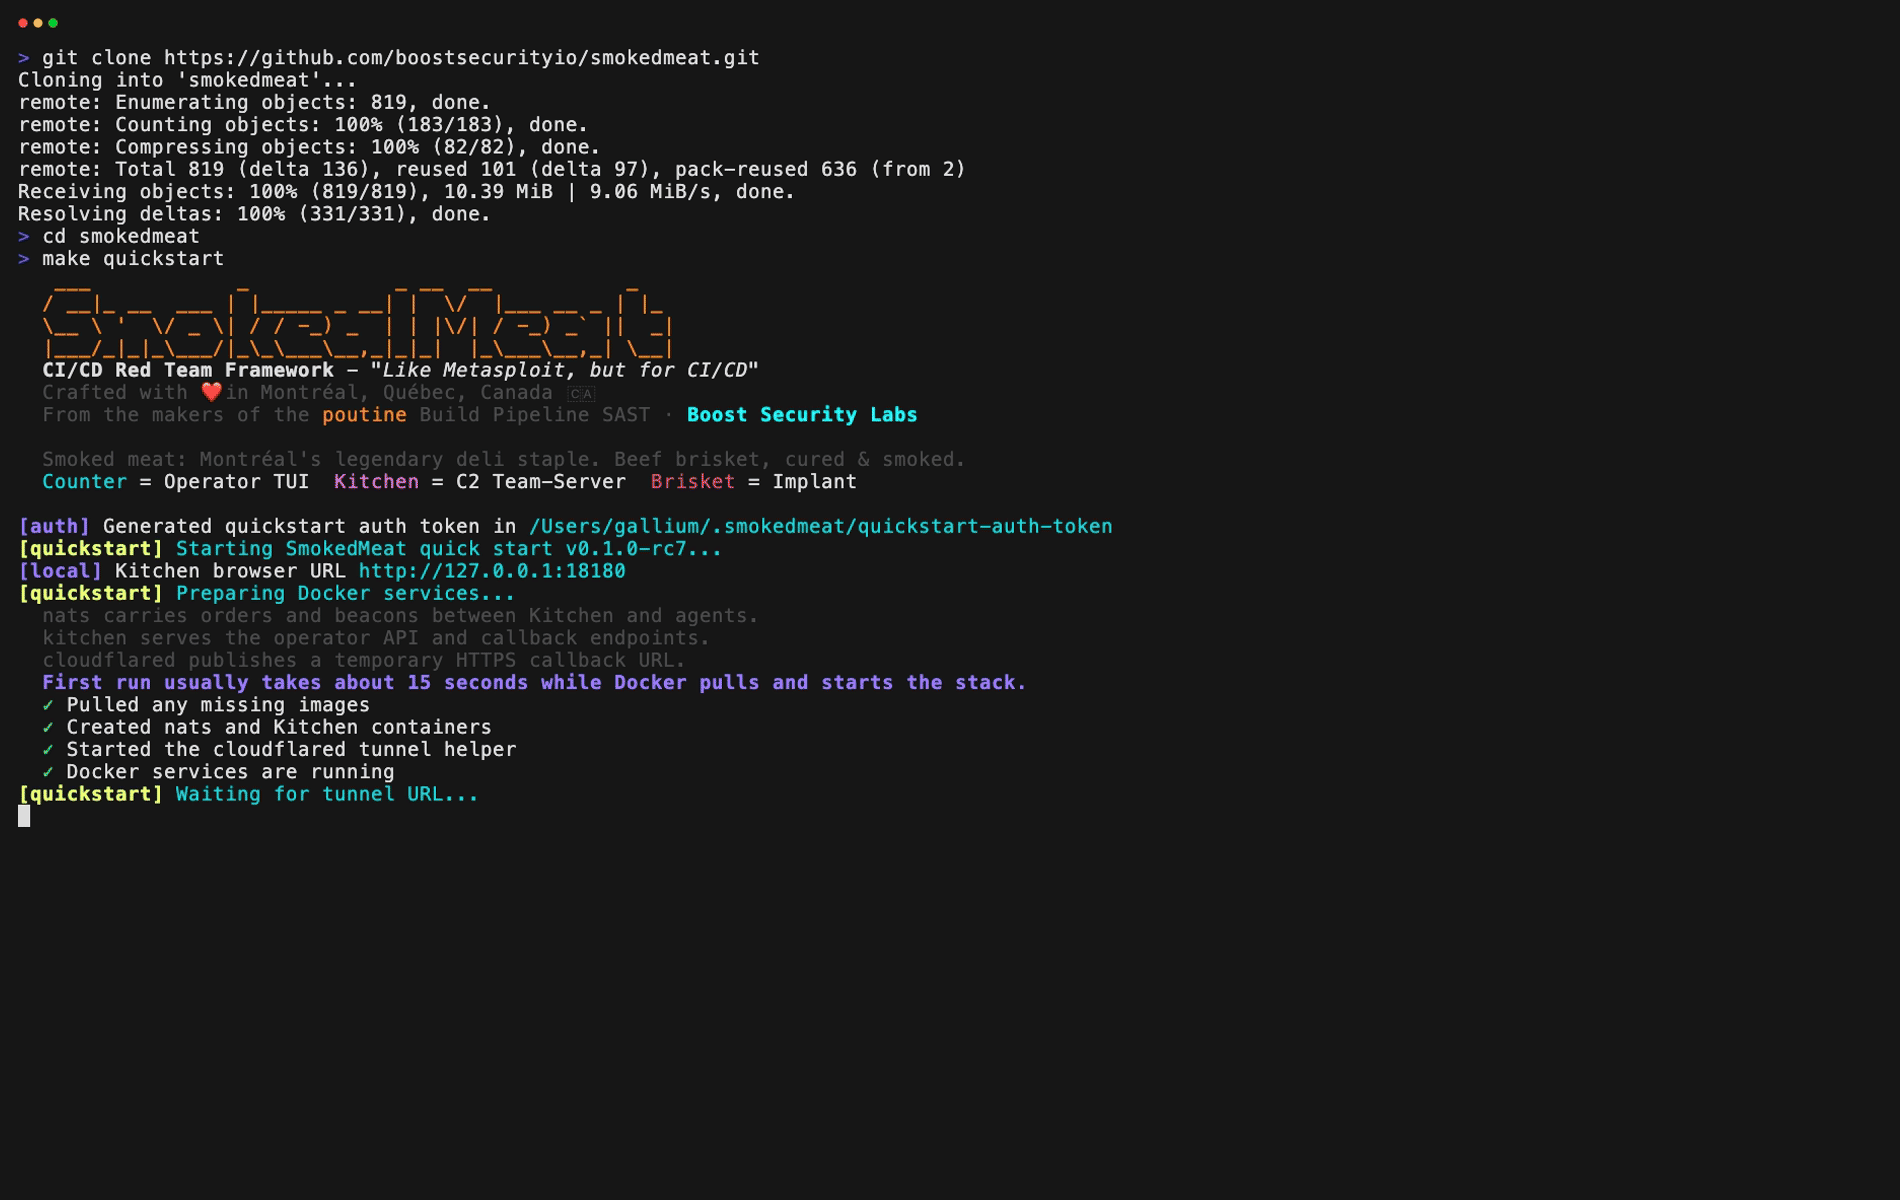 boostsecurityio/smokedmeat
A CI/CD Red Team Framework for demonstrating Build Pipeline security risks.
 flangvik/cobaltbus
Cobalt Strike External C2 Integration With Azure Servicebus, C2 traffic via Azure Servicebus
 luemmelsec/apex
Azure Post Exploitation Framework
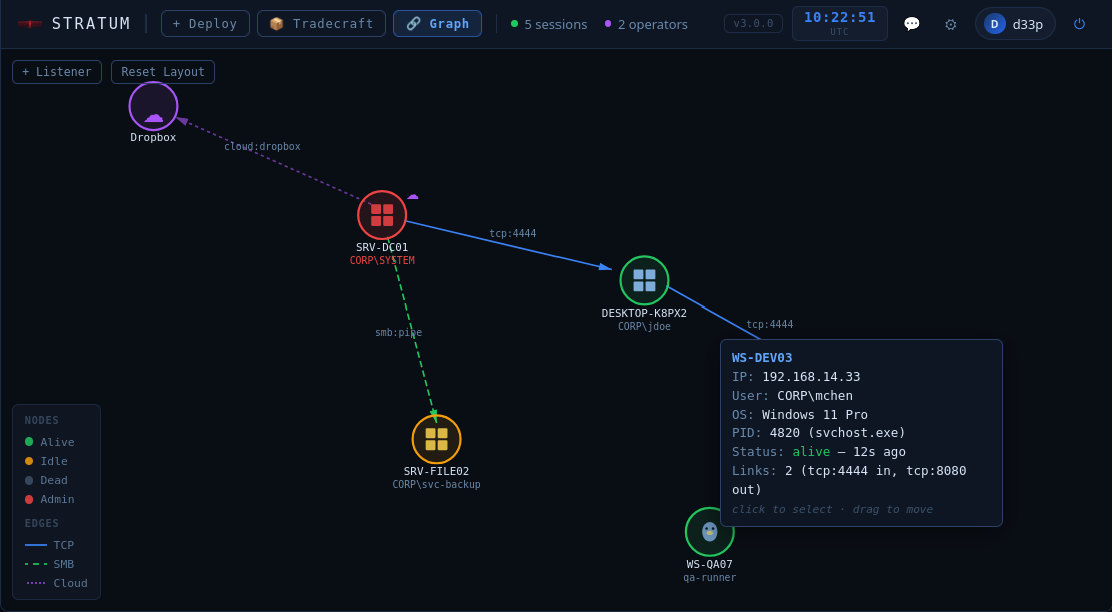 lame-projects/stratum-c2
Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting
 rnalter/thundercloud
Cloud Exploit Framework
 galoryber/fawkes
Fawkes is a golang Mythic C2 Agent exclusively written by AI.
 ajutamangdev/hatiyar
Modular penetration testing framework with a Metasploit-like interactive shell, pre-built CVE exploit modules, and cloud/network reconnaissance…
 nisec-eric/cve-2026-31431
Linux kernel local privilege escalation exploit for CVE-2026-31431, providing a reliable single-shot PoC with multiple language implementations,…