Domain-Controller-DC-Exploitation-with-Metasploit-Impacket

End-to-end Domain Controller exploitation using Metasploit and Impacket: discovered DC10, exploited Zerologon (CVE-2020-1472), extracted NTLM hashes,…

End-to-end Domain Controller exploitation using Metasploit and Impacket: discovered DC10, exploited Zerologon (CVE-2020-1472), extracted NTLM hashes,…

Balena Etcher versions prior to v2.1.4 on Windows are affected by a Time-of-Check to Time-of-Use (TOCTOU) race condition in the temporary file…

Controlled penetration testing lab demonstrating CVE-2011-2523 exploitation and mitigation techniques.

Metasploit module for MailEnable CVE-2022-36934 authentication bypass RCE

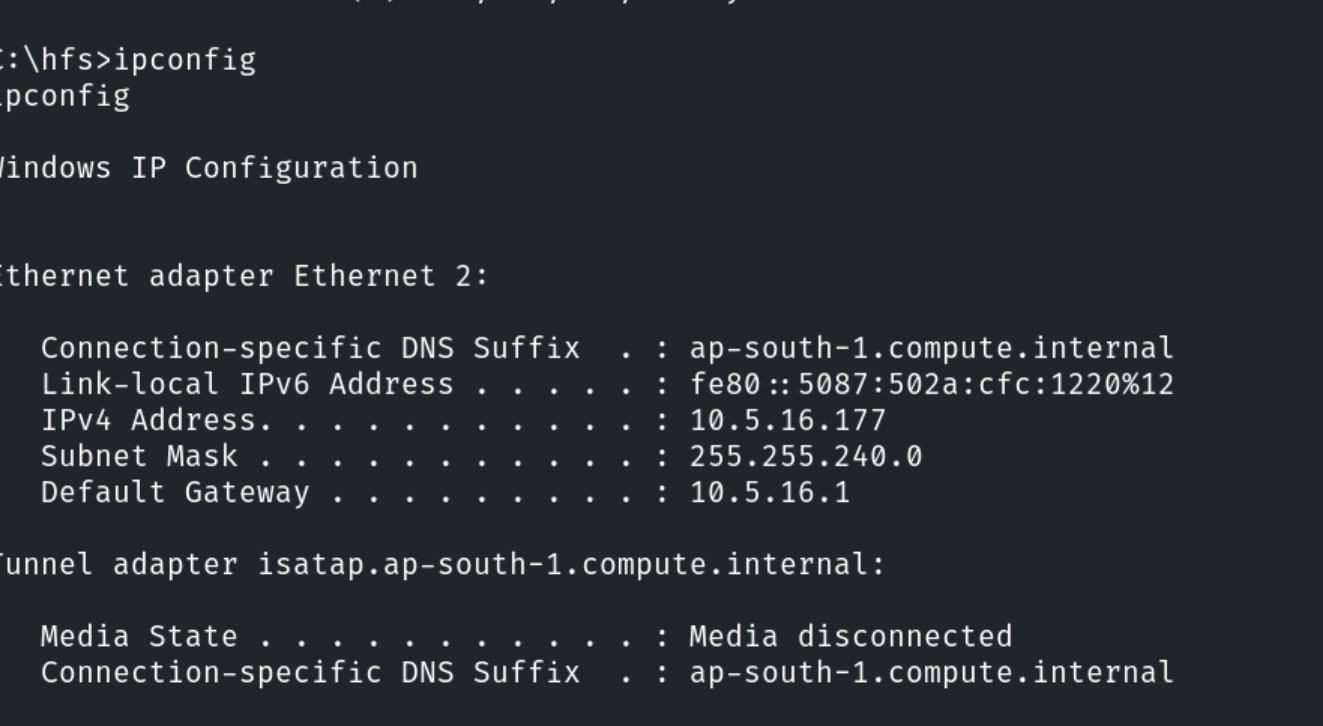
Metasploit RCE on HFS 2.3 - CVE-2014-62

SafeBreaches CVE-2024-49113 POC(LdapNightmare) Integrated into Metasploit


CVE-2026-50416: Windows 11 KASLR bypass

一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.