CVE-2026-54121-PoC-Exploit

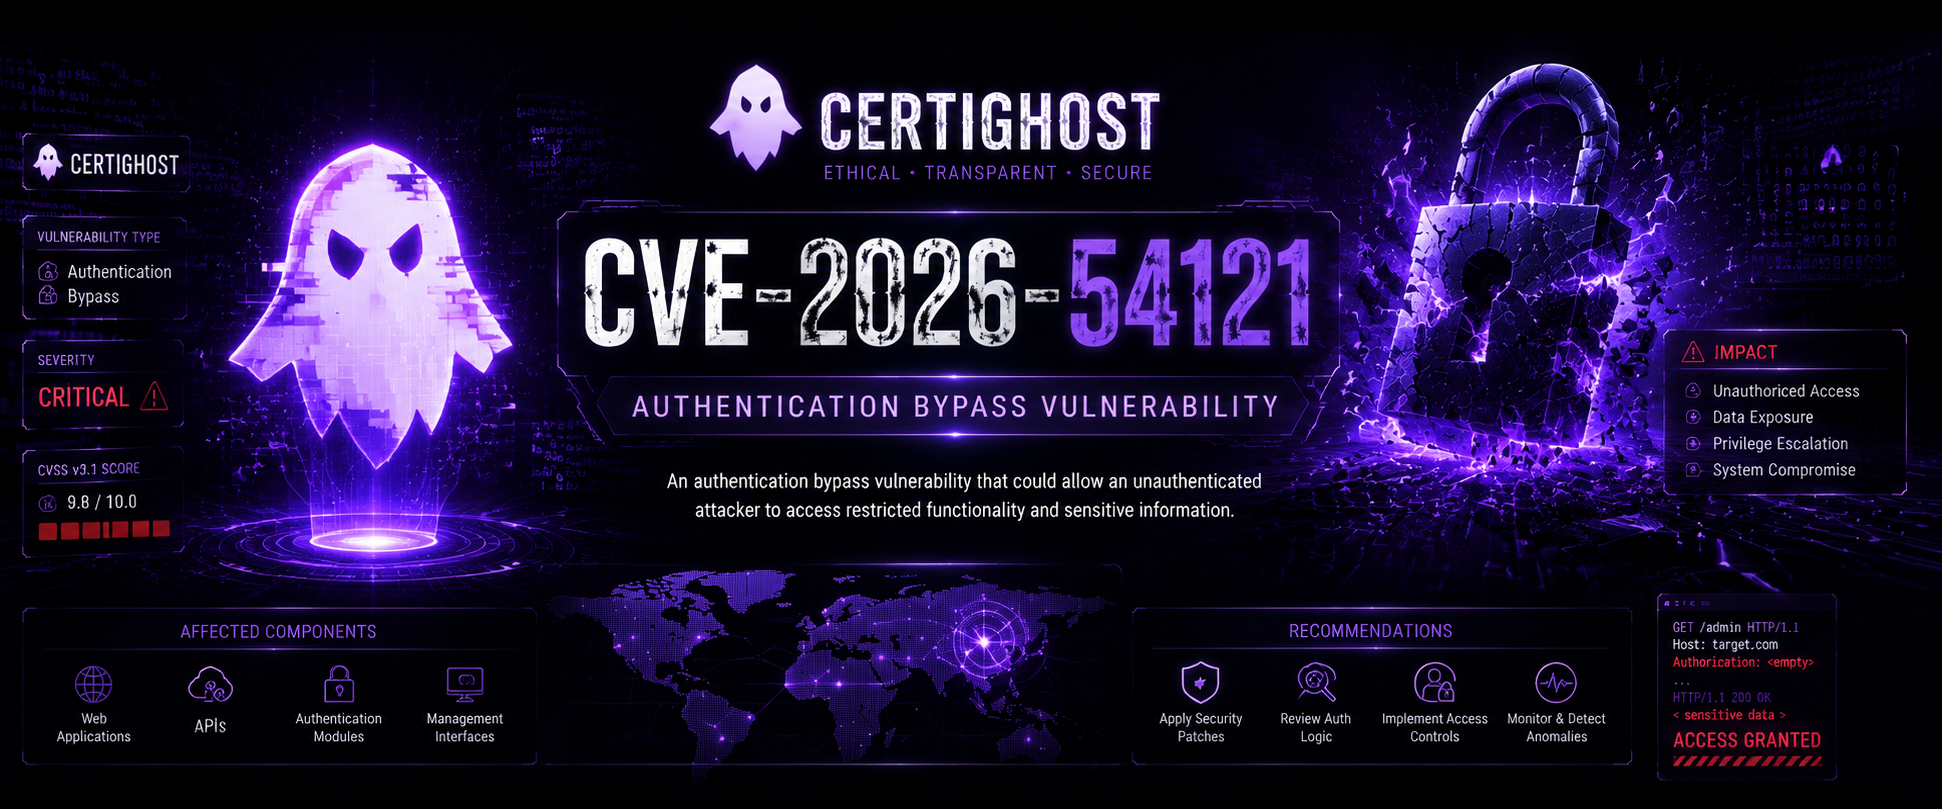
👻 CVE-2026-54121 - Best CertiGhost AD CS Multi-Exploit Framework | Advanced toolkit with rogue DC/LDAP servers, certificate abuse, PKINIT hash…

👻 CVE-2026-54121 - Best CertiGhost AD CS Multi-Exploit Framework | Advanced toolkit with rogue DC/LDAP servers, certificate abuse, PKINIT hash…

Exploit for CVE-2026-40369 that leverages kernel address leak and token forging to achieve privilege escalation in a browser sandbox environment.

👾 CVE-2026-60206 - Oracle WebLogic SAML Auth Bypass Exploit Framework ⚡Bash & Python versions. Features: --detect safe check, --exploit…

Discuz! X5.0 Authentication Bypass Exploit Framework (CVE-2026-49952) - Critical vulnerability allowing unauthenticated database backup access via…

Improved Metasploit module for CVE-2013-6117 (Dahua DVR authentication bypass)

CVE-2025-31200 is a zero-day, zero-click RCE in iOS CoreAudio’s AudioConverterService, triggered by a malicious audio file via iMessage/SMS.…

Metasploit module that exploits a WordPress unserialization vulnerability (CVE-2024-31211) in WP_HTML_Token to achieve remote code execution.

Python-based framework for generating Golden SAML tokens, Kerberos tickets, and Azure Access Tokens to exploit federated identity systems and…

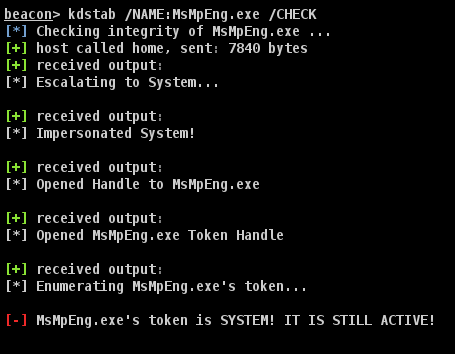
BOF combination of KillDefender and Backstab

app turn nil publics and privates into blanks 3 months ago config Use bundler/setup for more graceful bundler related failures 11 days ago data…

Cobalt Strike Beacon Object File implementing CVE-2020-0796 SMBGhost local privilege escalation with dual weaponization paths for token theft and…