

LazyOwn
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
ai-securitycommand-and-controlexploit-frameworks+8
300
grisuno/lazyownRed team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 karmanya03/overthrone
All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
 purpleailab/decepticon
Autonomous Hacking Agent for Red Team
 mrhenrike/embedxpl-forge
Embedded Device Security Assessment Framework — 700 modules, 350 CVEs, 55 vendors, APT Group Engine. Covers routers, IP cameras, GPON ONTs, ISP CPEs,…
 cisc0-gif/kitt
Python-Based Pentesting Framework

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 trustedsec/social-engineer-toolkit
The Social-Engineer Toolkit (SET) repository from TrustedSec - All new versions of SET will be deployed here.
 broskigx/oihk-pentesting
Autonomous multi-agent AI penetration-testing engine: a governed tool sandbox, an immutable evidence-and-validation gate, and a reproducible…
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
 aaaguirrep/offensive-docker
Offensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 cream-sec/cve-2019-0708-msf--
CVE-2019-0708-Msf-验证
 edu0x01/hack-tools
Project that brings together several pentest tools
 d3ckx1/omniscan
Multi-engine vulnerability scanner with built-in Nuclei Lite, Afrog, and XRay engines. Features asset discovery via FOFA/Shodan, OOB interaction…
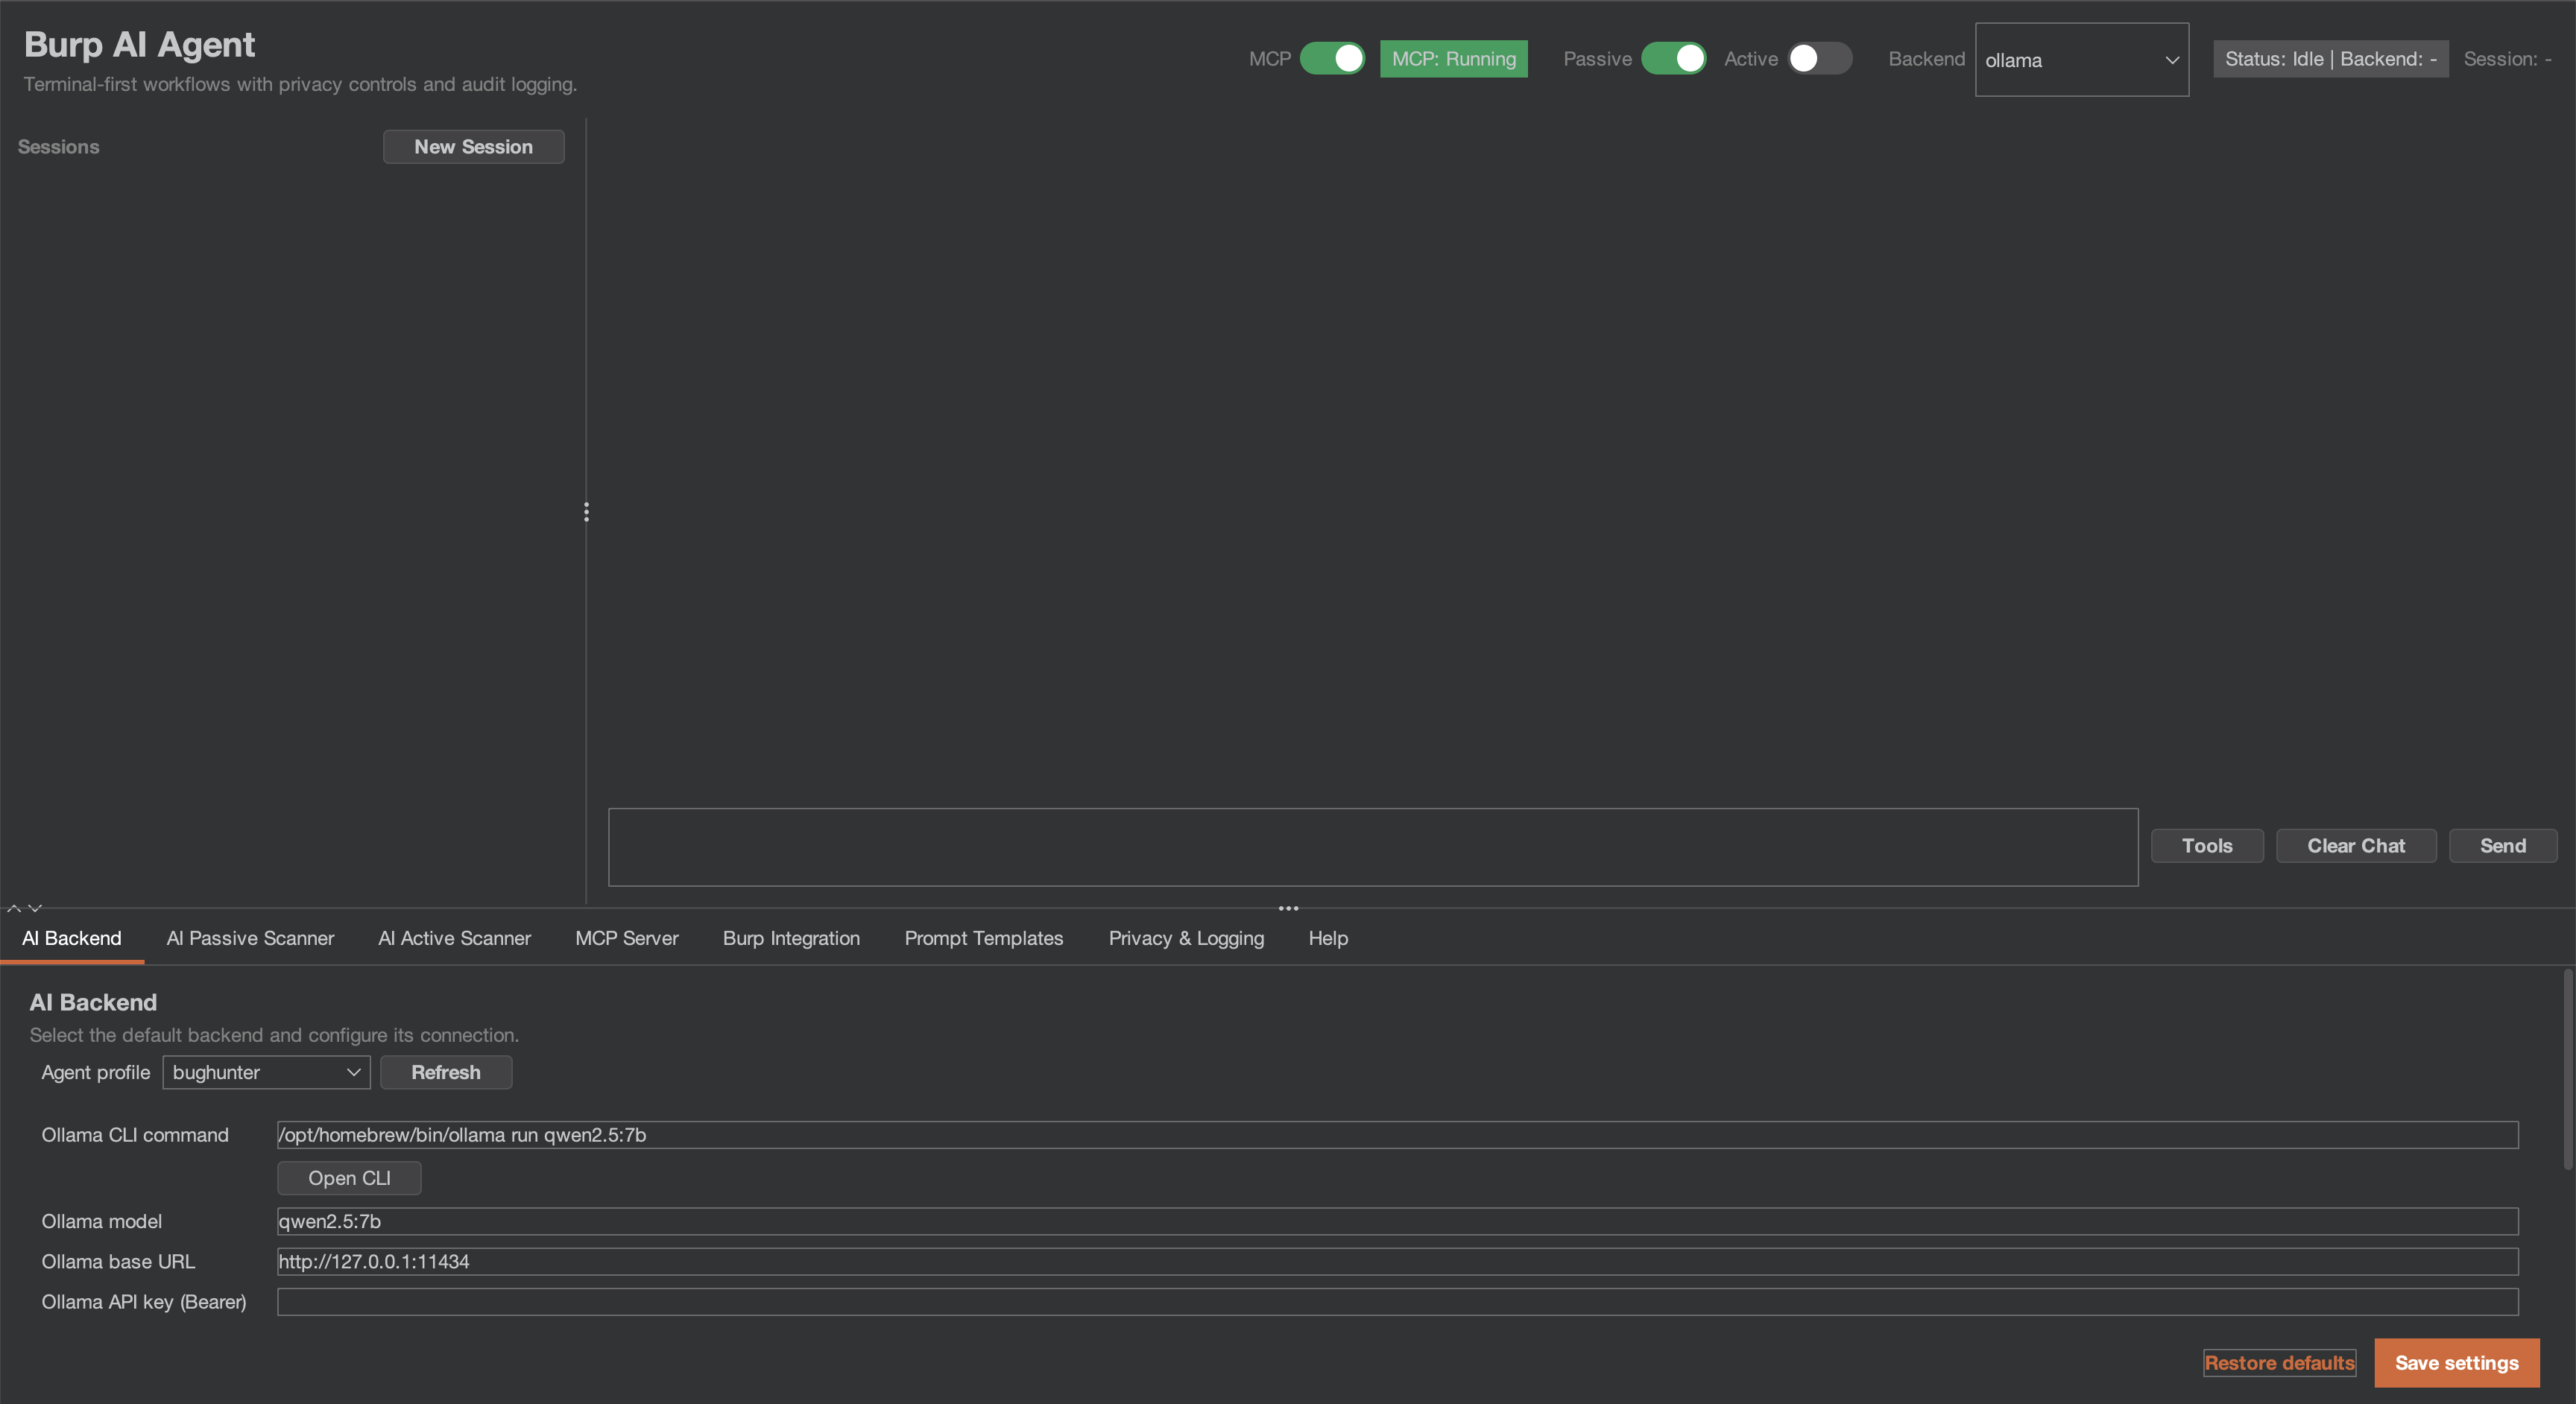 six2dez/burp-ai-agent
Burp Suite extension that adds built-in MCP tooling, AI-assisted analysis, privacy controls, passive and active scanning and more
 last-emo-boy/rikune
MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
 m4cs/darkspiritz
🌔 Official Repository for DarkSpiritz Penetration Framework | Written in Python 🐍
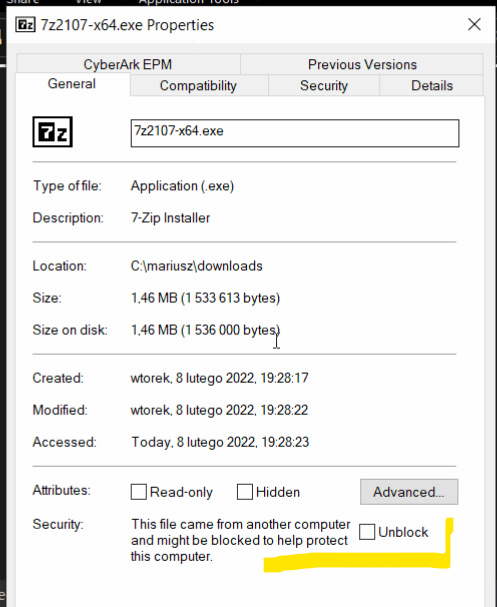 mgeeky/packmypayload
A PoC that packages payloads into output containers to evade Mark-of-the-Web flag & demonstrate risks associated with container file formats.…