

 1n3/findsploit
Find exploits in local and online databases instantly
 plackyhacker/shellcode-encryptor
A simple shell code encryptor/decryptor/executor to bypass anti virus.
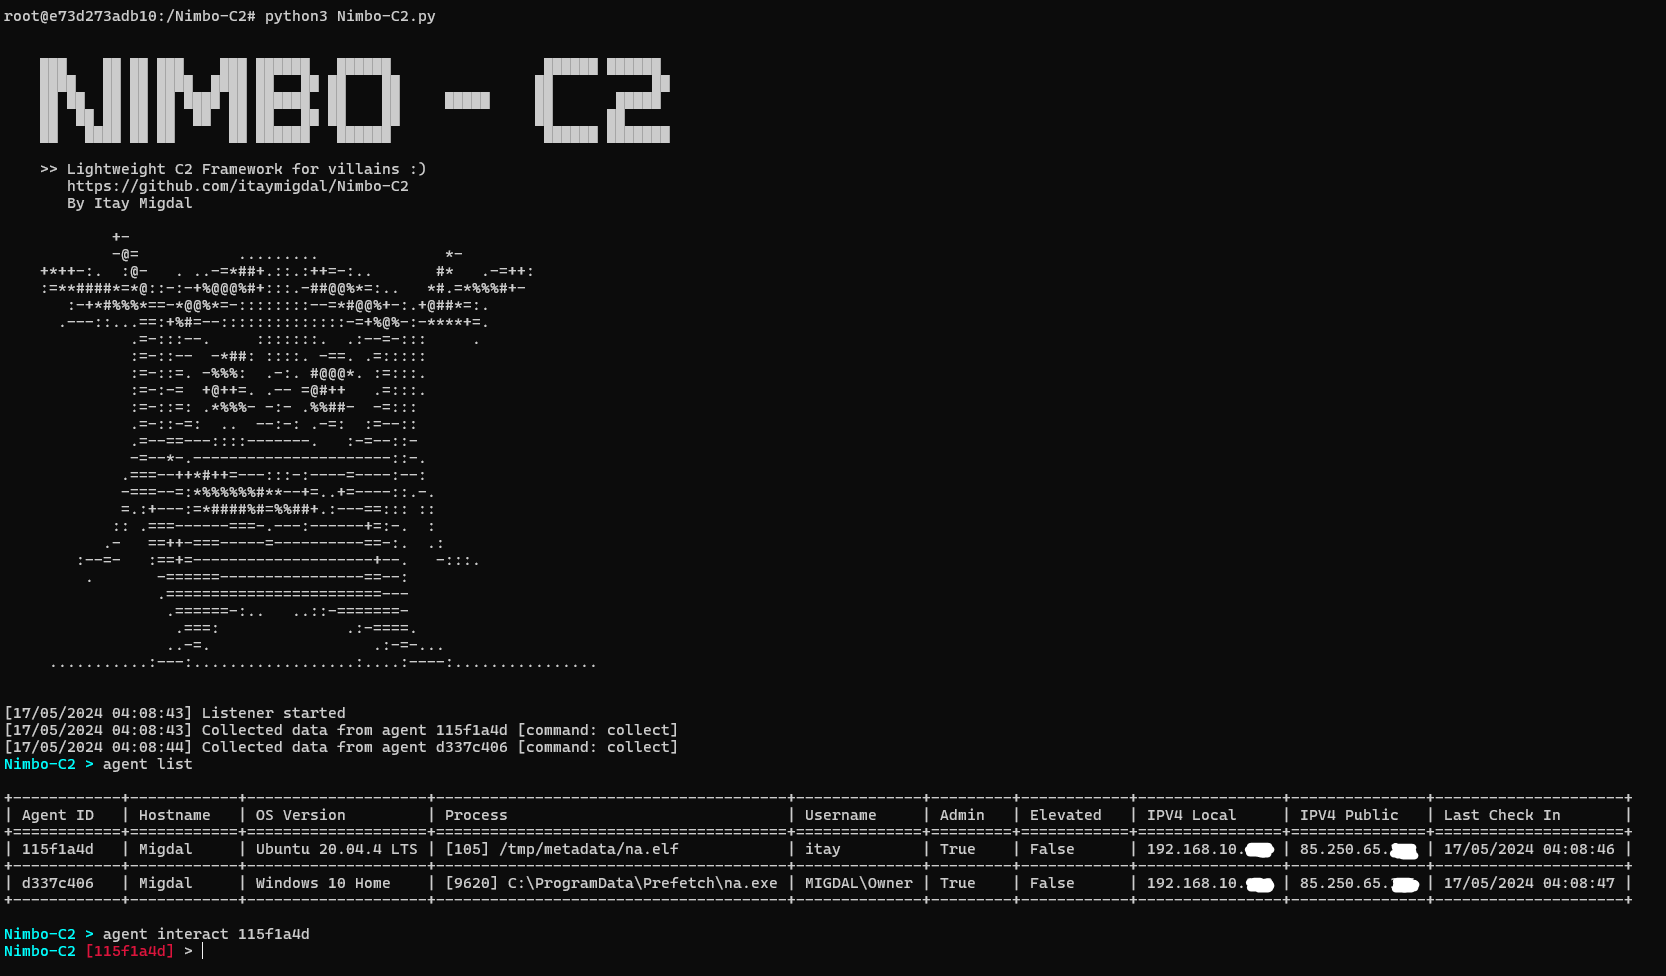 itaymigdal/nimbo-c2
Nimbo-C2 is yet another (simple and lightweight) C2 framework
 erarnitox/malvexc2
A simple C2 Framework written in modern C++
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 codextf2/customc2channeltemplate
template for developing custom C2 channels for Cobalt Strike using IAT hooks applied by a reflective loader.
 kcarretto/paragon
Red Team engagement platform with the goal of unifying offensive tools behind a simple UI
 enelg52/kittystager
KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…
 nova-master/cve-2022-21894-payload-new
C-based payload for CVE-2022-21894 that maps a second stage payload to call EFI services, extending the original PoC for Secure Boot bypass…
 samueltulach/voidmap
Using CVE-2021-40449 to manual map kernel mode driver
 f4t1h21/cve-2021-3560-polkit-dbus
f4T1H's PoC script for CVE-2021-3560 Polkit D-Bus Privilege Escalation
 x04000/cve-2021-4034
Pre-built PWNKIT exploit for CVE-2021-4034, a local privilege escalation vulnerability, providing a ready-to-use payload for educational testing.
 averagesecurityguy/c2
A simple, extensible C&C beaconing system.
 34zy/githarvest3r
Simple CVE github exploit gathering tool written in python.
 scent2d/poc-cve-2021-4034
Proof-of-concept exploit for CVE-2021-4034 (PwnKit), a local privilege escalation vulnerability in polkit's pkexec. Demonstrates exploitation and…
 rpranshu/autopwn
A simple bash based metasploit automation tool!
 kirill89/cve-2021-4034
Dockerized exploit for Polkit privilege escalation (CVE-2021-4034) that grants root access via pkexec, with a simple script to run and verify.