

sqlmap
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
api-securityapi-security-testingcrawler+12
sqlmapproject/sqlmapAutomatic SQL injection and database takeover tool
 xaitax/sploitscan
Aggregates CVE details, exploit databases, and EPSS scores with AI risk assessment and vulnerability scanner import for prioritized patching.
 dana-at-cp/backdoor-apk
backdoor-apk is a shell script that simplifies the process of adding a backdoor to any Android APK file. Users of this shell script should have…
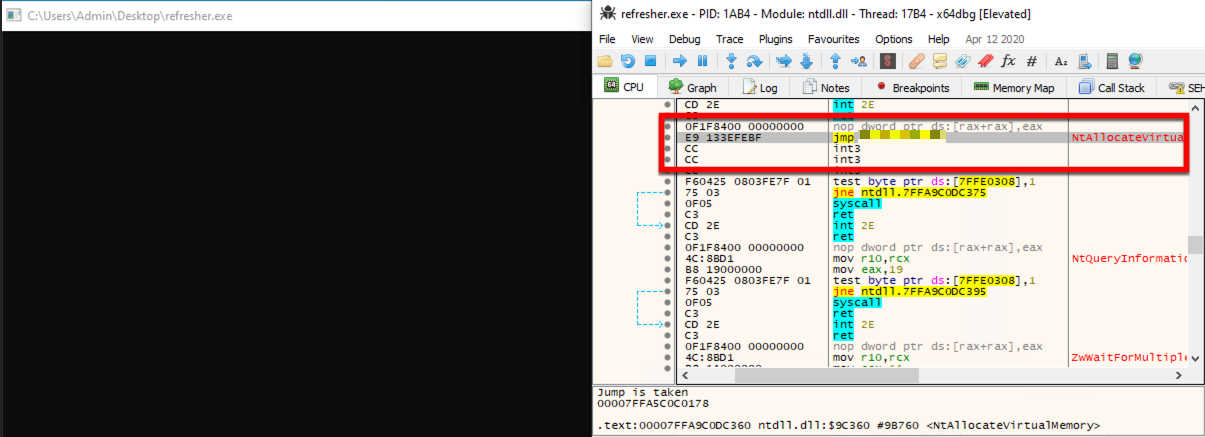 optiv/scarecrow
ScareCrow - Payload creation framework designed around EDR bypass.
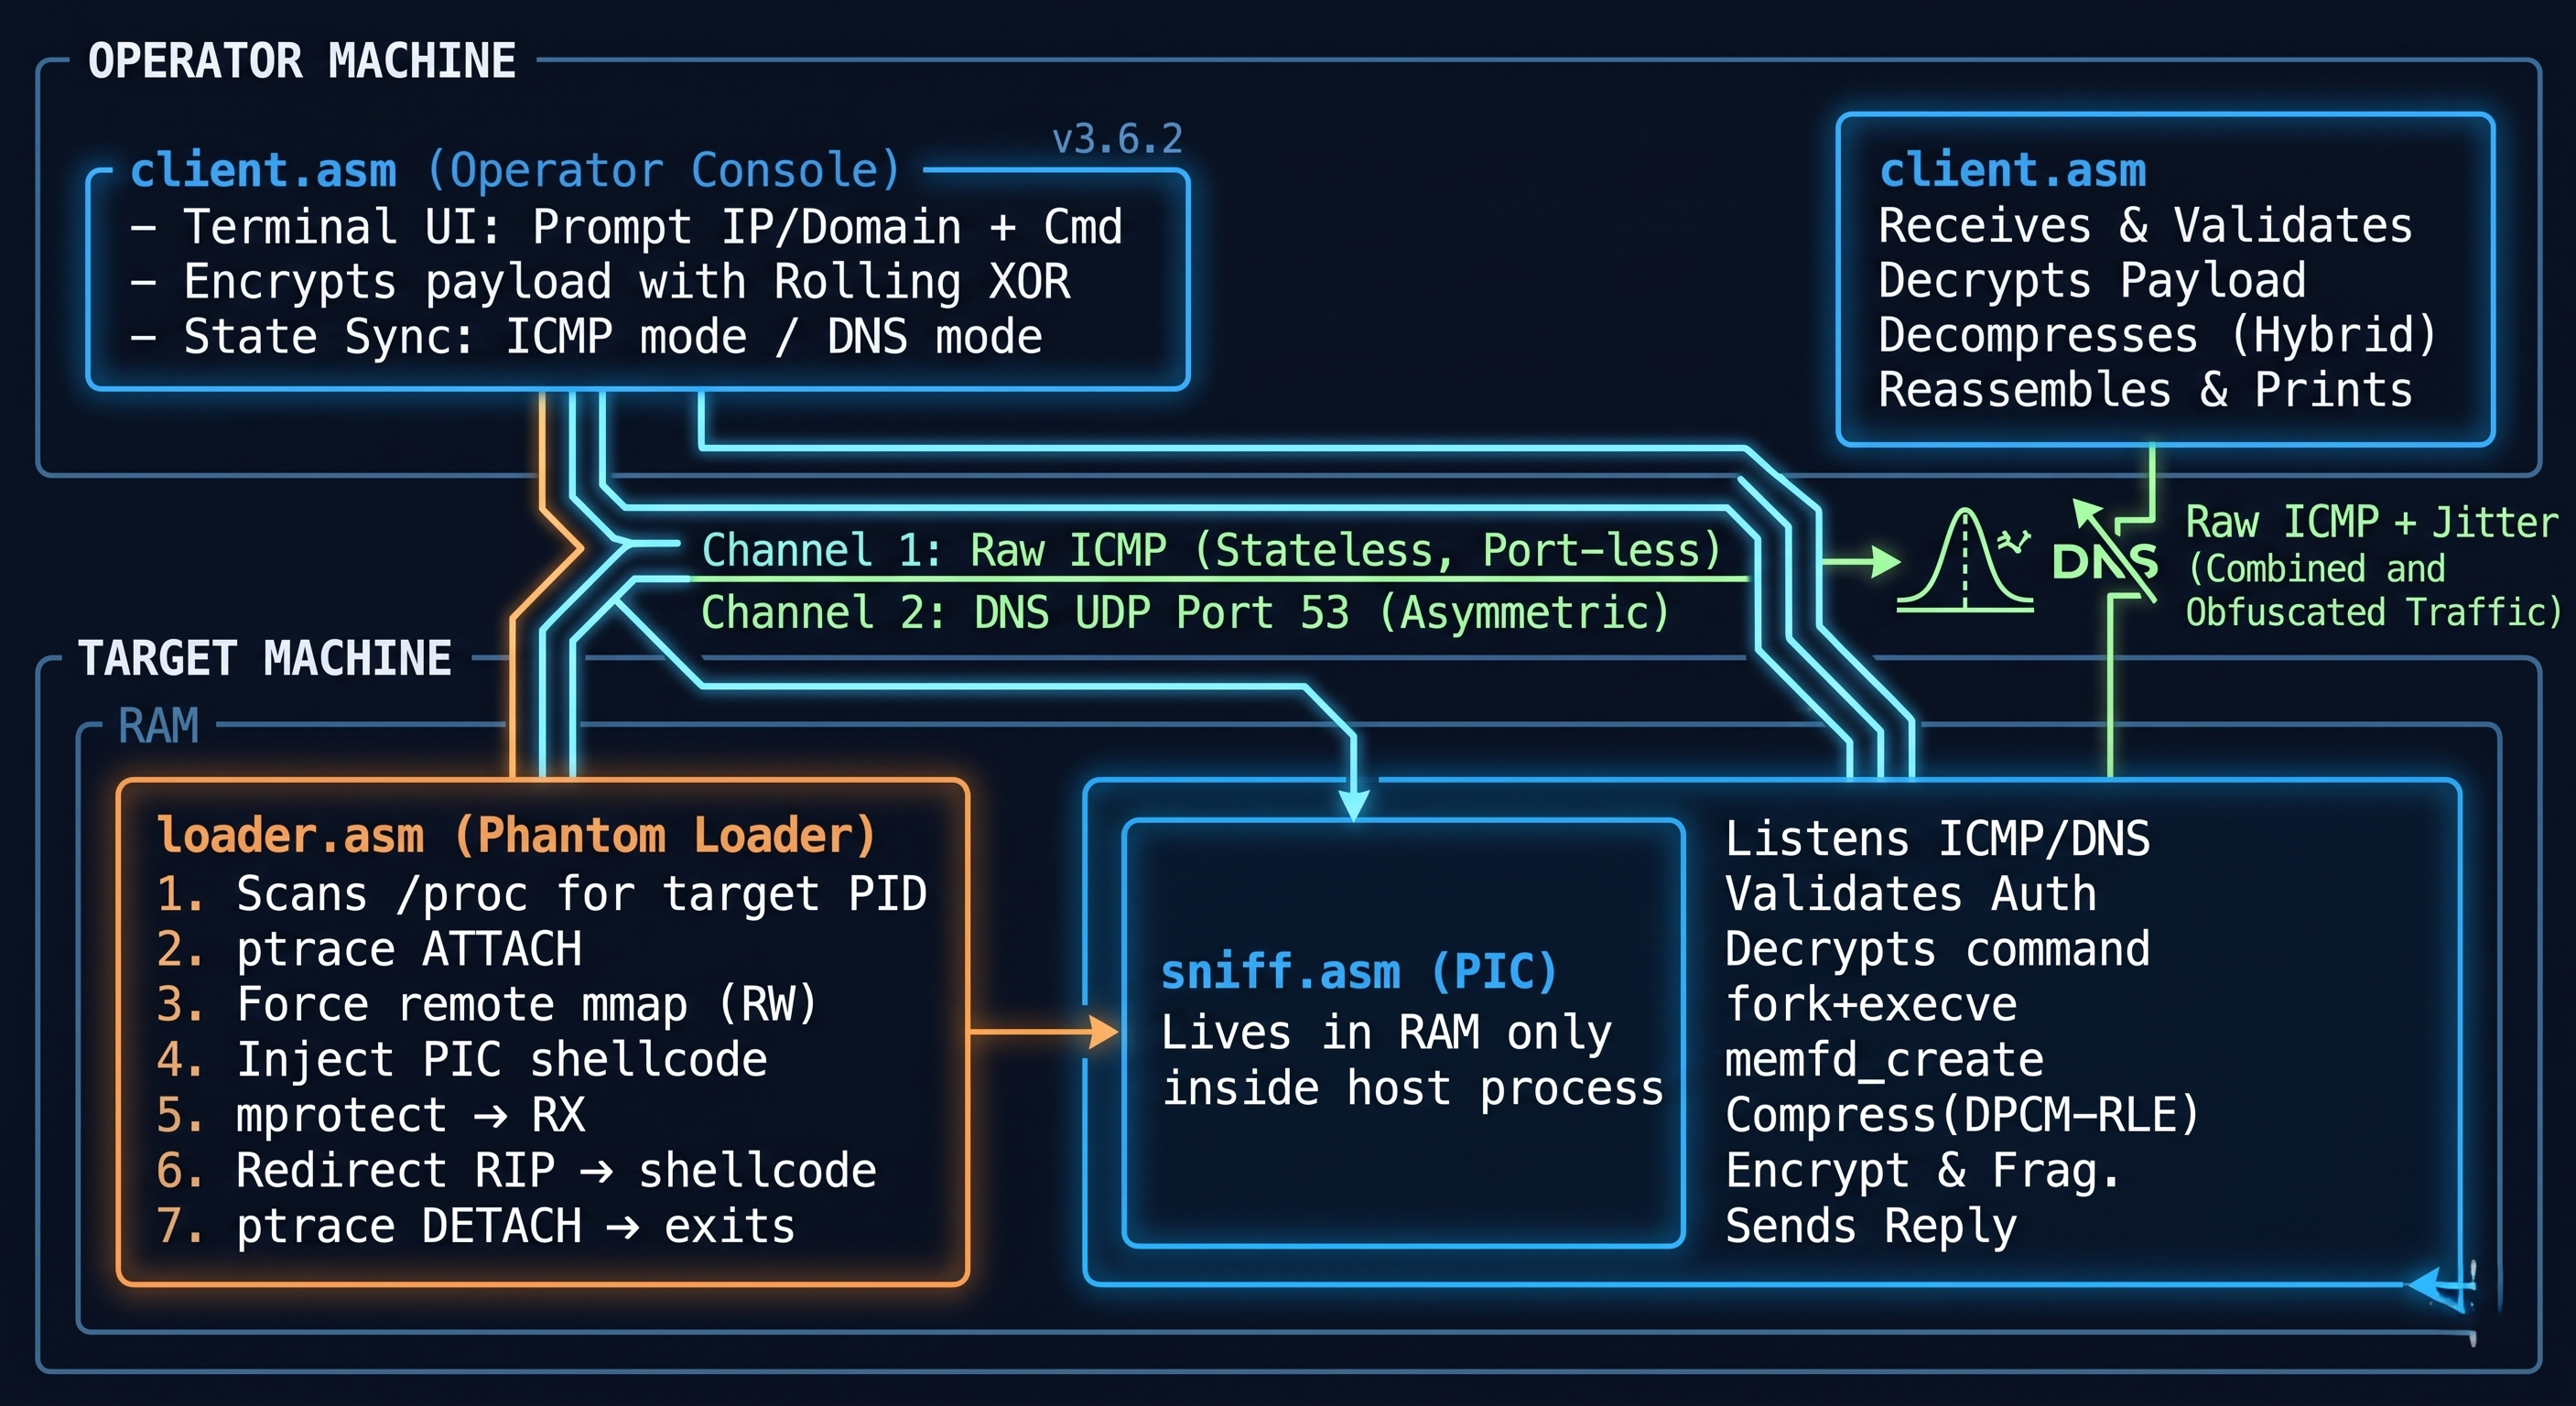 jm00nj/icmp-ghost-a-fileless-x64-assembly-c2-agent
Fileless x64 Assembly C2 framework with dual-channel ICMP/DNS protocol pivoting, direct syscall execution, and ptrace-based process injection for…
 tarpeg007/cve-2026-74586
Unprivileged proof-of-concept for CVE-2026-74586, a Linux kernel SCTP ASCONF use-after-free. Provides a raw-packet trigger, reliability metrics, and…
 magicbytes/magicarch
MagicArch is a comprehensive post-installation script built with Ansible, designed to transform a basic Arch Linux installation into a fully equipped…
 mwemuorg/mwemu
Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
 sneakynachos/cve-2026-74939-escape-the-mac-n-cheese-box
Firefox content-to-parent IPDL privilege escalation (N-day, bug 2054416): forged PDocumentChannel with RemoteTypeOverride -> privilegedabout process…
 sevagas/macro_pack
macro_pack is a tool by @EmericNasi used to automatize obfuscation and generation of Office documents, VB scripts, shortcuts, and other formats for…
 b4rtik/redpeanut
RedPeanut is a small RAT developed in .Net Core 2 and its agent in .Net 3.5 / 4.0.
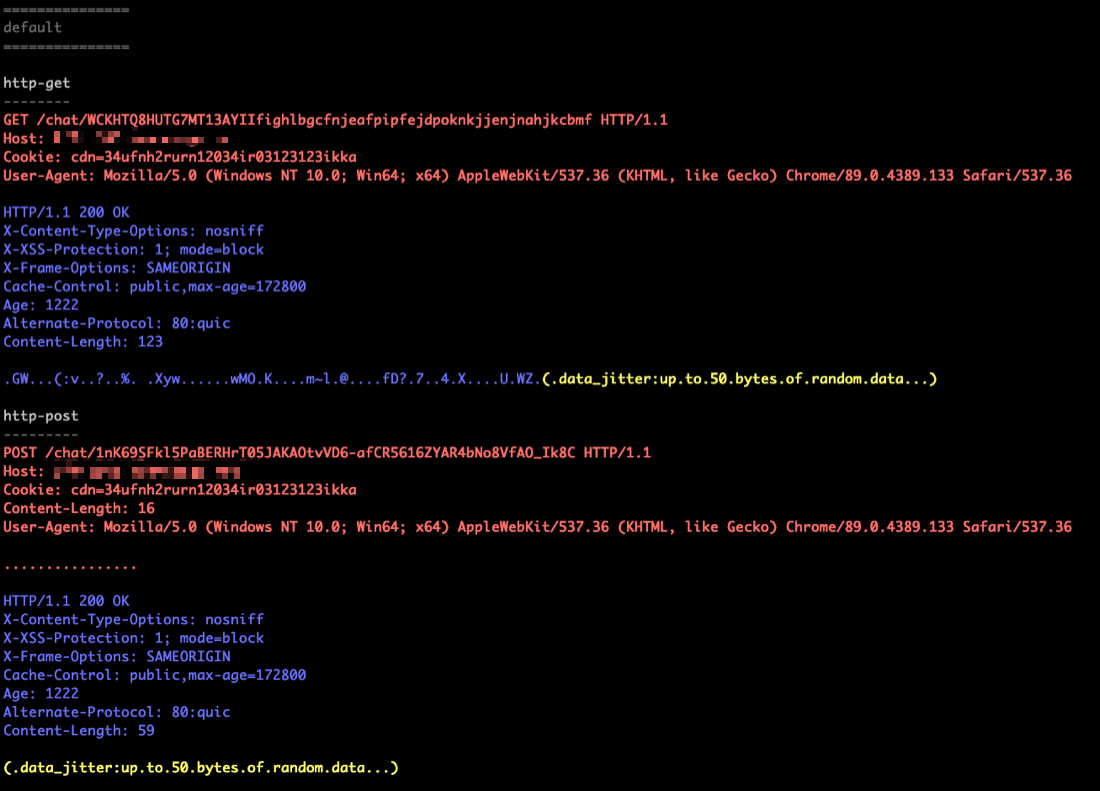 tylous/sourcepoint
Polymorphic C2 profile generator for Cobalt Strike that automates creation of evasive beacon configurations with randomized options for HTTP, DNS,…
 kvakirsanov/cve-2026-31431-live-process-code-injection
Proof-of-concept for CVE-2026-31431 demonstrating live process code injection via page cache, achieving arbitrary code execution in a running process…
 sneakynachos/cve-2026-4692-trust-me-im-in-rdm
Proof-of-concept exploit for Firefox BrowsingContext authorization bypass (CVE-2026-4692), demonstrating forged IPC messages to set InRDMPane and…
 bazad/launchd-portrep
CVE-2018-4280: Mach port replacement vulnerability in launchd on macOS 10.13.5 leading to local privilege escalation and SIP bypass.
 h4rk3nz0/cve-2023-20598-pdfwkrnl
CVE-2023-20598 Kernel Driver - Elevation of Privilege
 boku7/injectamsibypass
Cobalt Strike BOF - Bypass AMSI in a remote process with code injection.
 chompie1337/windows_mskssrv_lpe_cve-2023-36802
Local privilege escalation exploit for CVE-2023-36802 targeting Windows kernel streaming service (MSKSSRV) on Windows 11 22H2, using I/O Ring…