

BEAR-C2
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
adversarial-attackcommand-and-controldata-exfiltration+8
687
s3n4t0r-0x0/bear-c2The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 bishopfox/sliver
Adversary Emulation Framework
 vulnerscom/burp-vulners-scanner
Vulnerability scanner based on vulners.com search API
 taielab/awesome-hacking-lists
A curated collection of top-tier penetration testing tools and productivity utilities across multiple domains. Join us to explore, contribute, and…
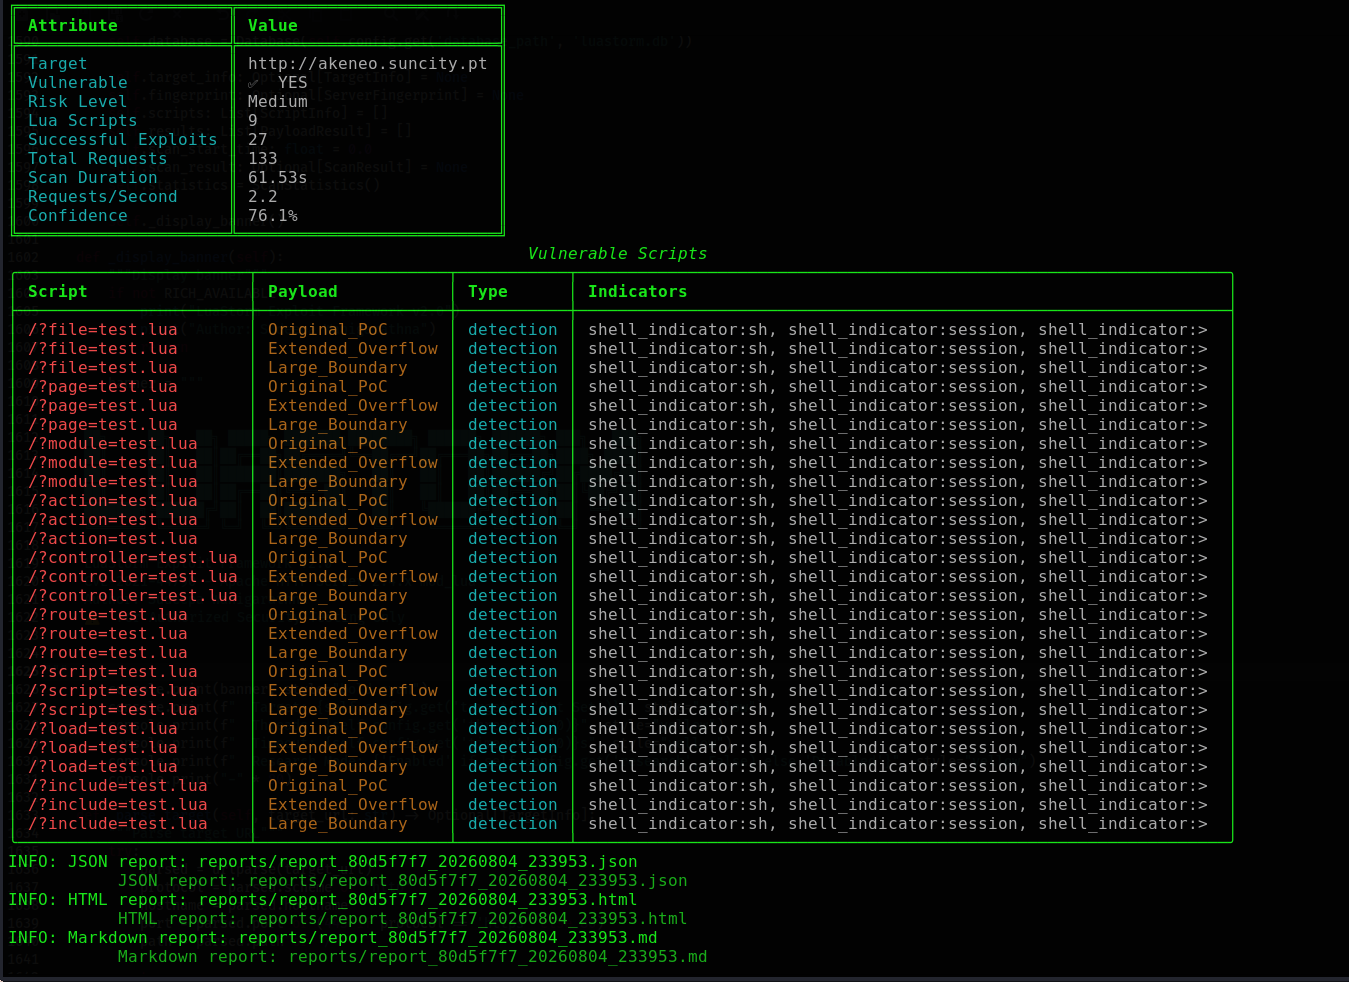 cerberusmrxi/apache-lua-buffer-overflow-exploit-cve-2021-44790
Apache HTTP Server 2.4.x mod_lua Buffer Overflow (CVE-2021-44790) - Advanced exploitation framework with fingerprinting, multi-stage scanning, plugin…
 alienwithin/owasp-mth3l3m3nt-framework
OWASP Mth3l3m3nt Framework is a penetration testing aiding tool and exploitation framework. It fosters a principle of attack the web using the web as…
 r00ts3c/ddos-rootsec
Explore RootSec's DDOS Archive, featuring top-tier scanners, powerful botnets (Mirai & QBot) and other variants, high-impact exploits, advanced…
 omriher/captipper
Malicious HTTP traffic explorer

 d0ubl3g/industrial-security-auditing-framework
ISAF aims to be a framework that provides the necessary tools for the correct security audit of industrial (OT) environments.
 zeop-cybersec/apache_normalize_path
Metasploit-Framework modules (scanner and exploit) for the CVE-2021-41773 and CVE-2021-42013 (Path Traversal in Apache 2.4.49/2.4.50)
 jephthai/evilvm
Forth-based compiler deployed as position-independent x86_64 shellcode, providing a remote code execution agent with interactive REPL over TCP, HTTP,…
 abdurahmon3236/cve-2024-38472
Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.
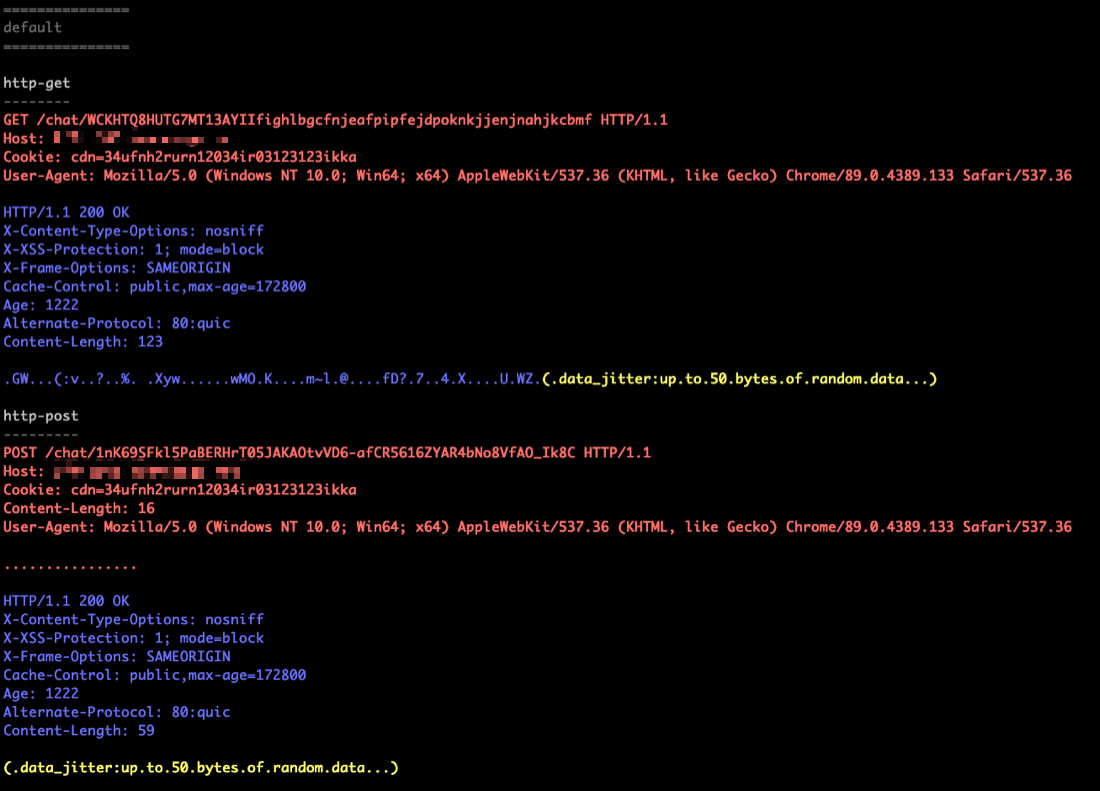 tylous/sourcepoint
Polymorphic C2 profile generator for Cobalt Strike that automates creation of evasive beacon configurations with randomized options for HTTP, DNS,…
 codextf2/openmalleablec2
Open Source Implementation of Cobalt Strike's Malleable C2
 jeanback1/cve-2019-0211-exploit
Local privilege escalation exploit for CVE-2019-0211 targeting Apache HTTP Server 2.4.17-2.4.38 with mod_php. Uses UAF in PHP to corrupt Apache…
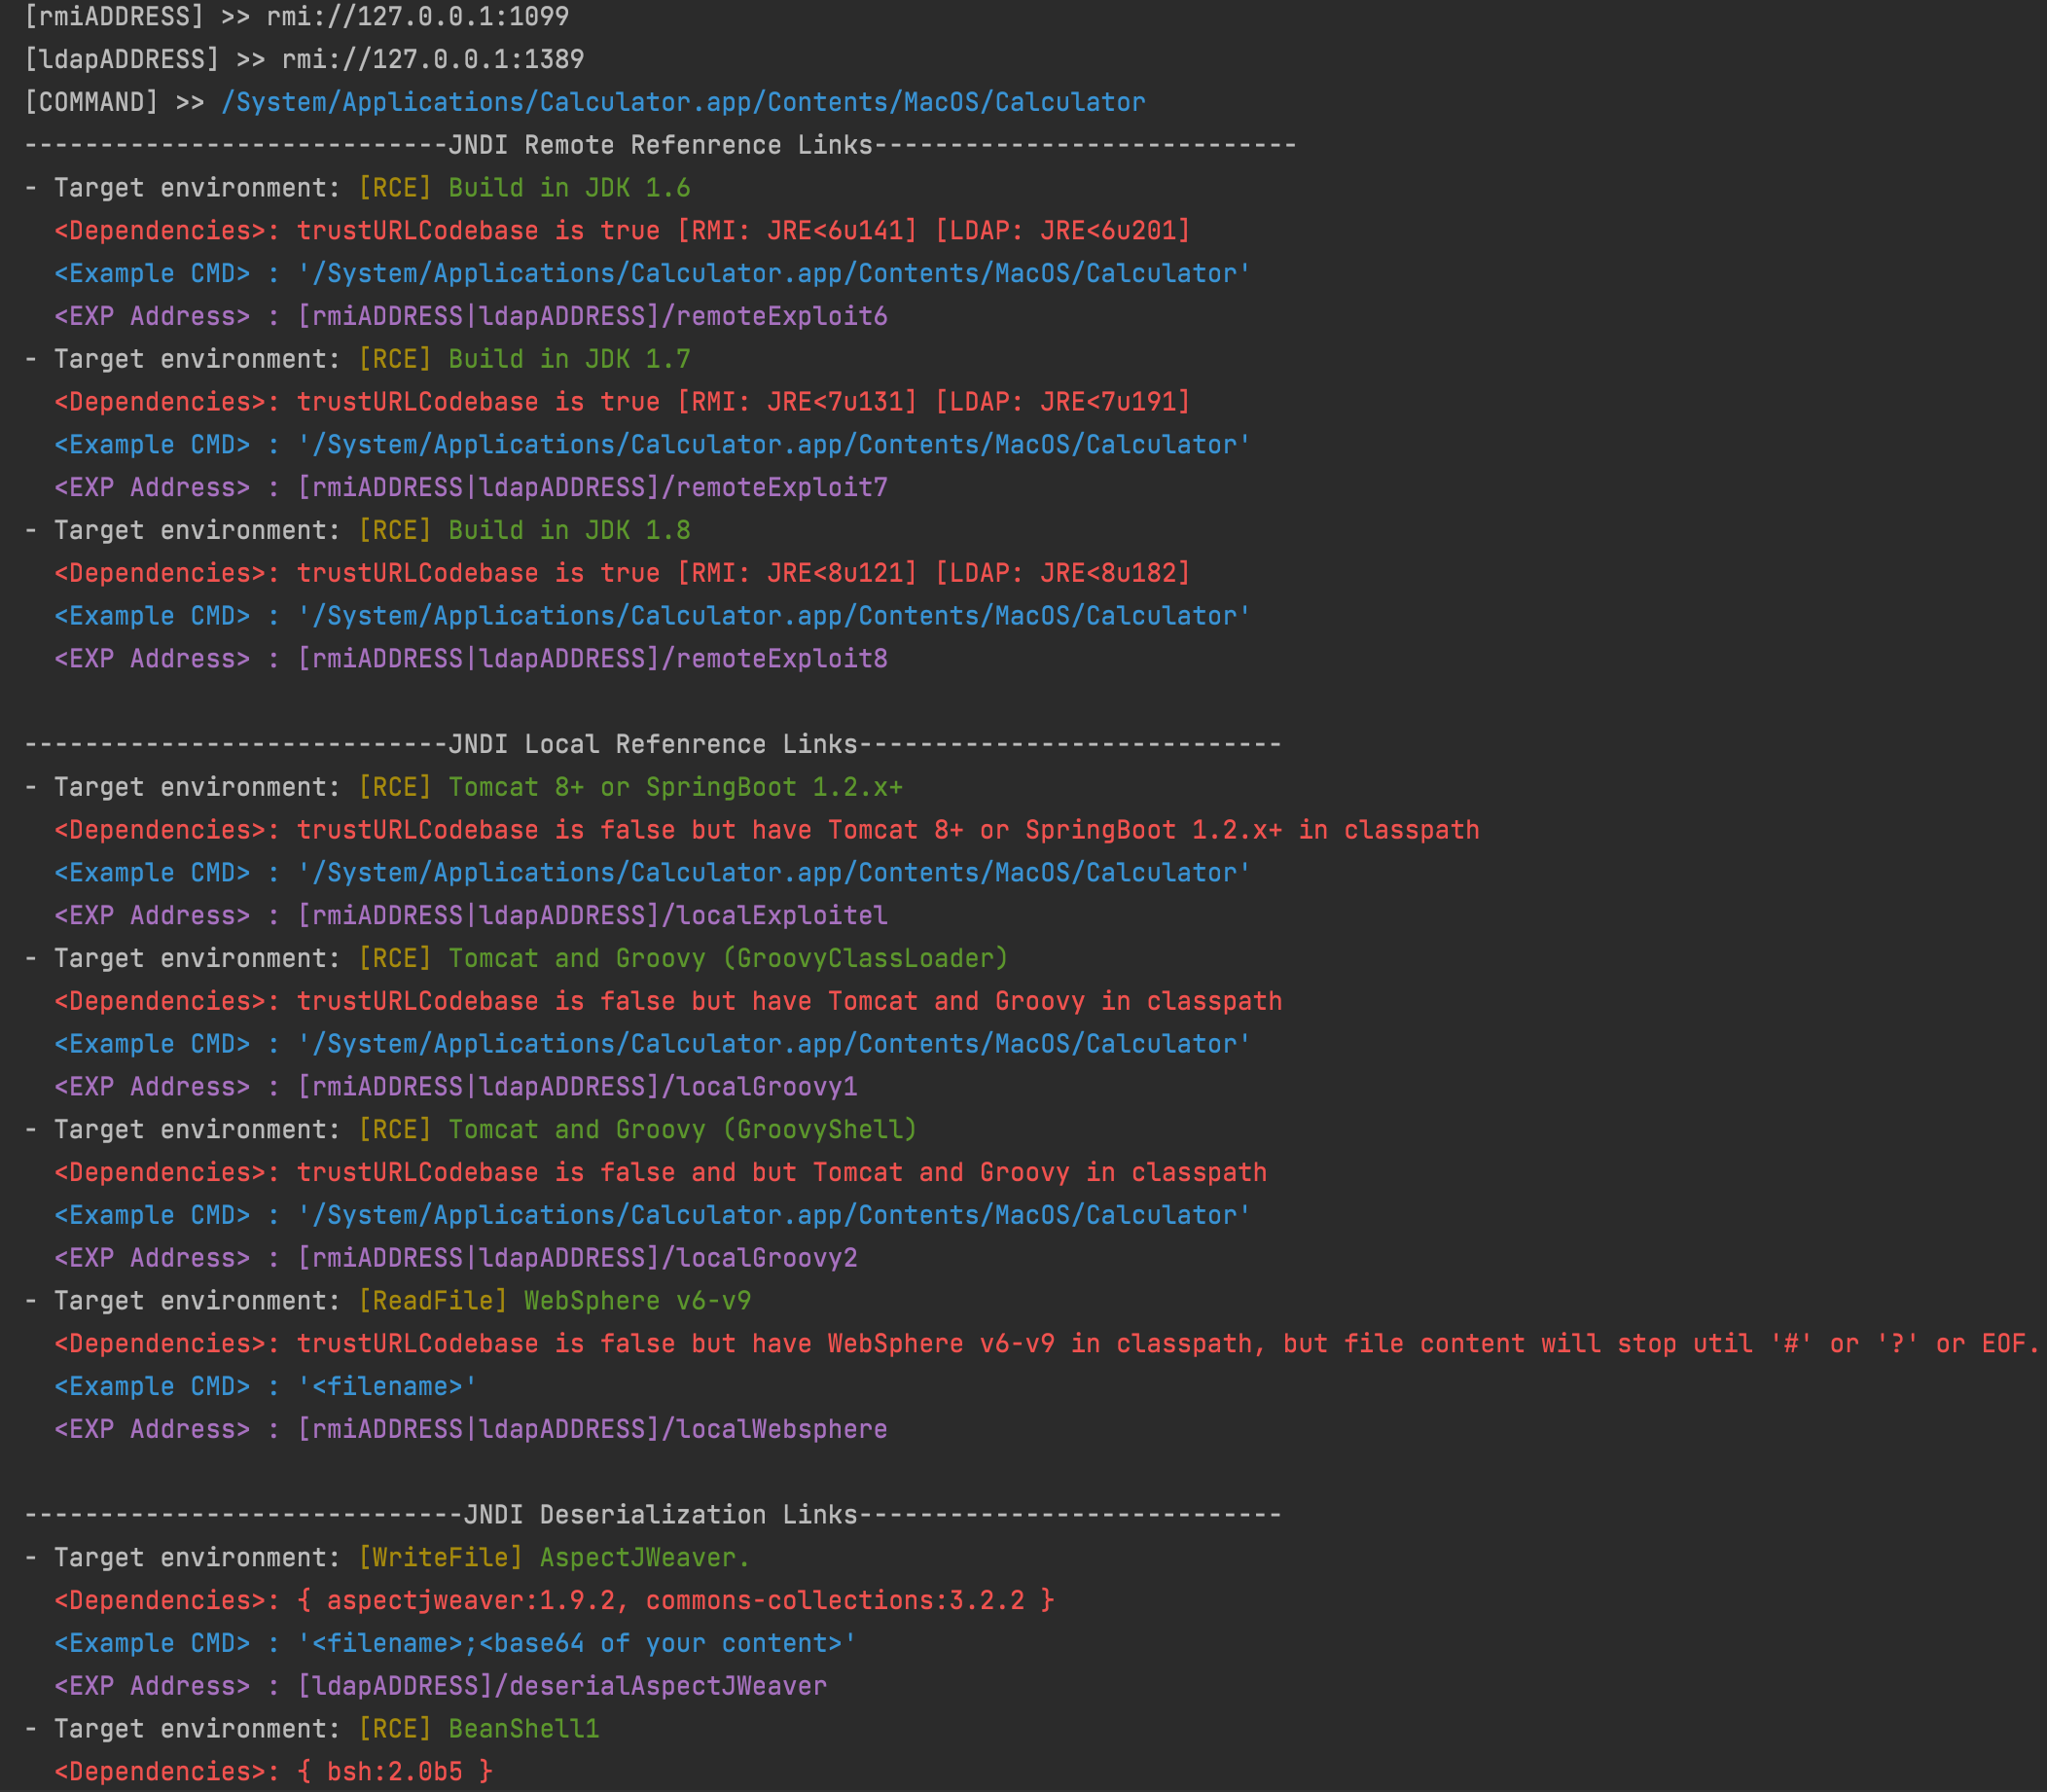 cckuailong/jndi-injection-exploit-plus
Generates workable JNDI injection links and deserialization payloads with 80+ gadgets, supporting RMI, LDAP, and HTTP servers for automated…
 gr1mmie/atlasc2
C# C2 Framework centered around Stage 1 operations
 vanshuk-bhagat/apache-http-server-vulnerabilities-cve-2021-41773-and-cve-2021-42013
In this project, I documented a detailed penetration testing process targeting Apache HTTP Server vulnerabilities, specifically CVE-2021-41773 and…