
CryKeX
 cryptolok/crykex
Linux Memory Cryptographic Keys Extractor
cryptographydigital-forensicsencryption-decryption-tools+2
cryptolok/crykexLinux Memory Cryptographic Keys Extractor
 iss4cf0ng/openpetya
A Proof-of-Concept bootkit and UEFI boot application inspired by Petya ransomware, written in Assembly, C, and C++
 carmaa/interrogate
Interrogate is a proof-of-concept tool for identification of cryptographic keys in binary material (regardless of target operating system), first and…
 gmh5225/eac-kernel-packet-fucker
Reverse-engineered Easy Anti-Cheat kernel driver bypass that intercepts memory allocation to suppress violation packets, with report decryption…
 awnumar/memguard
Software sandbox for storage of sensitive information in memory.
 freax13/cve-2024-21980-poc
Exploit for CVE-2024-21980 targeting AMD SEV firmware to decrypt arbitrary memory of decommissioned SEV-SNP guests via a command buffer enforcement…
 freax13/cve-2024-21978-poc
Exploit for AMD SEV-SNP firmware vulnerability CVE-2024-21978, enabling decryption of arbitrary guest memory via memory corruption of context pages.
 freax13/cve-2023-31355-poc
Exploit for AMD SEV-SNP firmware vulnerability (CVE-2023-31355) that decrypts arbitrary memory of decommissioned guests by corrupting the UMC key…
 egebalci/amber
Reflective PE packer.
 wack0/cve-2022-21894
baton drop (CVE-2022-21894): Secure Boot Security Feature Bypass Vulnerability
 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
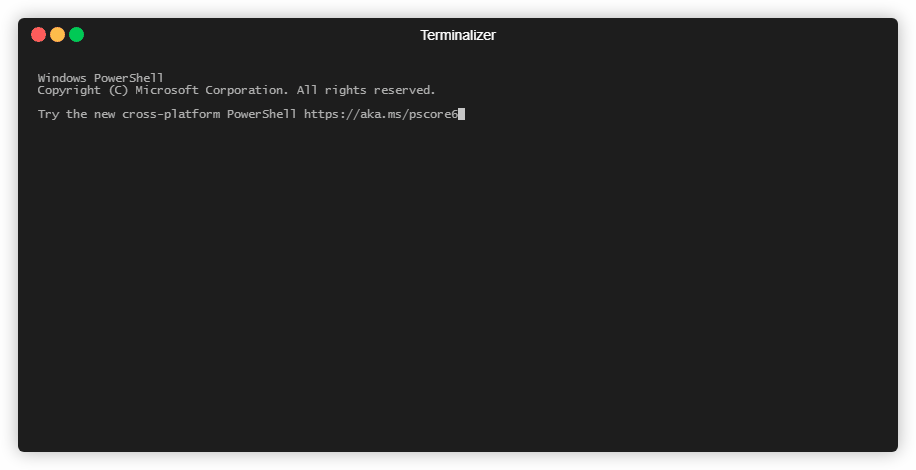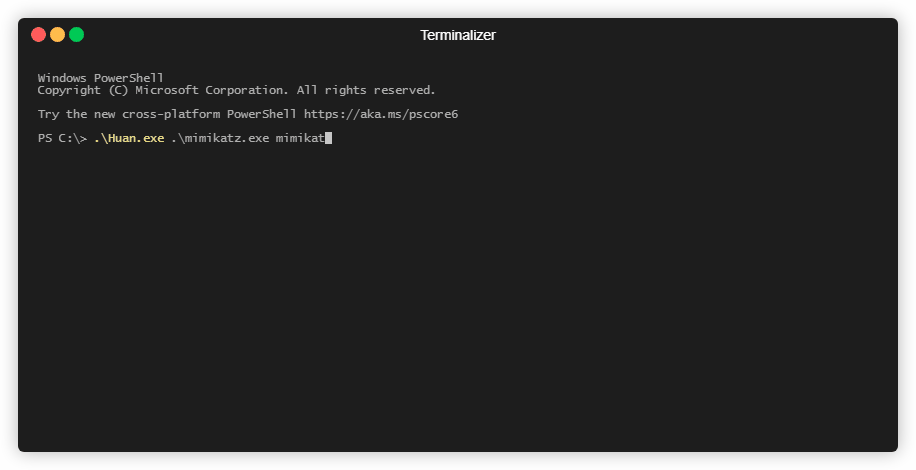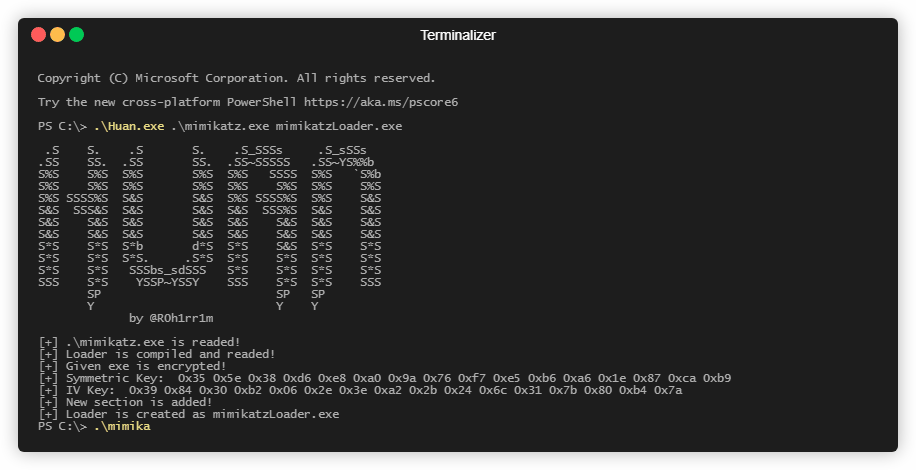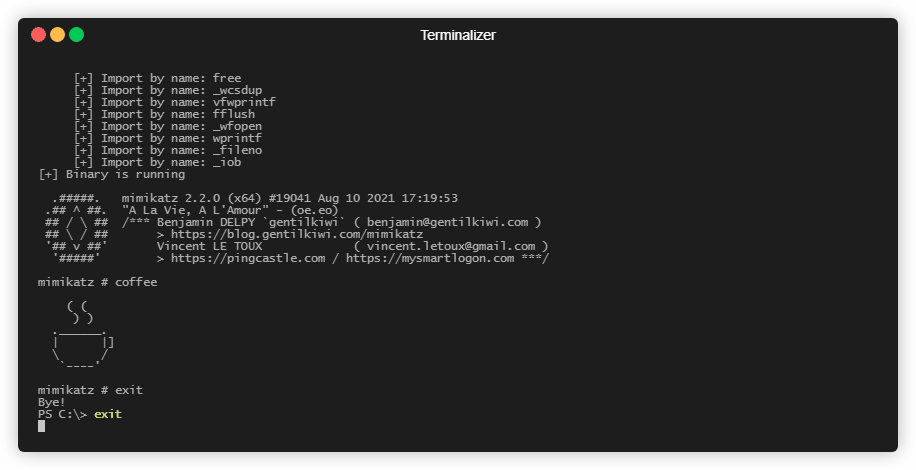 frkngksl/huan
Encrypted PE Loader Generator
 chaelsoo/hollow
A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
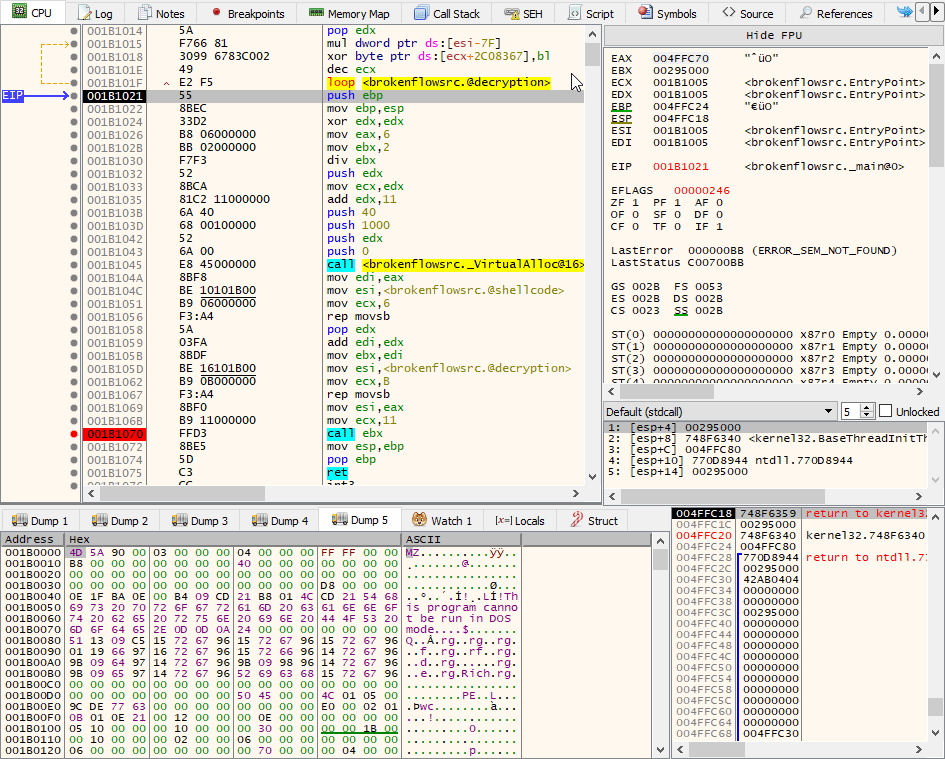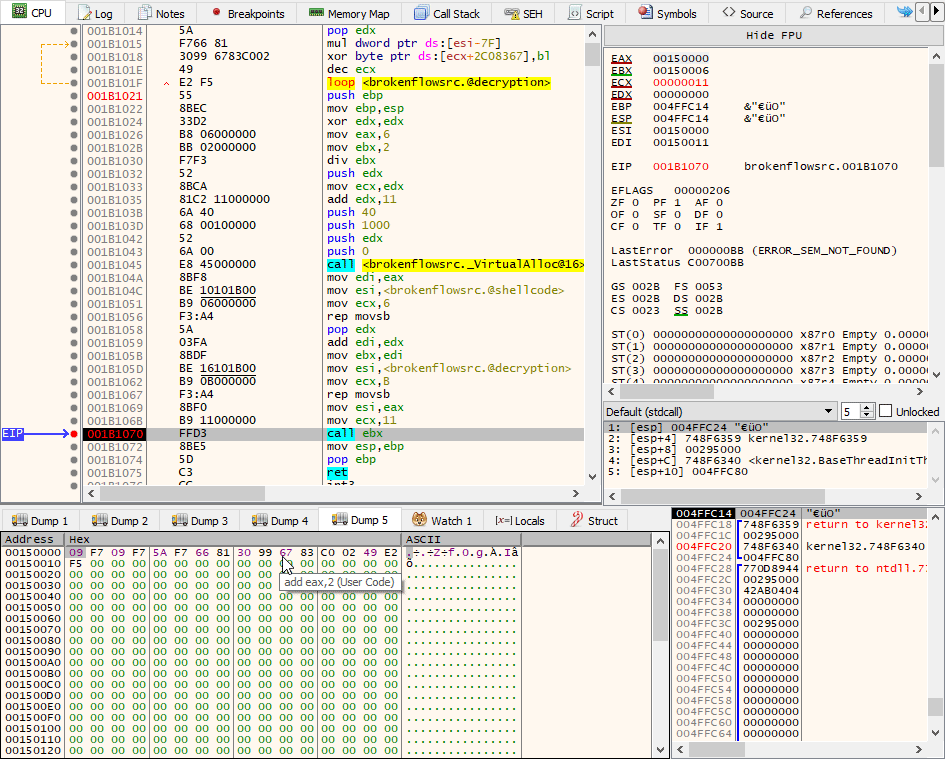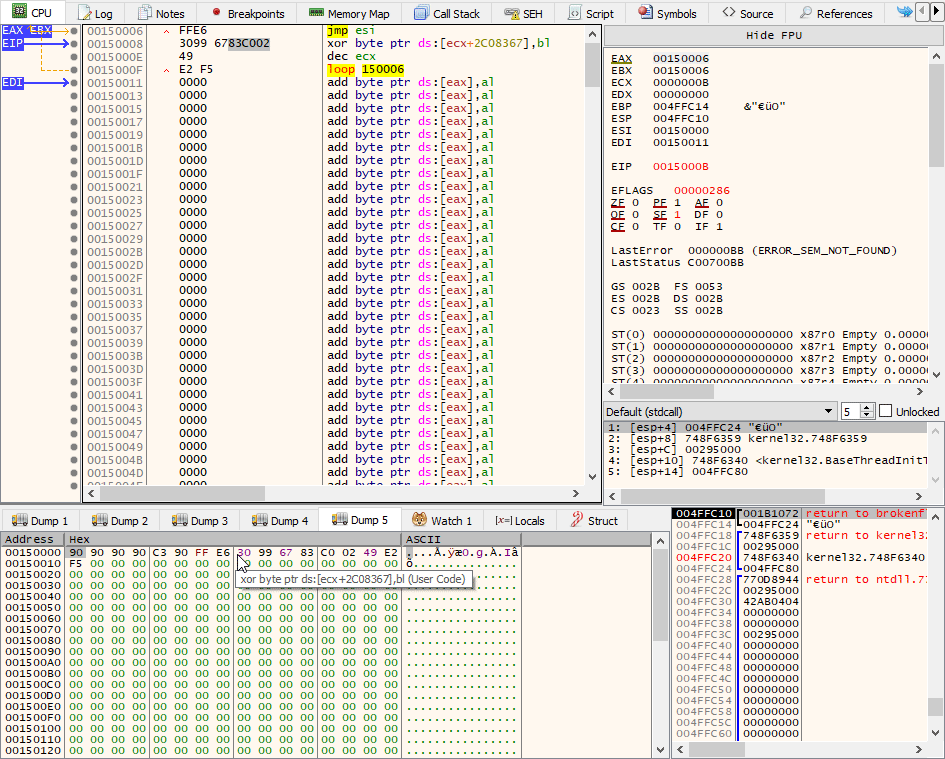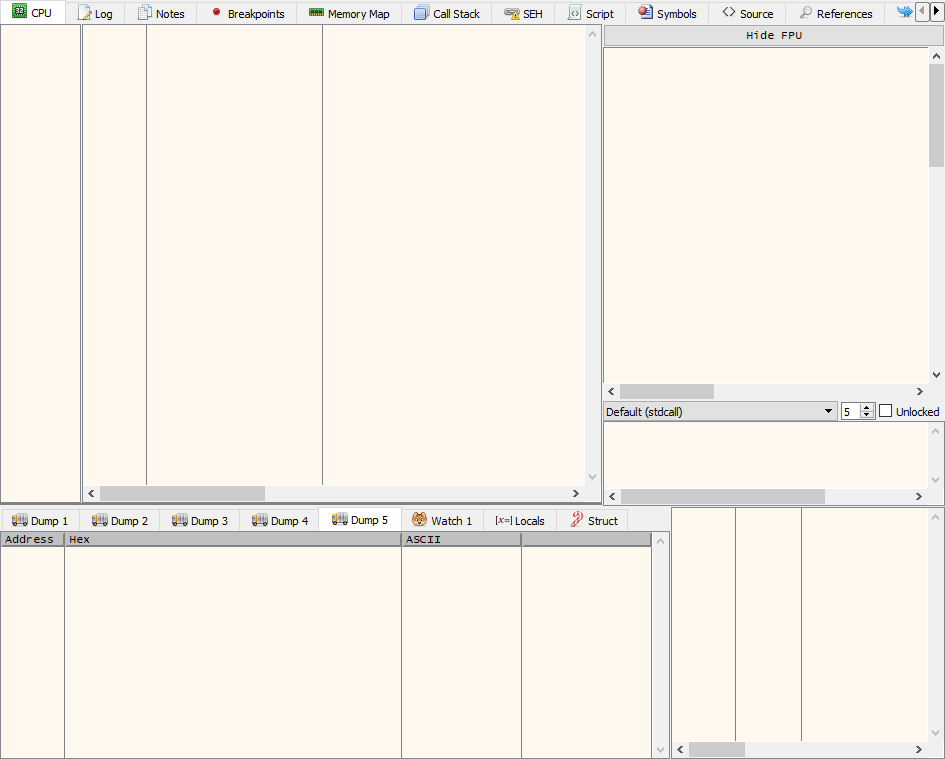 enkomio/brokenflow
A simple PoC to invoke an encrypted shellcode by using an hidden call
 gentilkiwi/curveball
CVE-2020-0601 exploit tool that computes alternative ECC private keys from public certificates, enabling certificate spoofing via curve parameter…
 syrins/cve-2025-8088-winrar-tool-gui
A Windows GUI tool demonstrating a proof-of-concept archive traversal technique related to CVE-2025-8088 using WinRAR’s CLI. Allows building crafted…
 vortexcry-organization/vortexcry-ransomware-release
Advanced ransomware using process injection and kernel driver loading via CVE-2019-16098 to encrypt files, disable recovery, and demand ransom. For…
 aurh1l-42-projects/woody-woodpacker
ELF binary packer that encrypts code sections and injects a runtime decryption stub for 64-bit Linux executables, demonstrating code injection and…