
test-certs-site
 letsencrypt/test-certs-site
A simple server to host the valid, revoked, and expired certificates required by Section 2.2 of the CA/Browser Forum Baseline Requirements.
api-security-testingdevsecopsencryption-decryption-tools+1
25
letsencrypt/test-certs-siteA simple server to host the valid, revoked, and expired certificates required by Section 2.2 of the CA/Browser Forum Baseline Requirements.
 loserlab/bigint-buffer-safe
Safe, pure-JS drop-in replacement for bigint-buffer. Fixes CVE-2025-3194 (CVSS 7.5). Zero dependencies, no native bindings.
 open-quantum-safe/liboqs
C library for prototyping and experimenting with quantum-resistant cryptography
 blasty/sonos
Exploit and tooling for Amlogic-based Sonos devices: dumps OTP/eFUSE via an EL3 exploit, extracts LUKS decryption keys, and fetches/decrypts OTA…
 eremiel/cve-2019-5420
Python exploit script for CVE-2019-5420, targeting Ruby on Rails signed-session AES GCM key brute-forcing to achieve remote code execution in…
 wack0/cve-2022-21894
baton drop (CVE-2022-21894): Secure Boot Security Feature Bypass Vulnerability
 hazcod/ransomwhere
A PoC ransomware sample to test out your ransomware response strategy.
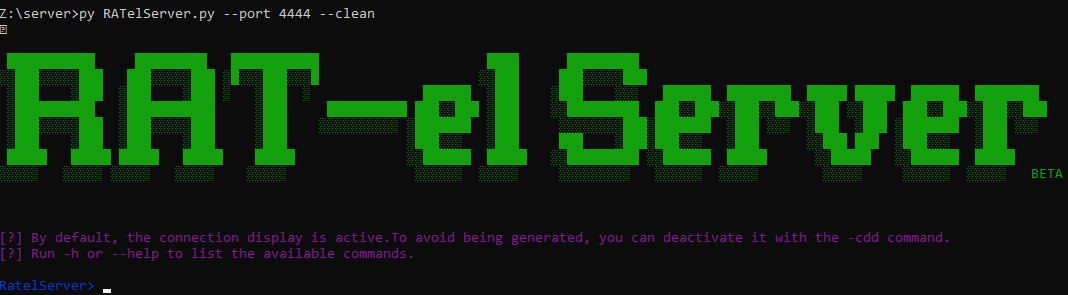 frenchcisco/ratel
RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…
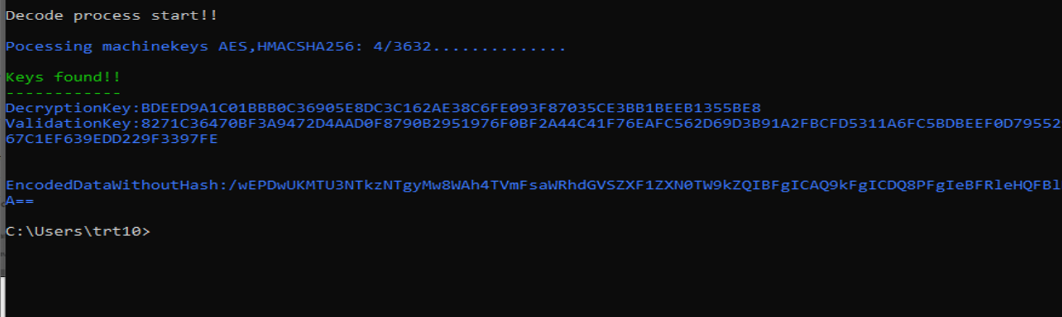 orwagodfather/aspdotnetwrapper-edited-
This Tool To Test Machine Keys In View State
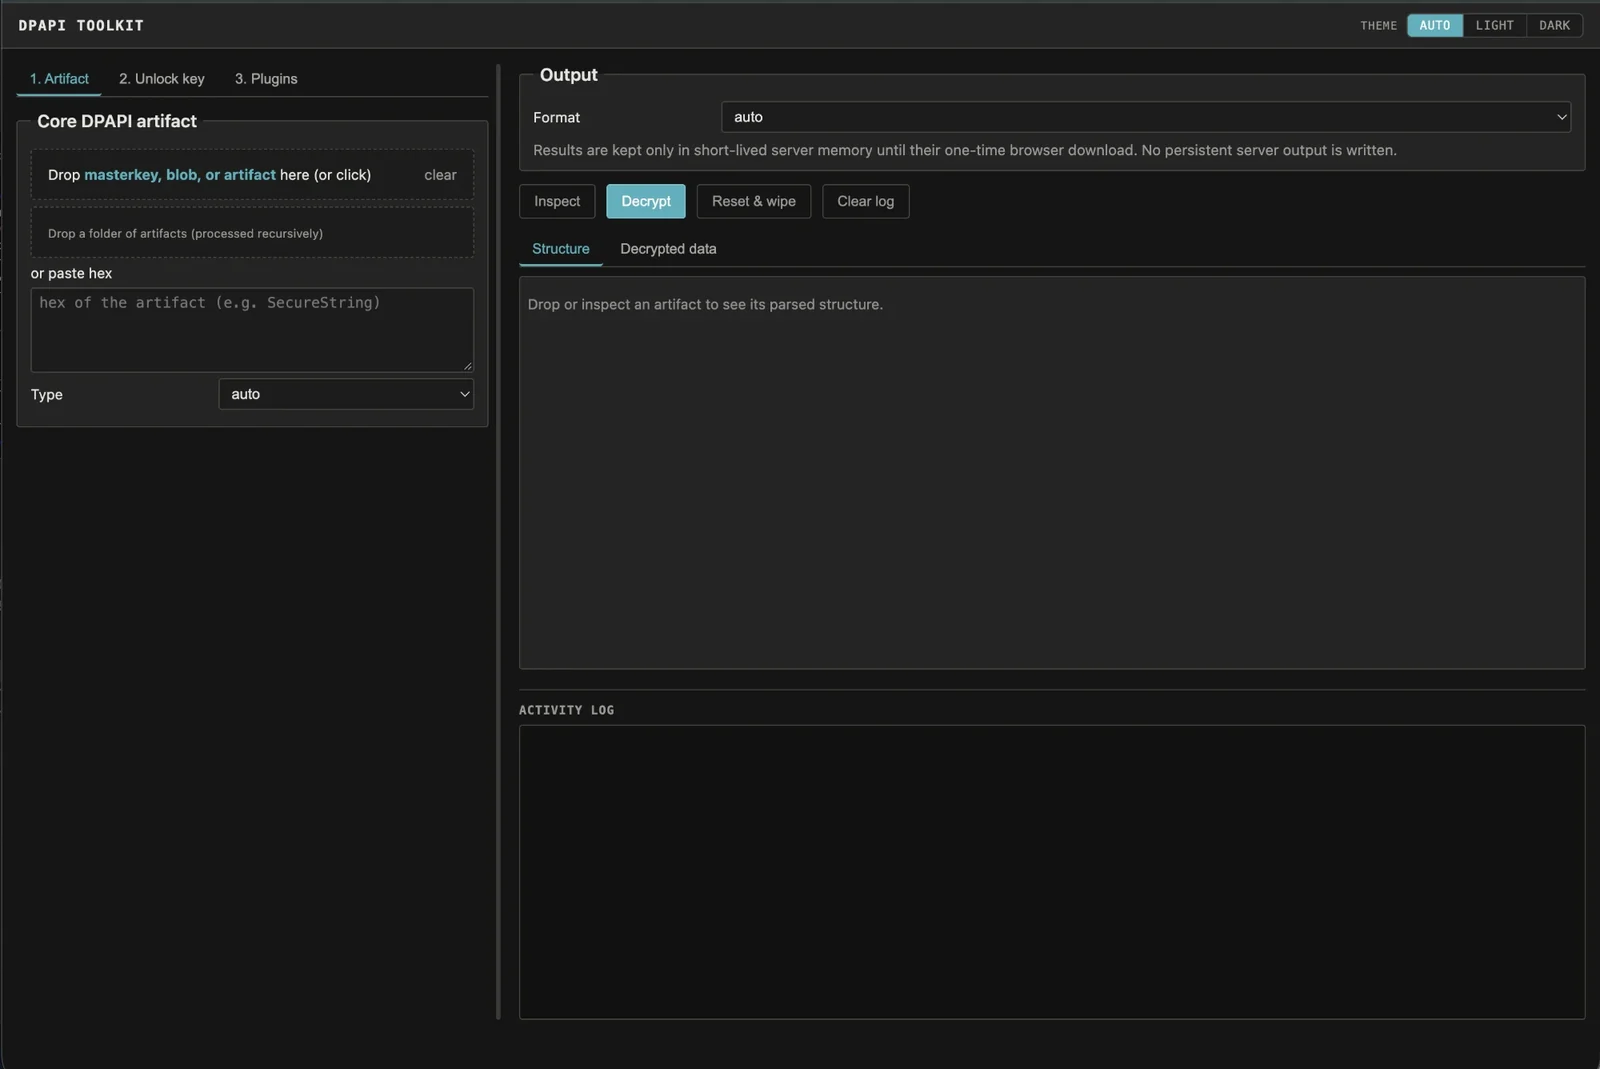 crypt0p3g/dpapi-toolkit
Drop any Windows DPAPI artifact and it identifies the format and the exact master key it needs, then decrypts once you supply the key. Offline, CLI +…
 synacktiv/nounours
Nounours is a tool designed to test APP_KEYs at scale on Laravel applications.
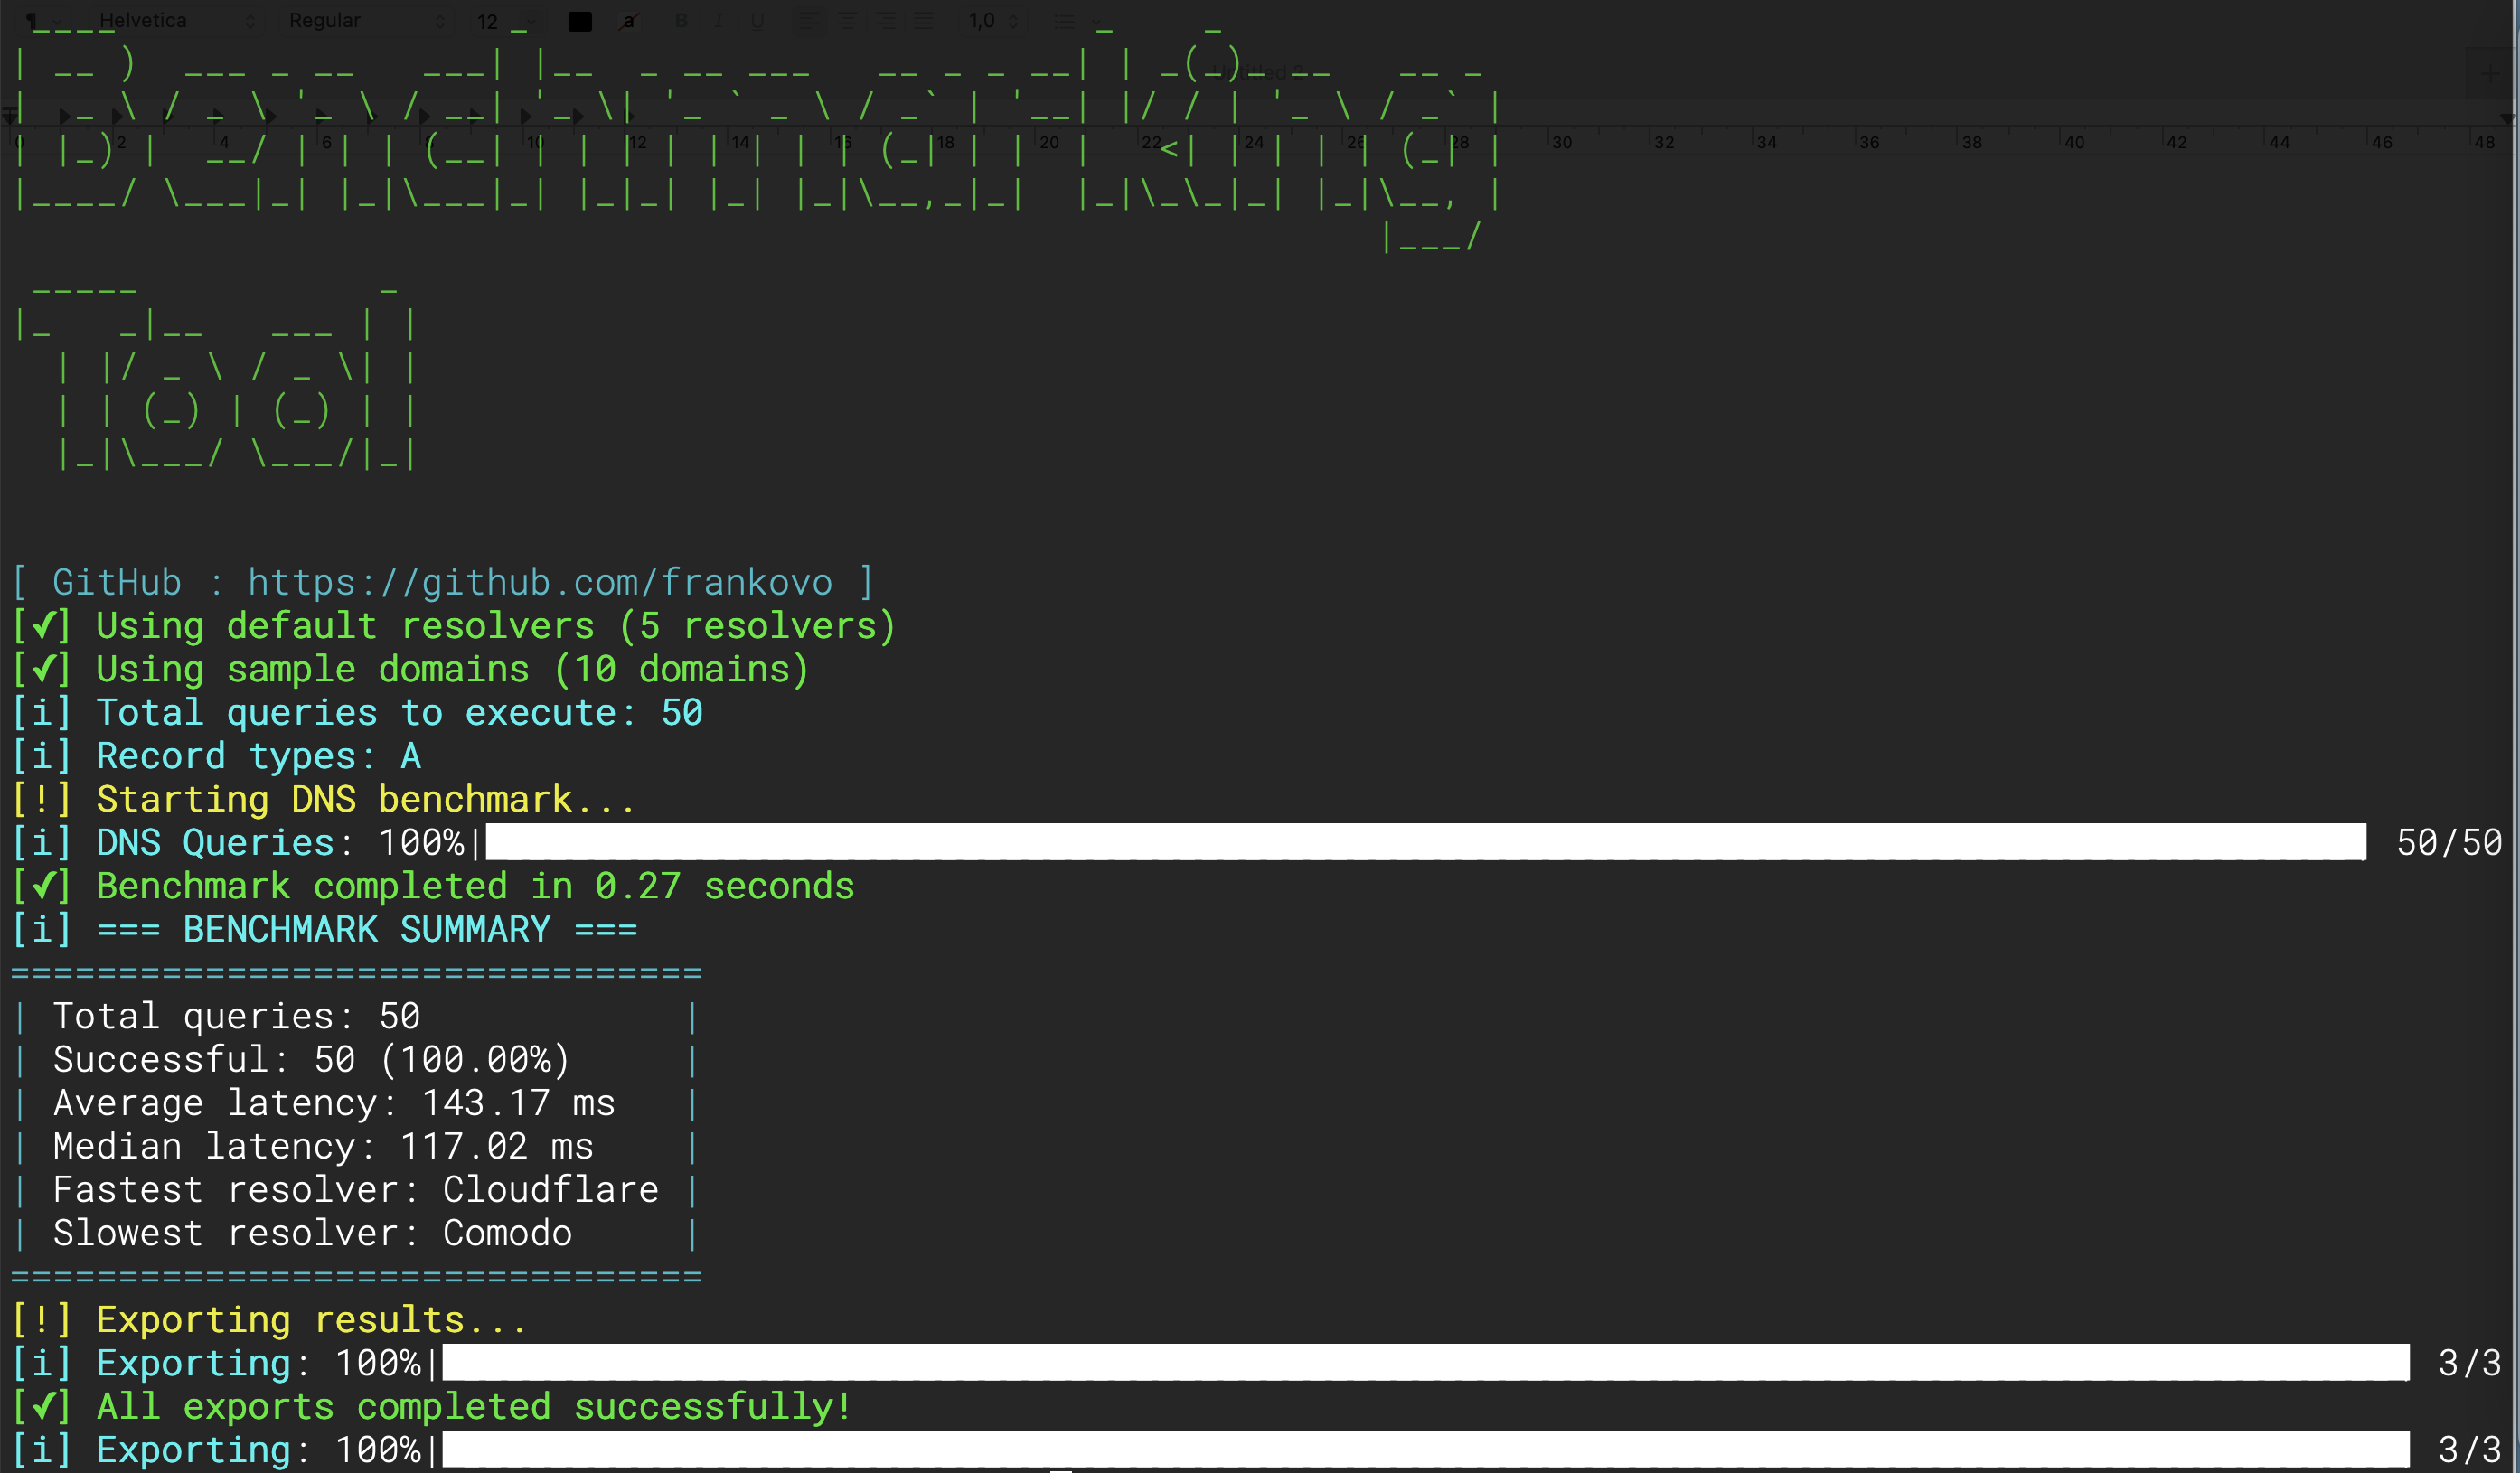 net-benchmark/dns-benchmark-tool
Fast, comprehensive DNS performance testing with DNSSEC validation, DoH/DoT support, and enterprise features
 rocketchat/rocket.chat
The Secure CommsOS™ for mission-critical operations
 hashicorp/vault
A tool for secrets management, encryption as a service, and privileged access management
 gchq/cyberchef
The Cyber Swiss Army Knife - a web app for encryption, encoding, compression and data analysis
 certbot/certbot
Certbot is EFF's tool to obtain certs from Let's Encrypt and (optionally) auto-enable HTTPS on your server. It can also act as a client for any…
 getsops/sops
Simple and flexible tool for managing secrets
 opennhp/opennhp
Cryptography-driven Zero Trust toolkit implementing NHP and DHP protocols to hide network infrastructure, encrypt data, and enforce default-deny…