

enject
 greatscott/enject
enject: Hide .env secrets from prAIng eyes: secrets live in local encrypted stores (per project) and are injected directly into apps at runtime,…
authenticationcloud-securitydevsecops+3
503
greatscott/enjectenject: Hide .env secrets from prAIng eyes: secrets live in local encrypted stores (per project) and are injected directly into apps at runtime,…
 ugzv/ublockdnsclient
Cross-platform system DNS client for uBlockDNS with device wide ad and tracker blocking and real time filter updates.
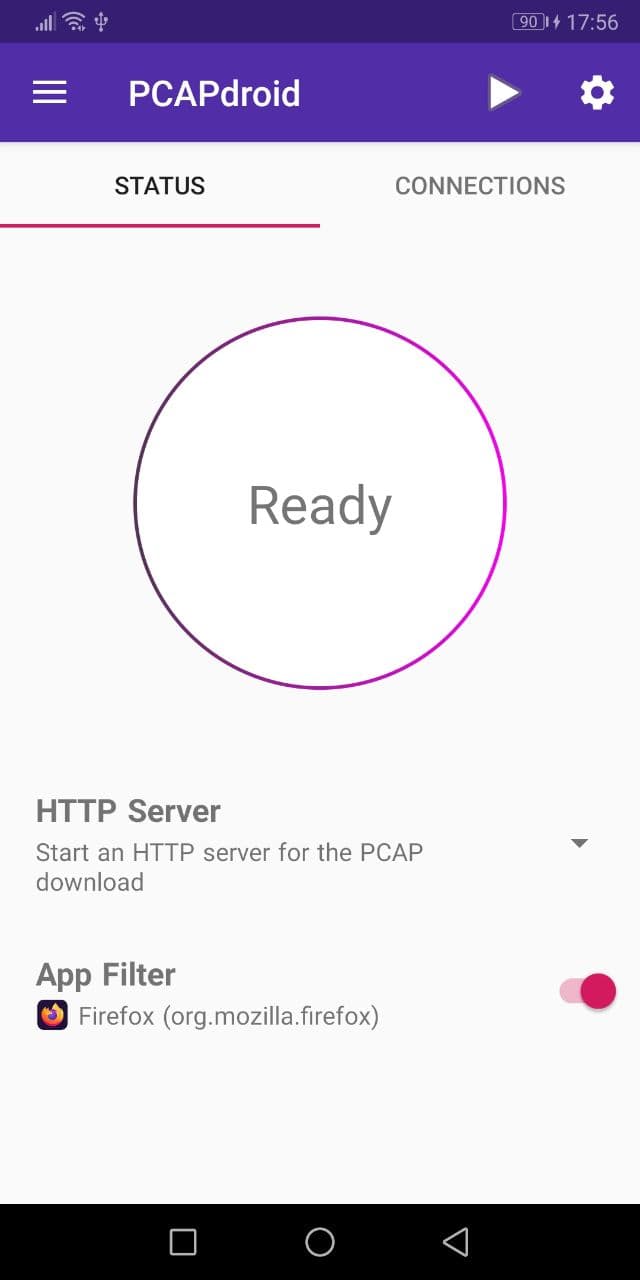 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
 mimi89999/webauthn_tpm_portable
Portable, hardware-backed WebAuthn credentials using TPM 2.0. Deterministic parent key derived from a master seed enables cross-device credential…
 owasp/owasp-java-encoder
The OWASP Java Encoder is a Java 1.5+ simple-to-use drop-in high-performance encoder class with no dependencies and little baggage. This project will…
 timvisee/send
📬 Simple, private file sharing. Mirror of https://gitlab.com/timvisee/send
 0xsch1zo/nullgate
Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.
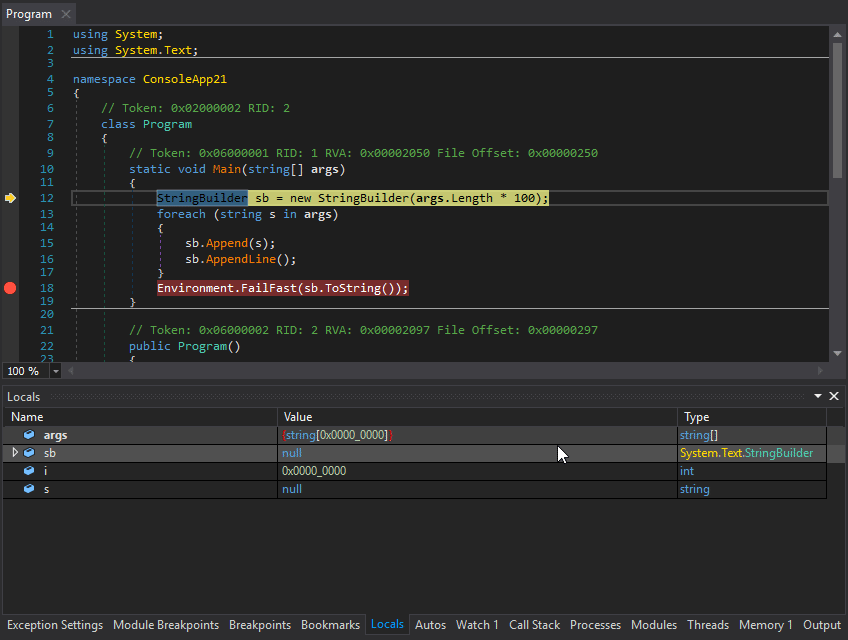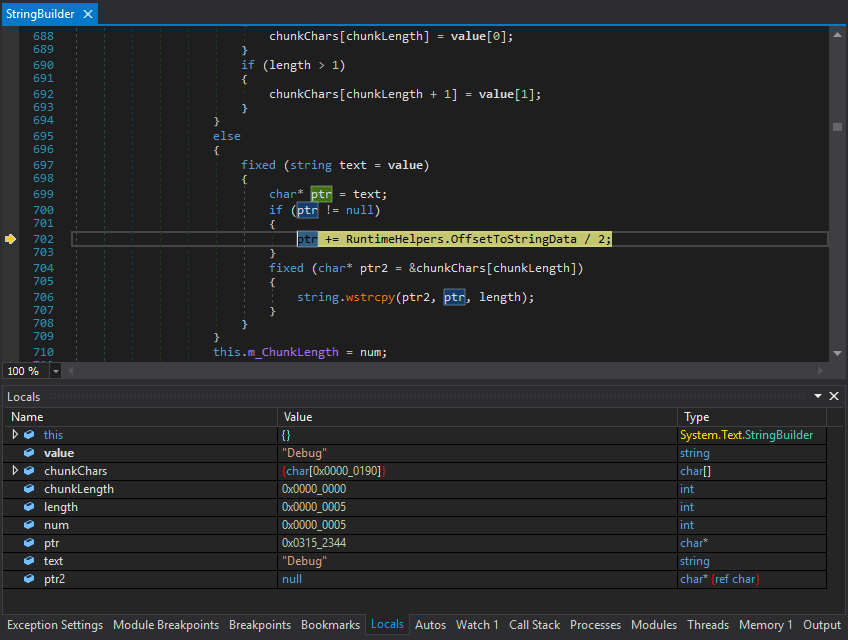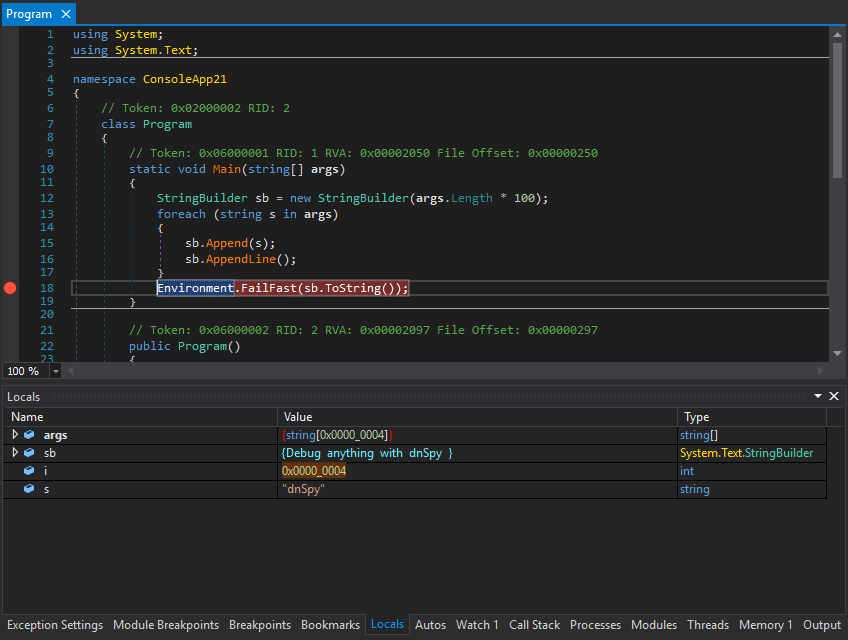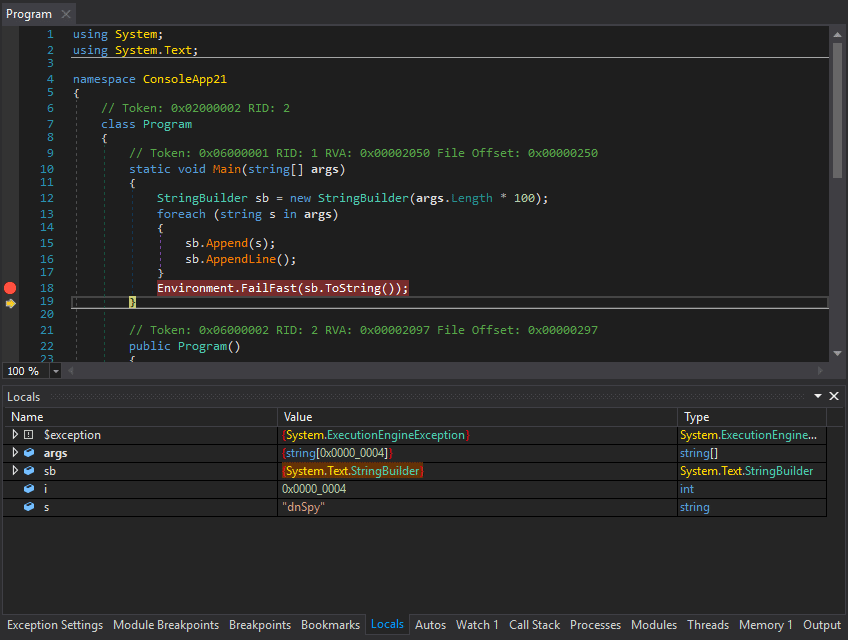 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
 battalkoc/kalici-dosya-silme-araci
Securely deletes files by overwriting them with user-specified iterations of random data, then removes the file to prevent recovery. Supports Python…
 rejithregi-group/securityproject
Python Security Project that implements a file encryption and decryption tool
 cobbr/elite
Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…
 qcomms/cqptoolkit
Framework for controlling QKD devices and managing symmetric keys. See the [project page here](https://qcomms.gitlab.io/cqptoolkit/)
 fevar54/cve-2024-42461
Fix for ECDSA and EDDSA signature verification in Wycheproof project, addressing missing length checks that allowed zero-byte manipulation during…
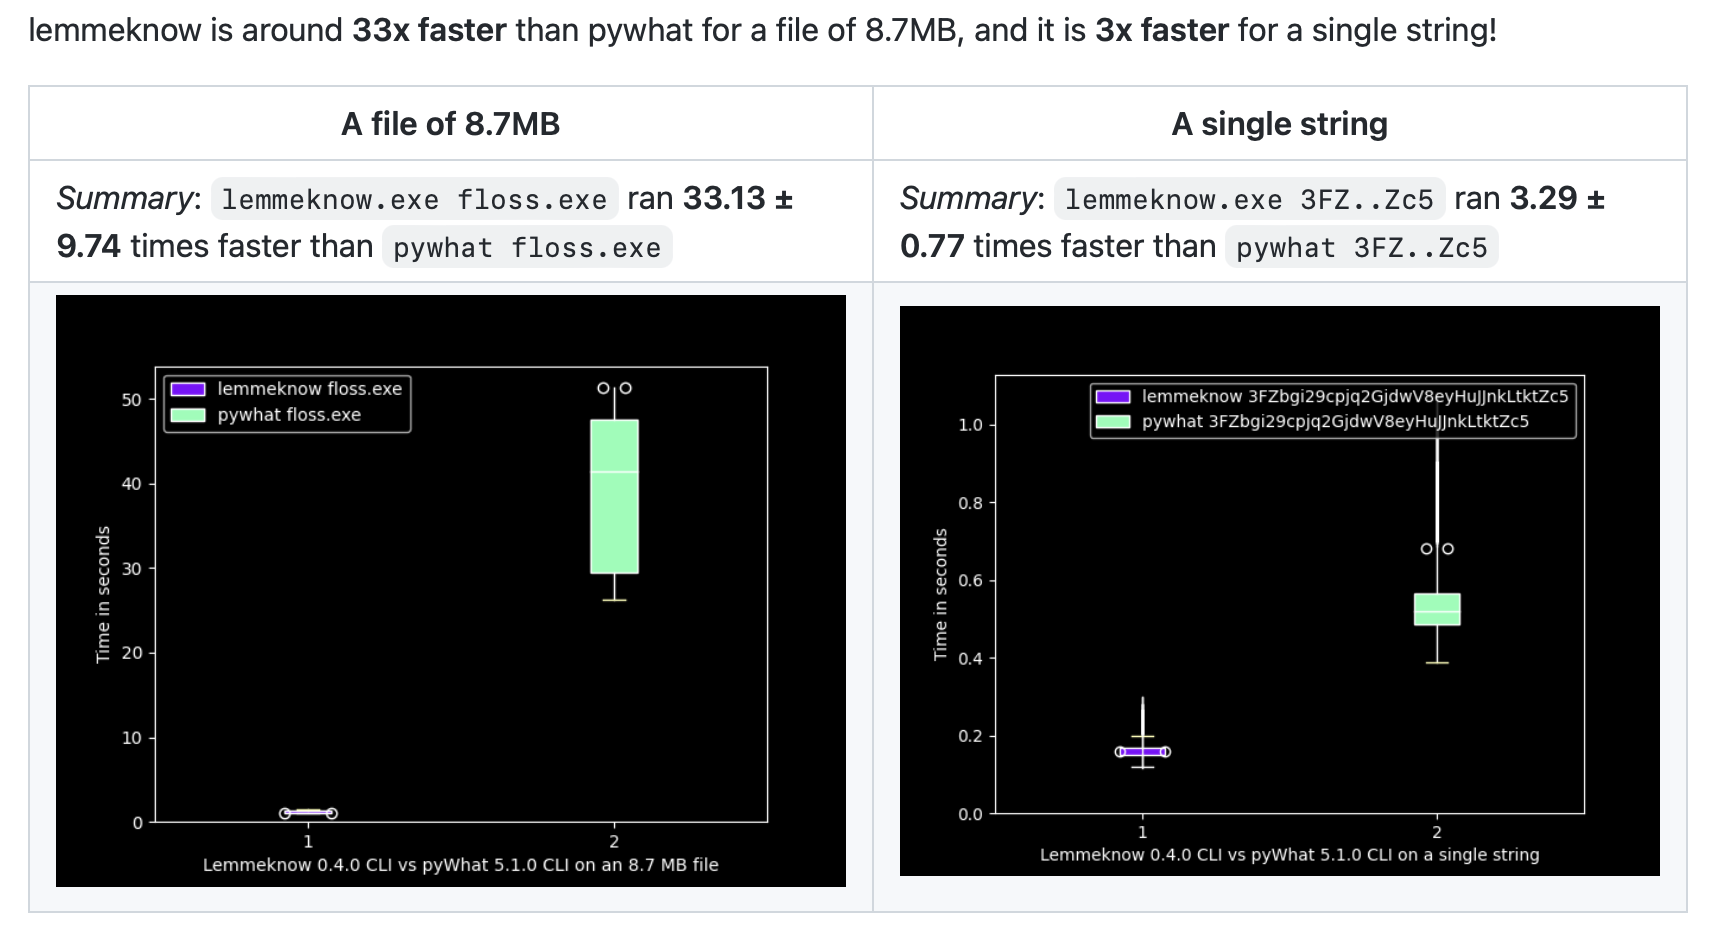 bee-san/ciphey
⚡ Automatically decrypt encryptions without knowing the key or cipher, decode encodings, and crack hashes ⚡
 cryptomator/cryptomator
Cross-platform client-side encryption for cloud storage with AES-256, encrypted filenames, obfuscated folder structure, and transparent virtual drive…
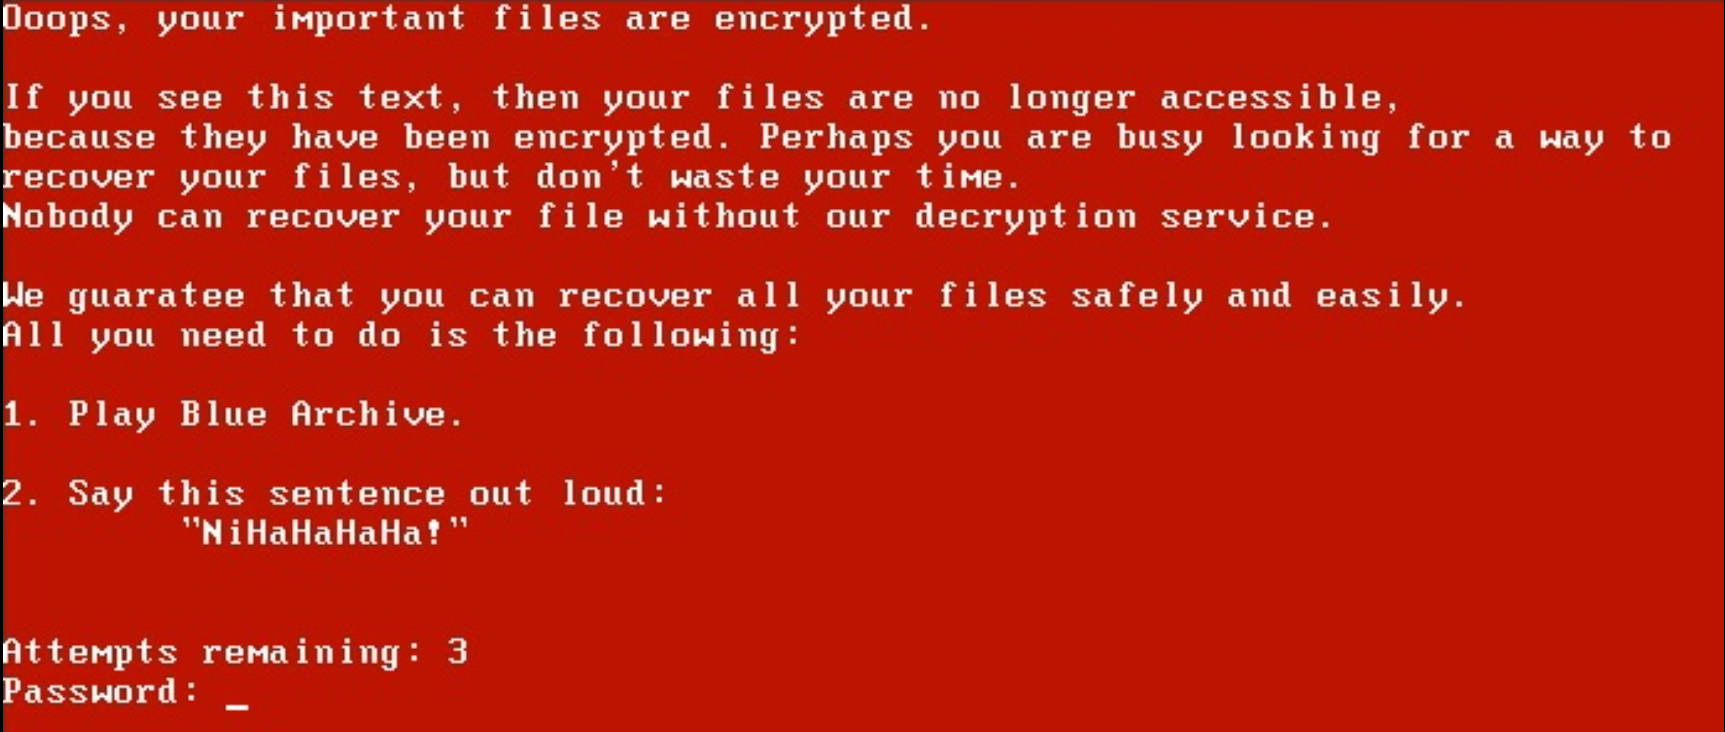 iss4cf0ng/openpetya
A Proof-of-Concept bootkit and UEFI boot application inspired by Petya ransomware, written in Assembly, C, and C++
 gmh5225/deluded-openssl-3.2.0
Robust open-source toolkit implementing TLS, DTLS, and QUIC protocols with a full-strength cryptographic library, command-line tool for key…