

voidsyscall
 voidsecsoftwares/voidsyscall
Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.
command-and-controlencryption-decryption-toolsids-ips-evasion+9
64
voidsecsoftwares/voidsyscallCross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.
 mephistolist/soviet
A Runtime Crypter in C for Linux ELF binaries.
 iss4cf0ng/eden-rat
An open-source Linux GUI-based Remote Access Tool developed in C# with a Python payload, intended for legitimate penetration testing and…
 gibmat/cve-2026-32606-poc
Proof-of-concept demonstrating bypass of TPM-bound LUKS disk encryption on Linux systems, extracting volume keys via custom root filesystem attack.
 aurh1l-42-projects/woody-woodpacker
ELF binary packer that encrypts code sections and injects a runtime decryption stub for 64-bit Linux executables, demonstrating code injection and…
 0xbbuddha/hermes
A Python agent targeting Linux for Mythic C2
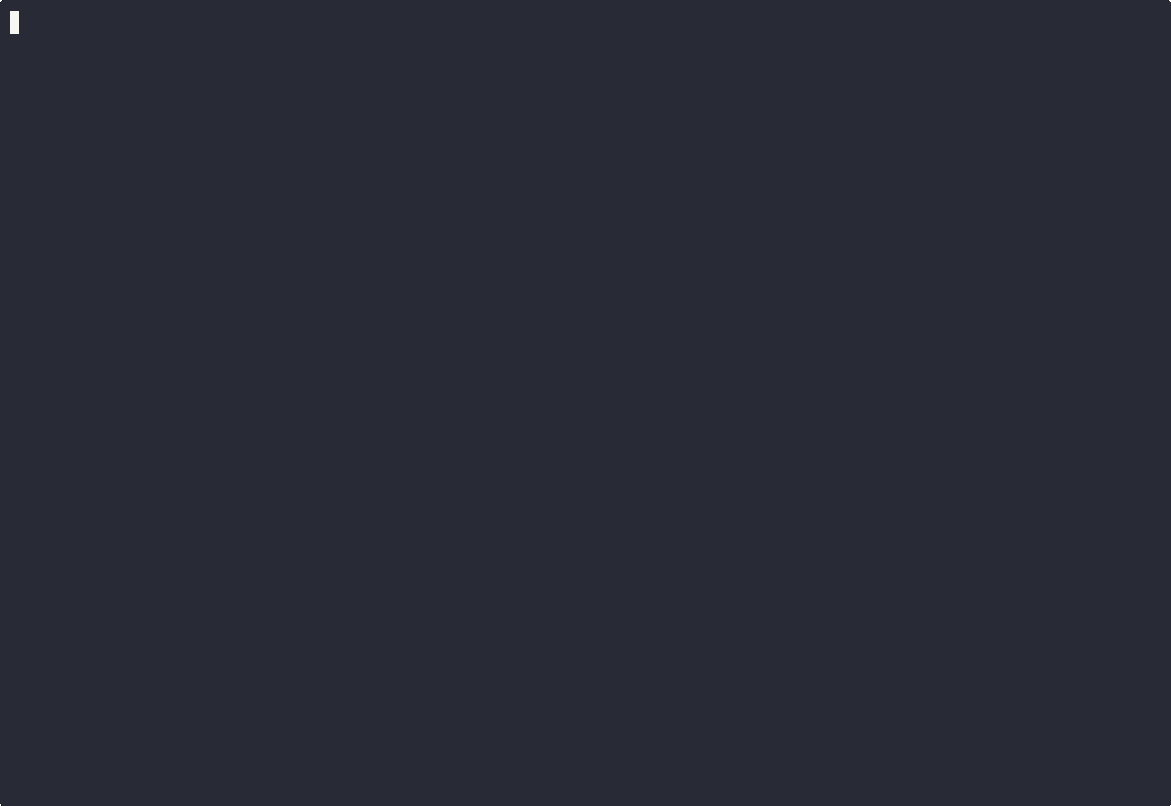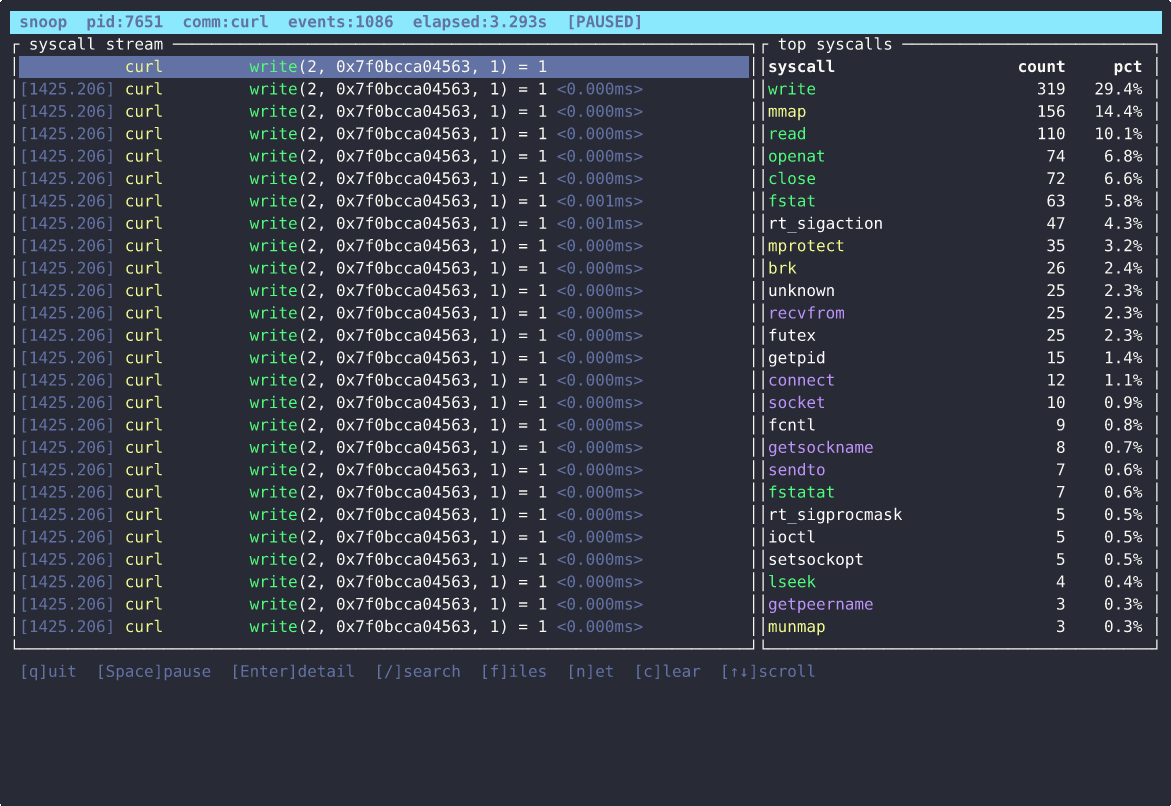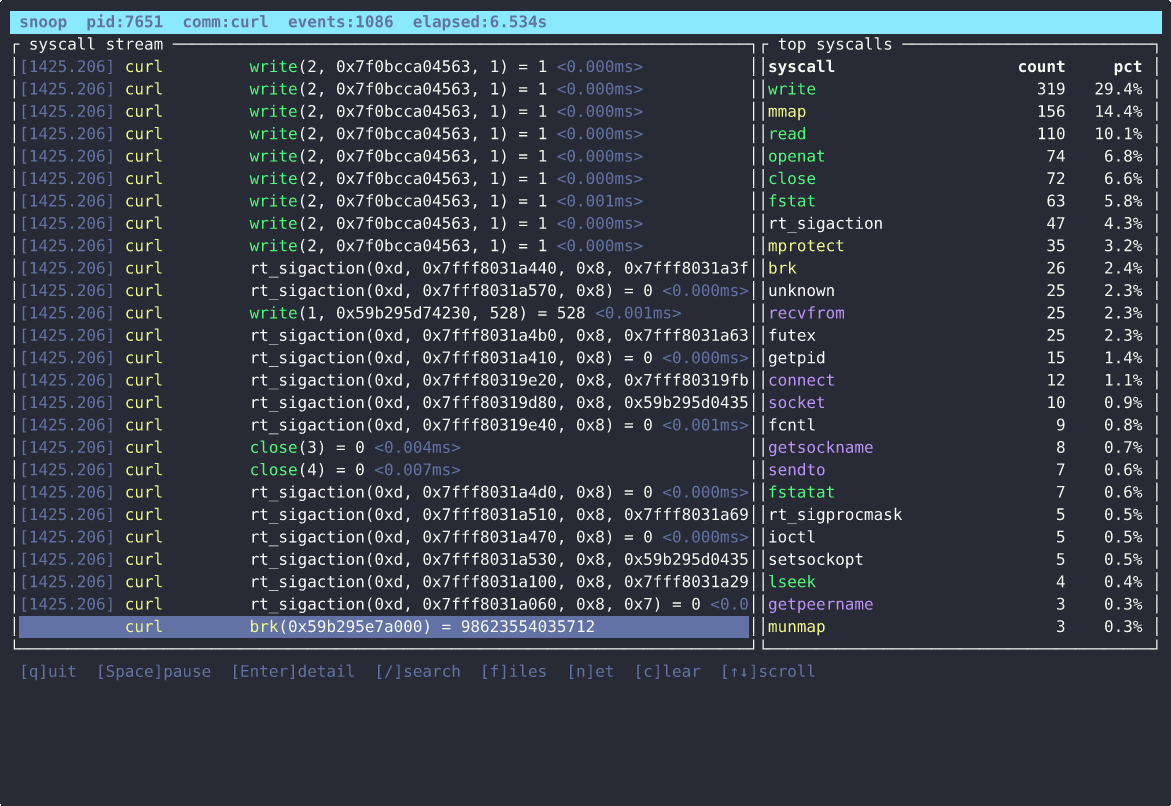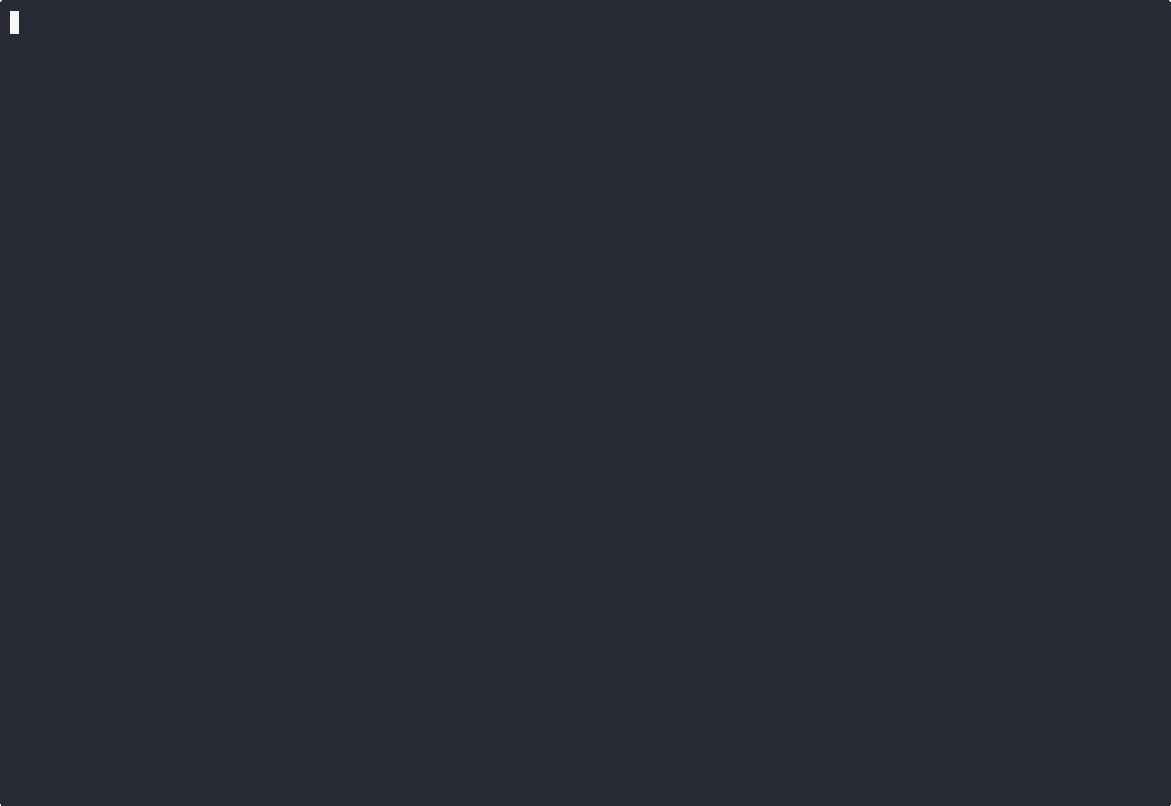 pandaadir05/snoop
A modern syscall tracer built on eBPF. Think strace, but with a real TUI, smart filters, TLS decryption, and output that's actually readable.
 mohamednourtn/terminator
Terminator metasploit payload generator
 rek7/ddoor
DDoor - cross platform backdoor using dns txt records
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
 hwdsl2/setup-ipsec-vpn
Automated IPsec VPN server setup with IPsec/L2TP, Cisco IPsec, and IKEv2 support. Includes helper scripts for user and certificate management, and…
 alisamtechnology/atscan
Advanced dork Search & Mass Exploit Scanner
 freax13/cve-2024-21980-poc
Exploit for CVE-2024-21980 targeting AMD SEV firmware to decrypt arbitrary memory of decommissioned SEV-SNP guests via a command buffer enforcement…
 freax13/cve-2023-31355-poc
Exploit for AMD SEV-SNP firmware vulnerability (CVE-2023-31355) that decrypts arbitrary memory of decommissioned guests by corrupting the UMC key…
 c-sprinks/bitlocker-bypass-research
BitLocker full-disk encryption bypass research using CVE-2023-21563 (BitPixie). Methodology, exploit chain, and defensive recommendations.
 anatol/booster
Fast and secure initramfs generator
 lesnuages/hershell
Multiplatform reverse shell generator
 owasp/zsc
OWASP ZSC - Shellcode/Obfuscate Code Generator https://www.secologist.com/