 amlweems/gringotts
proof of concept for CVE-2020-0601
 beemdevelopment/aegis
A free, secure and open source app for Android to manage your 2-step verification tokens.
 permissionlesstech/bitchat-android
Decentralized, encrypted peer-to-peer messaging app over Bluetooth mesh networks. No internet, servers, or phone numbers required. Features X25519 +…
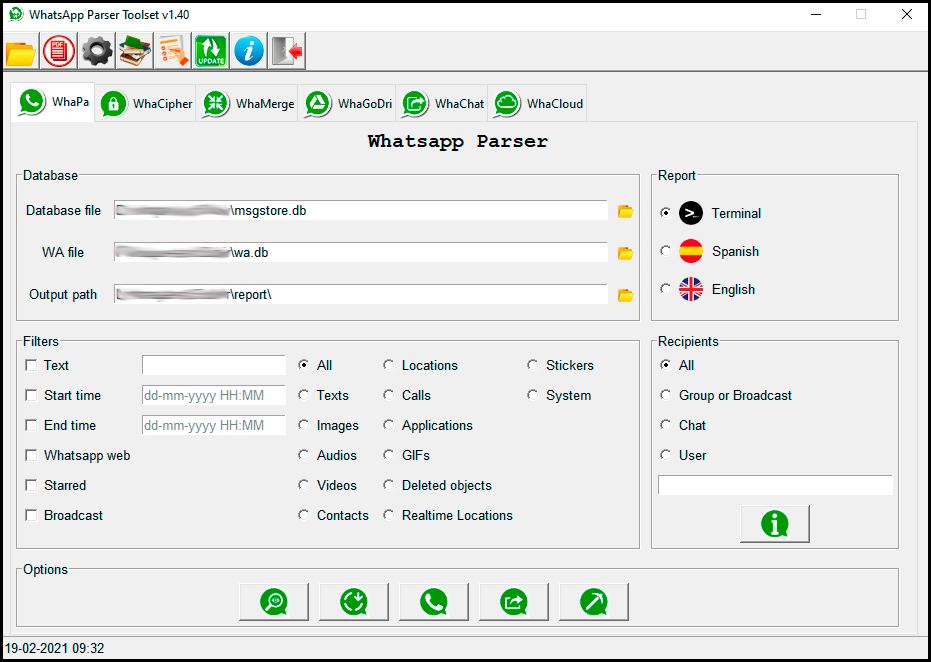 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
 eldavoo/wa-crypt-tools
Manage WhatsApp .crypt12, .crypt14 and .crypt15 files.
 barghest-ngo/mesh
Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…
 caveeroo/gv_decryptor
Gallery Vault dump recovery tool with automated discovery, key derivation and automatic media restoration.
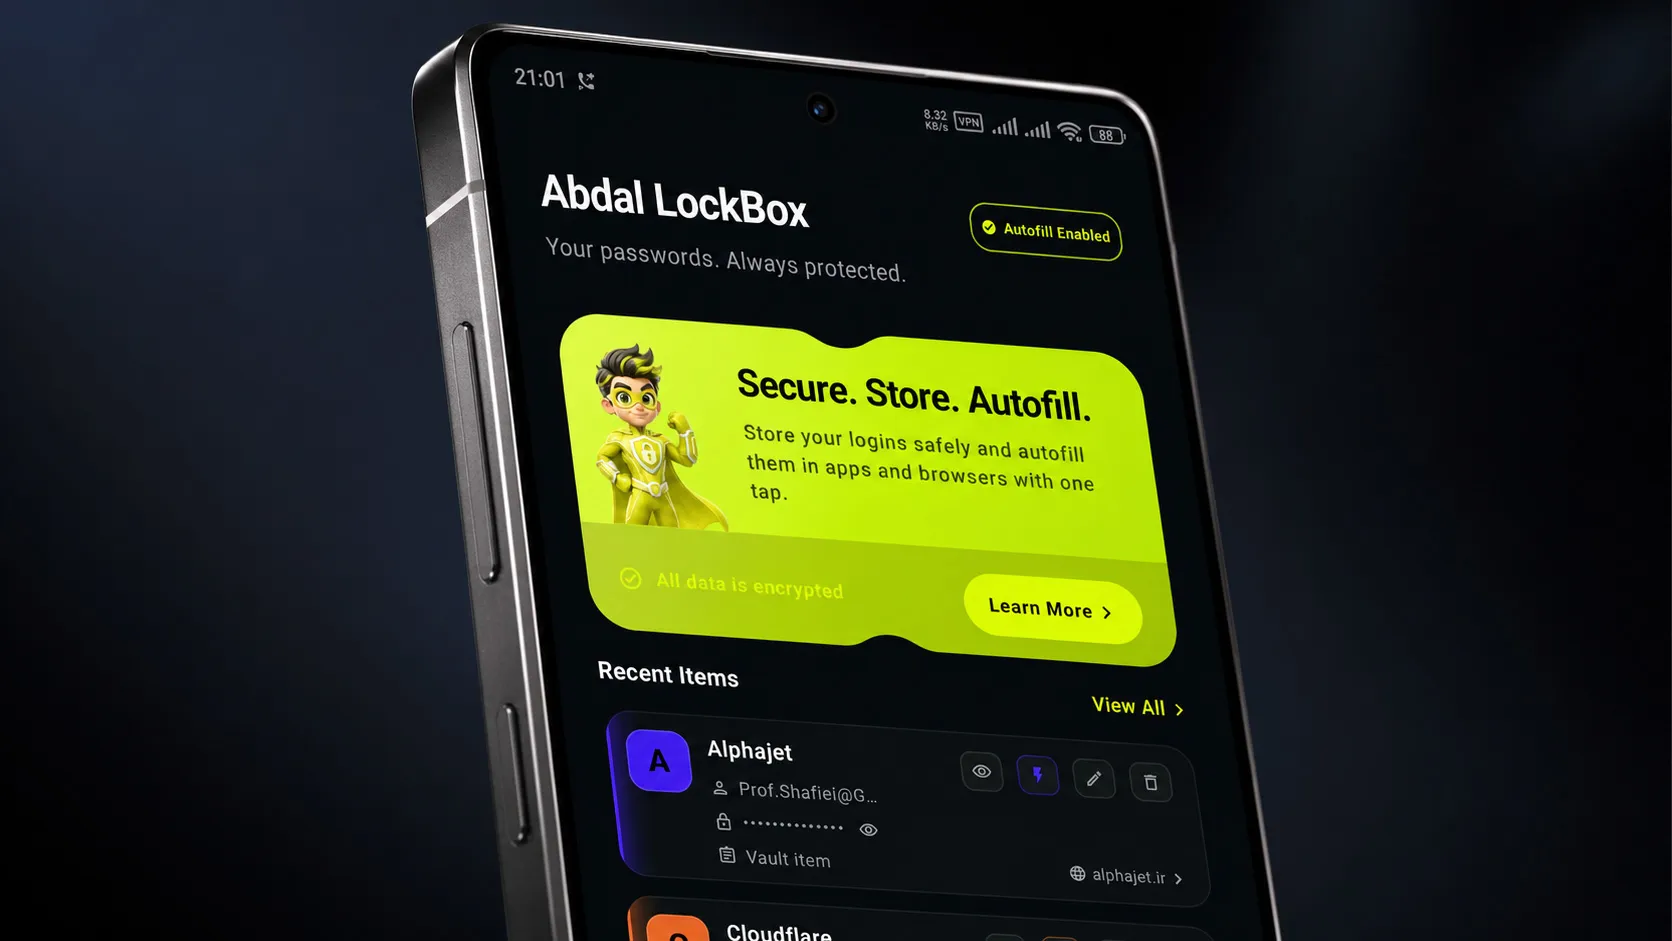
 prof.shafiei/abdal-lockbox
Local-first encrypted password vault for Android with Master Password access, Recovery Key support, Autofill integration, and portable encrypted…
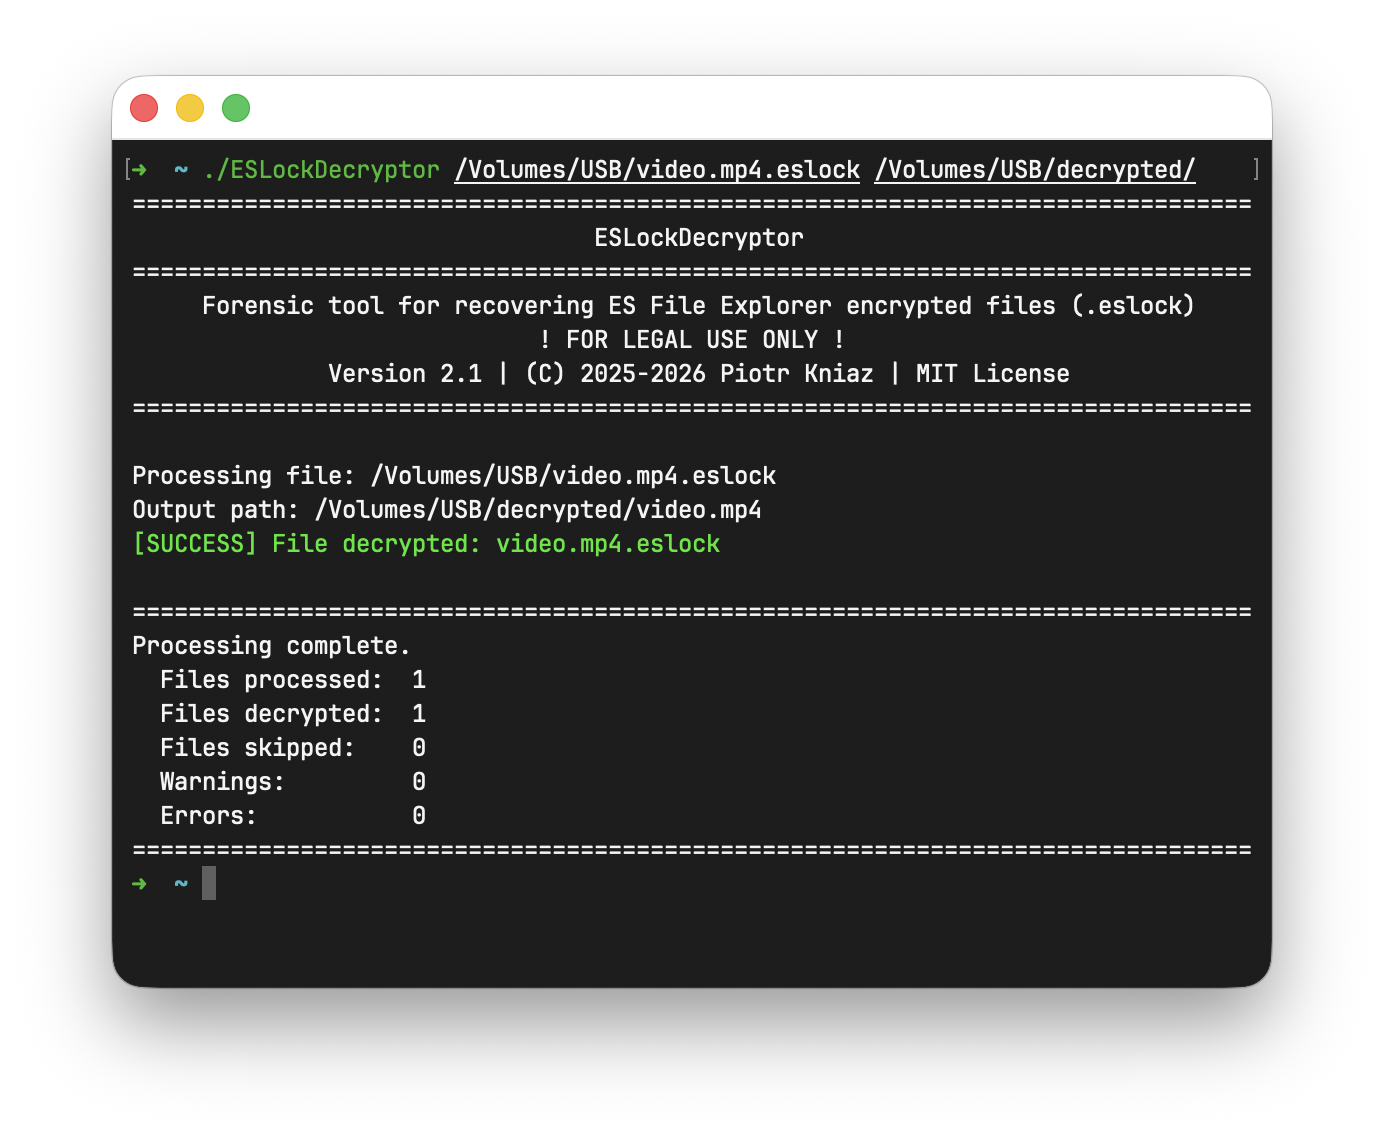 piotr-kniaz/eslockdecryptor
Utility for recovering ES File Explorer encrypted files (.eslock)
 jas502n/2024informationsecurityengineer
2024年信息安全工程师、2024InformationSecurityEngineer
 den4uk/andriller
📱 Andriller - is software utility with a collection of forensic tools for smartphones. It performs read-only, forensically sound, non-destructive…
 marcog3/whatsdump
Extract WhatsApp private key from any non-rooted Android device (Android 7+ supported)
 donctl/sandy
Release of the sandy framework.
 e-gleba/world_conqueror_4_ru
Translated strings for World Conqueror 4 (RU)
 crackercat/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 nicchongwb/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration