
psc
 stealth/psc
E2E encryption for multi-hop tty sessions or portshells + TCP/UDP port forward
encryption-decryption-toolsforensicsnetwork-security+2
stealth/pscE2E encryption for multi-hop tty sessions or portshells + TCP/UDP port forward
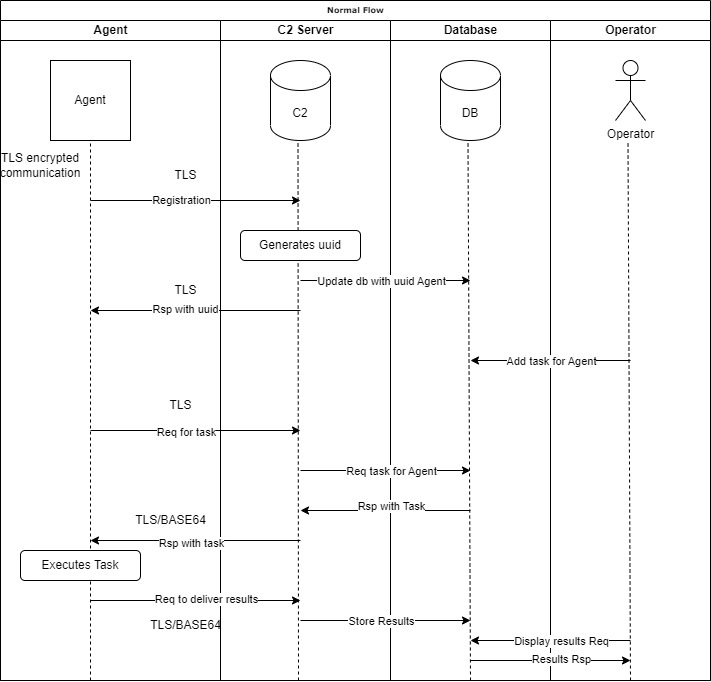 voukatas/commander
Python-based command and control framework with encrypted TLS communication, multiple agent support (Python/C), interactive sessions, file transfer,…
 lawndoc/mediator
An extensible, end-to-end encrypted reverse shell that works across networks without port forwarding.
 dereeqw/netspy
NetSpyC2 – Python C2 Server with RSA Key Exchange and AES-GCM Encrypted Sessions
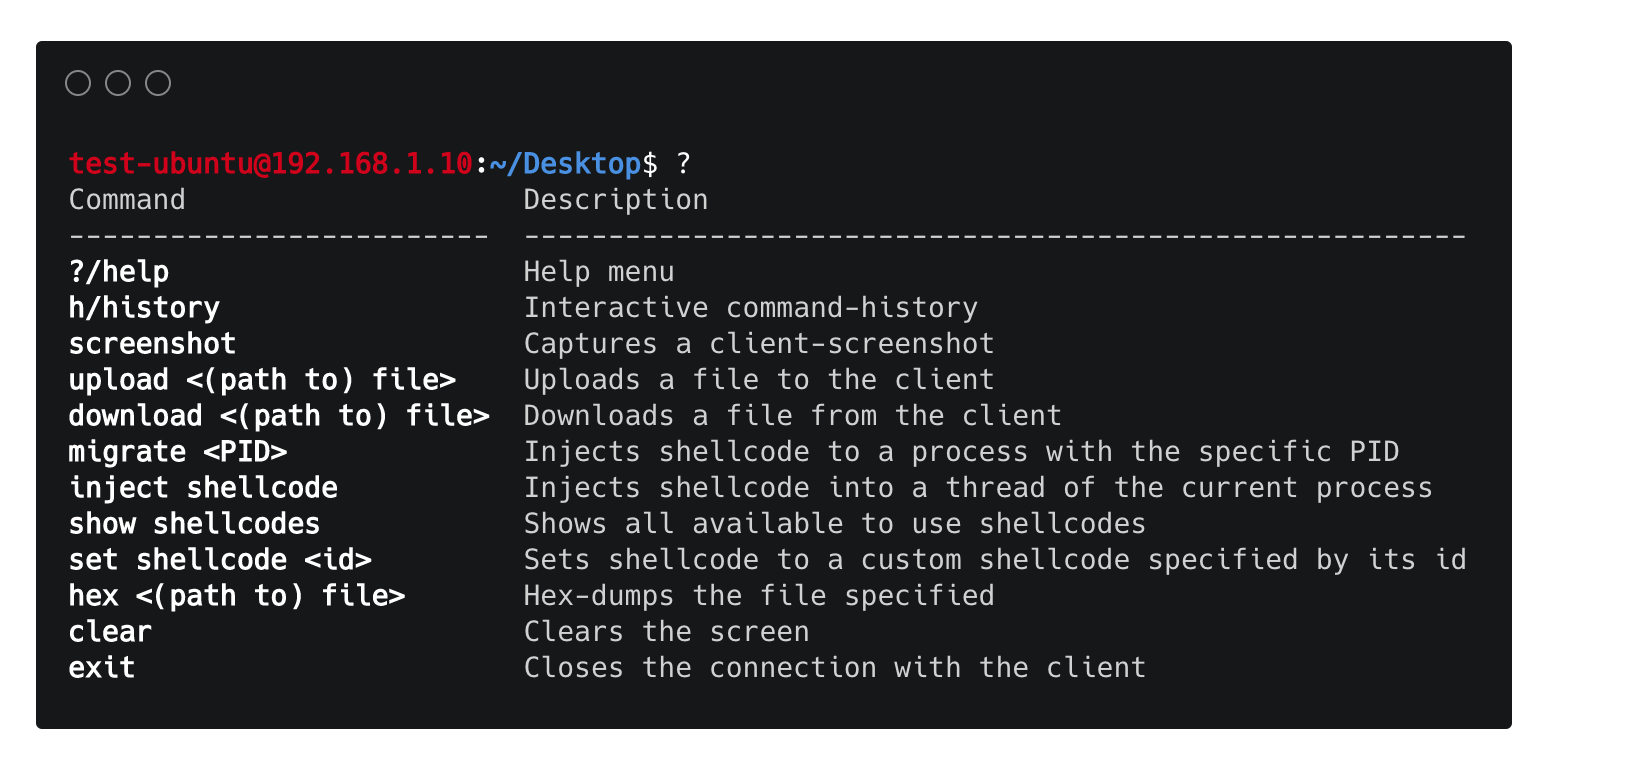 chrispetrou/hrshell
HRShell is an HTTPS/HTTP reverse shell built with flask. It is an advanced C2 server with many features & capabilities.
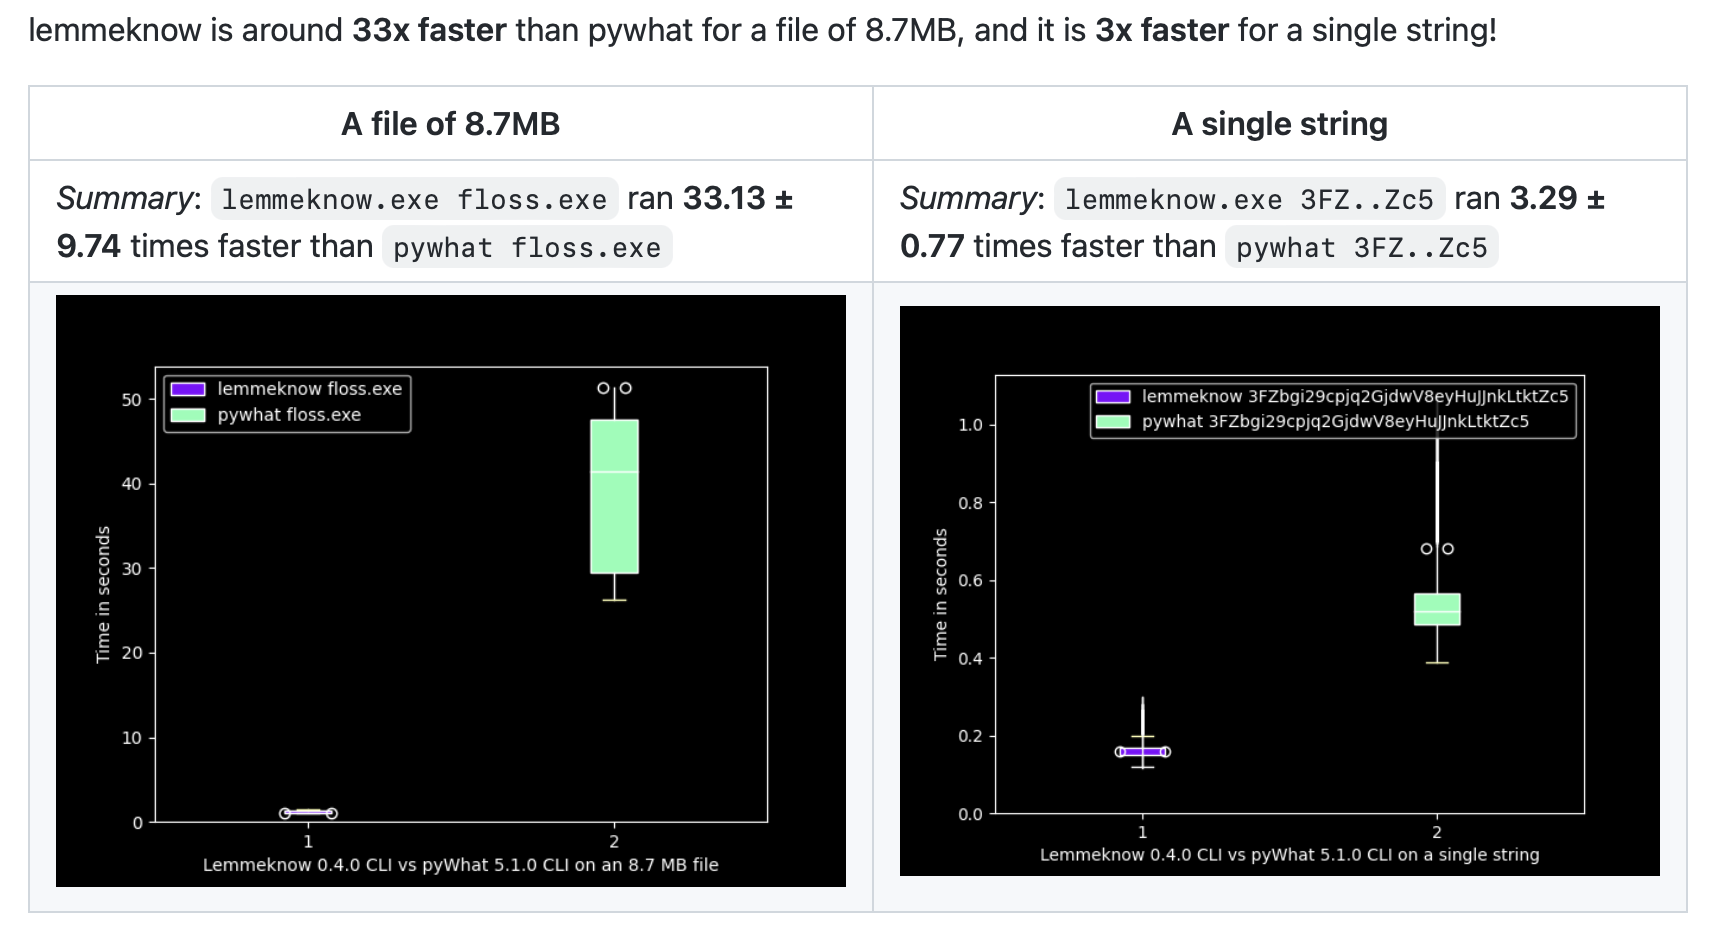 bee-san/ciphey
⚡ Automatically decrypt encryptions without knowing the key or cipher, decode encodings, and crack hashes ⚡
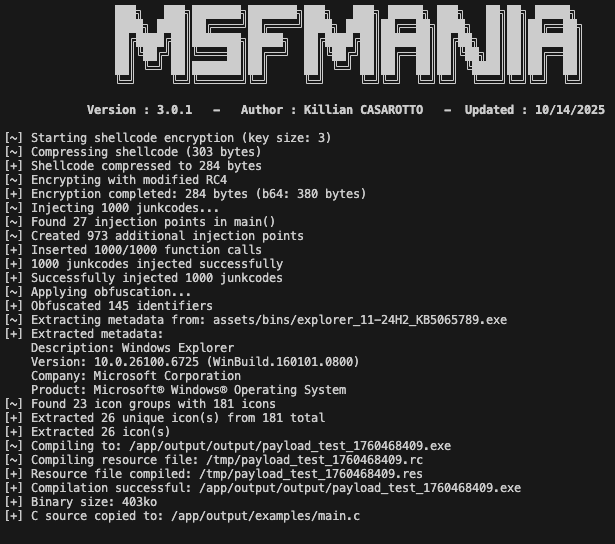 lepotekil/msfmania
Python AV Evasion Tools
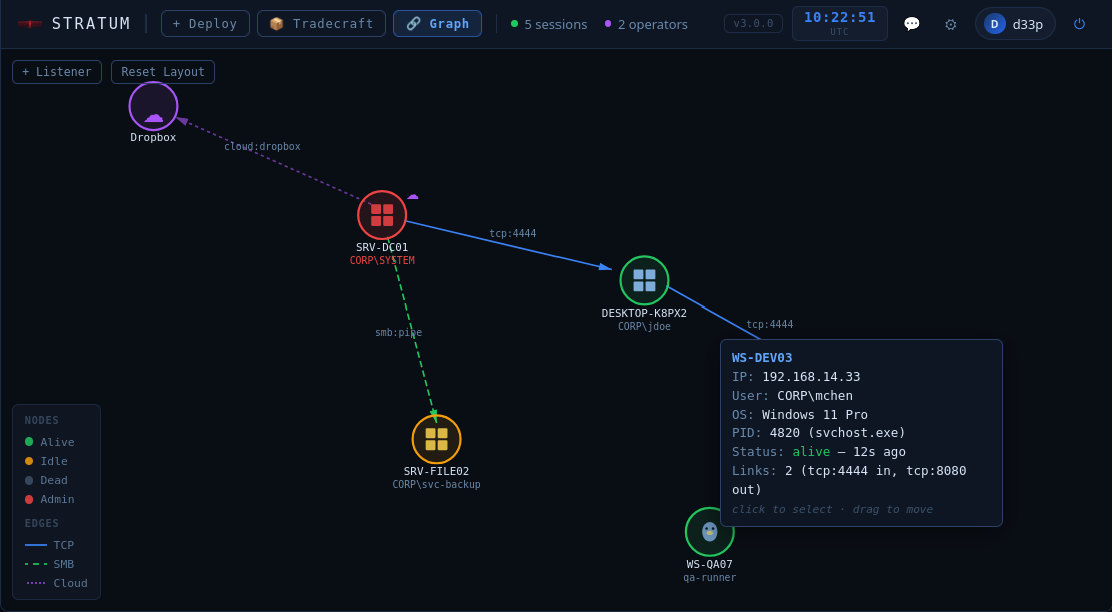 lame-projects/stratum-c2
Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
 gojue/ecapture
Capturing SSL/TLS plaintext without a CA certificate using eBPF. Supported on Linux/Android kernels for amd64/arm64.
 permissionlesstech/bitchat-android
Decentralized, encrypted peer-to-peer messaging app over Bluetooth mesh networks. No internet, servers, or phone numbers required. Features X25519 +…
 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
 eldavoo/wa-crypt-tools
Manage WhatsApp .crypt12, .crypt14 and .crypt15 files.
 den4uk/andriller
📱 Andriller - is software utility with a collection of forensic tools for smartphones. It performs read-only, forensically sound, non-destructive…
 barghest-ngo/mesh
Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…
 jb-selfcompany/tyr
True P2P Email on top of Yggdrasil Network for Android
 marcog3/whatsdump
Extract WhatsApp private key from any non-rooted Android device (Android 7+ supported)
 donctl/sandy
Release of the sandy framework.