
Ares
 cerbersec/ares
Project Ares is a Proof of Concept (PoC) loader written in C/C++ based on the Transacted Hollowing technique
binary-analysisdefensive-toolsencryption-decryption-tools+7
3364 years ago
cerbersec/aresProject Ares is a Proof of Concept (PoC) loader written in C/C++ based on the Transacted Hollowing technique
 nccgroup/pybeacon
A collection of scripts for dealing with Cobalt Strike beacons in Python
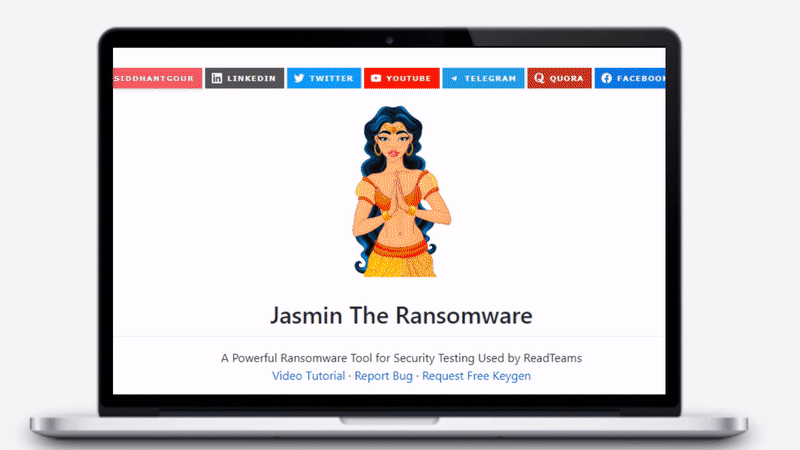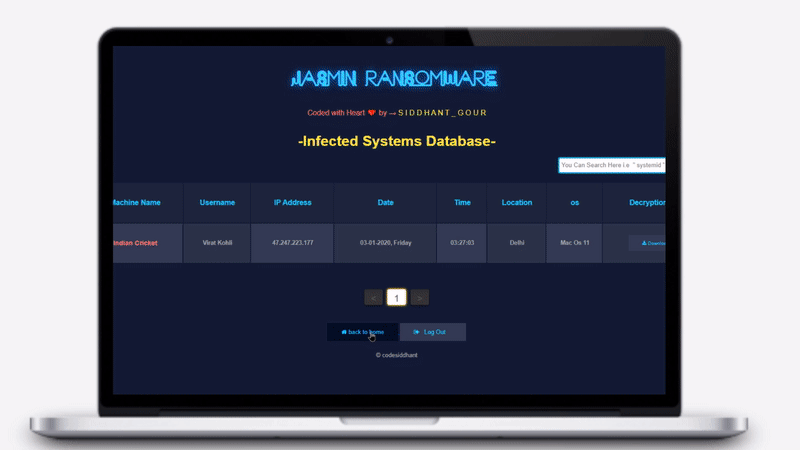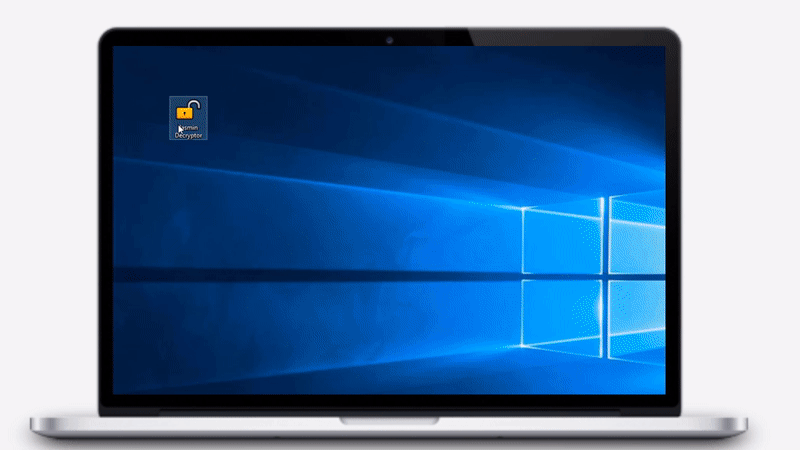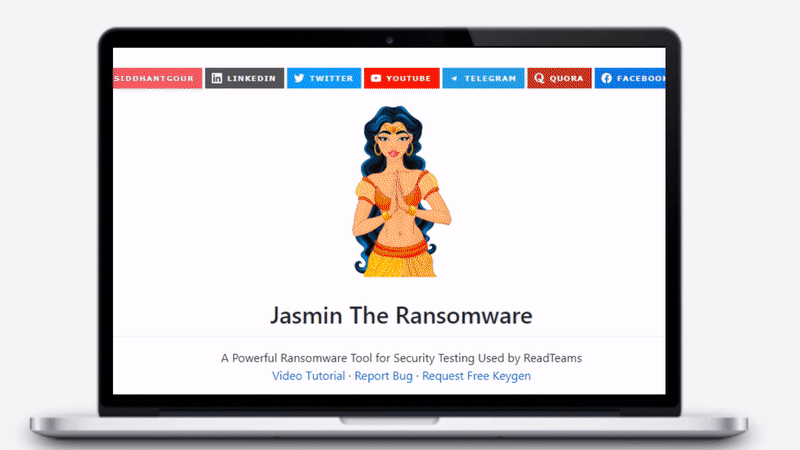 codesiddhant/jasmin-ransomware
Jasmin Ransomware is an advanced red team tool (WannaCry Clone) used for simulating real ransomware attacks. Jasmin helps security researchers to…
 ffri/cve-2025-24204
PoC and technical details of CVE-2025-24204
 guibacellar/nxransomware
A next generation of ransomware. Fully written using a .Net Framework + C&C System
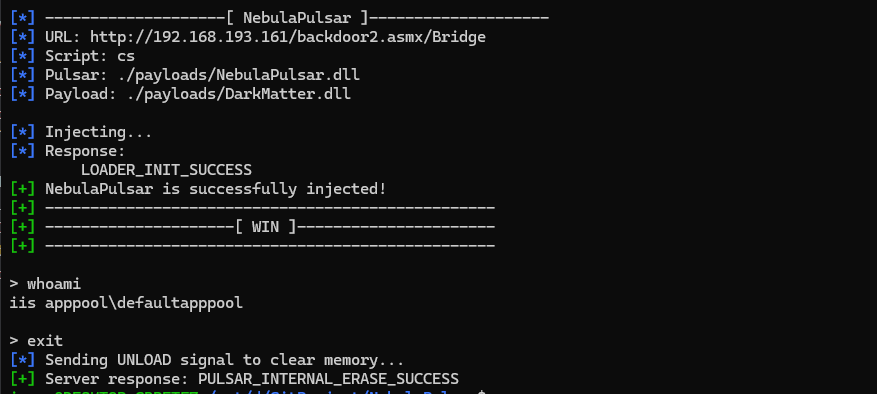 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…
 nccgroup/pip3line
The Swiss army knife of byte manipulation
 helgesverre/sony-vp-extract
Decrypt and extract voice guidance MP3 prompts from Sony WH-1000XM4 encrypted voice packs. AES key extracted via Bluetooth firmware dump of the…
 dump-guy/powershell-tools
Collection of some easy of use tools - in powershell.
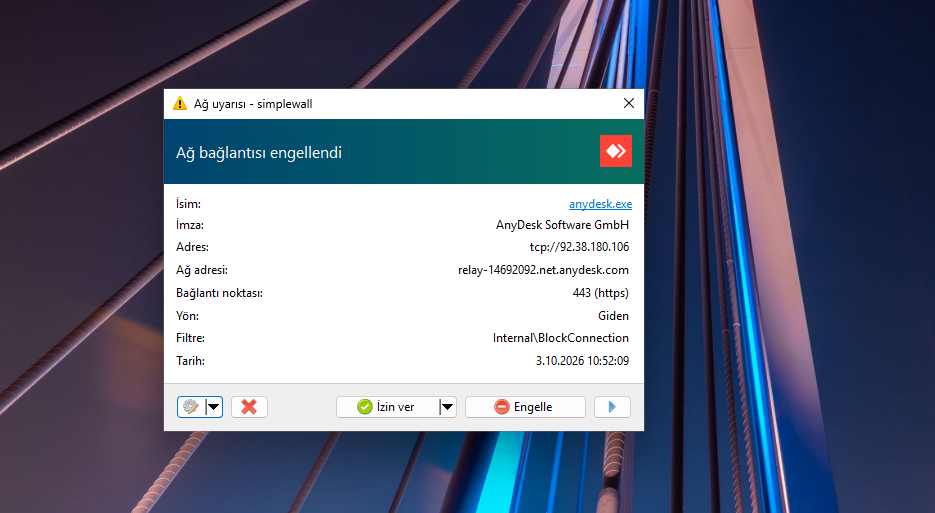 kaandemir993/python-shellcode-anydesk-apc-injection-remote-ip-address-analysis
Reverse engineering write-up of Python shellcode that APC-injects into AnyDesk, exfiltrates to a C2 over HTTPS with AES/RSA, and persists via…
 freax13/cve-2024-21978-poc
Exploit for AMD SEV-SNP firmware vulnerability CVE-2024-21978, enabling decryption of arbitrary guest memory via memory corruption of context pages.
 freax13/cve-2023-31355-poc
Exploit for AMD SEV-SNP firmware vulnerability (CVE-2023-31355) that decrypts arbitrary memory of decommissioned guests by corrupting the UMC key…
 nicchongwb/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
 skelsec/pypykatz
Mimikatz implementation in pure Python
 mattifestation/powershellarsenal
A PowerShell Module Dedicated to Reverse Engineering
 egebalci/amber
Reflective PE packer.