

CVE-2025-55182-RCE-shell
 ruoji6/cve-2025-55182-rce-shell
Burp Suite/antsword - Interactive shell (HTTP hijack + POST + AES-256-CBC/BASE64)
command-and-controlencryption-decryption-toolsexploitation+5
31
ruoji6/cve-2025-55182-rce-shellBurp Suite/antsword - Interactive shell (HTTP hijack + POST + AES-256-CBC/BASE64)
 blacksnufkin/deadmanswitch
DeadManSwitch in rust with several triggers (remote local and network)
 farghlymal/config-extractors
Extracts and decrypts malware configuration data from captured samples, automating C2 endpoint discovery, credential extraction, and indicator triage…
 qarait/ephemera
Zero-Trust SSH CA
 tweathers-sec/doppelganger_assistant
Card calculator and Proxmark3 Plugin for writing and/or simulating every card type that Doppelgänger Community, Pro, Stealth, and MFAS support.
 mhelwig/adwind-decryptor
Simple decrypter for Java AdWind, jRAT, jBifrost trojan
 tothi/kali-rpi-luks-crypt
Full disk encryption for Kali on Raspberry using LUKS
 fishermavis/bsod_bitlocker_recover
Python script for carving Bitlocker VMK keys
 bishopfox/sonicrack
Decrypt encrypted SonicOSX firmware images
 hakavlad/tird
Encrypt files & Hide encrypted data
 ianxtianxt/ecologyexp.jar
泛微oa数据库配置文件读取
 zolderio/token-proxy
A transparent PII redaction proxy for LLM API traffic. Sits between an application and an LLM provider (currently Anthropic), pseudonymizing…
 synacktiv/synodecrypt
A tool to decrypt all Synology encrypted archives (SPK, PAT, ...)
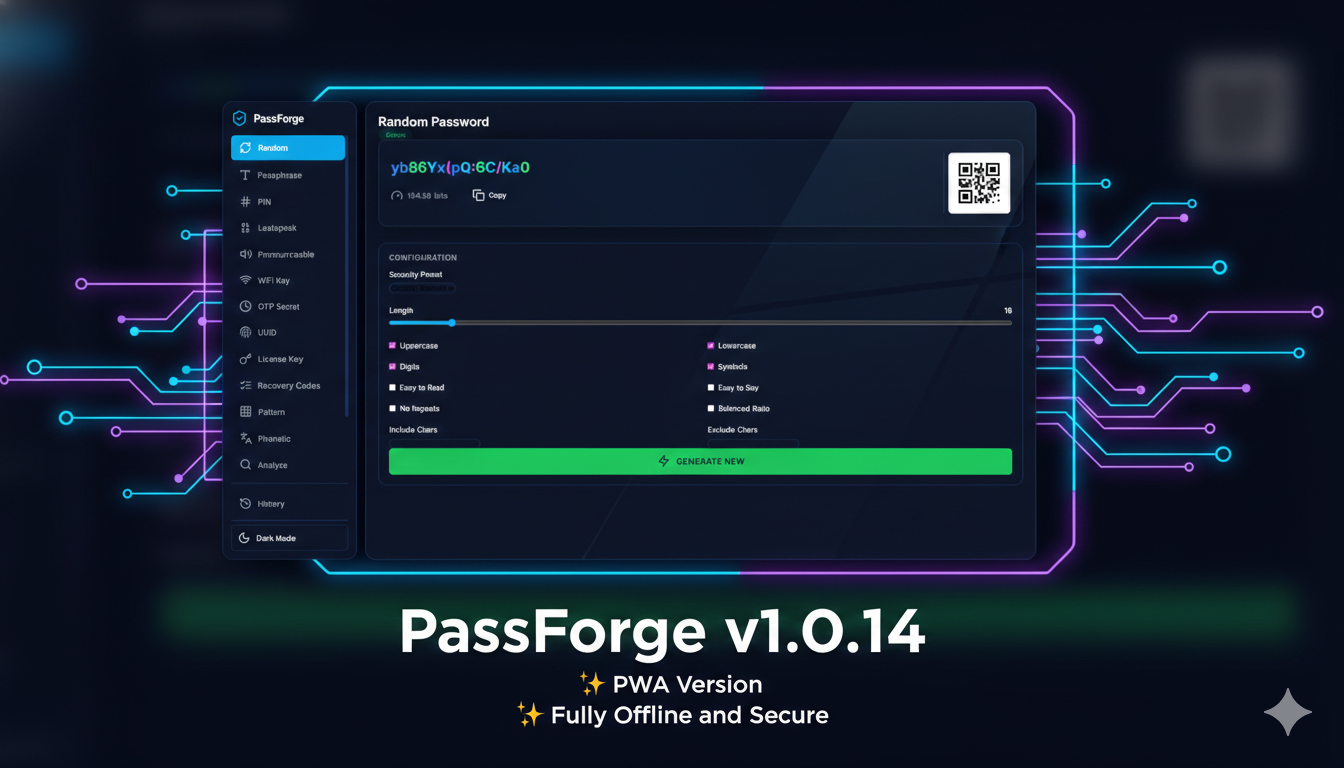 krishnakanthb13/password_generator
A production-ready, cryptographically secure password generator CLI with 17 generation modes, entropy transparency, and comprehensive customization…

 contiki-ng/tinydtls
A version of tinyDTLS that is refactored to be more easy to use "standalone" (e.g. without bindings to a specific IP-stack).
 user696/mrrat
:mouse: This is a cross-platform Python 2.x Remote Access Trojan (RAT)
 elevenpaths/iphonerestrictionspasscodebf
Extracts and decrypts the 4-digit restriction passcode from iPhone backups on Windows machines, enabling recovery of device access controls.