
aegis
 1llu50ry/aegis
Single-header C++20 software protection SDK with polymorphic VM code virtualization, compile-time MBA and string obfuscation, 25+ crypto primitives,…
anti-botbinary-analysiscryptography+6
3
1llu50ry/aegisSingle-header C++20 software protection SDK with polymorphic VM code virtualization, compile-time MBA and string obfuscation, 25+ crypto primitives,…
 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
 loadingalias/rscrypto
Rust cryptography w/ zero required deps: hashes, checksums, MACs, KDFs, password hashing, AEADs, signatures, RSA, key exchange, ML-KEM, and ML-DSA.…
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 captmag/maldev
Creation of multiple Malware tools consisting of evasion, enumeration and exploitation
 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 kraxel/virt-firmware
Toolkit for decoding, inspecting, and modifying UEFI firmware volumes and variable stores. Supports secure boot certificate enrollment, PE binary…
 sslmate/go-pkcs12
Go library for encoding and decoding PKCS#12 files
 merces/bashacks
A set of functions to increase productivity while hacking with Bash
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
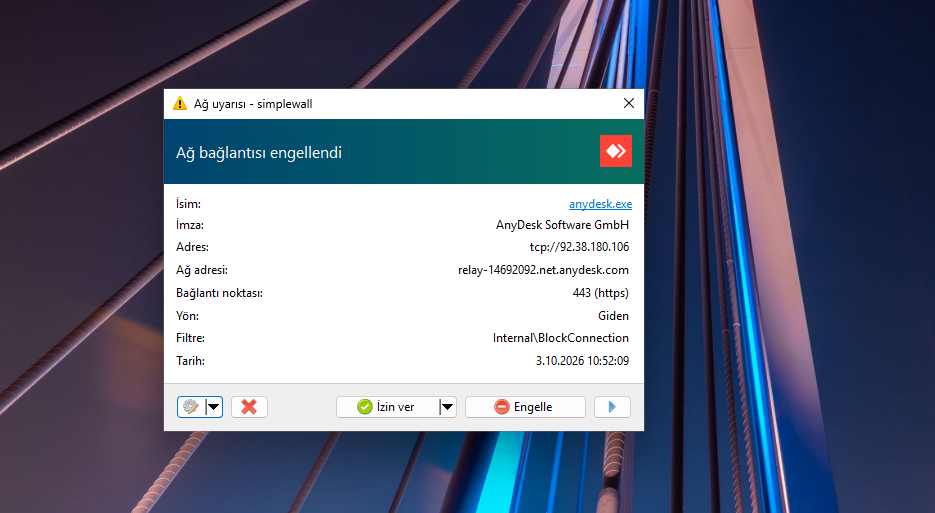 kaandemir993/python-shellcode-anydesk-apc-injection-remote-ip-address-analysis
Reverse engineering write-up of Python shellcode that APC-injects into AnyDesk, exfiltrates to a C2 over HTTPS with AES/RSA, and persists via…
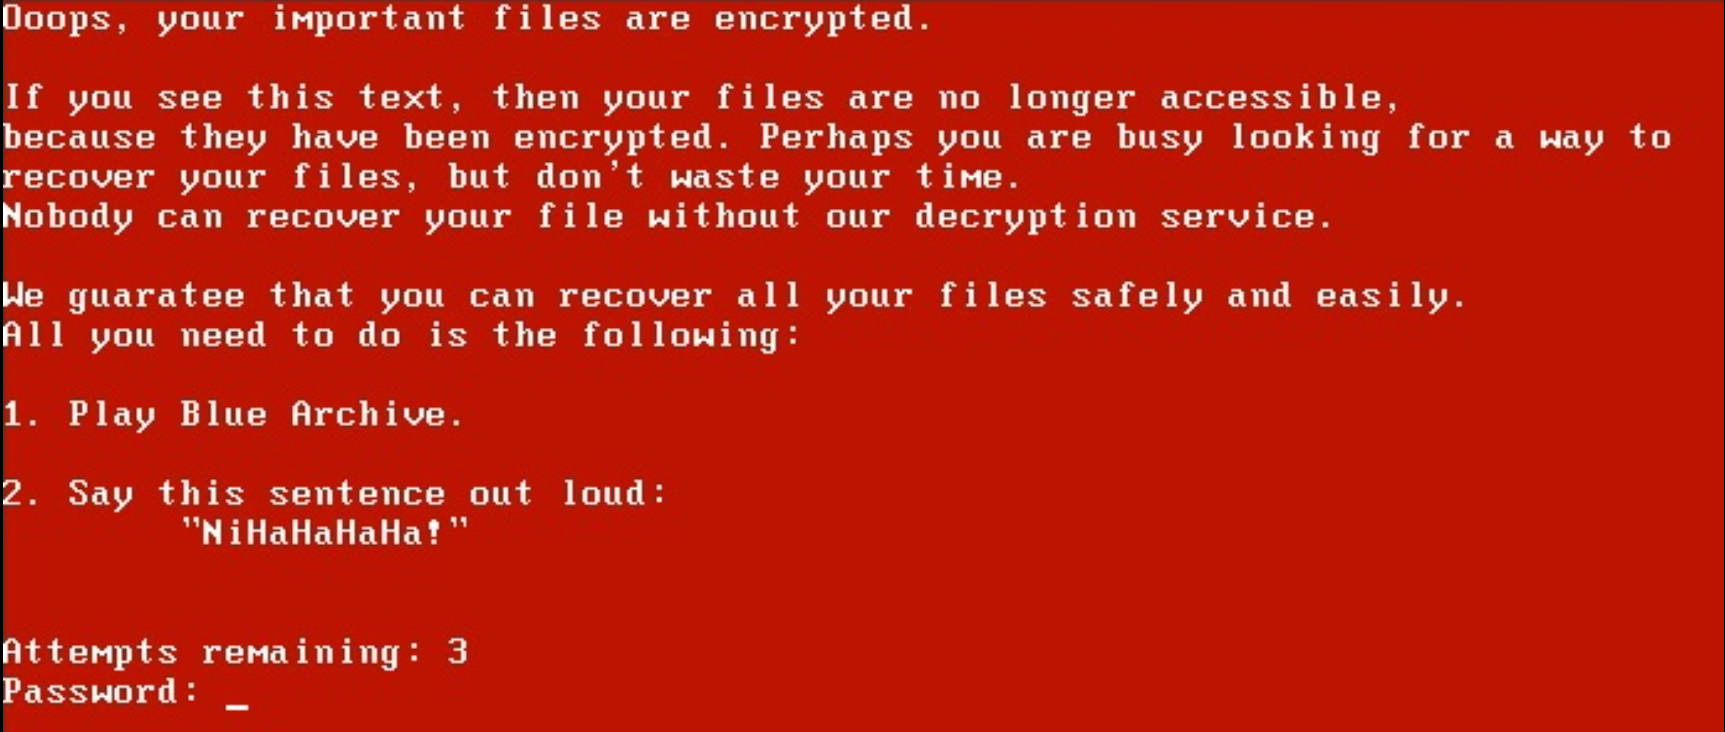 iss4cf0ng/openpetya
A Proof-of-Concept bootkit and UEFI boot application inspired by Petya ransomware, written in Assembly, C, and C++
 volexity/donut-decryptor
Extracts and decrypts inner payloads from Donut obfuscator samples by detecting loader shellcode signatures, parsing the DONUT_INSTANCE structure,…
 helgesverre/sony-vp-extract
Decrypt and extract voice guidance MP3 prompts from Sony WH-1000XM4 encrypted voice packs. AES key extracted via Bluetooth firmware dump of the…
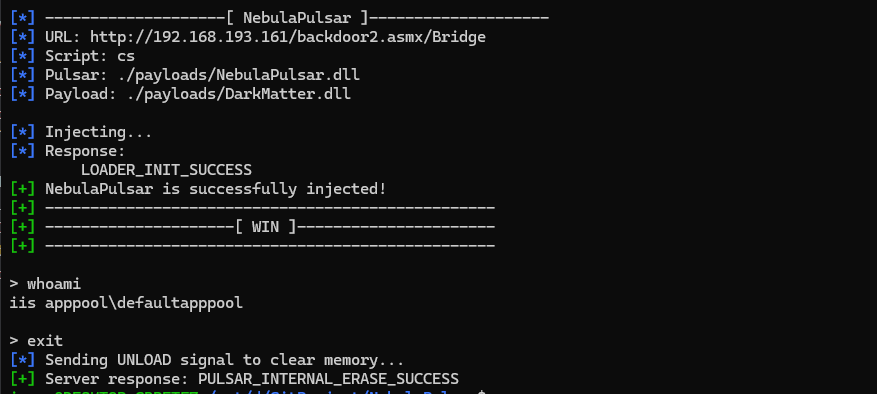 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…
 awnumar/memguard
Software sandbox for storage of sensitive information in memory.
 skelsec/pypykatz
Mimikatz implementation in pure Python
 xm0kht4r/ven0m-ransomware
Fully undetectable and evasive ransomware written in Rust, leveraging a BYOVD technique to disable AV/EDR solutions on the infected systems.