
frida-ios-dump
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
encryption-decryption-toolsios-securitymobile-app-pentesting+4
3.9k
alonemonkey/frida-ios-dumpExtracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
 kjcracks/clutch
Jailbreak-only iOS utility that decrypts installed app executables and dumps them as .ipa or raw binary files for security research and…

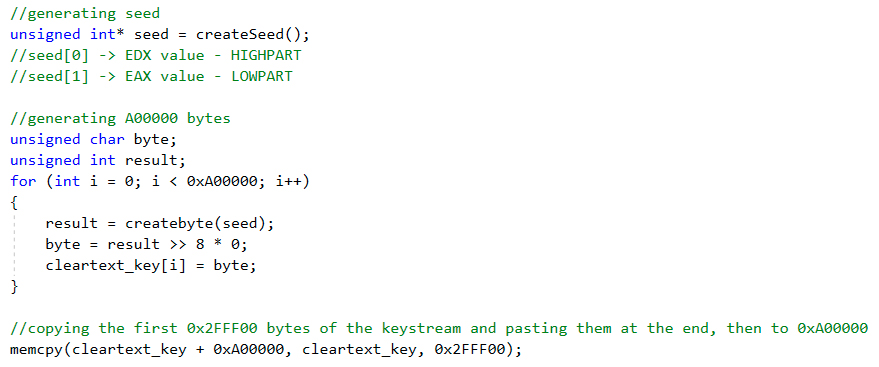 reecdeep/hivev5_keystream_decryptor
bad stuffs by bad guys
 dump-guy/powershell-tools
Collection of some easy of use tools - in powershell.
 prof.shafiei/abdal-lockbox
Local-first encrypted password vault for Android with Master Password access, Recovery Key support, Autofill integration, and portable encrypted…
 dodo-sec/kpot-string-decrypter
IDA python scripts to decrypt strings from KPOT and set those as comments
 watchfulip/tp-link-decrypt
Decrypt TP-Link Firmware
 jas502n/2024informationsecurityengineer
2024年信息安全工程师、2024InformationSecurityEngineer

 nccgroup/pip3line
The Swiss army knife of byte manipulation
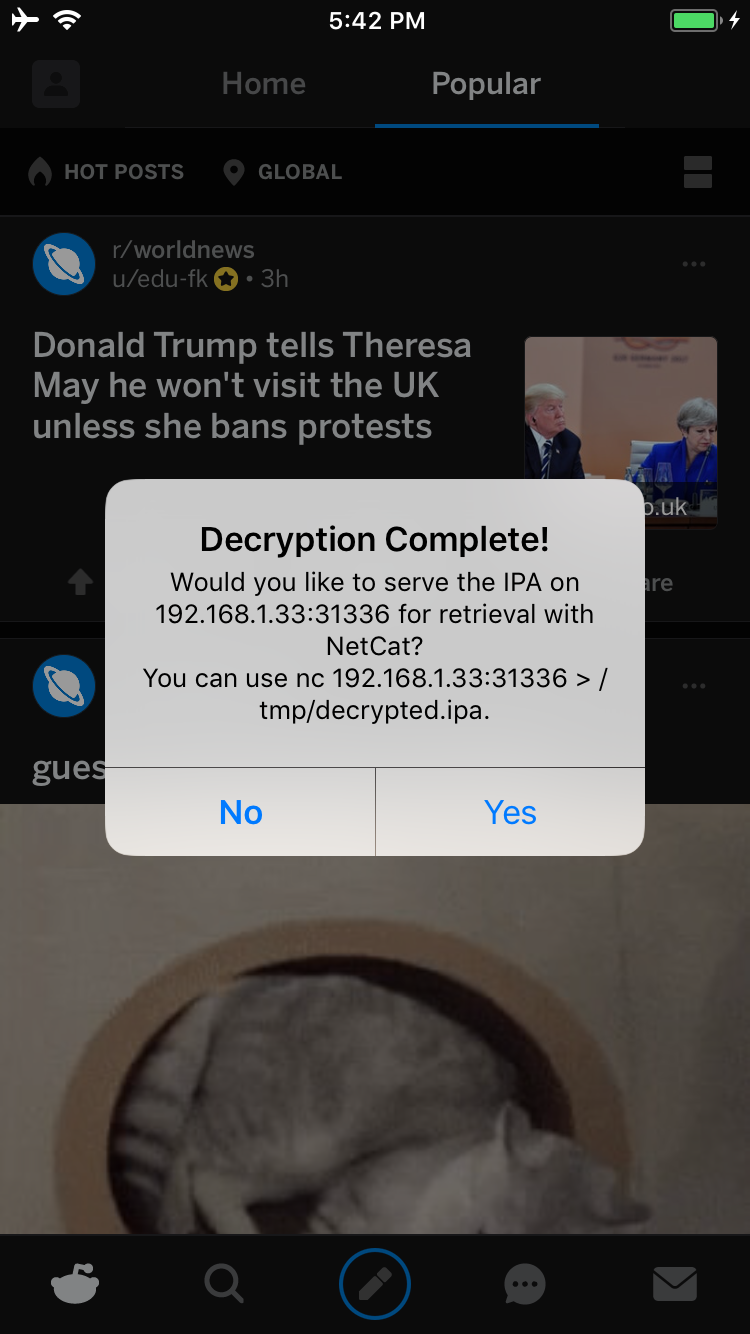 bishopfox/bfdecrypt
Utility to decrypt App Store apps on jailbroken iOS 11.x
 synacktiv/canon-tools
Tools used for decrypting Canon printers firmwares
 corelight/zeek-xor-exe-plugin
Zeek plugin to detect and decrypt XOR-encrypted EXEs
 eldavoo/wa-crypt-tools
Manage WhatsApp .crypt12, .crypt14 and .crypt15 files.
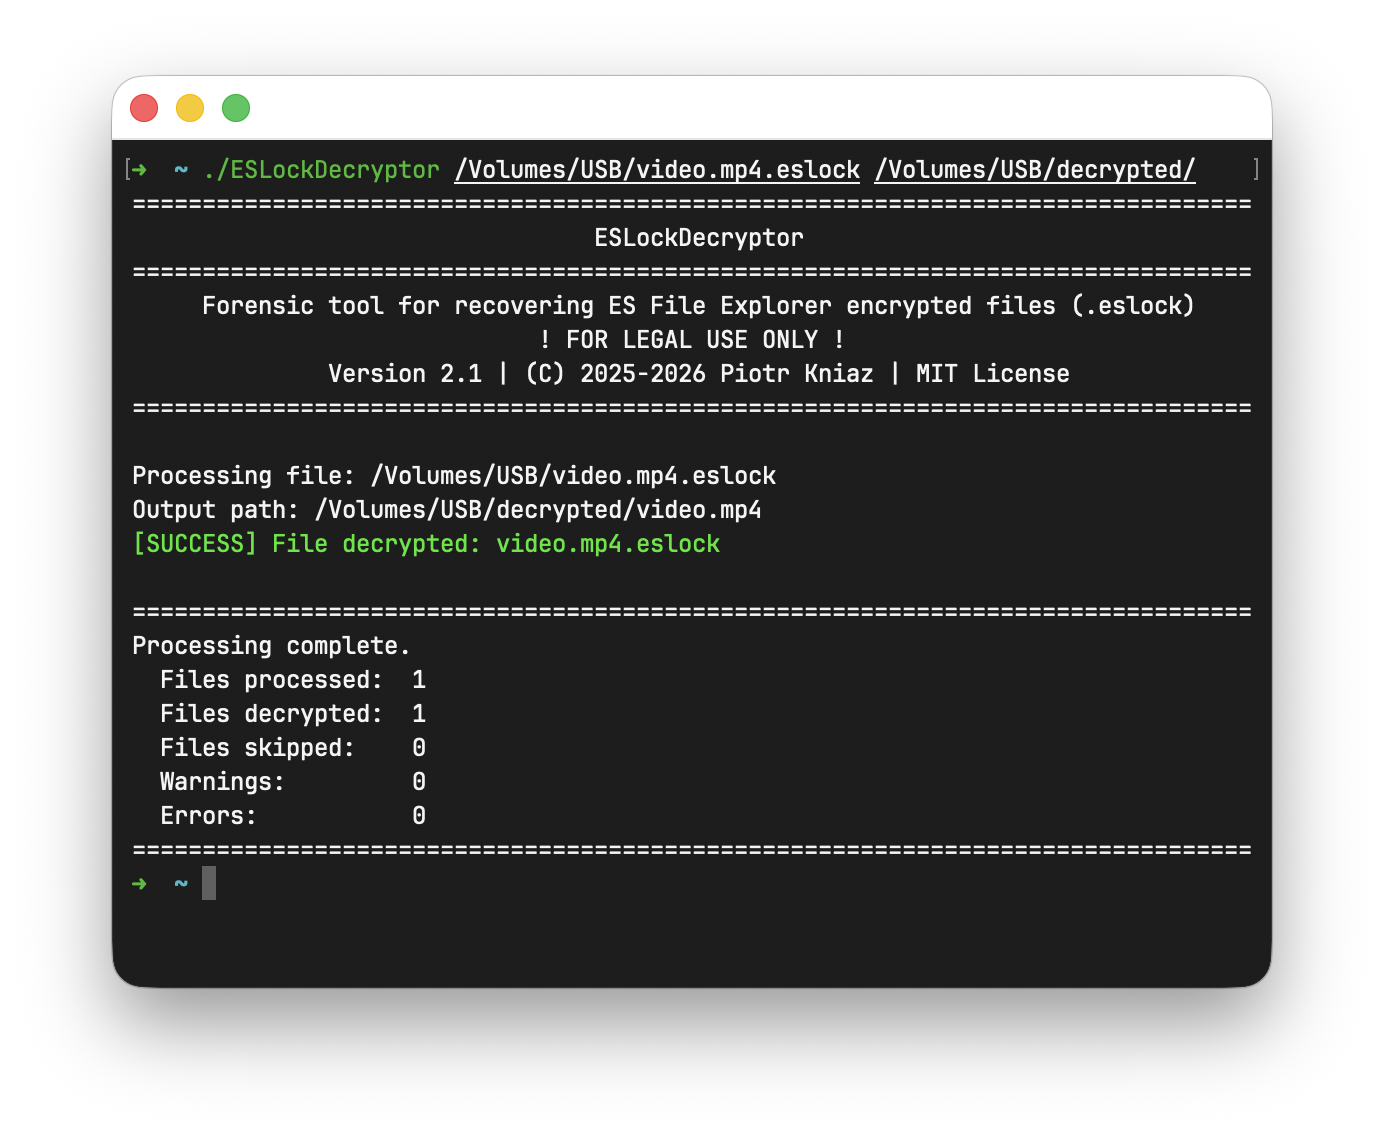 piotr-kniaz/eslockdecryptor
Utility for recovering ES File Explorer encrypted files (.eslock)
 hackerschoice/bincrypter
Pack/Encrypt/Obfuscate ELF + SHELL scripts