

Hollow
 chaelsoo/hollow
A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
binary-exploitationencryption-decryption-toolsexploitation+7
103
chaelsoo/hollowA shellcode loader generator with support for multiple injection techniques, built for red team engagements.
 freax13/cve-2024-21980-poc
Exploit for CVE-2024-21980 targeting AMD SEV firmware to decrypt arbitrary memory of decommissioned SEV-SNP guests via a command buffer enforcement…
 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
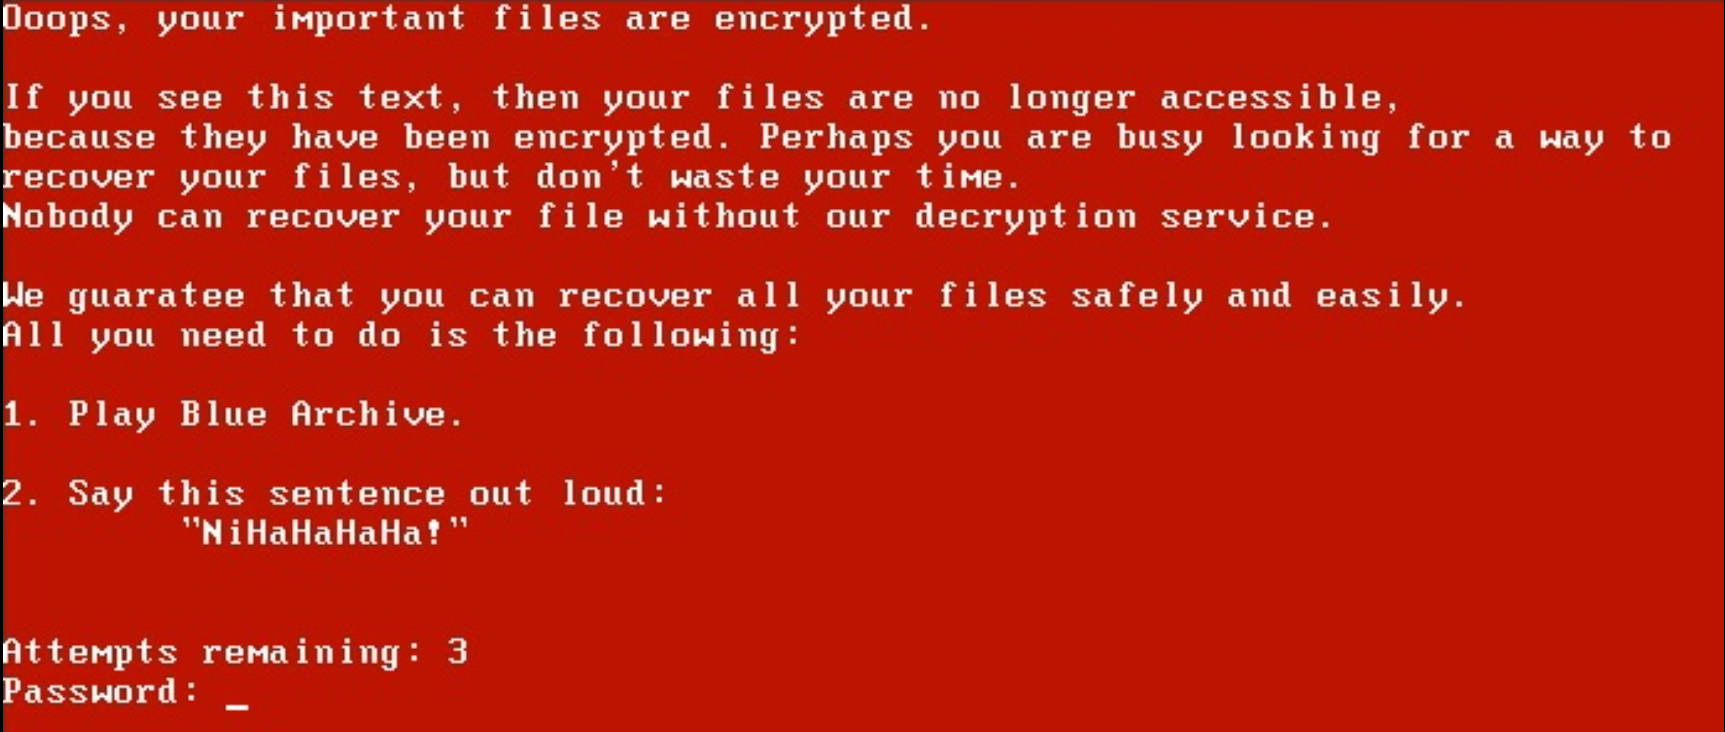 iss4cf0ng/openpetya
A Proof-of-Concept bootkit and UEFI boot application inspired by Petya ransomware, written in Assembly, C, and C++
 syrins/cve-2025-8088-winrar-tool-gui
A Windows GUI tool demonstrating a proof-of-concept archive traversal technique related to CVE-2025-8088 using WinRAR’s CLI. Allows building crafted…
 freax13/cve-2023-31355-poc
Exploit for AMD SEV-SNP firmware vulnerability (CVE-2023-31355) that decrypts arbitrary memory of decommissioned guests by corrupting the UMC key…
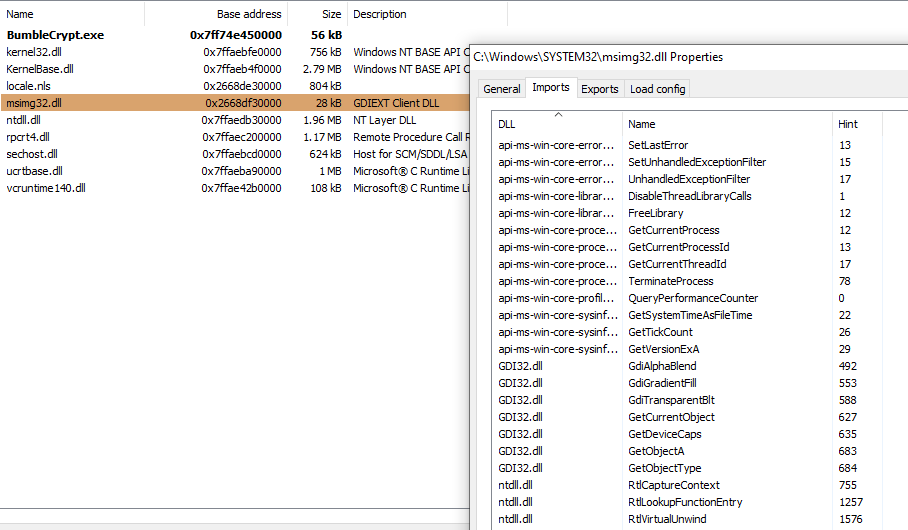 knight0x07/bumblecrypt
A Bumblebee-inspired Crypter
 3xpl01tc0d3r/processinjection
This program is designed to demonstrate various process injection techniques
 egebalci/amber
Reflective PE packer.
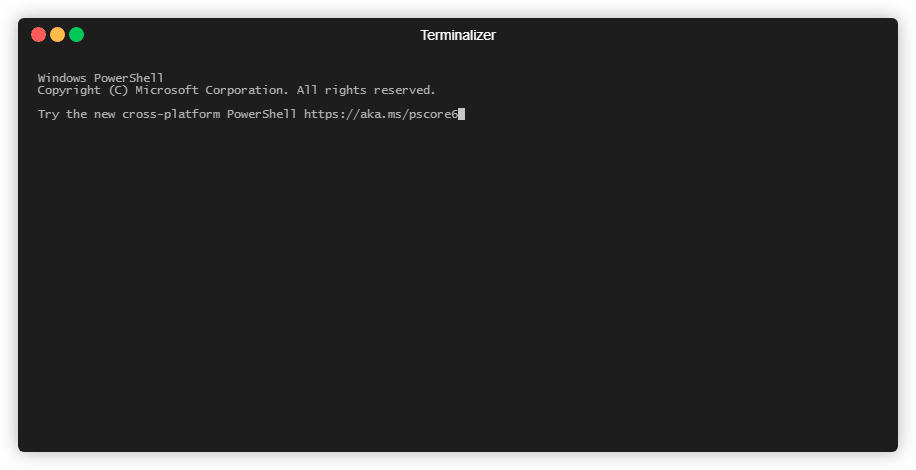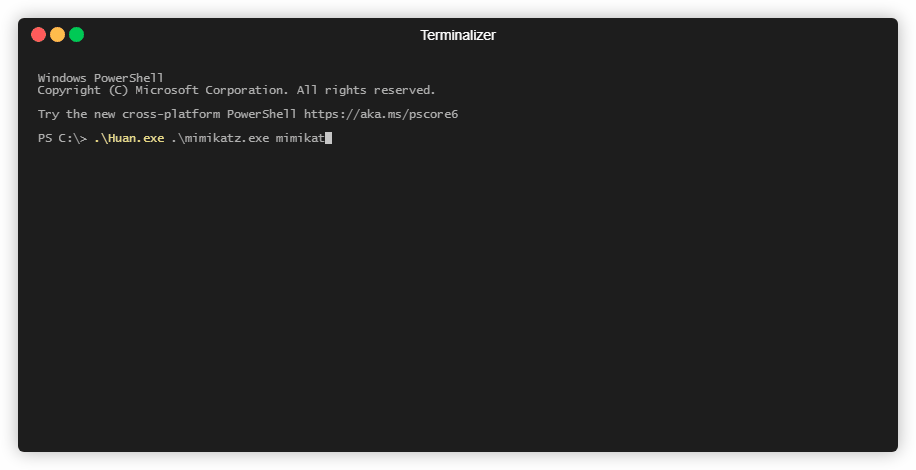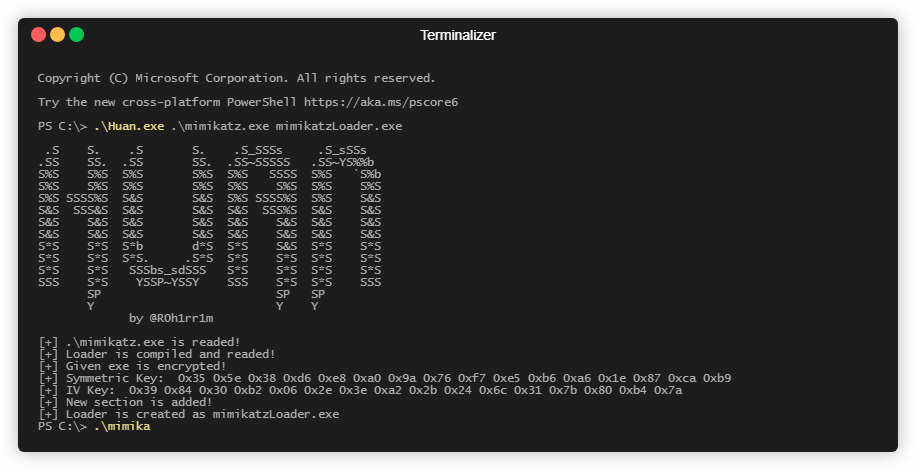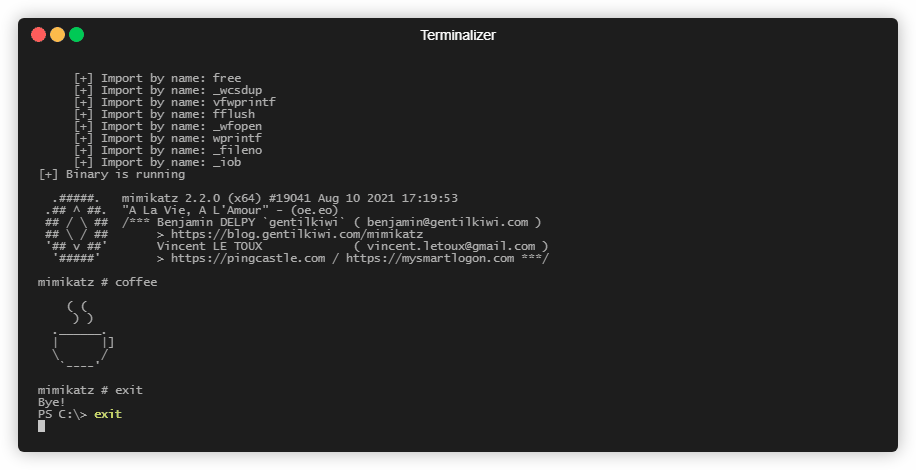 frkngksl/huan
Encrypted PE Loader Generator
 wack0/cve-2022-21894
baton drop (CVE-2022-21894): Secure Boot Security Feature Bypass Vulnerability
 enkomio/brokenflow
A simple PoC to invoke an encrypted shellcode by using an hidden call
 aurh1l-42-projects/woody-woodpacker
ELF binary packer that encrypts code sections and injects a runtime decryption stub for 64-bit Linux executables, demonstrating code injection and…
 freax13/cve-2024-21978-poc
Exploit for AMD SEV-SNP firmware vulnerability CVE-2024-21978, enabling decryption of arbitrary guest memory via memory corruption of context pages.
 vortexcry-organization/vortexcry-ransomware-release
Advanced ransomware using process injection and kernel driver loading via CVE-2019-16098 to encrypt files, disable recovery, and demand ransom. For…
 gentilkiwi/curveball
CVE-2020-0601 exploit tool that computes alternative ECC private keys from public certificates, enabling certificate spoofing via curve parameter…