
CVE-2026-20169
Windows-native IoT vulnerability scanner that discovers exposed management interfaces, tests default credentials, and validates network segmentation…

Windows-native IoT vulnerability scanner that discovers exposed management interfaces, tests default credentials, and validates network segmentation…

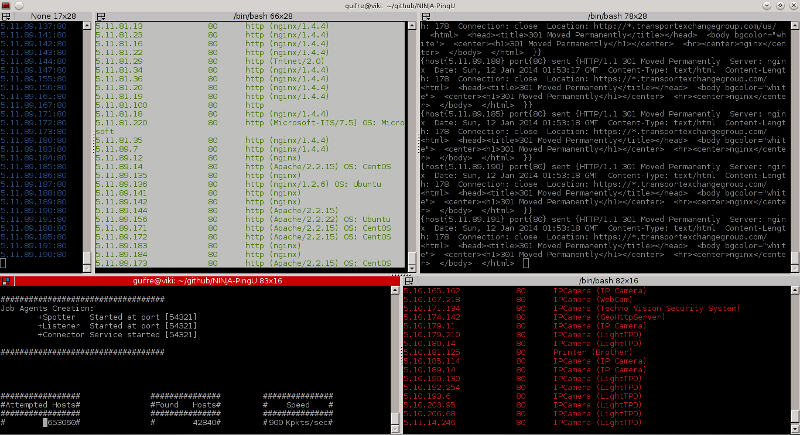
High-performance network scanner for large-scale IP and port scanning with service identification, embedded device detection, and vulnerability…

Proof-of-concept exploit and vulnerability disclosure for HiSilicon hi3520d DVR/NVR devices. Demonstrates RCE via web interface, backdoor…

Android Bluetooth stack (Fluoride) with a proof-of-concept for CVE-2022-20140, demonstrating a Bluetooth vulnerability and providing build…

Towards Large-Scale Emulation of IoT Firmware for Dynamic Analysis

exploits and proof-of-concept vulnerability demonstration files from the team at Hacker House

Independent IoT security research, vulnerability disclosures, and PoCs focusing on firmware analysis, hardware interfaces, and cryptographic flaws.

Android Bluetooth stack (Fluoride) source code for AOSP 10 r33, specifically related to CVE-2021-0431 Bluetooth vulnerability research and…

CVE-2026-43499 (GhostLock) — Linux kernel futex PI rt_mutex UAF ARM32 privilege escalation research targeting Huawei Watch 4 Pro (kernel 5.4.210)

IoT Security research conducted during my internship at IIIT Allahabad, leading to CVE-2026-65893, CVE-2026-65894, and the CERT-In Vulnerability Note…

Active fingerprinting tool that identifies 16 embedded TCP/IP stacks on network devices using ICMP, TCP, HTTP, SSH, and FTP probing techniques for…

Analyzing and Reproducing the Command Injection Vulnerability (CVE-2023-0861) in NetModule Routers

Technical articles detailing IoT vulnerability research, including WiFi communication flaws and firmware update weaknesses in connected devices, with…

Metasploit module exploiting unauthenticated command injection in multiple Netgear router models to achieve remote code execution with root…

A technical case study and exploitation analysis of the Authentication Bypass vulnerability in TP-Link TL-WR840N firmware (CVE-2018-12633).

PoC for DoS vulnerability CVE-2021-37740 in firmware v3.0.3 of SCN-IP100.03 and SCN-IP000.03 by MDT. The bug has been fixed in firmware v3.0.4.

Dahua CVE-2026-29115

Documentation of CVE-2020-25748: Cleartext transmission vulnerability in Rubetek IP cameras allowing MITM interception and modification of video…