EvilCrowRF_Custom_Firmware_CC1101_FlipperZero

This firmware is an alternative to the EvilCrowRF default firmware. Module: CC1101 - Compatible Flipper Zero file.

This firmware is an alternative to the EvilCrowRF default firmware. Module: CC1101 - Compatible Flipper Zero file.

Tools for analyzing and reverse engineering MediaTek baseband firmware, including file extraction, symbol parsing, and Ghidra integration for modem…

Determine which CPU architecture is used in a binary file.


A buffer overflow in the component nfc_device_load_mifare_ul_data of Flipper Devices Inc., Flipper Zero before v0.65.2 allows attackers to cause a…

Watchguard Sysa-dl file format

Rom-0 file password decrypter

Technical disclosure of CVE-2024-33676: weak authentication on Enel X JuiceBox EV chargers enabling PII extraction, settings manipulation, and OS…

PoC exploit for CVE-2018-18778: arbitrary file read in mini_httpd 1.29 via empty Host header, affecting IoT devices from Huawei, Zyxel, and others.

Proof-of-concept exploit for CVE-2023-31716, a Local File Inclusion vulnerability in FUXA SCADA/HMI software versions <= 1.1.12, enabling arbitrary…

A tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)

Wi-Fi Geolocation Spoofing with ESP8266 / ESP32

Rust library and format specification for creating and loading Independent Guest Virtual Machine (IGVM) files, supporting hardware-isolated VMs with…

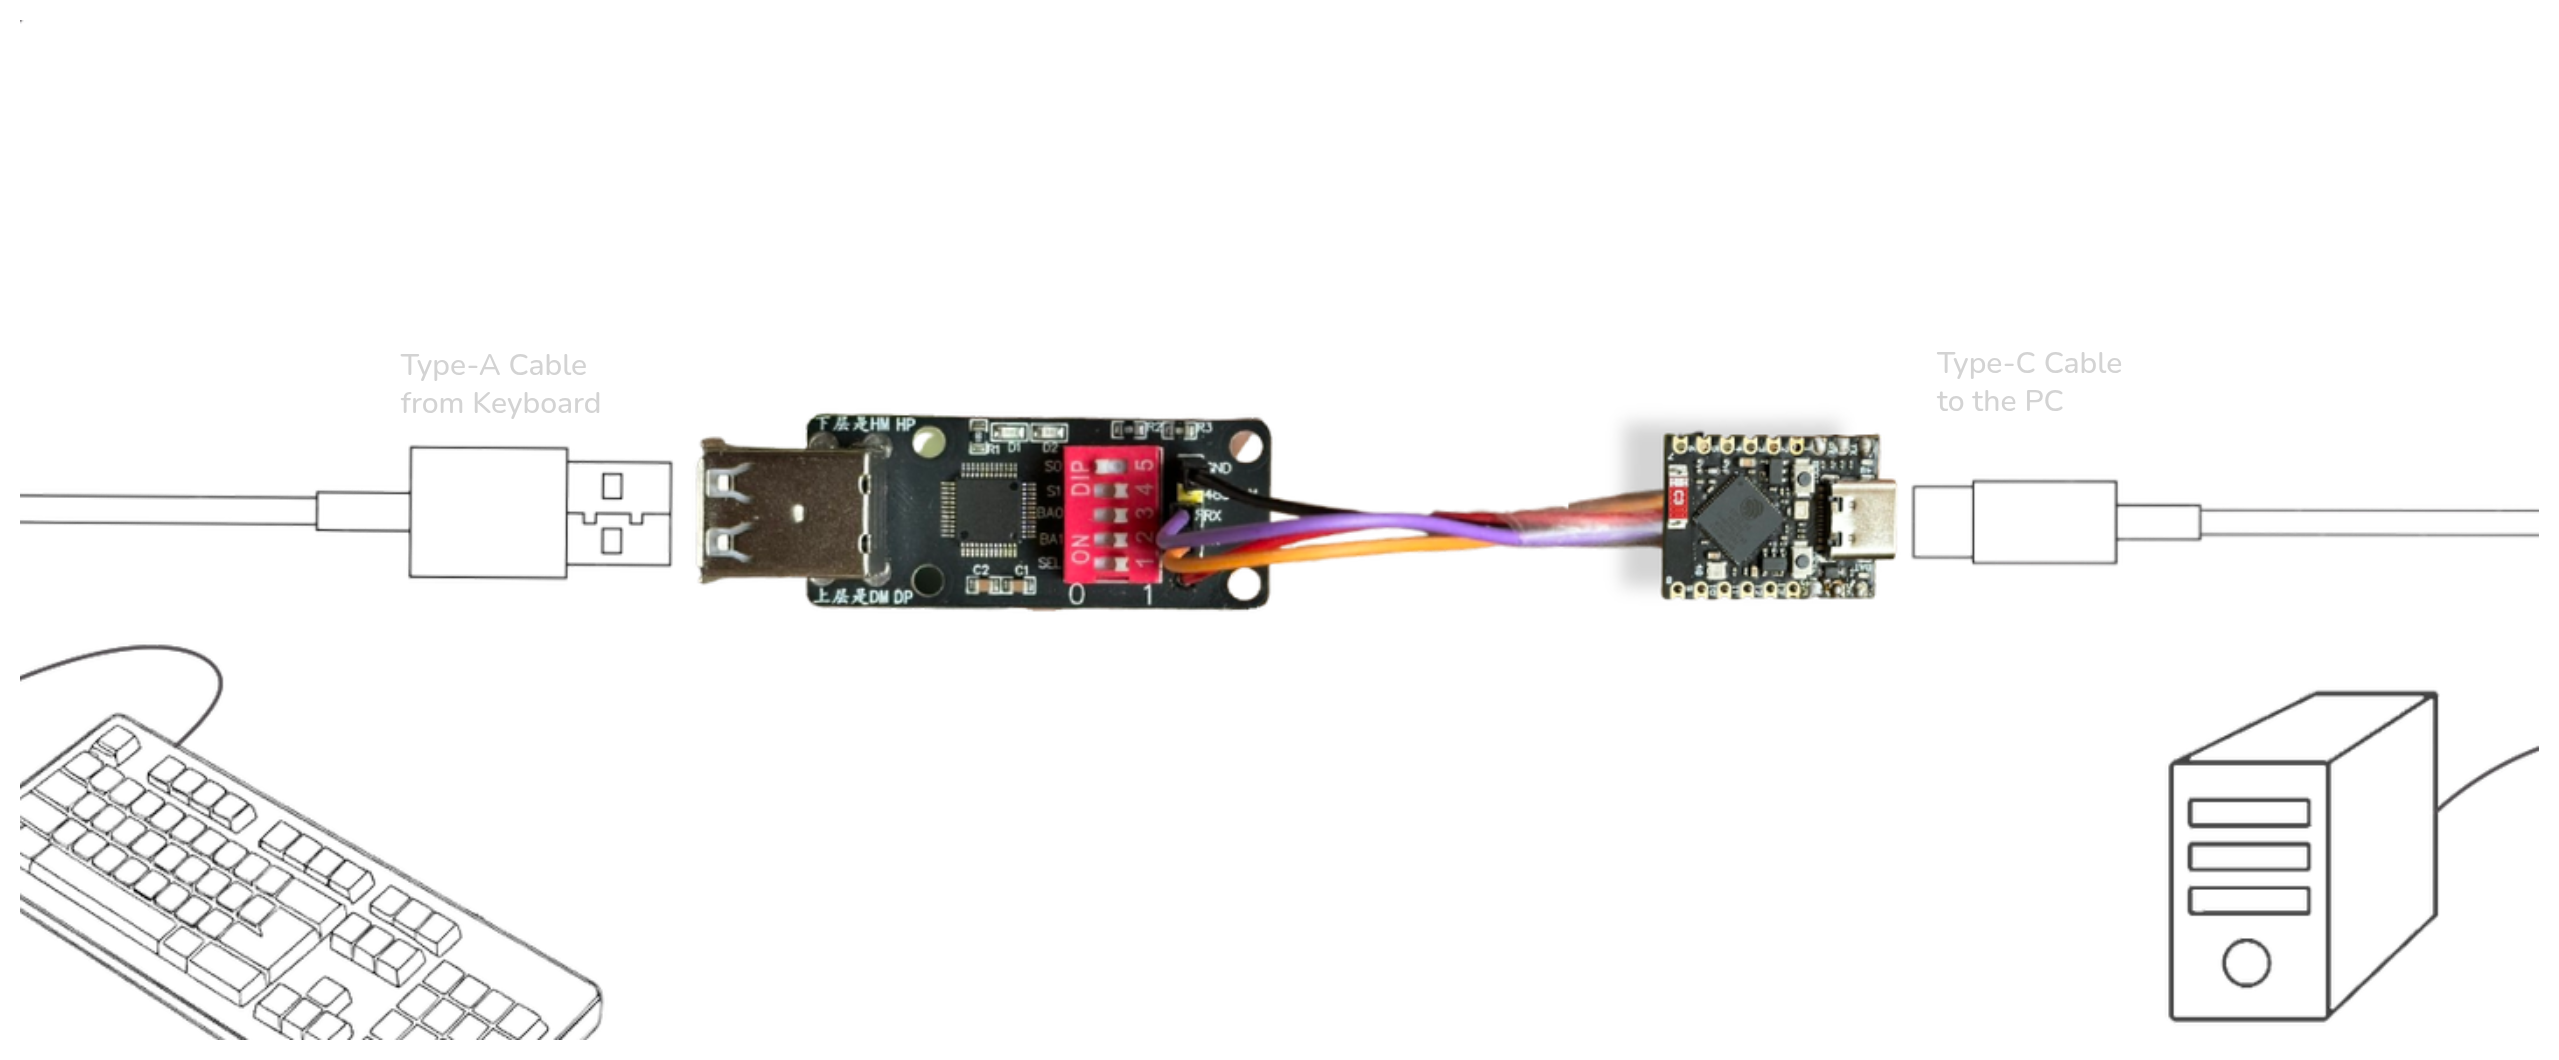
A ESP32-S3–based usb keylogger with wifi, easy DIY-able with widely available hardware.

nanoMIPS module for Ghidra

Proof-of-concept for CVE-2026-90847, an authenticated RCE in iux_set.cgi via malicious .cfg tar upload that writes commands into crontab for…

Framework for controlling QKD devices and managing symmetric keys. See the [project page here](https://qcomms.gitlab.io/cqptoolkit/)

An app that enables payload injection into a Switch console from an Android device by exploiting the CVE-2018-6242 vulnerability