
CVE_2022_38181_Raven
 pro-me3us/cve_2022_38181_raven
CVE-2022-38181 POC for FireTV 2nd gen Cube (raven)
android-securitybinary-exploitationembedded-systems-security+3
7
pro-me3us/cve_2022_38181_ravenCVE-2022-38181 POC for FireTV 2nd gen Cube (raven)
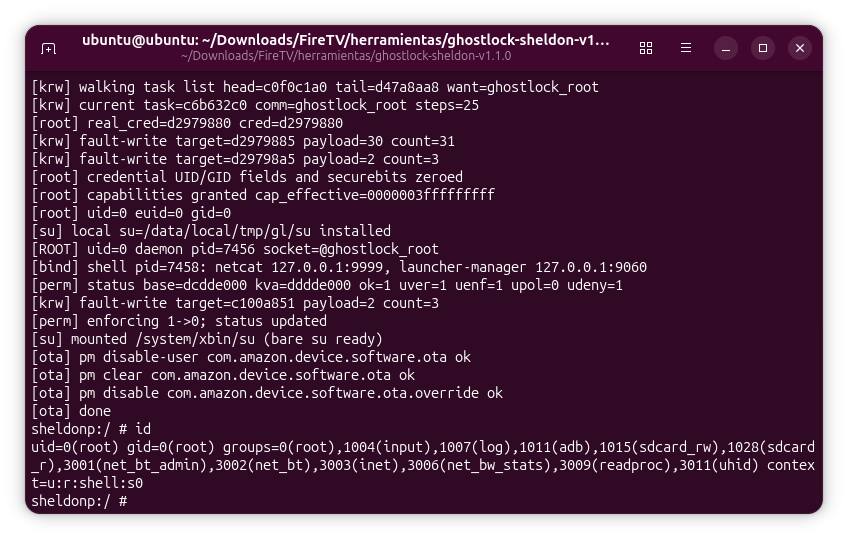 accessmodifier364/cve-2026-43499-firetv-sheldonp-writeup
Security research write-up on exploiting CVE-2026-43499 on the Amazon Fire TV Stick 3rd Gen (sheldonp), from temporary root to bootloader unlock.
 pro-me3us/cve_2022_38181_gazelle
CVE-2022-38181 POC for FireTV 3rd gen Cube (gazelle)
 pro-me3us/cve_2022_46395_gazelle
CVE-2022-46395 POC for FireTV 3rd gen Cube (gazelle)
 rfidresearchgroup/proxmark3
Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…
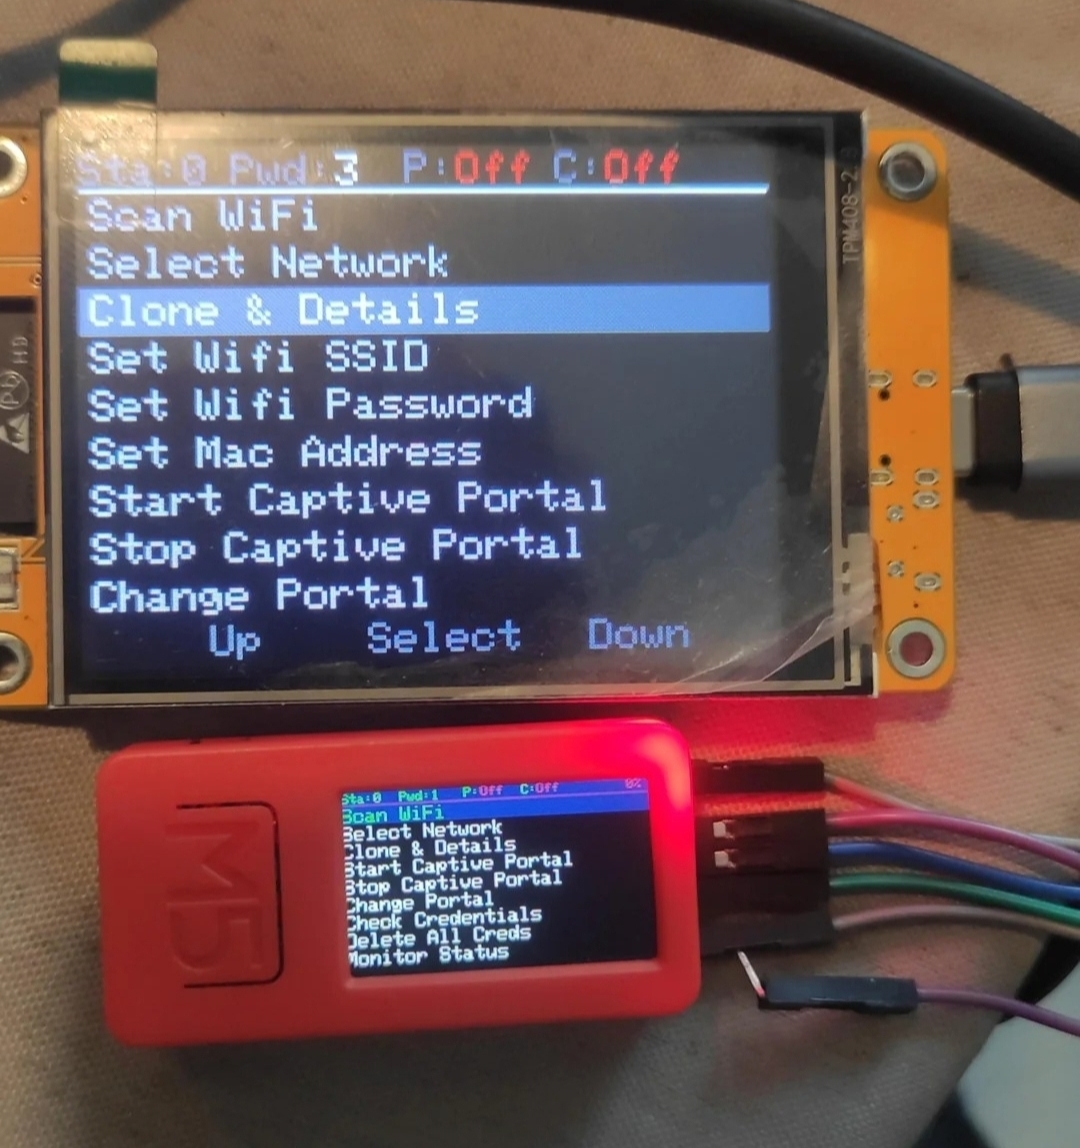 7h30th3r0n3/evil-m5project
Multi-purpose WiFi penetration testing toolkit for M5Stack devices. Performs network scanning, evil-twin attacks, deauthentication, captive portal…
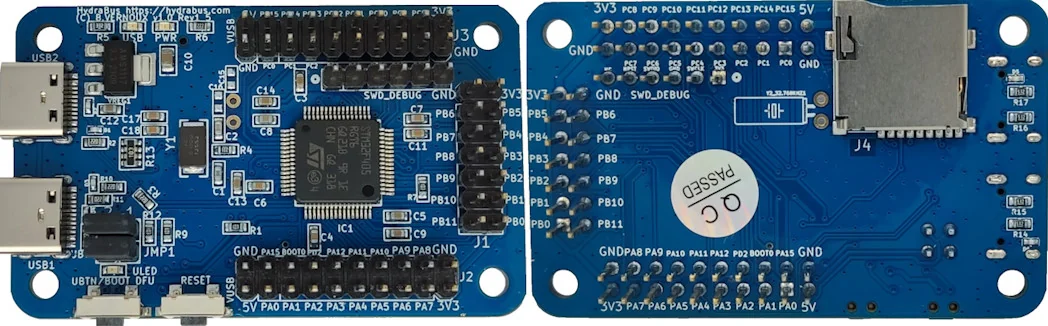 hydrabus/hydrafw
Open-source firmware for HydraBus, a multi-tool for embedded hardware debugging, hacking, and penetration testing, supporting protocols like SPI,…
 owasp/owasp-istg
The IoT Security Testing Guide (ISTG) provides a comprehensive methodology for penetration tests in the IoT field, offering flexibility to adapt…
 iotsrg/iot-pentest-devices-and-purpose
Curated guide to IoT penetration testing hardware and software tools for 2025, covering Bluetooth, Zigbee, Z-Wave, WiFi, RFID, automotive, and…
 askhatov21/best-practices-cybersecurity-otanata-project
CVE-2024-3273 — Authorized Penetration Test Report D-Link DNS-320L NAS | Client: Otonata
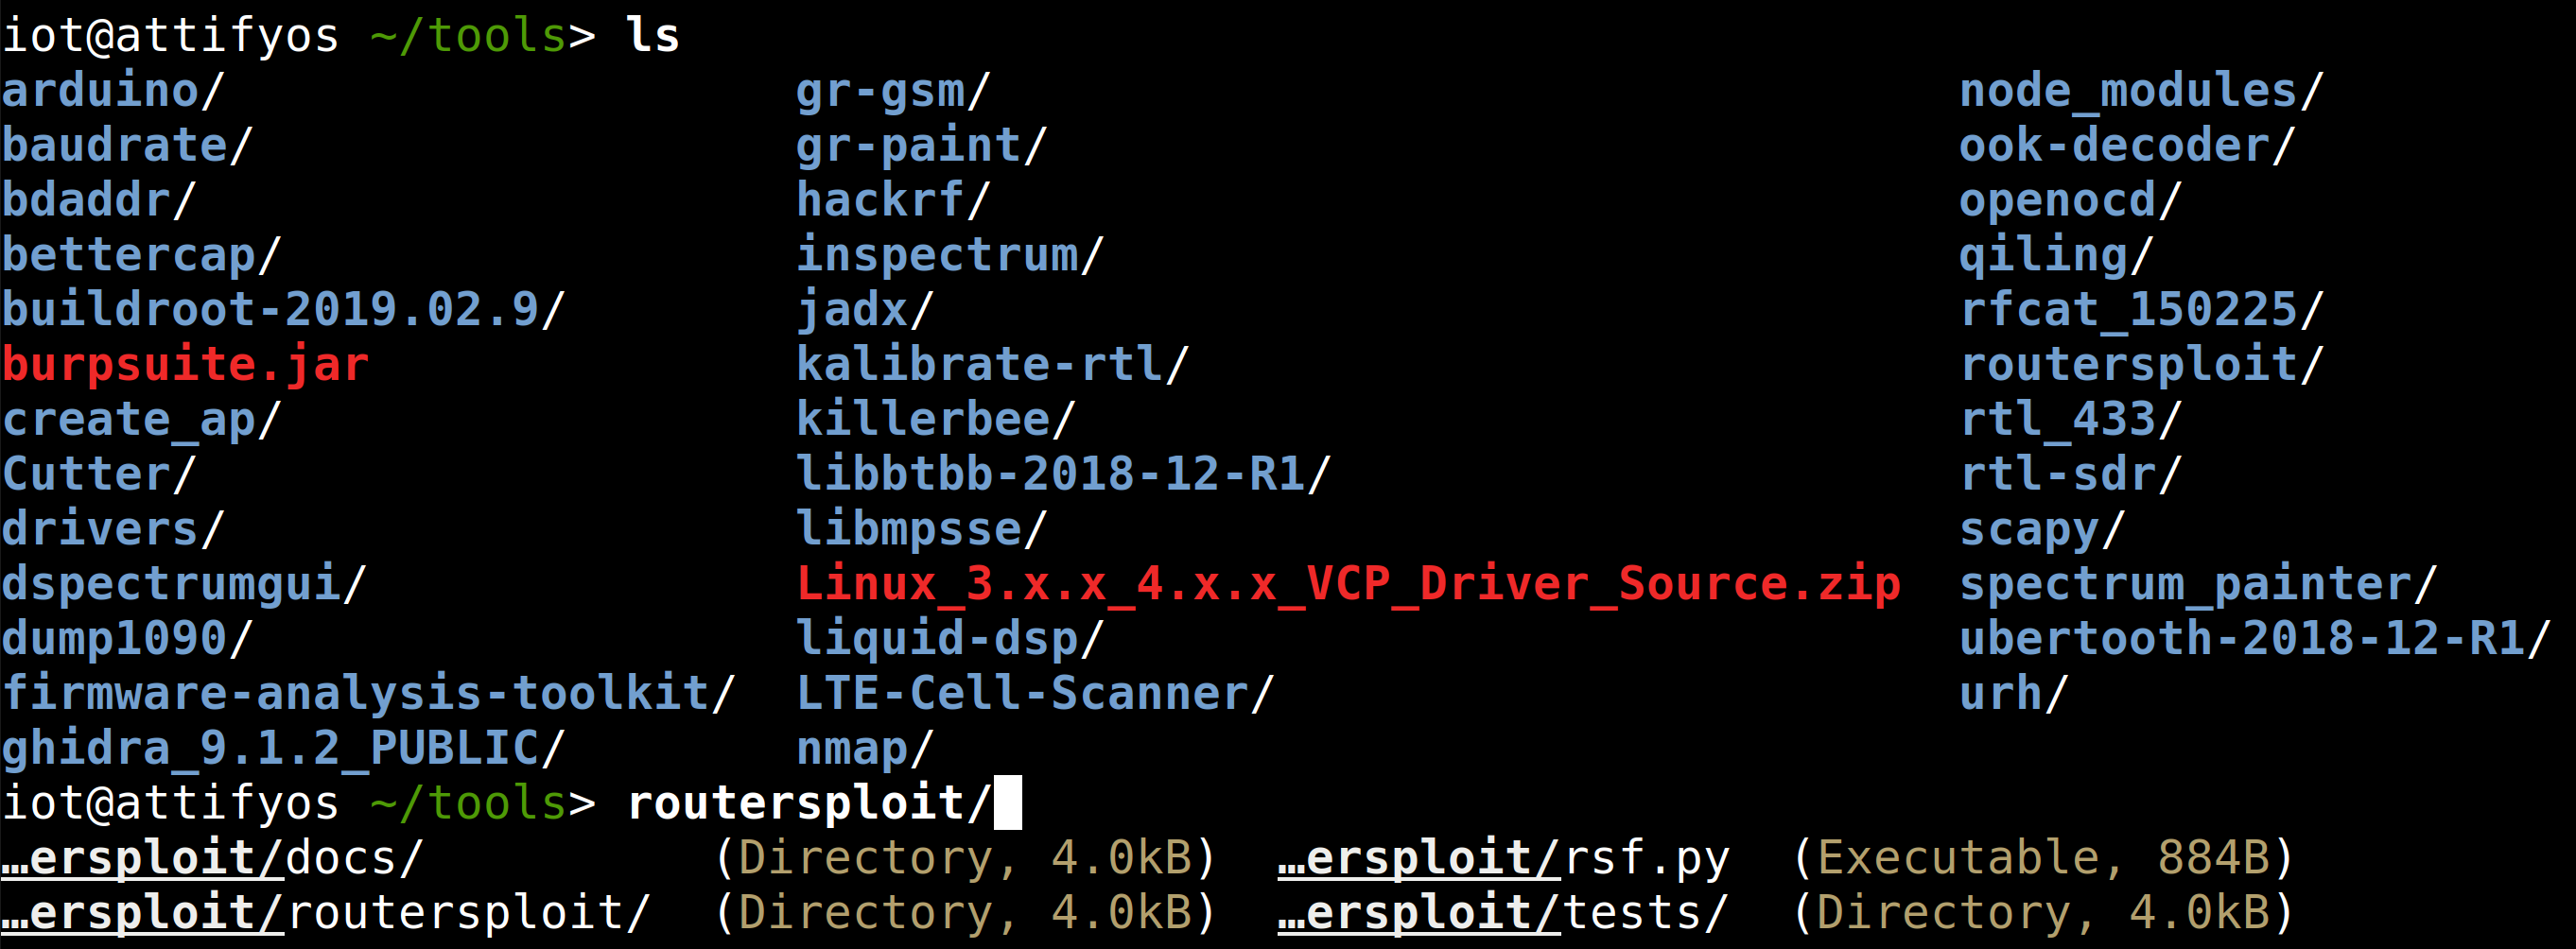 adi0x90/attifyos
Attify OS - Distro for pentesting IoT devices
 bishopfox/zigdiggity
A ZigBee hacking toolkit by Bishop Fox
 horkimhab/cve-2022-25477
CVE Realtek SD card reader. CVE-2022-25477, CVE-2022-25478, CVE-2022-25479, CVE-2022-25480, CVE-2024-40432, CVE-2024-40431
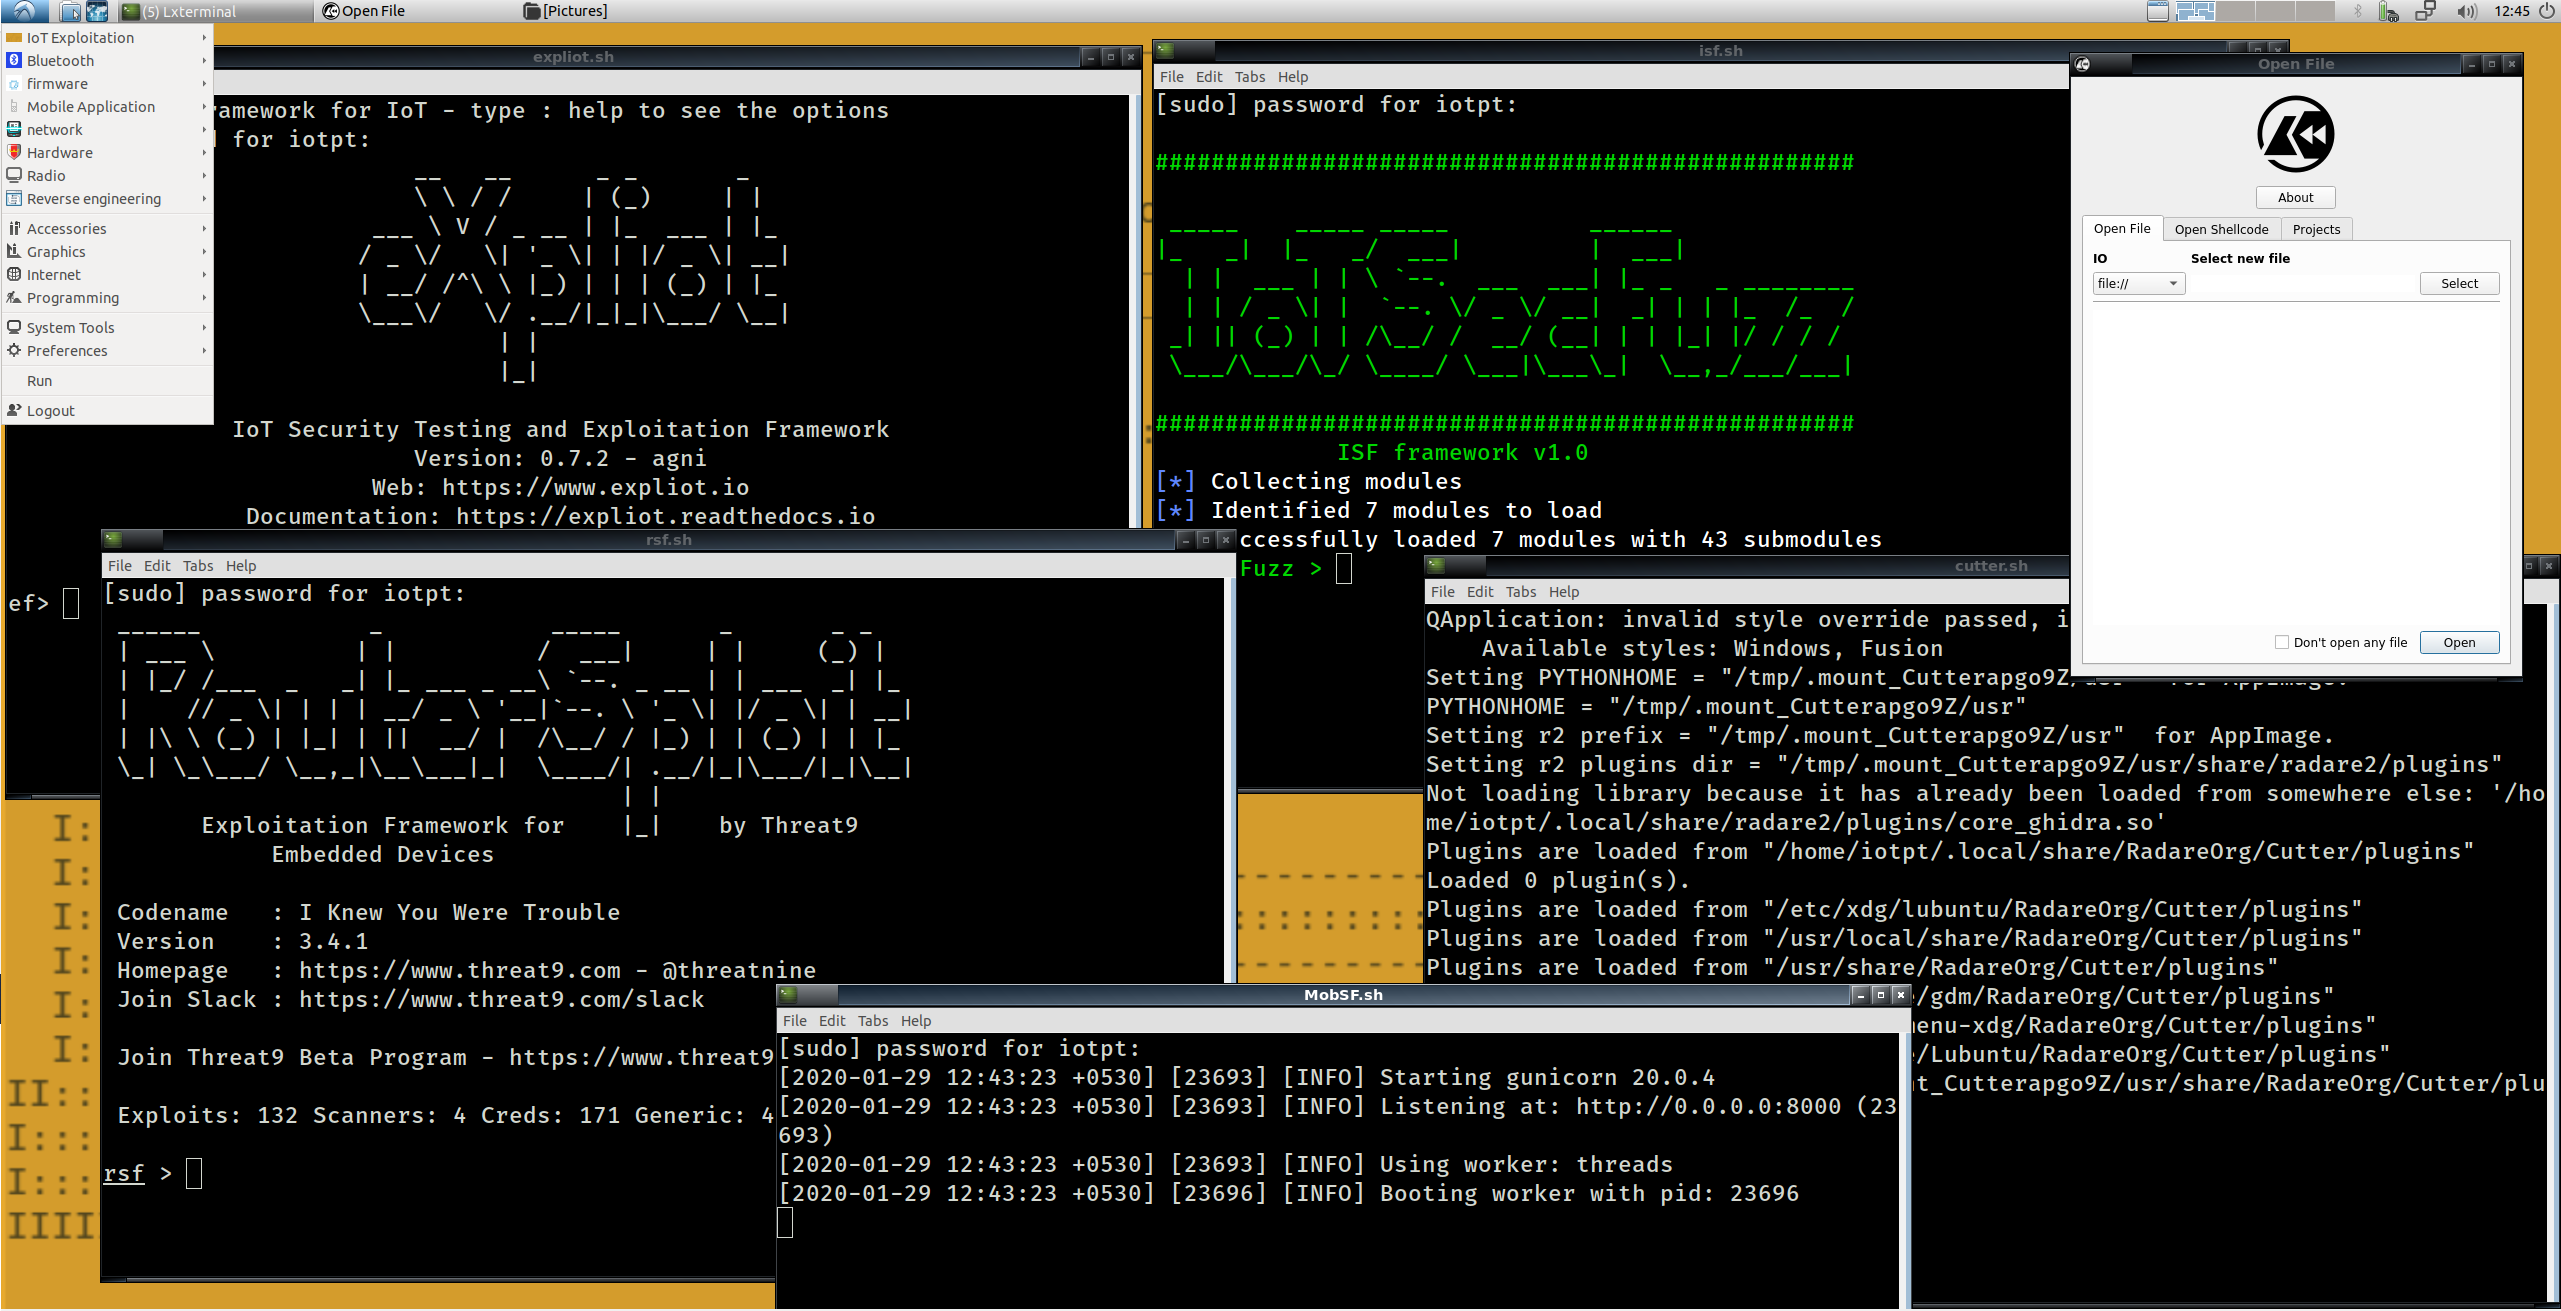 iot-ptv/iot-pt-v1
A Virtual environment for Pentesting IoT Devices
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 librepods-org/librepods
AirPods liberated from Apple's ecosystem.
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…